The Industry's Premier Virtual Event for AI in GRC
Confirmed Speakers
Industry leaders sharing insights on governance, risk, and compliance
Sue Gomez
Chief Operating Officer for Corporate Audit
State Street
James Downing
Chief Compliance Officer
JLL Capital Markets
Patrick Simonnet
Chief Audit Executive
Bank of China USA
Masood Ali
MD Data Strategy & Governance
State Street
Spruille Braden
Head of Enterprise Resilience
MassMutual
Sadhana Deot
Vice President, Global Ethics & Compliance
Trimble
Clifton Roberts
Senior Director, Legal & Business Compliance
Intel Corporation
Maria T. Buccieri
Senior Director, Enterprise Compliance & Ethics
Amtrak
Michael Cover
Director
Blue Cross Blue Shield of Michigan
Solomon Ugah
Global Cyber Compliance Leader
Rockwell Automation, Inc
Jessica Markun
Senior Vice President, Finance & Risk
FCCI Insurance Group
Michael Rasmussen
Analyst & Pundit
GRC 20/20 Research & GRC Report
Gaurav Kapoor
Co-founder & Vice Chairman
MetricStream
Marc Levine
Chief Executive Officer
MetricStream
Shreyank S. Kamat
Associate Vice President - Product Management
MetricStream
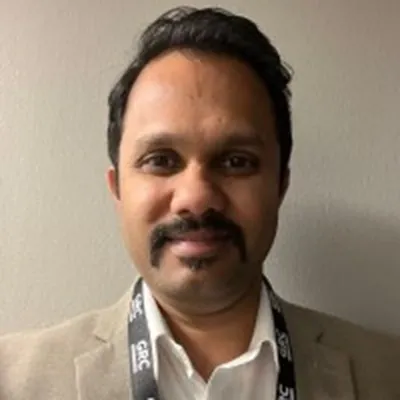
Anil Kumar G K
Associate Vice President
MetricStream
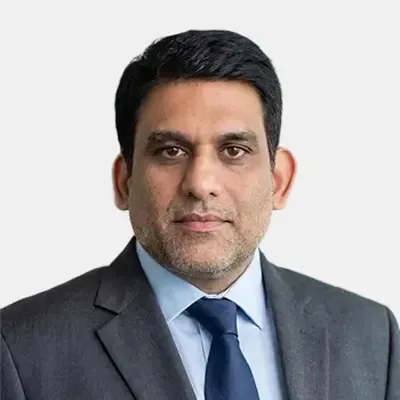
Kiran Hariharan
Vice President, R&D, Head of AI Framework & Products
MetricStream
Agenda & Sessions
7:30–11:30 AM Pacific / 10:30 AM–2:30 PM Eastern, both days. Sessions run 40 minutes with a 5-minute break in between.
 7:30 AM – 7:40 AM
Introduction and Welcome
Speakers
 7:40 AM - 8:10 AM
Orchestrating the AI Future of GRC
Speakers
Cyber threats, regulatory change, and operational complexity continue to put pressure on risk and compliance teams, and organizations want a simpler, faster way to manage GRC. This keynote looks at where GRC is heading with an AI-powered strategy, and how to decide where human judgment and AI insight each add the most value. You'll learn how AI-Powered Connected GRC simplifies governance and improves outcomes across the enterprise.
8:15 AM - 8:45 AM
Turning GRC into a Strategic Business Advantage
Speakers
Join Marc Levine, CEO of MetricStream, as he shares his vision for the future of GRC and how organisations can transform GRC into a strategic business advantage. In this keynote, Marc will explore how a focus on customer experience, simplicity, and business value can help organisations strengthen decision-making, drive better outcomes, and realise greater value from their GRC programmes.
8:50 AM - 9:20 AM
Beyond the Interface: AI-Powered Innovation Across Risk and Compliance
Speakers
Discover how MetricStream is advancing the GRC experience through AI-powered innovation across Risk and Compliance. This session will showcase the latest AI enhancements designed to simplify complex workflows, deliver actionable insights, and help users make more informed decisions. Explore how AI is being embedded into everyday GRC activities through intelligent assistance, automation, and recommendations, with human judgment remaining central to critical decisions. We will also highlight the completion of MetricStream’s UI/UX uplift journey, setting the foundation for a more intuitive, connected, and intelligent product experience.
9:25 AM - 10:05 AM
How AI Is Transforming the Roles of Chief Risk, Audit & Compliance Officers
Speakers
Risk, compliance, and audit teams have traditionally focused on identifying issues, assessing controls, and looking back at what went wrong. AI is changing that model, helping Chief Audit, Risk & Compliance leaders identify emerging risks earlier, navigate regulatory complexity faster, strengthen assurance, and free their teams to make the judgment calls that matter most. Explore how AI can shift these functions from reactive oversight to proactive, forward-looking assurance.
10:10 AM - 10:40AM
From Reactive to Resilient: GRC Transformation in Action
Speakers
Join Jessica Markun, SVP, Finance & Risk at FCCI, for a real-world case study on transforming GRC from a reactive function into a proactive, resilient business capability. Explore how organisations can strengthen risk management, improve cross-functional collaboration, and embed resilience into everyday decision-making to navigate uncertainty and drive better business outcomes.
10:45 AM - 11:15AM
From GRC Silos to a System of Intelligence: Connecting Risk, Compliance and AI to Drive Growth
Speakers
Organisations are drowning in GRC data but starving for actionable insight, and AI is raising the stakes. As regulations such as the EU AI Act takes hold and boards demand accountability for how AI is used, GRC functions are being asked to govern AI as well as be transformed by it. This panel brings together assurance and risk leaders across industries, including regulated industries such as financial services, energy, and telecommunications who have evolved their GRC functions from reactive reporting to proactive intelligence hubs. Panelists will share how they are breaking down data silos, applying AI and analytics to deliver real-time, predictive risk insight to boards and business leaders, and building the governance to keep AI trustworthy, explainable, and compliant. Attendees will learn practical strategies to extract strategic value from GRC data, use AI to manage and deliver insights across the organization, and position risk functions as essential partners in business growth.
11:15 AM - 11:30 AM
Summit Day 1 Recap & Closing
7:30AM - 7:40 AM
Introduction and Welcome
Speakers
7:40 AM - 8:10 AM
Agentic AI in GRC: From Novelty to Strategic Business Advantage
Speakers
Agentic AI is moving fast from experimentation into how organizations manage risk, compliance, audit, cybersecurity, and business processes, but realizing its strategic value takes more than deploying agents. It requires rethinking how GRC is connected, governed, and operated. Michael Rasmussen explores the shift from individual AI use cases toward a connected, intelligent GRC operating model, examining the evolving relationship between AI agents and human decision makers, the governance AI driven action demands, and what organizations must build now, accountability, guardrails, transparency, and oversight, to turn Agentic AI from an emerging capability into lasting, sustainable GRC value at scale.
8:15 AM - 8:45 AM
Inside a Real GRC Transformation: Lessons from the Field
Speakers
Explore a real-world GRC transformation through the experience of Blue Cross Blue Shield of Michigan. In this case study, Michael Cover, Director, shares practical insights, key lessons learned, and challenges encountered along the transformation journey, offering actionable takeaways for organisations looking to strengthen their GRC programmes and drive meaningful business outcomes.
8:50 AM - 9:30 AM
The AI Way to Build an Enterprise GRC Program That Works on the Ground
Speakers
Discover how organisations are moving AI from strategy into the day-to-day realities of risk, compliance, resilience and cybersecurity. This panel will explore how AI can help connect GRC functions, streamline processes, strengthen controls and identify emerging risks, while ensuring that governance and human judgement remain at the centre of decision-making.
9:35 AM - 10:05 AM
Building a Modern Risk & Integrity Ecosystem: Integrating Governance, Policy Management, Learning, Communications, and AI
Speakers
This session would explore how organizations can move beyond traditional policy repositories and compliance programs to create a more connected governance ecosystem that strengthens risk awareness, enables better employee decision-making, and leverages technology and AI responsibly.
10:10 AM - 10:40 AM
From UX to AI: What's New Across MetricStream's Risk & Compliance Suite
Speakers
This session takes you inside the most significant enhancements across MetricStream's Risk and Regulatory Compliance suites. We'll cover the Euphrates UX uplift — delivering a cleaner, more intuitive experience — alongside a range of new functional features that give risk and compliance teams greater control and visibility. And at the heart of it all: AI. Discover how MetricStream's latest AI capabilities are helping teams cut through complexity, reduce manual effort, and stay ahead of risk and regulatory change — faster and with greater confidence. A practical, product-focused session built for professionals who want to see real capability, not just concepts.
10:45 AM - 11:45 AM
AI Architecture for GRC
Speakers
Explore how to design an effective AI architecture for GRC by creating shared context across obligations, evidence, controls, assessments, issues, and prior decisions. Discover why isolated AI agents can create more noise rather than meaningful outcomes, and how traceability, governance by design, and user-centric interaction models can help GRC professionals and frontline owners make better decisions, streamline processes, and drive practical business value. The session will examine the key architectural considerations, design trade-offs, and challenges involved in making AI in GRC effective, transparent, and accountable.
11:15 AM - 11:30 AM
Final Reflections: What to Expect in 2027
Speakers
Why Attend?
Transform your GRC strategy
AI-Native Risk Intelligence for Confident Decisions
Continuous Compliance Powered by Automation
Proactive, AI-Driven Assurance for Agile Audits
U.S. Regulatory Readiness: SOX, NIST CSF 2.0 & State Privacy Law
One Unified View Across Cyber, Risk & Compliance
Past Attendees
Attendee Snapshot
Connect with decision-makers across industry and seniority
Audience by Industry
Industry representation breakdown
Audience by Seniority
Leadership & decision-maker roles
The Future of GRC, Built for How Work Happens Today

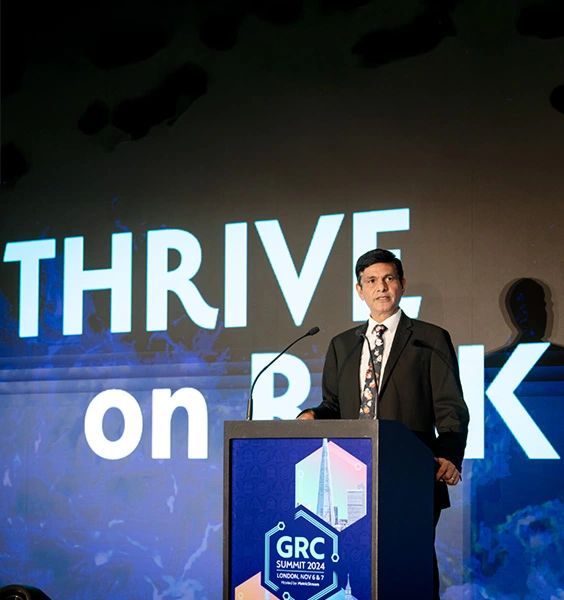
Now in its 14th year, the GRC Summit is the industry's premier gathering for governance, risk, compliance, and cyber leaders. This year, AI runs through every session, from agentic workflows to autonomous assurance, as organizations work out scaling AI in GRC adoption in 2026.
Two focused half-day mornings replace the usual multi-day commitment. With no travel or full days away from your team, you get to focus on the sessions that matter.
Reserve Your Free Seat Now.
Past Summits
Agenda & Sessions
7:30–11:00 AM Pacific / 10:30 AM–2:00 PM Eastern, both days. Sessions run 40 minutes with a 5-minute break in between.
| Time | Slot | Title |
|---|---|---|
| 7:30 AM – 8:10 AM PT | Opening keynote | Orchestrating the Future of GRC with Connected Intelligence |
| 8:15 AM – 8:55 AM PT | Product Keynote | Beyond the Risk Register: AI and Connected GRC for Continuous Resilience |
| 9:00 AM – 9:35 AM PT | Case Study | From Reactive to Resilient: GRC Transformation in Action |
| 9:35 AM – 10:15 AM PT | CXO Panel | How AI Is Transforming the Roles of Chief Risk, Audit & Compliance Officers |
| 10:20 AM – 11:10 AM PT | Expert Talk | Agentic AI in GRC: From Novelty to Strategic Business Advantage |
| Time | Slot | Title |
|---|---|---|
| 7:30 AM – 8:10 AM PT | Opening Keynote | External Keynote & Fireside Chat |
| 8:15 AM – 8:55 AM PT | Panel | The AI Way to Build an Enterprise GRC Program That Works on the Ground |
| 9:00 AM – 9:30 AM PT | Case Study | Inside a Real GRC Transformation: Lessons from the Field |
| 9:35 AM – 10:15 AM PT | Panel | AI-Powered Risk, Compliance & Cyber Resilience: Enterprise Strategies for Financial Institutions in 2027 |
| 10:20 AM – 10:50 AM PT | Product Session | AI Architecture for GRC |
| 10:50 AM – 11:00 AM PT | Closing Keynote | From Insight to Action: Closing Reflections |