Enterprise GRC Solution
Agentic Enterprise GRC for Continuous Intelligence, Governed Decisions, and Action
Stop using multiple GRC tools and spreadsheets. Get one connected system that automates risk and compliance work with AI Assistants and Agents.
GRC Assistants
Get instant answers, navigate directly to relevant workflows with domain specific assistants.
GRC Agents
Purpose-built agents assess risks, test controls, gather evidence, identify gaps, and recommend actions.
Agent Ecosystem
Build your own or deploy purpose-built agents by MetricStream and partners.
Measurable Impact of Smarter Enterprise GRC
133
modeled return on investment over three years
$8.4M
in three-year, risk-adjusted present-value benefits
$2.3M
saved by moving to MetricStream GRC
Source: The Total Economic Impact™ of MetricStream Enterprise GRC and MetricStream Business Value Calculator.
Amplifying Outcomes for the Modern Enterprise
Modern Enterprise GRC Software Built on One Intelligent Foundation, Ready for Every Decision
Contextual Intelligence Fabric Connecting GRC Data Elements
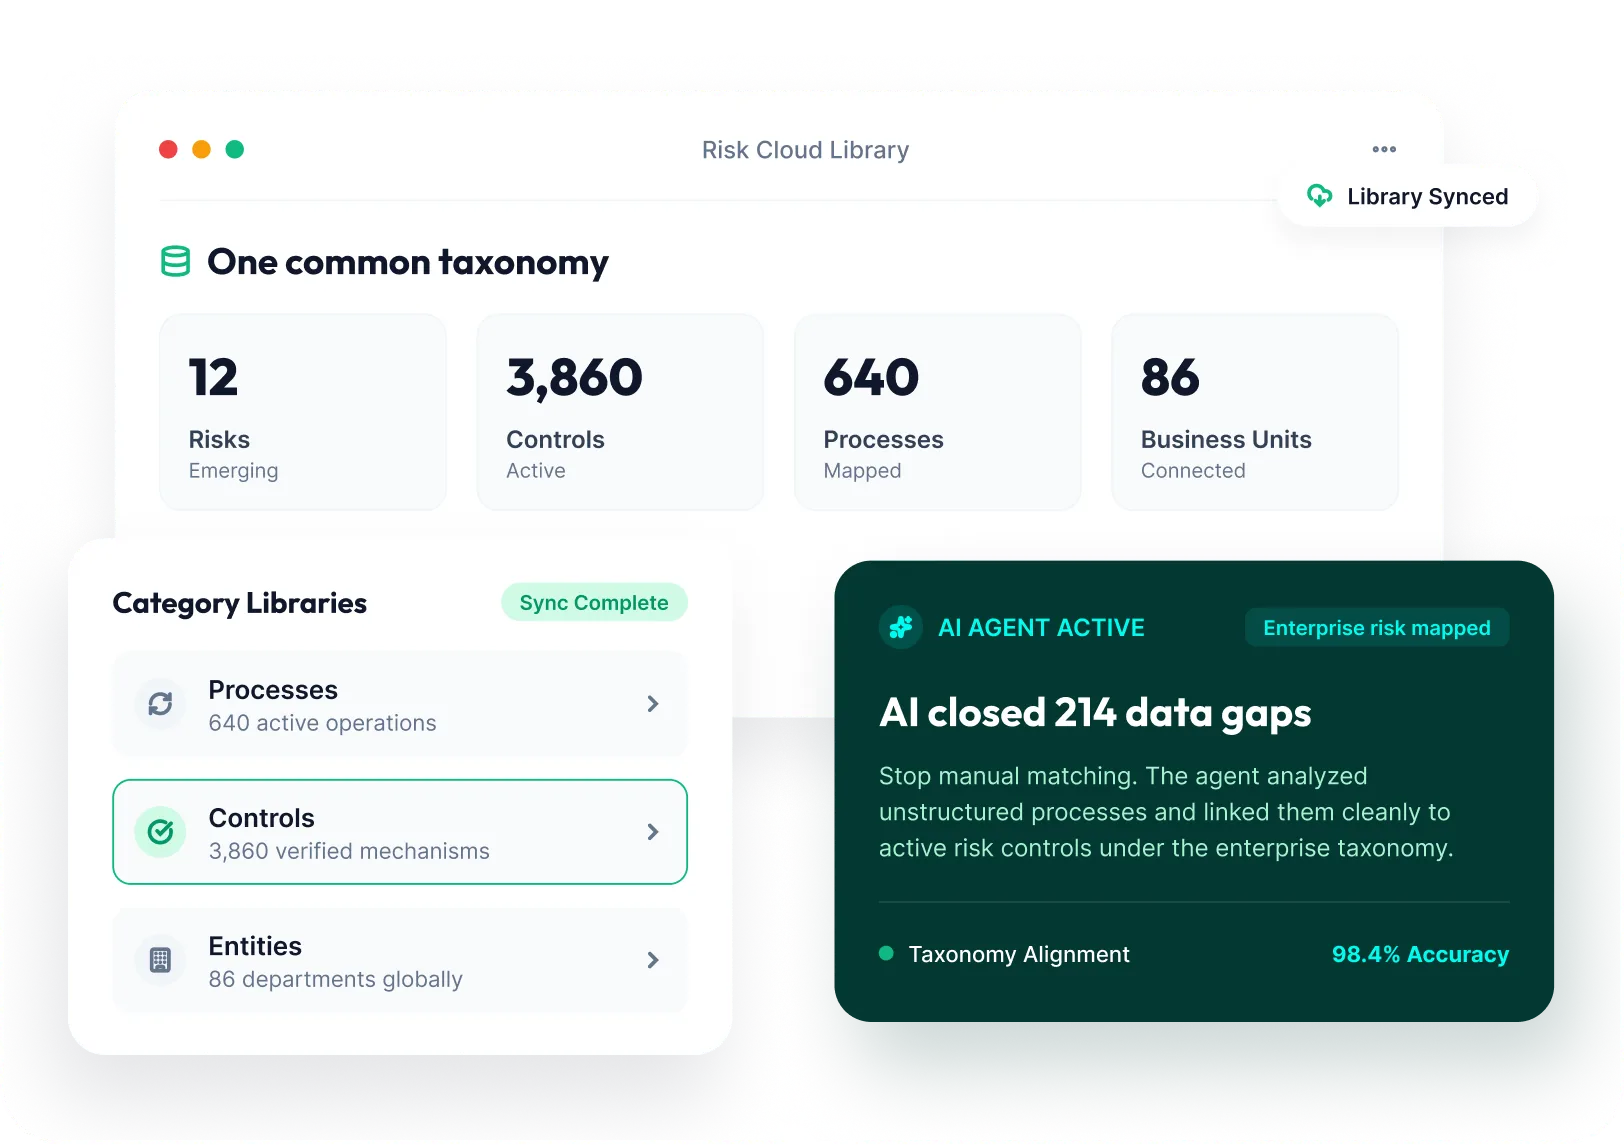
GRC software needs a connected data model. A federated data model links every entity in a many-to-many fashion, so a single risk, control, obligation, or asset stays connected to every process, policy, audit, and third party it touches, giving you one true, connected view of the organization instead of siloed records.
Zero Blind Spots With One Connected View of Enterprise and Operational Risk
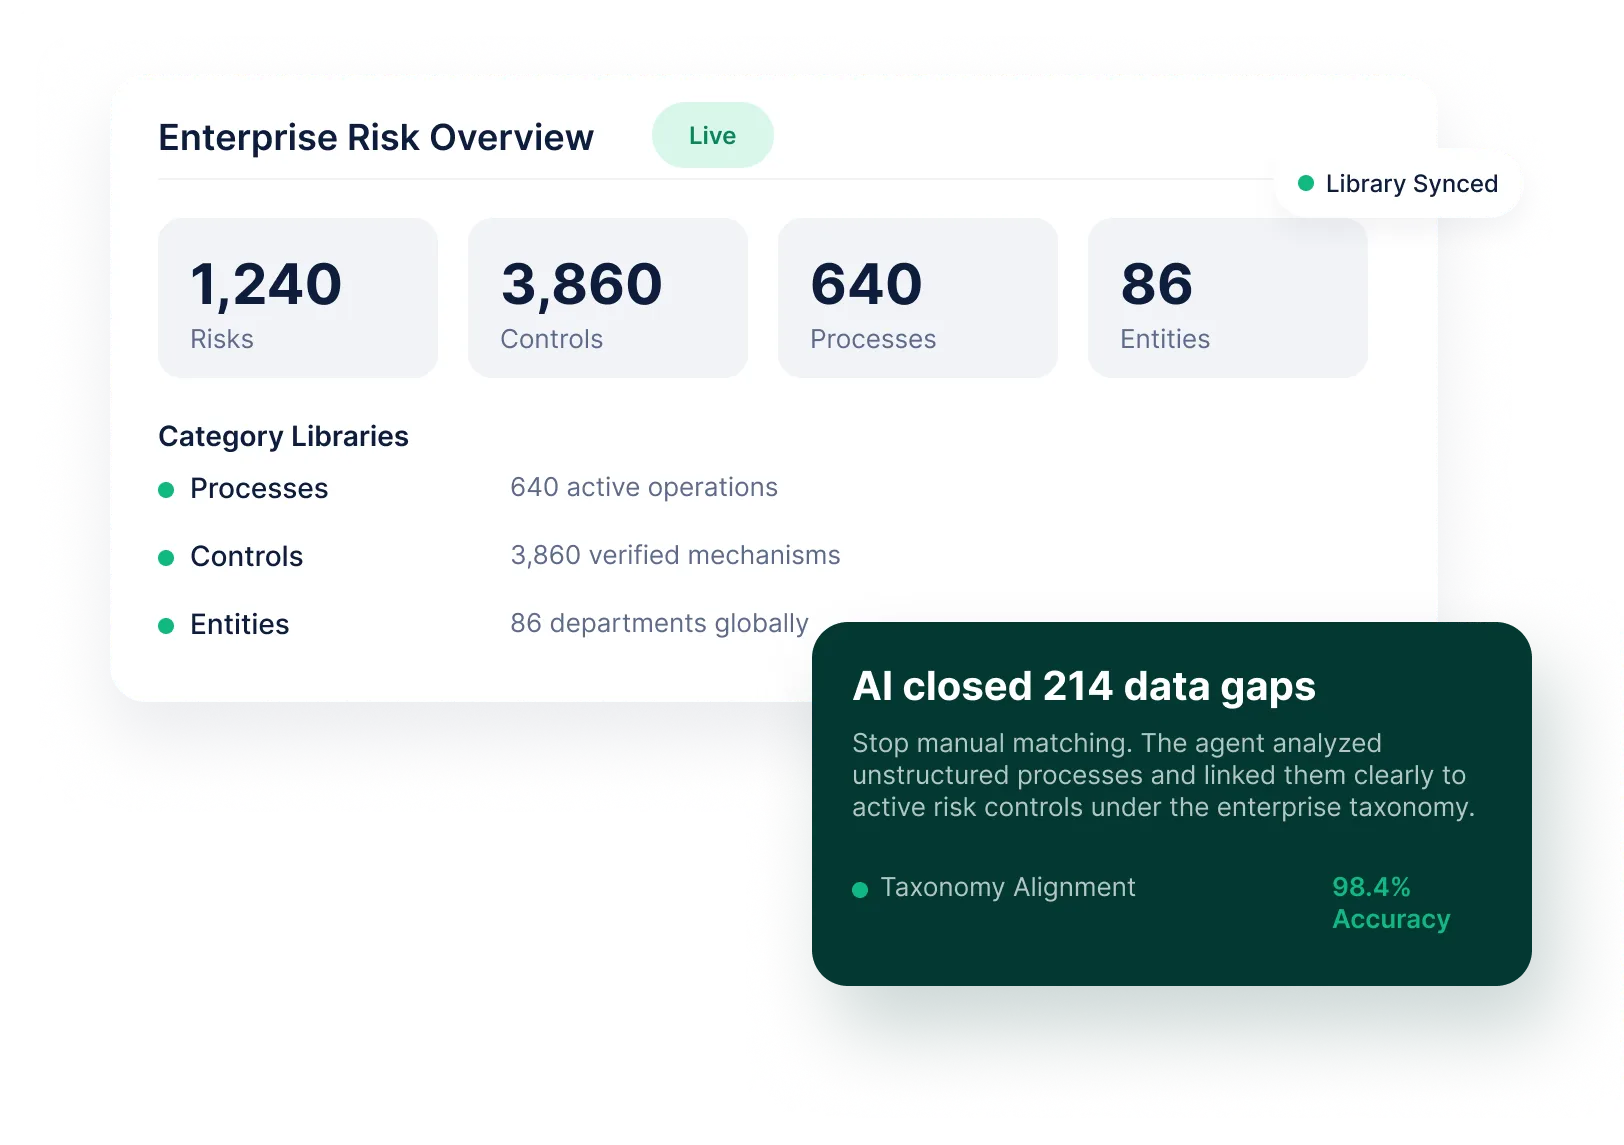
Enterprise and operational risk no longer sits in silos and spreadsheets. Centralize risks and controls and map it to organizational entities in , Risk Assistant and Agents performing automated assessments, control testing, and KRI tracking against risk thresholds and exposure. Capture issues and actions across the risk management lifecycle, and get AI-generated risk narratives for board-ready visibility.
Continuous Policy and Compliance as Regulations Evolve
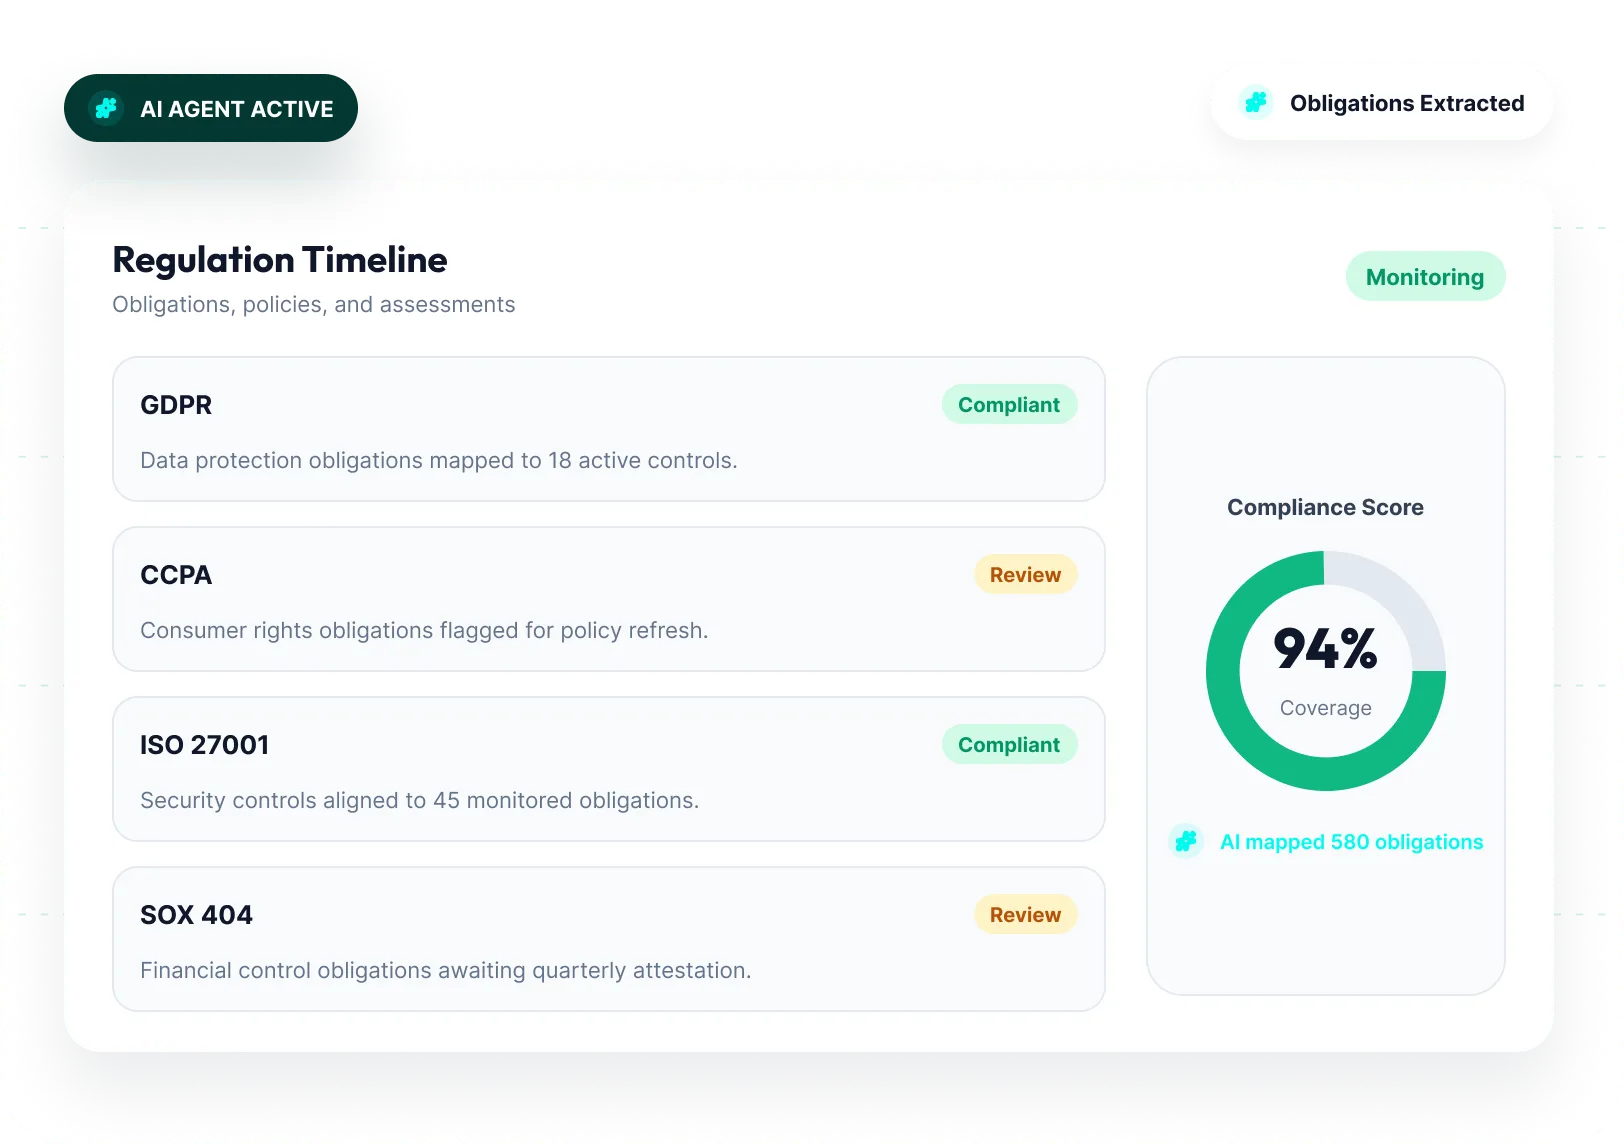
Stay on top of regulations and obligations with AI assistants and agents continuously monitoring and mapping them to relevant controls, policies, assessments, tests, evidence, and issues in a single connected solution. Compliance Agents extract obligations, flag control gaps, and recommend remediation as requirements change. Policy Assistant gives your teams source-cited answers, while agents track conflicts and connect policies to risk.
Cyber Resilience Through Real-Time Visibility into Cyber and IT Risk, Compliance
Get complete visibility into your cyber risk and compliance exposure across your enterprise by connecting security signals, assets, , regulations, standards, cyber controls, and policies in a centralized, intelligent repository. Perform risk assessments and control testing continuously, quantify risk in monetary terms to prioritize issues and actions.. Your risk and compliance teams get one real-time view of exposure
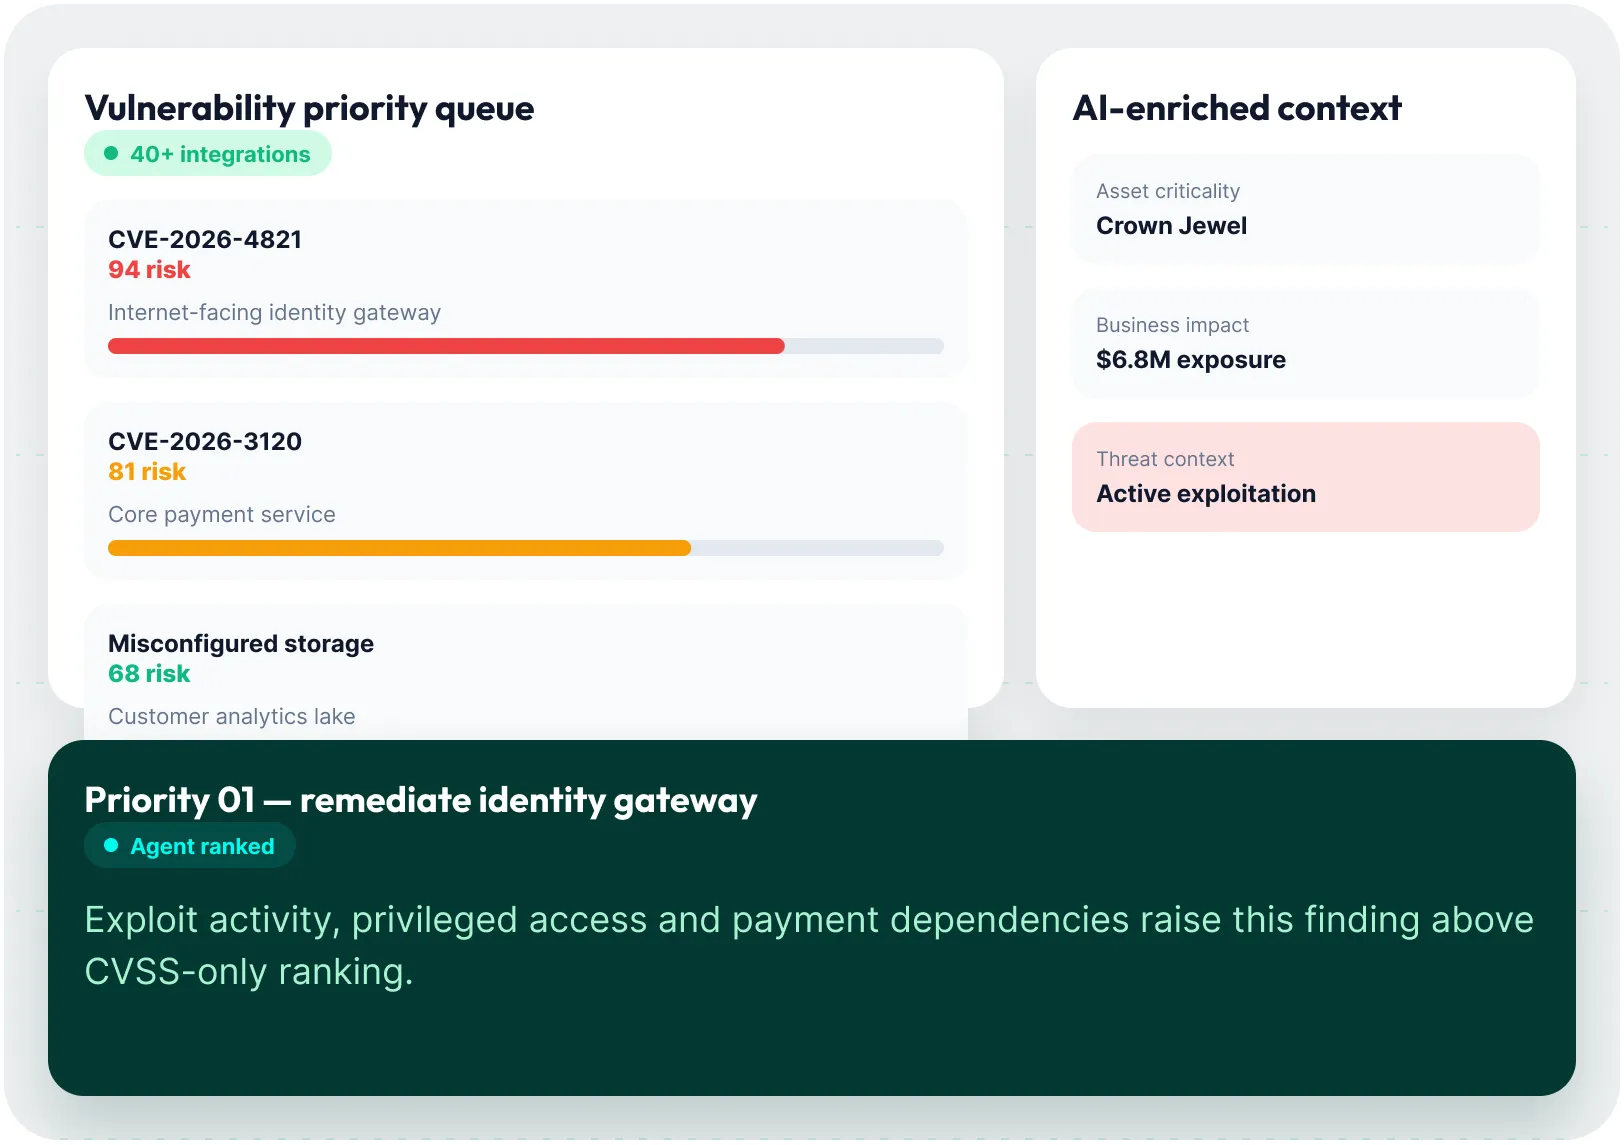
Confident Decisions With Third-Party Risk Assessed and Monitored End to End
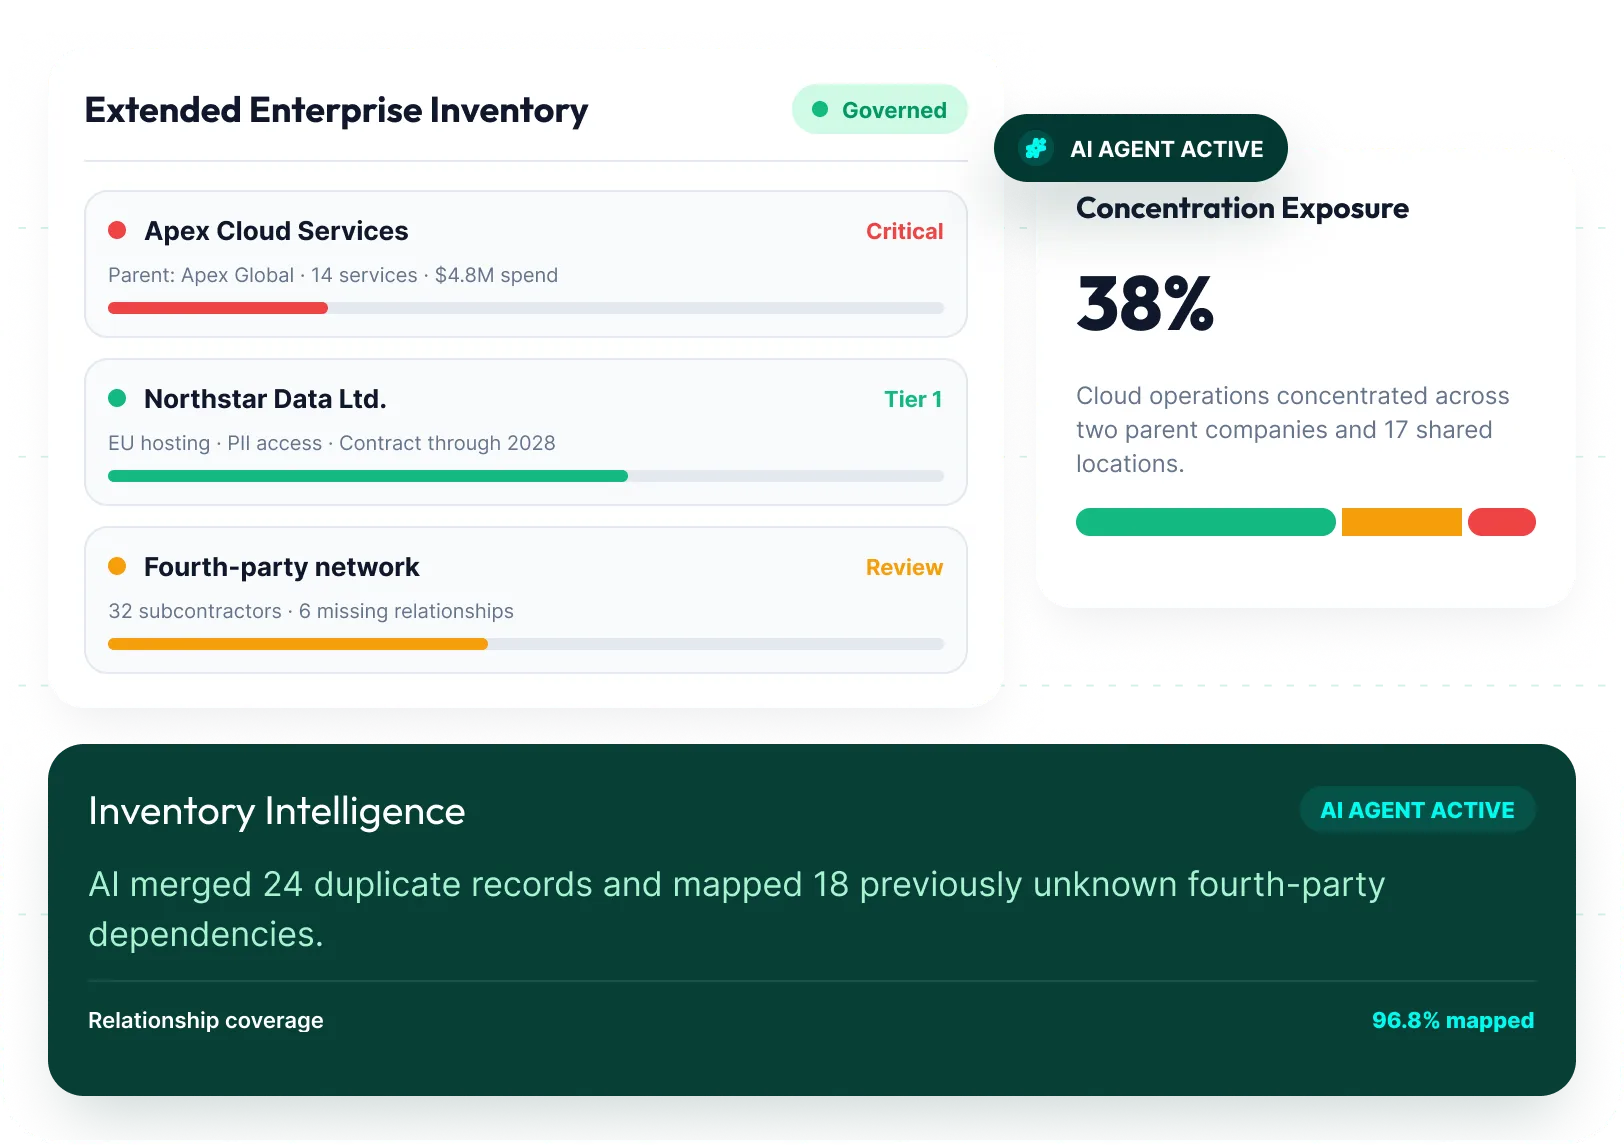
Automate third-party risk management by streamlining assessment and monitoring cyber, financial, compliance, ESG, performance, and resilience risk from onboarding through offboarding. Agents flag emerging vendor risk, prioritize reassessments, and connect findings to contracts and issues. Your extended ecosystem stays protected without slowing the business down.
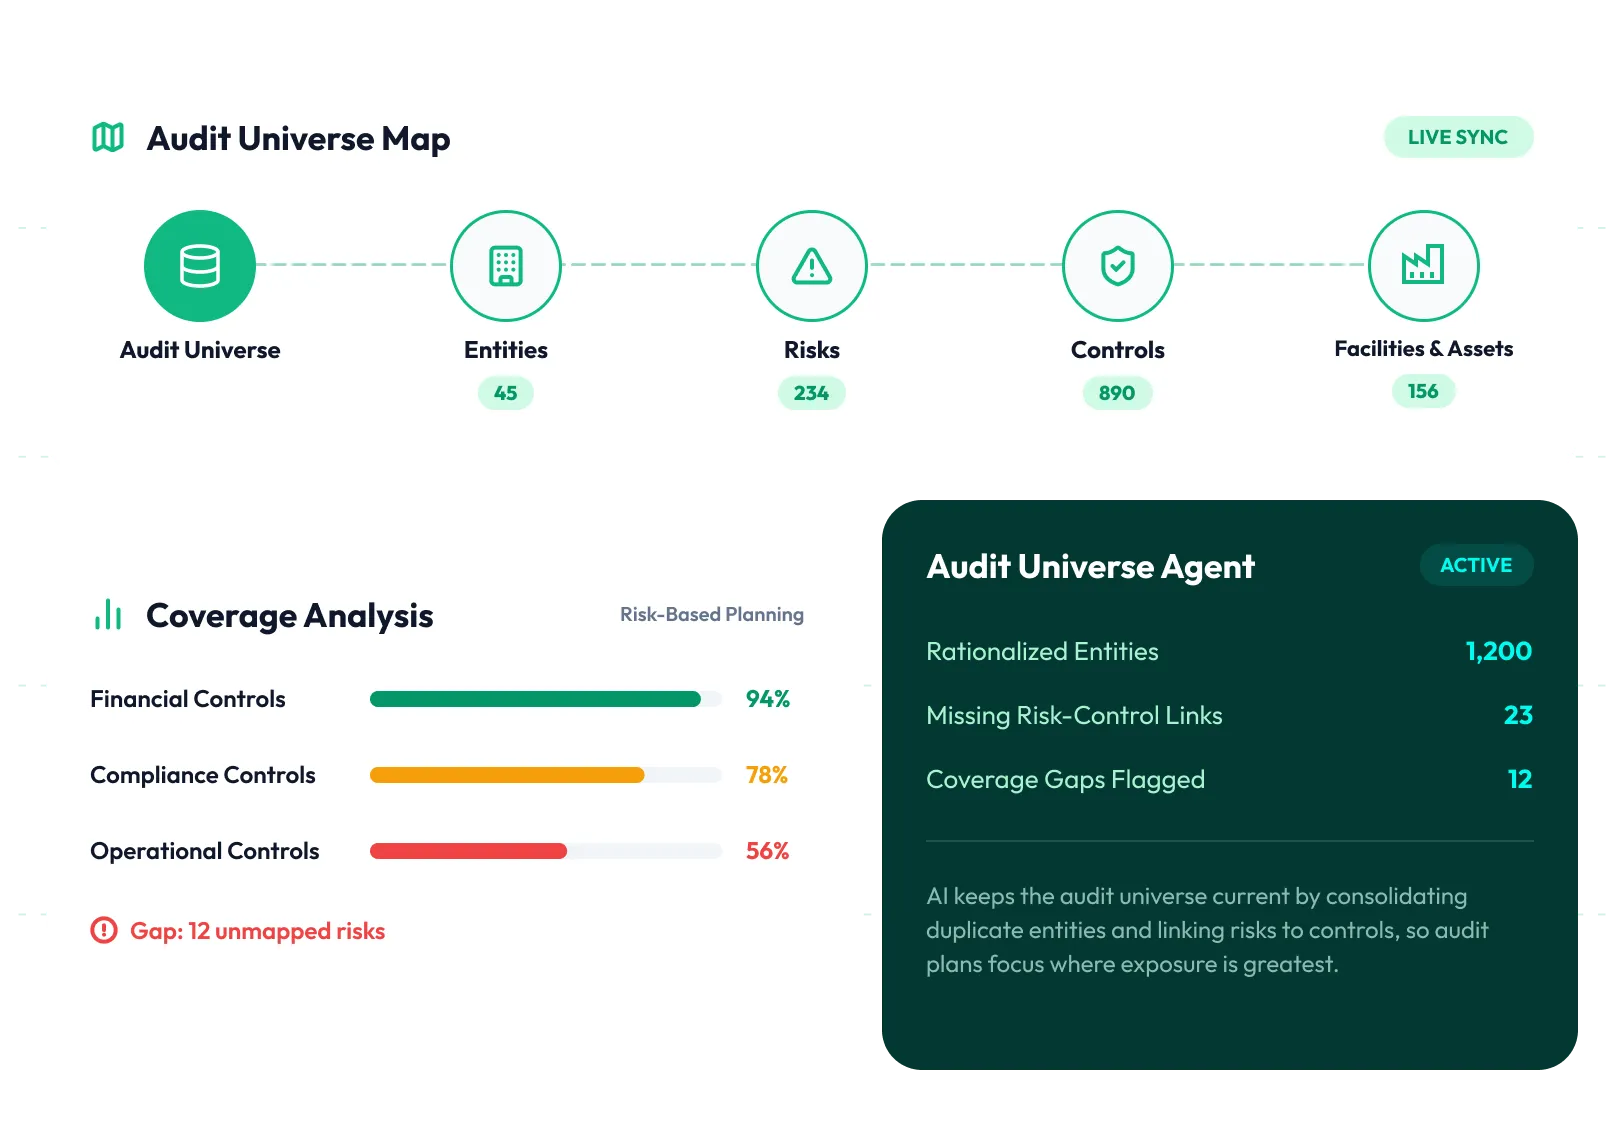
Internal Audit Strengthened With Faster, Risk-Based Reviews
Deliver board-ready assurance with continuous audit intelligence across the audit universe to risks, controls, evidence, testing, and findings. Accelerate planning, fieldwork, evidence review, issue identification, reporting, and follow-up across internal audit and controls using agents and assistants. Your team delivers assurance faster and with greater confidence.
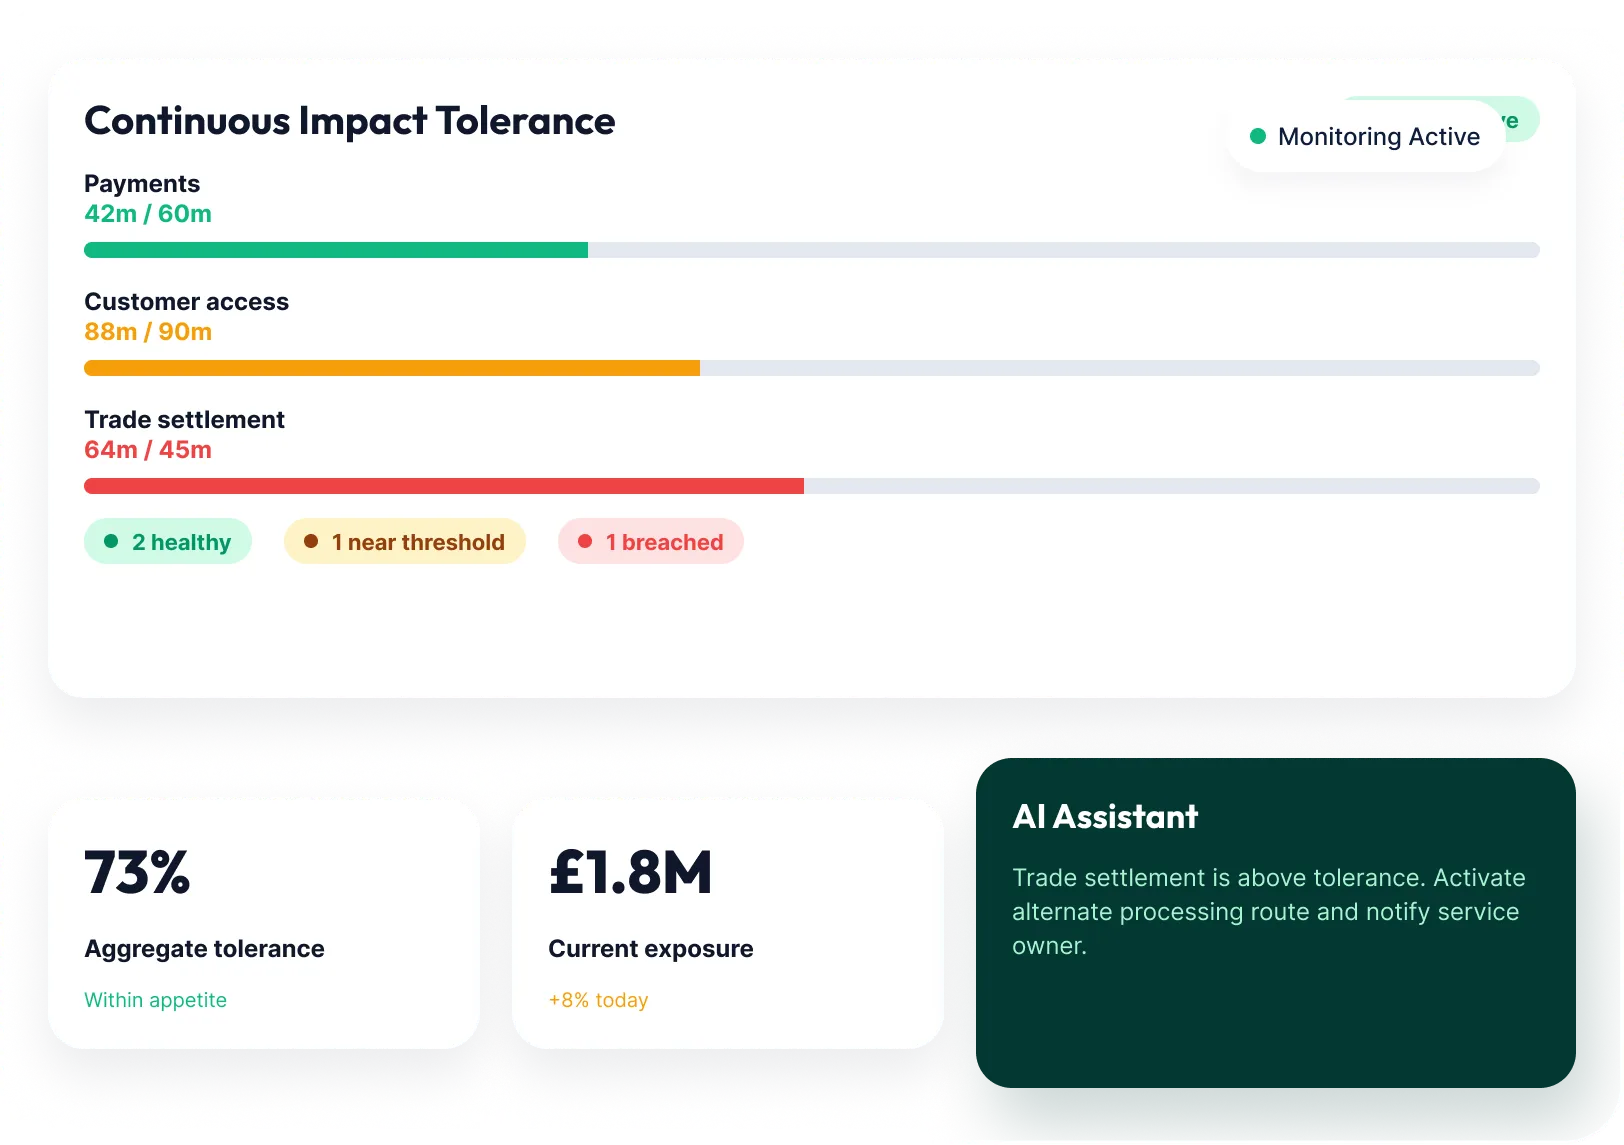
Protect Continuity With Operational Resilience Built to Withstand Disruption
Anticipate disruption, protect operations, and accelerate recovery with real-time intelligence across critical services, processes, assets, people, facilities, and third parties. Impact assessments, scenario tests, continuity plans, crisis coordination, and recovery workflows run on one platform. Your business keeps operating and recovers faster when disruption strikes.
Traditional GRC Software vs. MetricStream’s AI-Powered Solution
Embraced by the Business. Trusted by the Board. Aligned with Auditor and Regulator Expectations.
-
Deep-Domain Products
Purpose-built capabilities across every major GRC function.
-
AI-Native Platform
Federated data, assistants, agents, APIs, security, and model governance.
-
Enterprise-Grade Trust
Citations, traceability, permissions, guardrails, and human accountability.
-
Built to Adapt
Configure workflows, methodologies, taxonomies, reports, and integrations.
-
Proven Global Scale
More than one million users across over 35 countries.
-
Dedicated Experts
GRC and AI specialists support transformation, adoption, and outcomes.
See What MetricStream GRC Could Be Worth to Your Organization
Use our interactive ROI calculator, built by Forrester, to estimate what Enterprise GRC could deliver for your organization. Enter details such as annual revenue, number of GRC tools, and compliance exposure to see your potential savings, payback period, and return on investment.
Calculate My ROIInsights on AI and GRC

Analyst Report
MetricStream Named a Leader in IDC MarketScape 2025 Worldwide GRC Software Report
Download the excerpt to see why MetricStream was recognized as a GRC Leader in 2025.
Download Now
eBook
From Ad Hoc to Intelligent : Accelerating Your Operational Risk Management Maturity Journey with AI
Explore the 4-stage ORM maturity journey from ad hoc processes to AI-powered risk
Read More
Case Study
Global Bank Enhances Business Decision-Making with MetricStream BusinessGRC
Read how a global bank enhanced business decision-making by successfully moving from a traditional approach to a single, connected GRC system.
Read More
Whitepaper
Unlocking AI Value in GRC
Learn how GRC leaders are adopting AI responsibly and proving measurable ROI at scale.
Read MoreEnterprise GRC Solution FAQs
GRC (Governance, Risk, and Compliance) software provides a unified framework for managing an organization's governance structures, risk management programs, and compliance obligations. Organizations need GRC software because the volume and complexity of risks, regulations, and audit requirements have grown beyond what manual, spreadsheet-based approaches can effectively manage. GRC software automates key workflows, provides real-time visibility across the organization's risk and compliance posture, and enables better-informed decision-making at every level.
MetricStream's AI-first GRC solution replaces fragmented, manual approaches—spreadsheets, emails, and siloed tools—with a unified, AI-powered system where risk, compliance, audit, cyber, third-party, and resilience programs share a common data model. Automated workflows eliminate repetitive manual tasks, real-time dashboards replace periodic reporting cycles, and AI capabilities accelerate issue identification and remediation. This integrated approach reduces the cost of GRC operations and improves the quality and timeliness of risk and compliance intelligence.
MetricStream's GRC platform covers enterprise risk management, operational risk, IT and cyber risk, compliance management, internal audit, financial controls, SOX compliance, policy management, third-party risk management, business continuity management, operational resilience, and case and incident management. These domains are managed on a single connected platform with shared libraries of risks, controls, regulations, and processes, enabling organizations to manage GRC holistically rather than as a collection of separate programs.
MetricStream's GRC platform reduces compliance costs in several ways. It rationalizes controls across multiple regulatory frameworks so that a single control can satisfy requirements from several regulations, reducing the total number of assessments required. Automated workflows eliminate manual compliance activities. AI-powered issue classification reduces triage effort. And a centralized policy portal reduces the time required to create, update, and communicate policies. Customers have reported a 90% reduction in time taken to manage compliance activities and a 39% reduction in expected regulatory losses.
A connected GRC approach links all governance, risk, and compliance data into a single federated data model, ensuring risks, controls, policies, and obligations remain connected to every process and asset. This replaces siloed spreadsheets and disconnected tools, giving organizations a single, unified view rather than fragmented records.
GRC software automates routine GRC work, including risk assessments, control testing, and evidence collection, while providing real-time visibility of risk and compliance across your organization. This reduces manual work, improves decision-making, and helps organizations stay continuously audit-ready for faster and easier compliance reviews.
MetricStream's GRC platform covers enterprise risk management, operational risk, IT and cyber risk, compliance management, internal audit, financial controls, SOX compliance, policy management, third-party risk management, business continuity management, operational resilience, and case and incident management. These domains are managed on a single connected platform with shared libraries of risks, controls, regulations, and processes, enabling organizations to manage GRC holistically rather than as a collection of separate programs.
MetricStream's GRC platform reduces compliance costs in several ways. It rationalizes controls across multiple regulatory frameworks so that a single control can satisfy requirements from several regulations, reducing the total number of assessments required. Automated workflows eliminate manual compliance activities. AI-powered issue classification reduces triage effort. And a centralized policy portal reduces the time required to create, update, and communicate policies. Customers have reported a 90% reduction in time taken to manage compliance activities and a 39% reduction in expected regulatory losses.
MetricStream's GRC platform provides role-based executive dashboards and advanced visualizations that translate GRC data into clear, actionable intelligence for board and C-suite audiences. Dashboards display top risks, compliance status by regulation, audit findings, KRI trends, and cyber risk exposure in financial terms. Automated report generation reduces the time GRC teams spend preparing board materials, and real-time data ensures that executive briefings reflect the organization's current risk and compliance position.
MetricStream's GRC platform is designed to accommodate organizations operating across multiple regulatory jurisdictions by supporting jurisdiction-specific compliance frameworks, multi-entity organizational structures, and localized risk and compliance data. Regulatory intelligence feeds provide updates on regulations across regions, which are automatically mapped to the organization's risks, controls, and policies. Compliance status can be reported at the global, regional, or entity level, giving compliance teams the visibility they need to manage multi-jurisdictional programs efficiently.
AI is embedded throughout MetricStream's GRC platform to automate labor-intensive tasks and improve the quality of risk and compliance intelligence. AI classifies issues, identifies duplicate findings across programs, recommends remediation actions, and monitors Key Risk Indicators for threshold breaches. AI also powers smart policy search, automated audit finding summarization, and continuous threat and vulnerability monitoring. These capabilities free GRC professionals from repetitive manual work so they can focus on higher-value analysis and strategic decision-making.
MetricStream's GRC platform is a low-code/no-code cloud solution trusted by over one million professionals in 35+ countries. Its federated data model and configurable architecture allow it to scale from a single GRC domain—such as internal audit or IT compliance—to a fully integrated enterprise GRC program spanning risk, compliance, audit, cyber, and resilience. Organizations can add modules as their GRC maturity grows without replacing the underlying platform, protecting their technology investment.
MetricStream's GRC platform includes Observation Management capabilities that empower frontline business users to report risks, anomalies, and concerns through intuitive interfaces—including mobile apps, browser plugins, chatbots, and web forms—without requiring formal GRC training. Anonymous reporting options encourage employees to flag sensitive issues, including ethics violations and fraud. AI-powered triage routes observations to the appropriate teams for investigation, ensuring that risk intelligence from the front line reaches decision-makers quickly.
Implementation timelines for MetricStream's GRC platform vary based on the number of modules deployed, organizational complexity, and data migration requirements. MetricStream's low-code/no-code architecture reduces implementation time compared with traditional GRC platforms by allowing organizations to configure workflows, data models, and dashboards without custom development. Organizations typically begin with a prioritized subset of GRC capabilities and expand over time, using MetricStream's GRC Journey framework to guide program maturity development.
Read our detailed GRC software comparison guide.