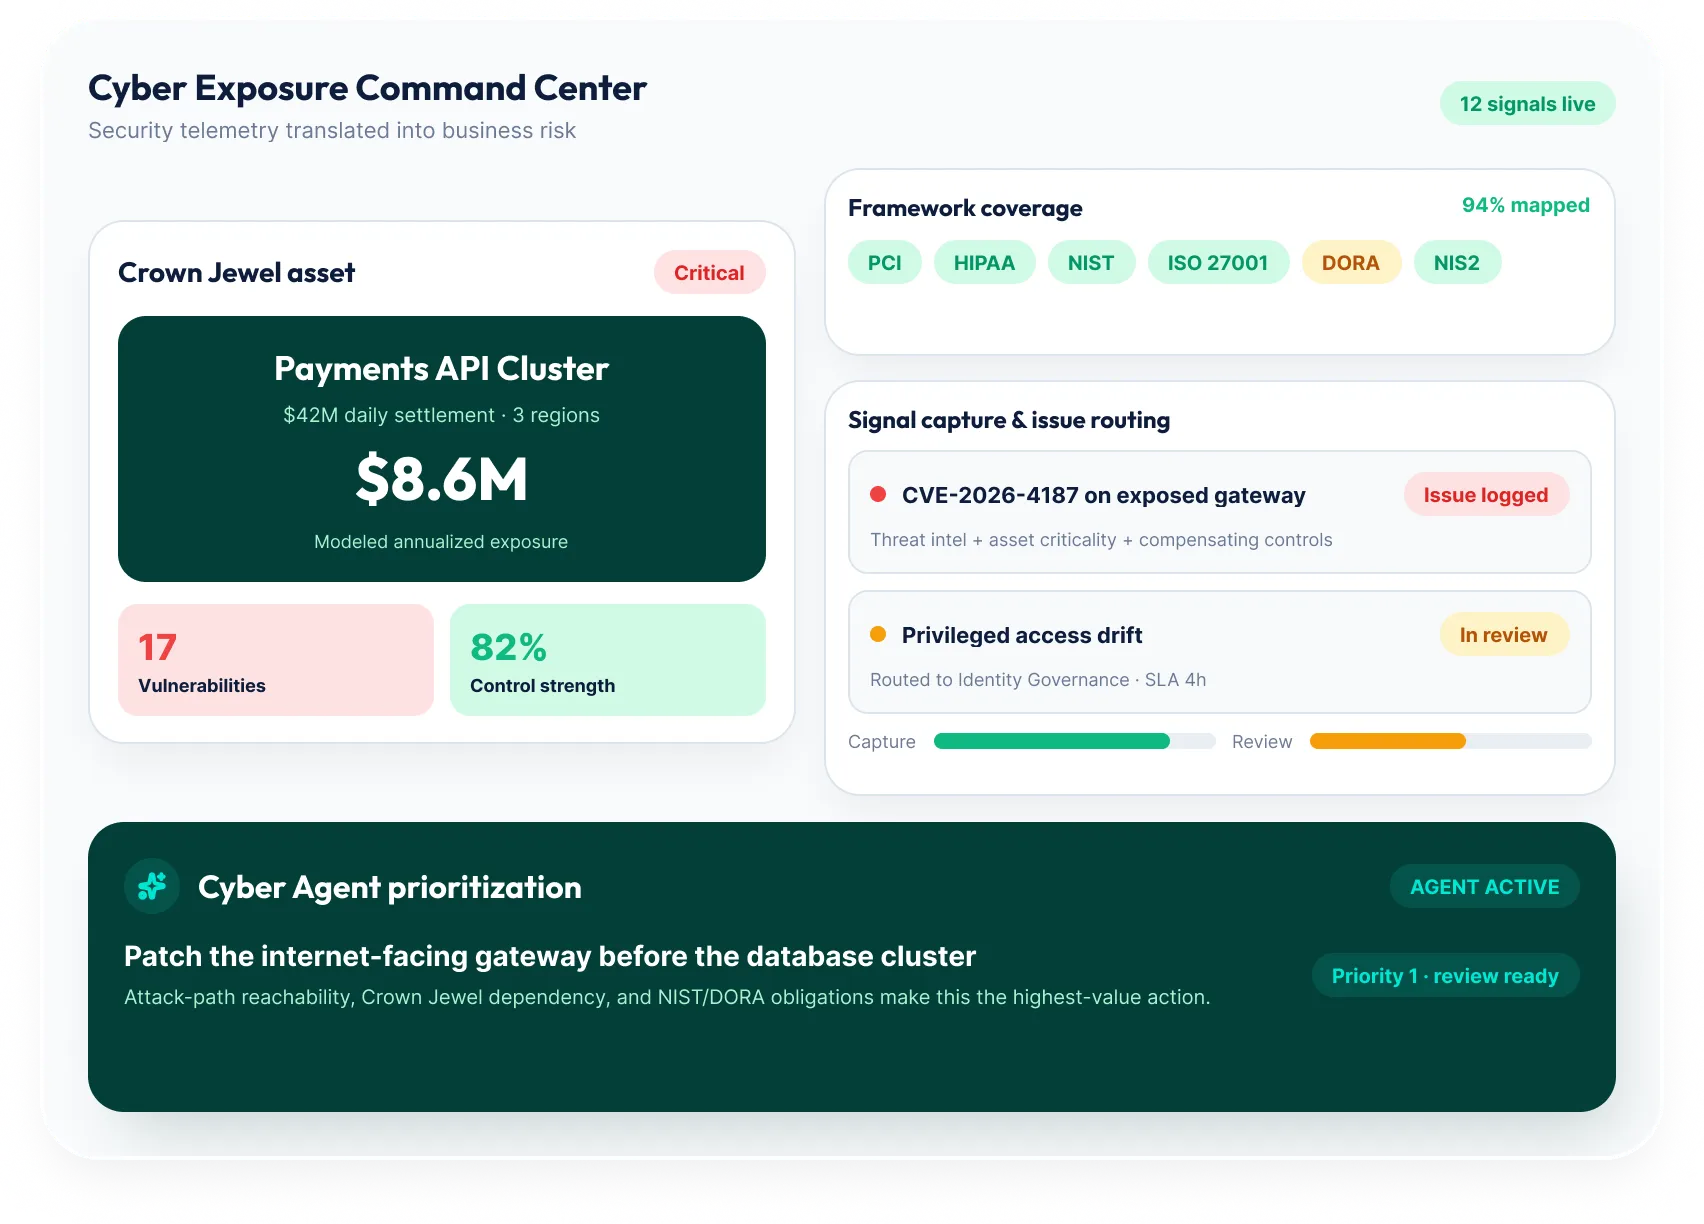
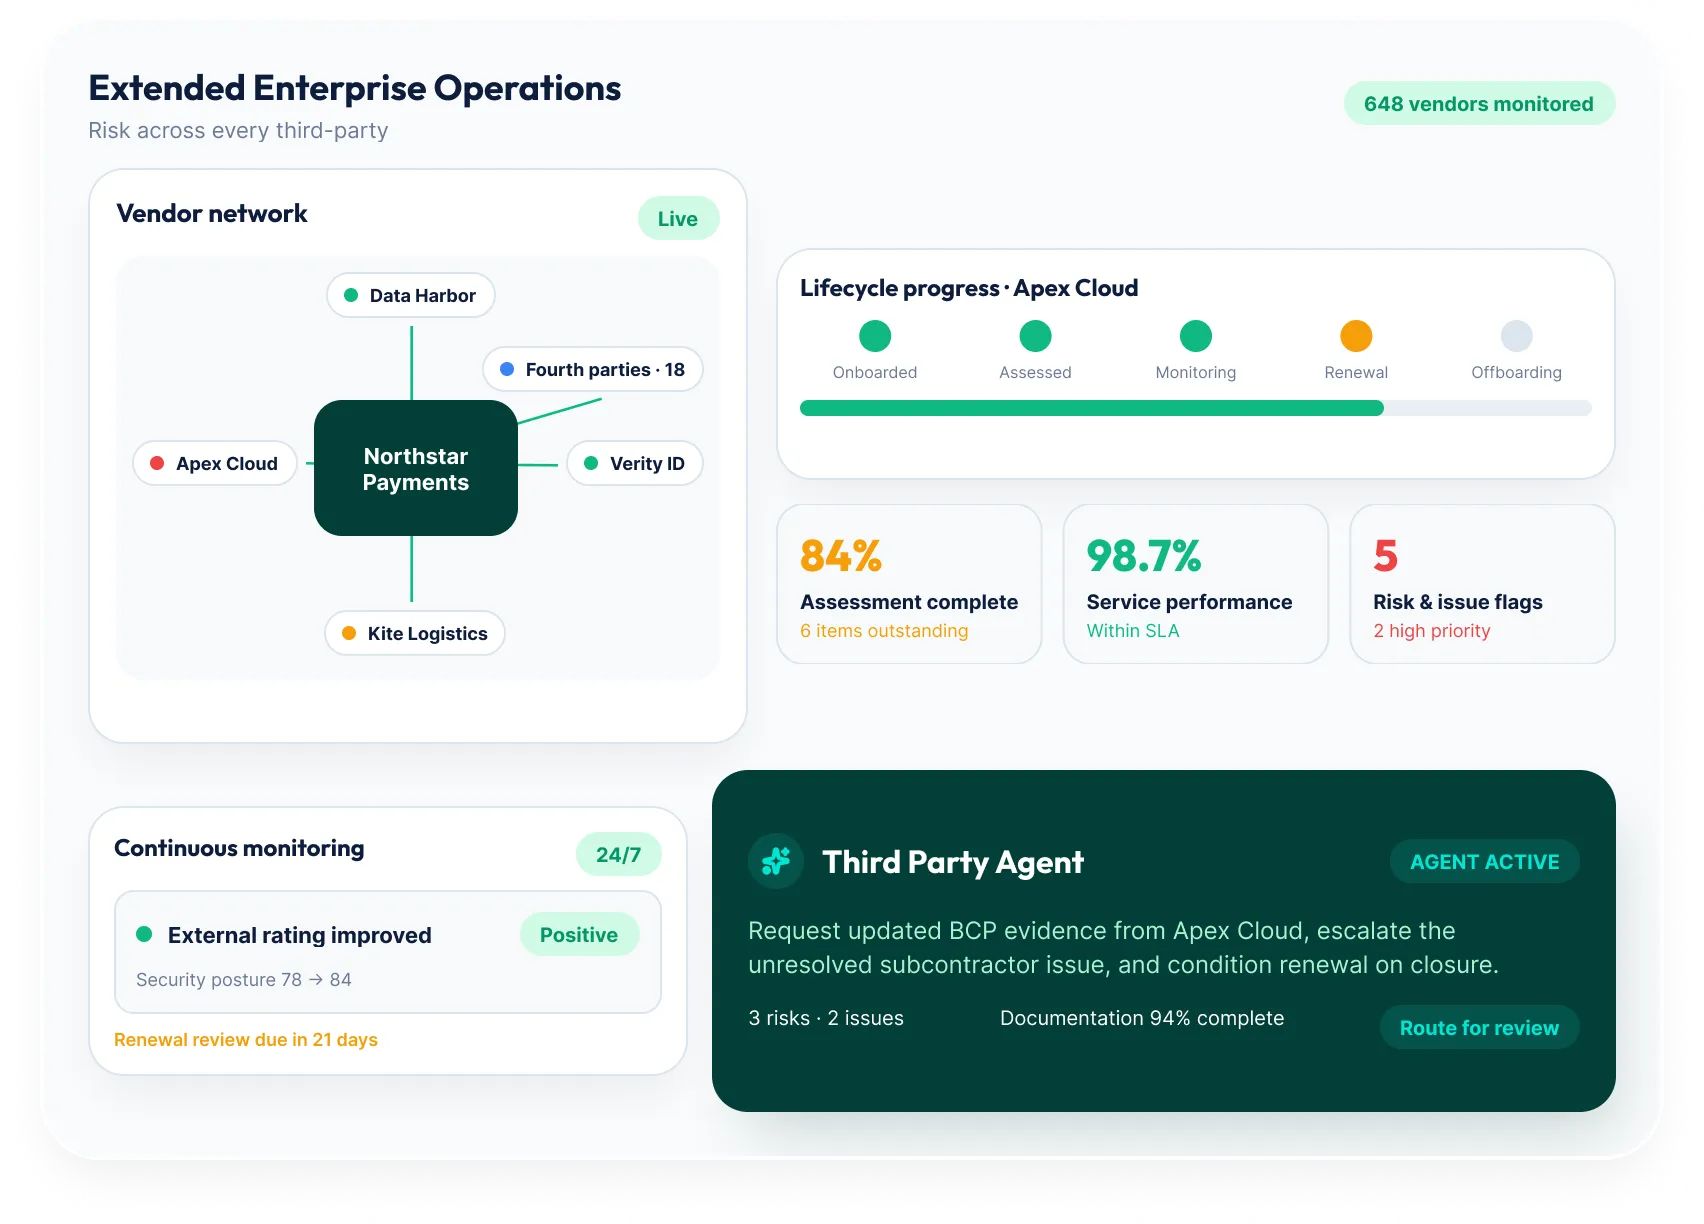
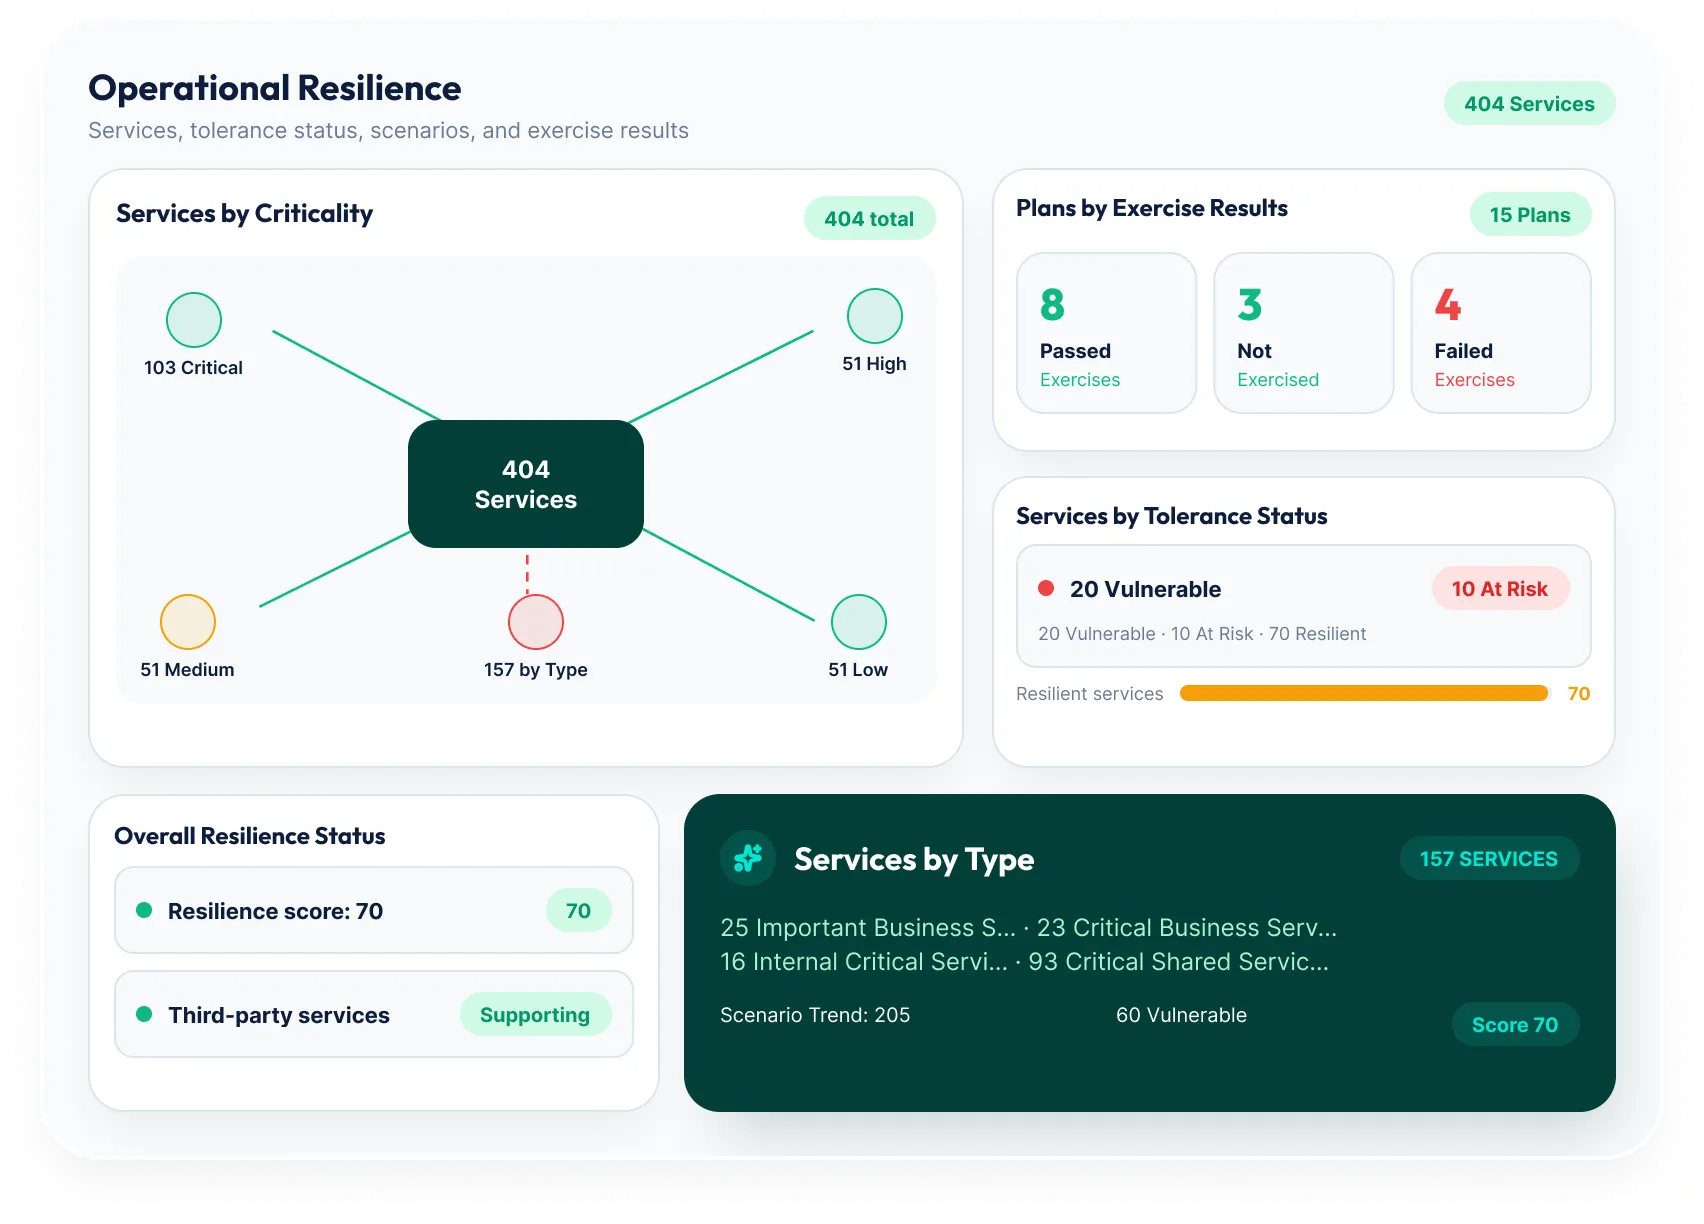
Continuous Sensing
Monitor for emerging risks, compliance violations, control failures, and threat signals — inside and outside the organization — before they escalate.
Transform GRC from periodic, manual checks to continuous oversight.
Monitor for emerging risks, compliance violations, control failures, and threat signals — inside and outside the organization — before they escalate.
Uncover gaps, anomalies, and trends across your risk and control environment. Get fast insights and actionable decisions from narrative summaries and recommendations.
AI Assistants provide guidance, answer questions, and recommend next best actions inside the workflows teams already use.
Automate assessments, gather evidence for controls, and get in-workflow recommendations at the scale manual processes can't match, all while maintaining human oversight.
Know that remediation worked. Validate it with audit closure insights, quality checks, and effectiveness signals.
80%
improvement in risk and control framework-related operational efficiency
85%
reduction in controls and associated costs
66%
reduction in the time taken to complete cyber risk assessments
Source: MetricStream’s Business Value Calculator
Category Leader across all seven GRC categories
Chartis Research, 2026
IDC MarketScape for GRC, 2025
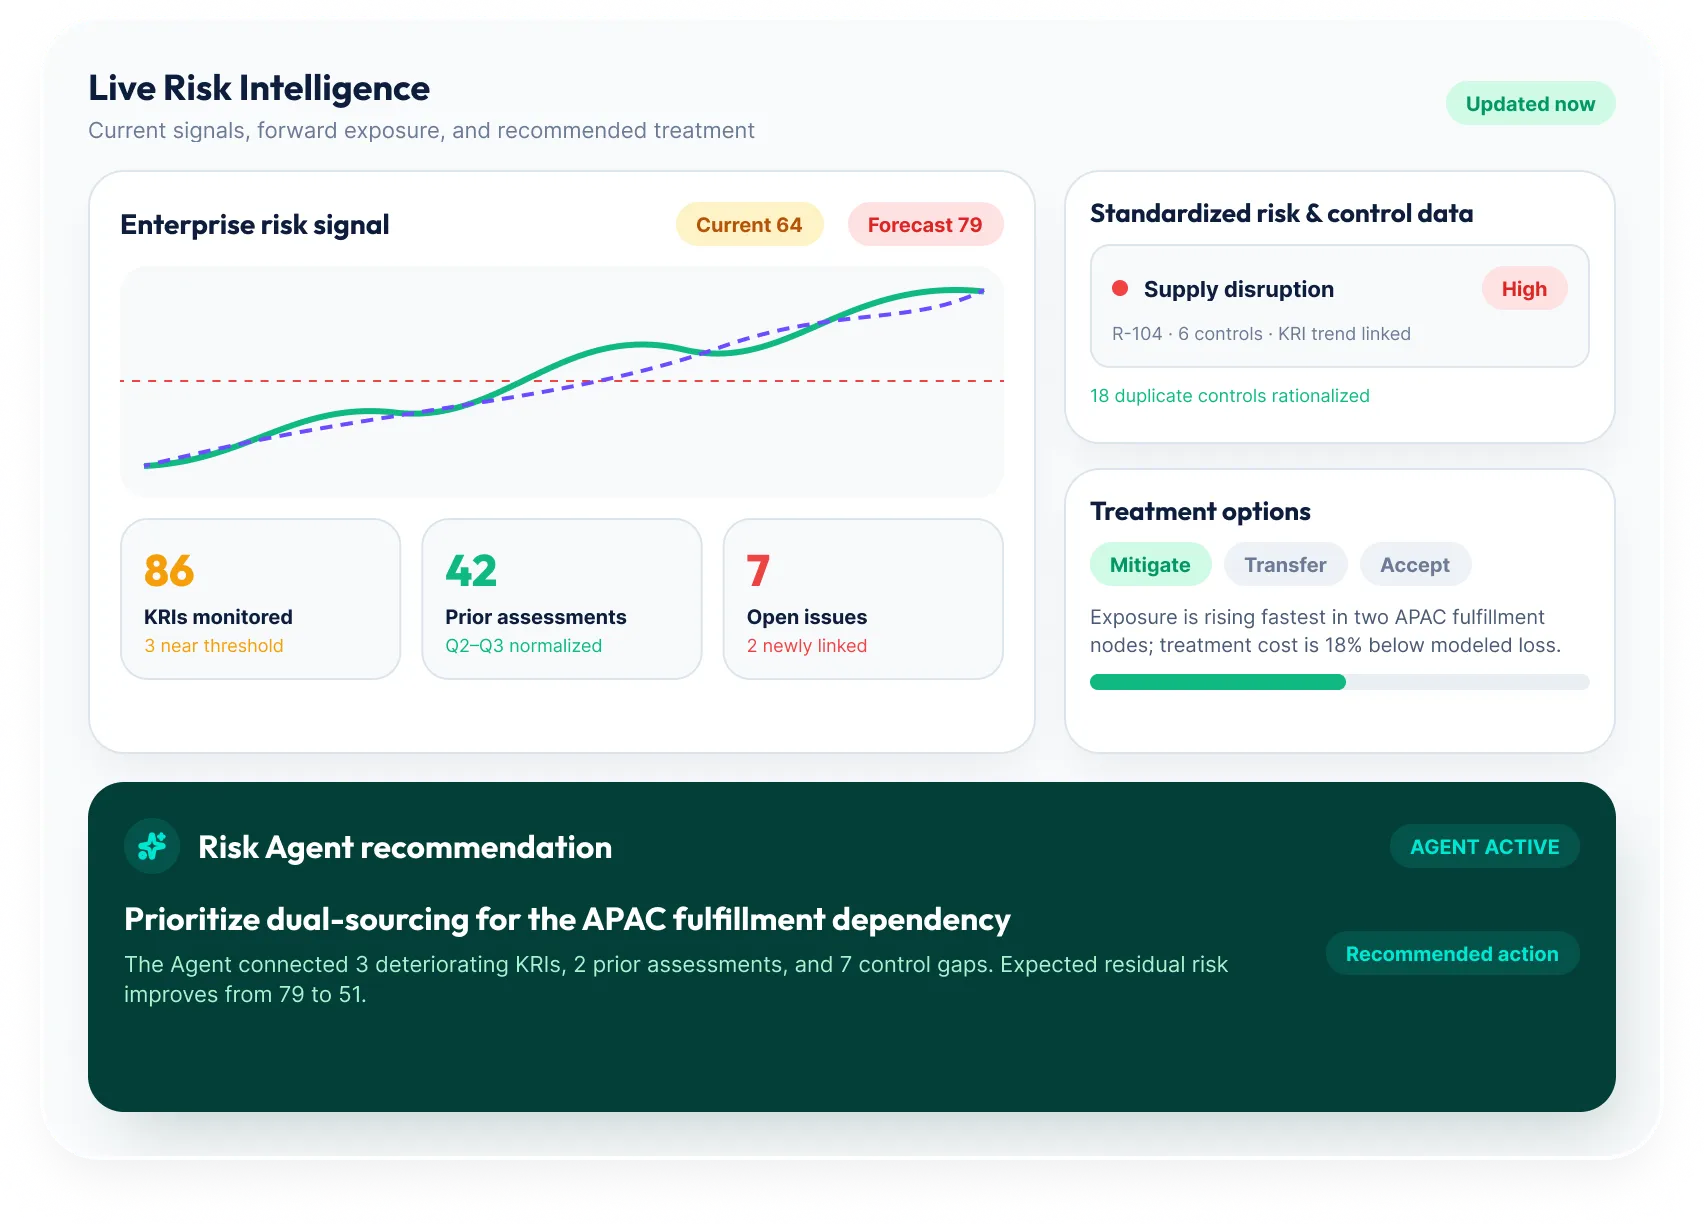
Drive faster action with real-time risk intelligence that gives leaders a current and future view of risk. Risk Assistants and Agents standardize and rationalize risk and control data, pull in prior assessments and KRIs, identify contextual insights, and recommend issues and actions. Take the right risks and choose the right treatment.
GRC Capability
Legacy GRC
MetricStream GRC
Process, Asset, Risk, Compliance, Control, Policy Libraries
Siloed, inconsistent data spread across point solutions
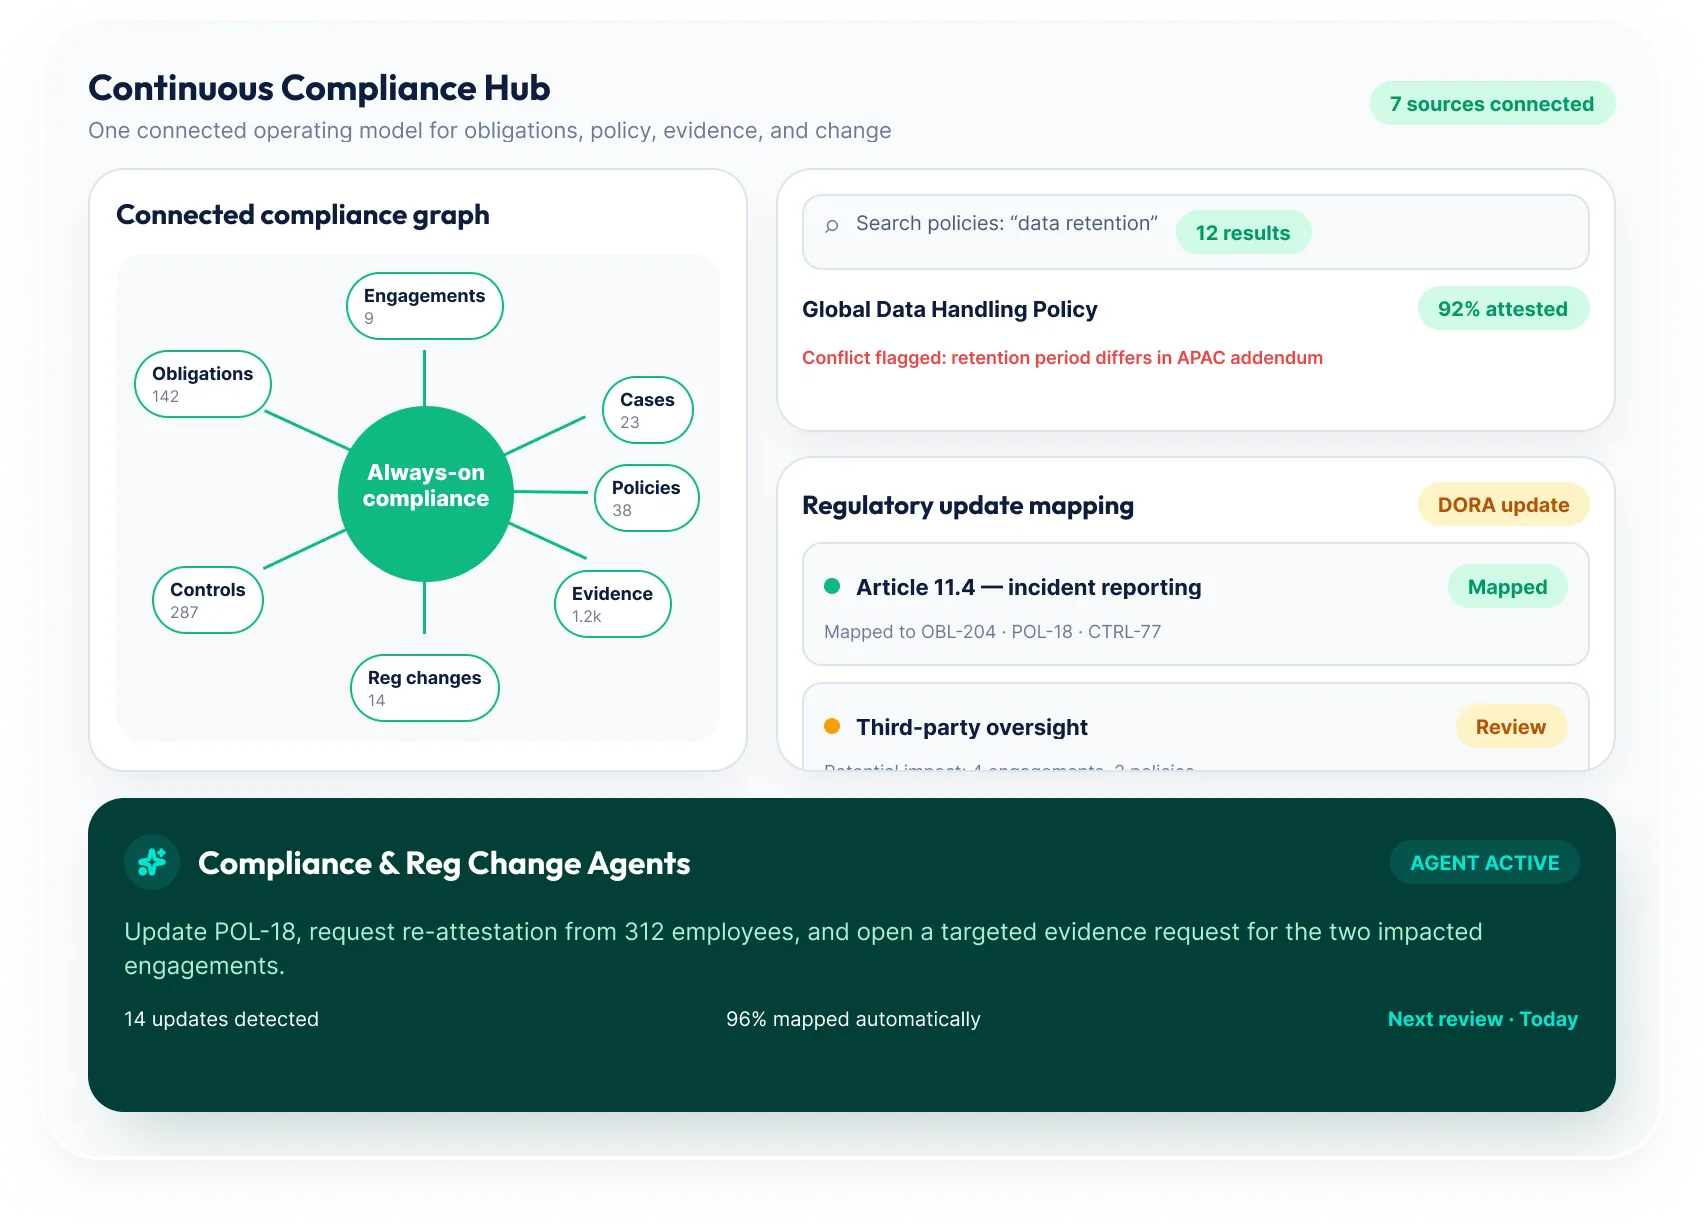
AI standardizes and rationalizes risk and control data on a centralized federated model connecting risks, controls, regulations, policies, and third parties
Regulatory Change Management
Manual monitoring of scattered regulatory sources, delayed impact analysis
AI summarizes updates, assesses applicability, and extracts obligations for immediate action
Risk & Compliance Assessments
Manual, time- consuming, and largely periodic
AI-assisted data capture, contextual recommendations, and agentic workflows
Control Testing & Assurance
Over-testing or under-testing, manual evidence collection
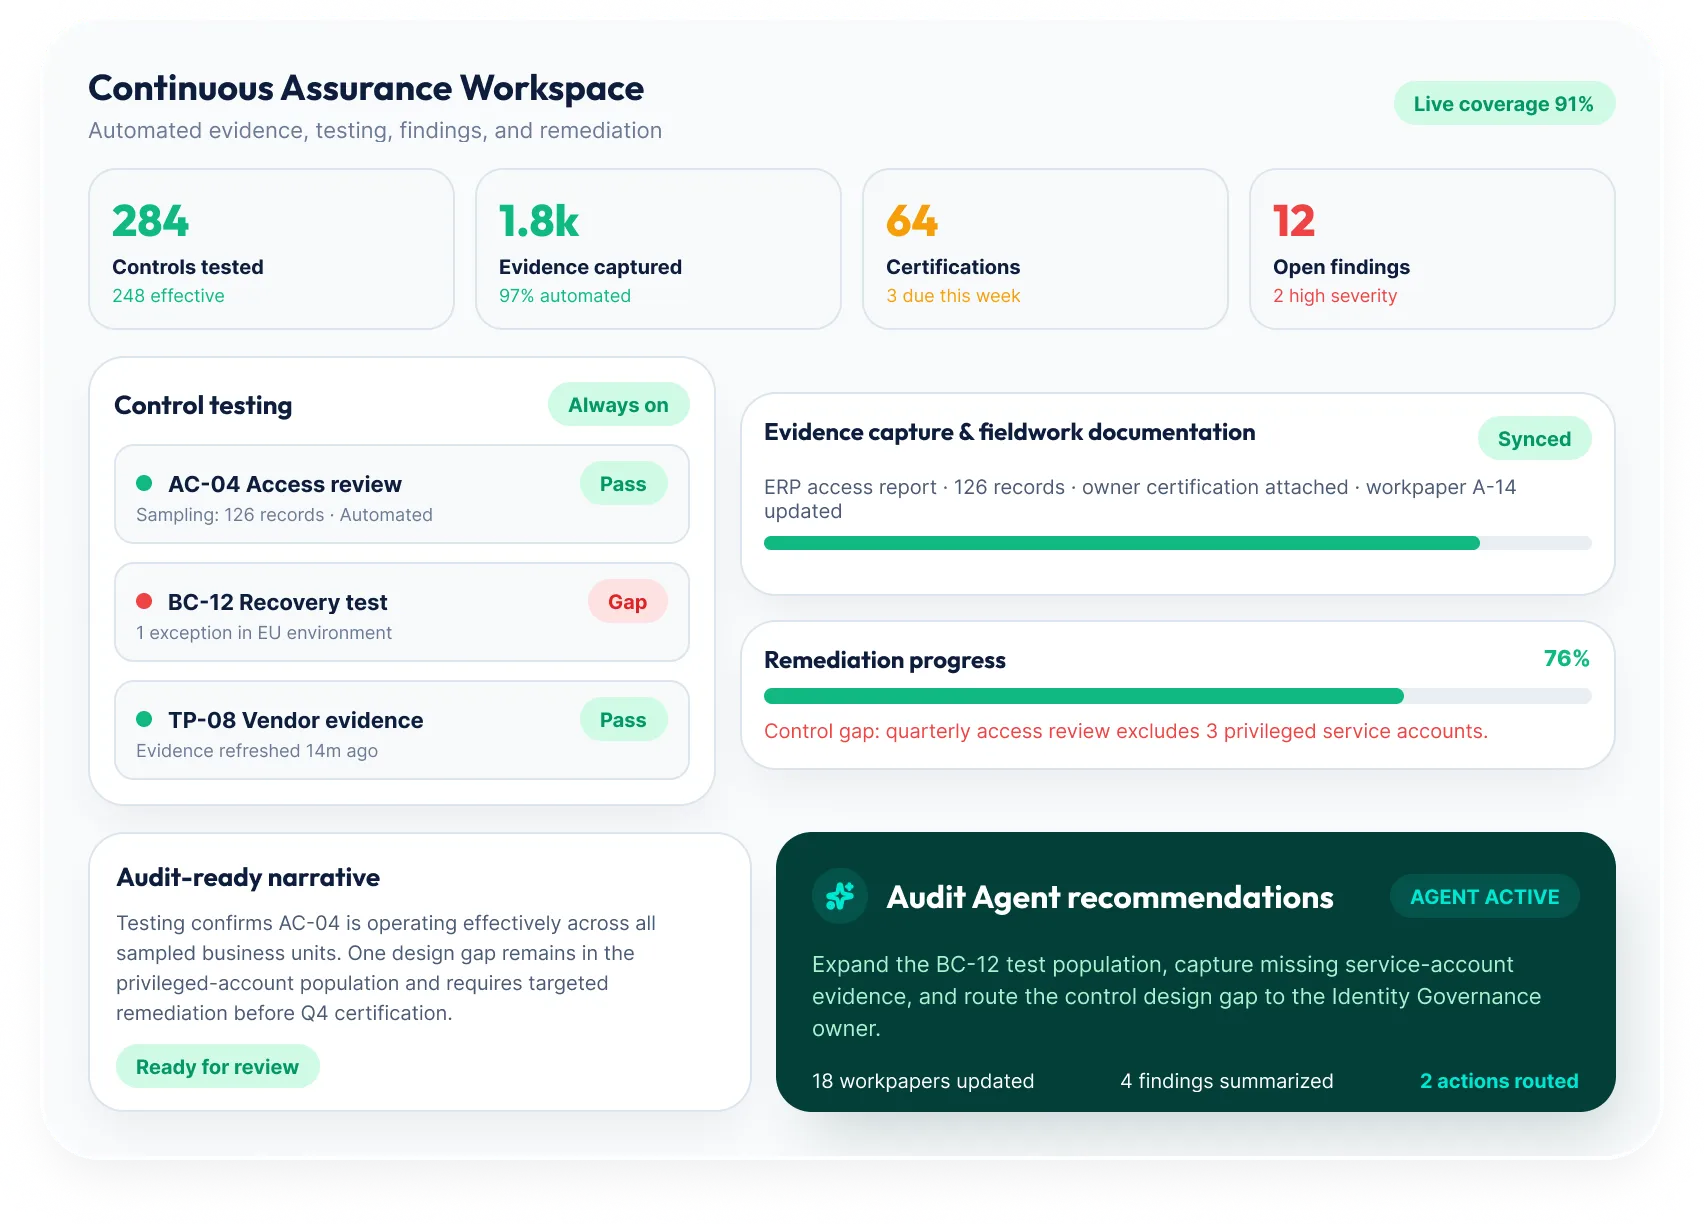
AI rationalizes controls, prioritizes testing based on risk, and accelerates evidence gathering, cutting audit cycle time without sacrificing rigor
Cyber & Third- Party Oversight
Disconnected scanners, questionnaires, and spreadsheets
Connected risk, compliance, and vendor oversight with quantified exposure
Internal Audit & SOX Compliance
Manual audit planning, evidence chasing, and spreadsheet-based fieldwork
AI-assisted planning, automated evidence capture, and audit-ready narratives across audit and SOX cycles
Resilience & Business Continuity
Static continuity plans, disconnected from daily risk and control data
Continuous resilience assessments and automated response plans tied to real-time risk
Issue & Remediation
Reactive reporting and inconsistent follow up
AI clusters related issues, identifies patterns, and recommends remediation
Reporting & Board Intelligence
Static and fragmented reports
Real-time, source-backed intelligence narratives connecting every signal
Use our interactive ROI calculator, built by Forrester, to estimate what Enterprise GRC could deliver for your organization. Enter details such as annual revenue, number of GRC tools, and compliance exposure to see your potential savings, payback period, and return on investment.
Calculate My ROI
A common taxonomy and shared libraries, continuously analyzed and cleaned by AI, form one connected foundation, replacing siloed, overlapping tools and duplicated effort.
Agents catch risk and compliance issues earlier, reducing fines and losses with broader audit, risk, and control coverage.
Assistants and Agents turn data into insights, narratives, and recommendations across risk, compliance, and audit.
Agents automate assessments, testing, and audits, delivering reporting ready for regulators and leadership.
Assistants surface the evidence that assures boards, regulators, and senior management of the program's strength and maturity.
Assistants guide adoption, driving uptake across the business with collaboration across teams and regions.
MetricStream's approach to governance, risk, and compliance replaces periodic, manual reviews with continuous, AI-powered sensing, intelligence, and action enabling risk, compliance, audit, cyber, and third-party data to update and inform decisions in real time.
Traditional GRC relies on siloed data, manual assessments, and static reports. MetricStream GRC connects that data on a single federated platform and layers in AI Assistants and Agents that detect emerging risks, recommend actions, and automatically execute defined tasks, while keeping humans in control of every consequential decision.
Assistants provide in-workflow guidance, includinganswering questions, explaining fields, and helping teams capture data faster. Agents go further, acting autonomously on defined tasks such as pulling assessment data, logging issues, and routing items for review, while humans retain control over every consequential decision.
MetricStream AI spans risk, compliance, policy, audit, regulatory change management, cyber risk, third-party risk, and business continuity management, with each Assistant and Agent trained on domain-specific context.
Every AI recommendation operates within built-in guardrails and human oversight — from Assist, where AI surfaces information and a person acts, to Augment, where AI drafts content for review, to Delegate, where AI executes a defined workflow under a human-set scope and override.
Customers report up to an 80% improvement in risk and control framework-related operational efficiency, an 85% reduction in controls and associated costs, and a 66% reduction in time to complete cyber risk assessments. Use the ROI calculator above to model your own results.
Most organizations start with a single domain, such as Risk, Compliance, Audit, Cyber, or Third Party,rather than a full rollout, so measurable impact begins with the first assessment cycle. Modeled payback across the platform is typically under six months.