$8.4M
net benefit in three years
Drive continuous intelligence, decisions, and action across operations, compliance, audit, and cybersecurity. Earn the trust of your board, customers, and stakeholders with purpose-built AI assistants and agents embedded in the MetricStream GRC solution.
Climate events, fraud, model risk, and regulators across jurisdictions mean that any gap in visibility carries a price for insurers. Even so, siloed systems across underwriting, claims, and operations can hide how these risks interact. Insurers must see risk as a single picture.
Insurance operations are complex. MetricStream's GRC solution, powered by AI assistants and agents, absorbs that complexity, recommending actions and executing approved ones within guardrails that the organization controls.
$8.4M
net benefit in three years
60
reduction in controls managed and tested
50
lesser costs through GRC tool consolidation
Source: The Total Economic Impact™ of MetricStream Enterprise GRC, a commissioned study conducted by Forrester Consulting, March 2026 and MetricStream Business Value Calculator.
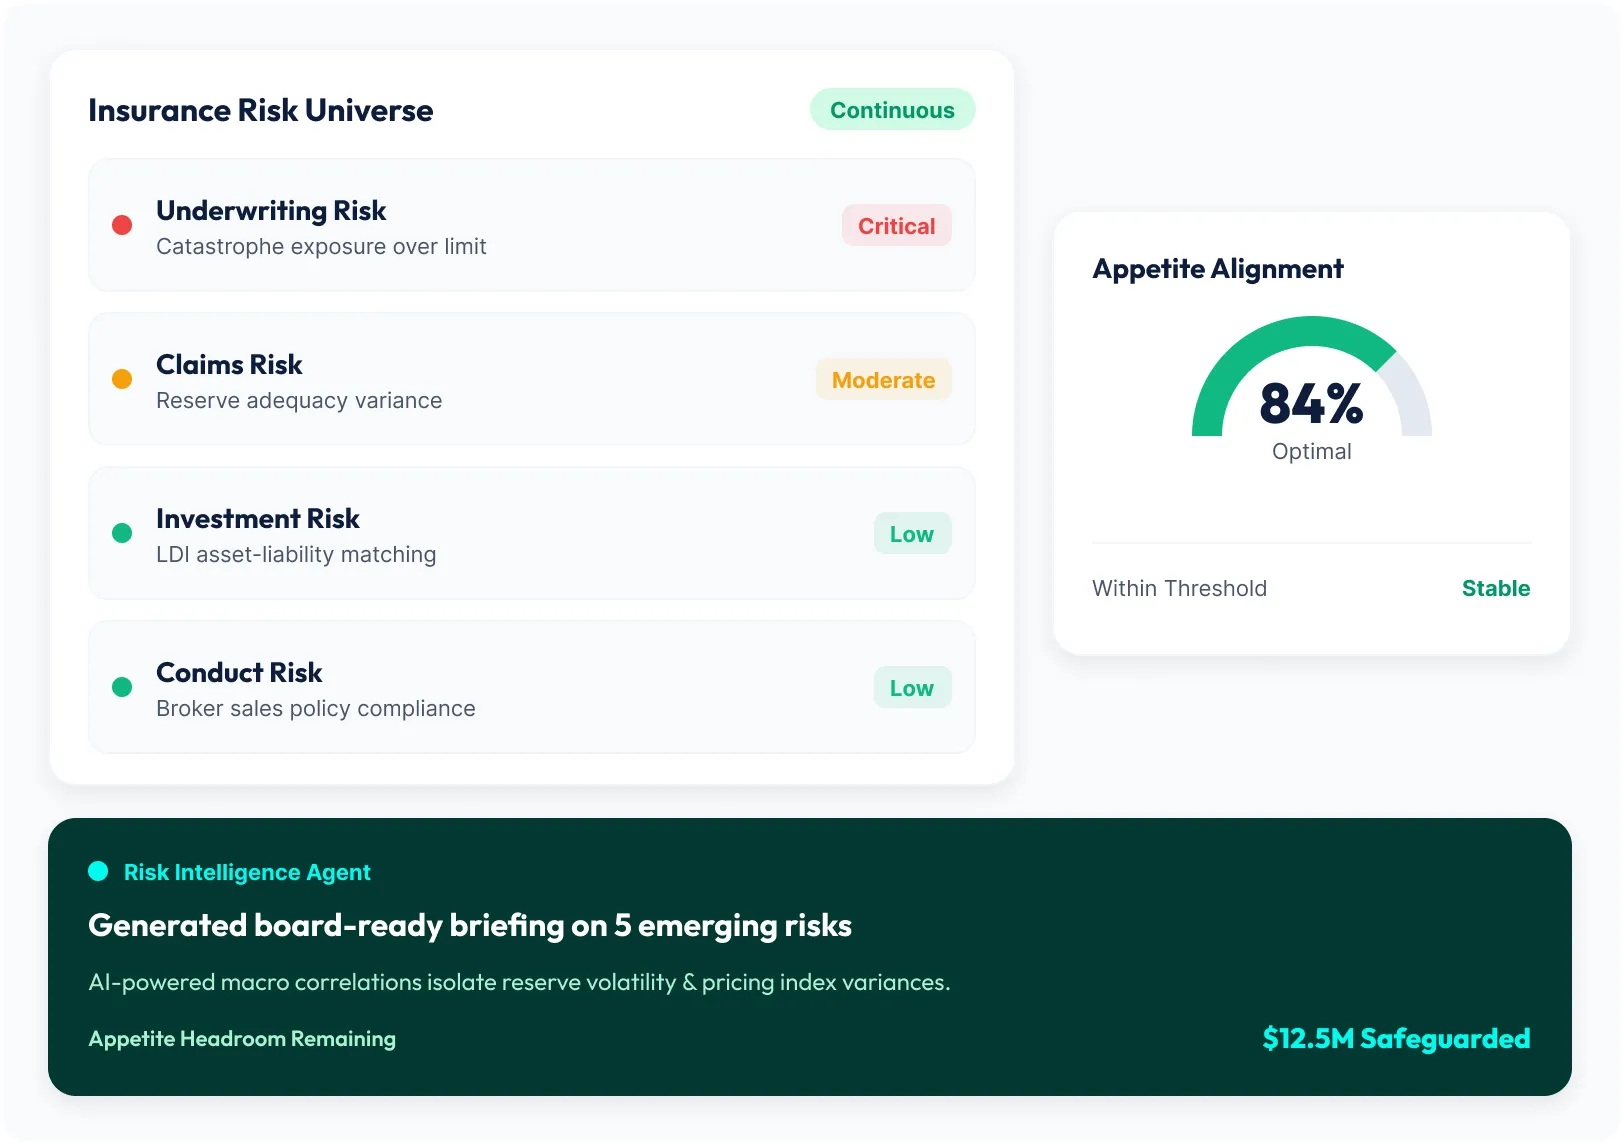
Get a single view into strategic, operational, conduct, model, technology, and emerging risks across legal entities and product lines, alongside critical services, dependencies, and recovery actions. Risk Assistants and Agents highlight emerging risks, prepopulate assessments, correlate indicators, and generate board-ready briefings aligned with the risk appetite, giving insurance organizations a single connected view of risk and resilience.
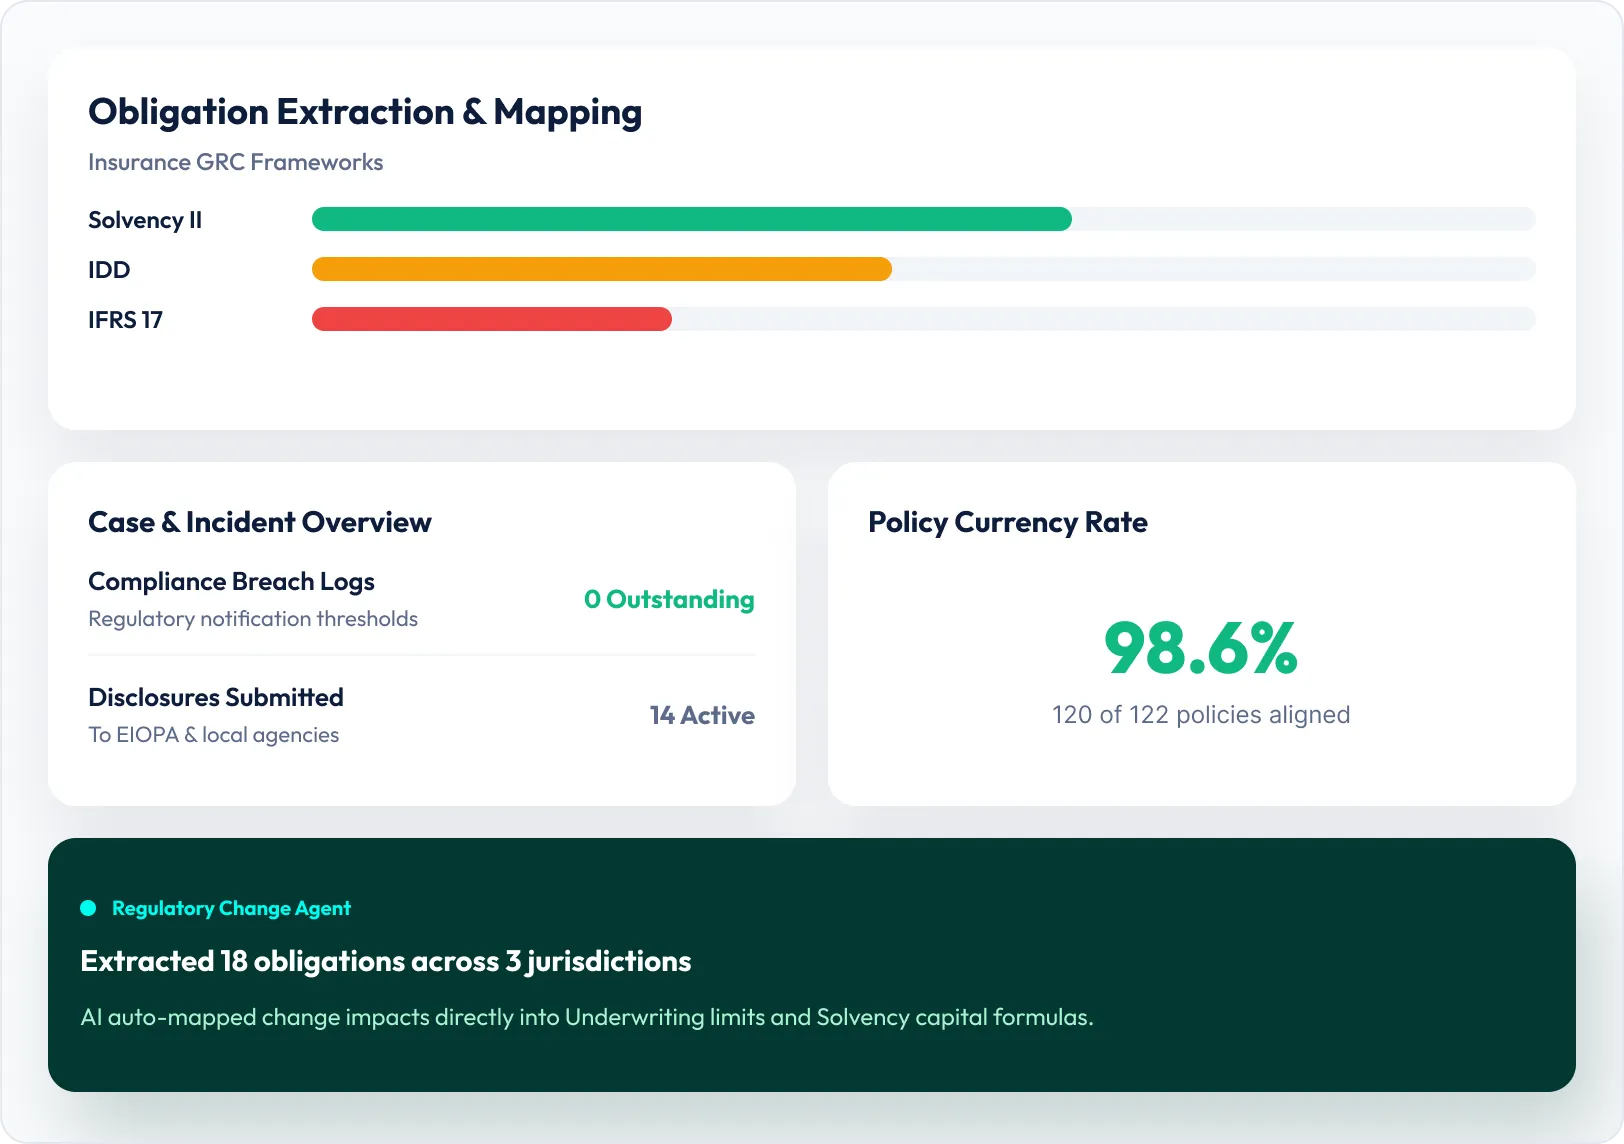
Regulatory developments, obligations, and policy changes are tracked across jurisdictions and insured products, with cases and incidents captured alongside them. Regulatory Change Assistants and Agents assess applicability, extract obligations, and recommend affected controls, while Policy Assistants and Agents provide source-backed policy answers and summarize, keeping every policy and case current and audit-ready.
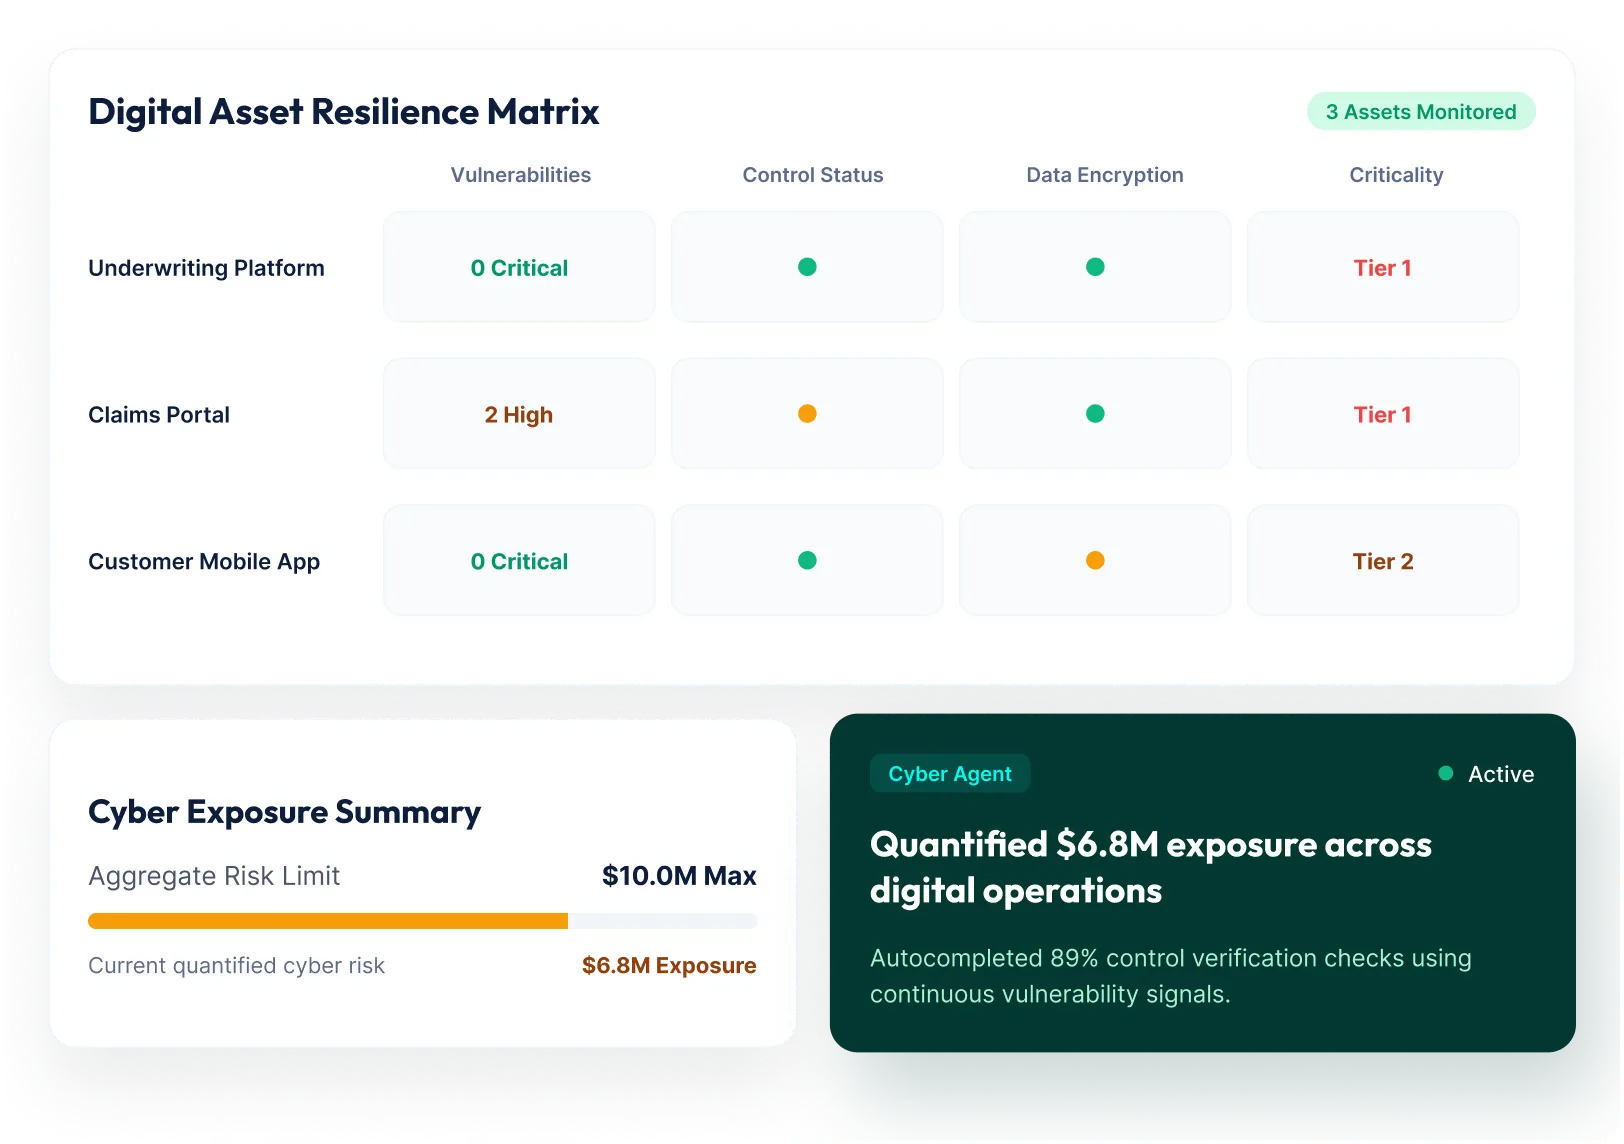
Understand cyber risks and their impact across the enterprise by mapping risks to applications, data, vulnerabilities, controls, and business processes. Cyber Assistants and Agents identify cybersecurity control gaps, standardize control definitions, prioritize assessments and tests, and quantify exposure in business terms, then recommend remediation for the risks that matter most, ensuring digital insurance operations stay protected and resilient.
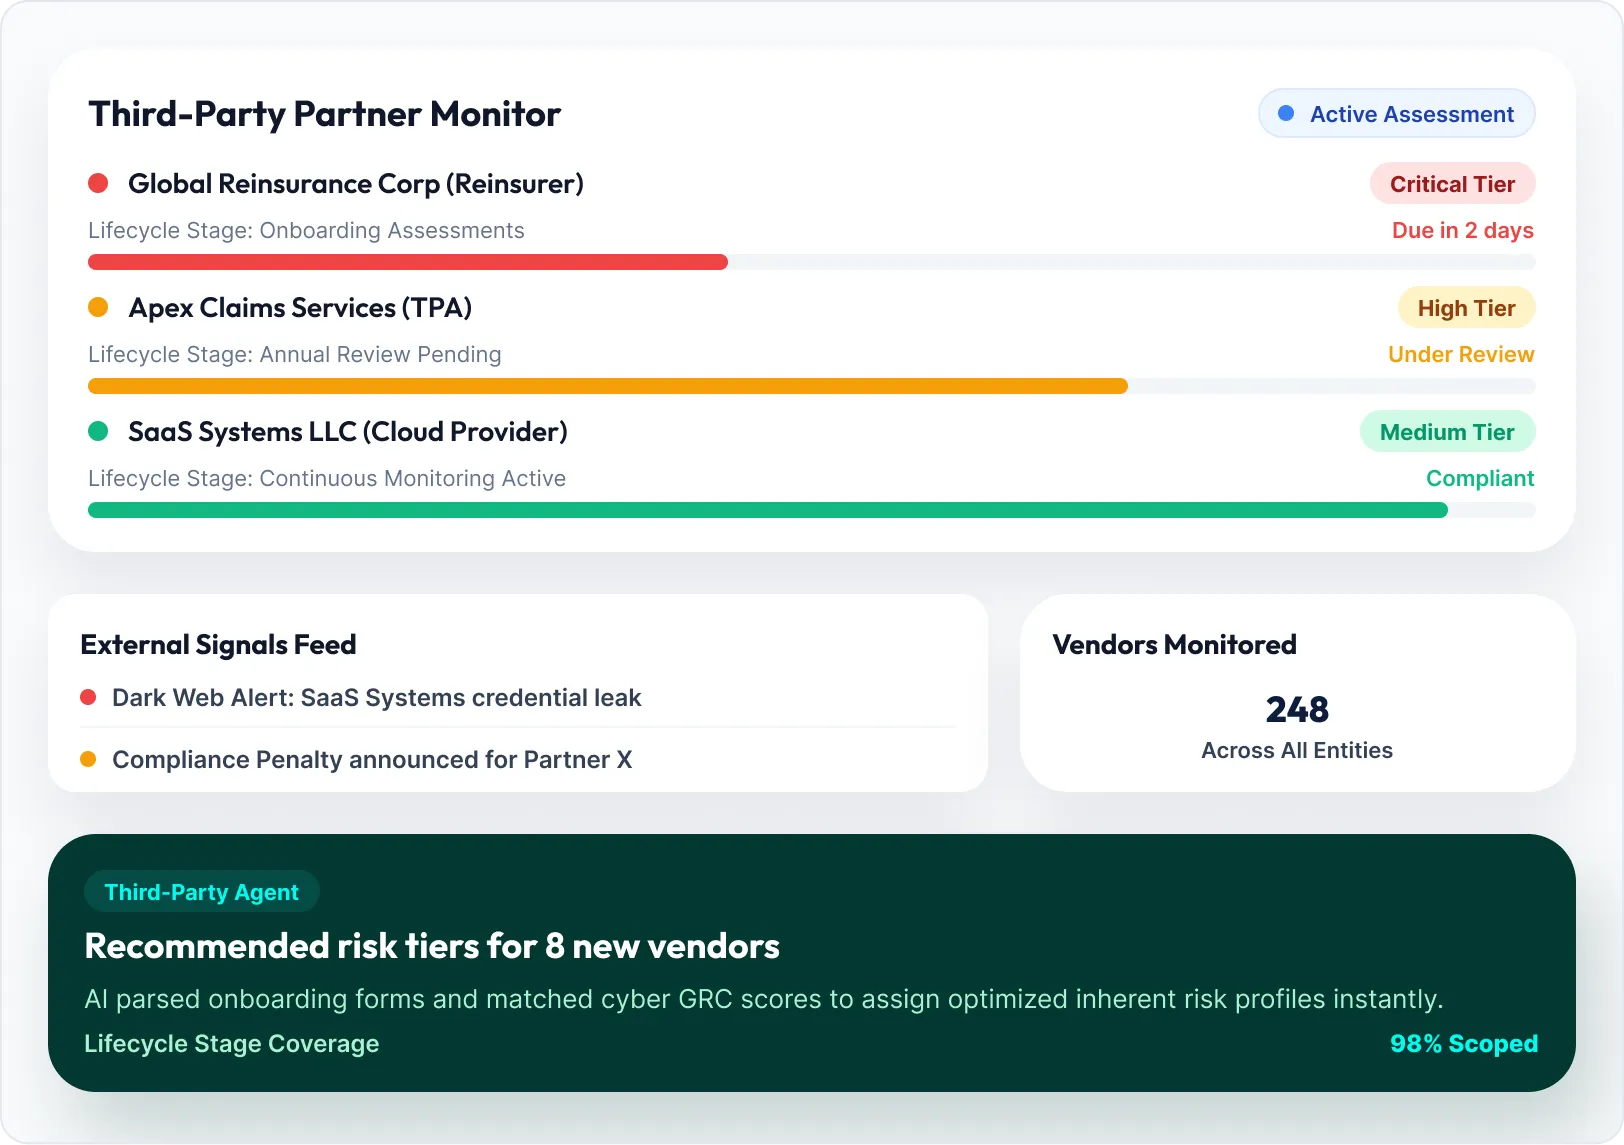
Third-party risks don't wait for the next assessment cycle. Get a complete, real-time picture of risks across risk domains of suppliers, cloud providers, administrators, data partners, distributors, and other third parties across their full lifecycle, from onboarding to offboarding. Third-Party Assistants and Agents recommend inherent-risk tiers, conduct scope assessments, interpret evidence, and monitor external signals, then guide remediation efforts, ensuring every relationship stays visible, assessed, and under control.
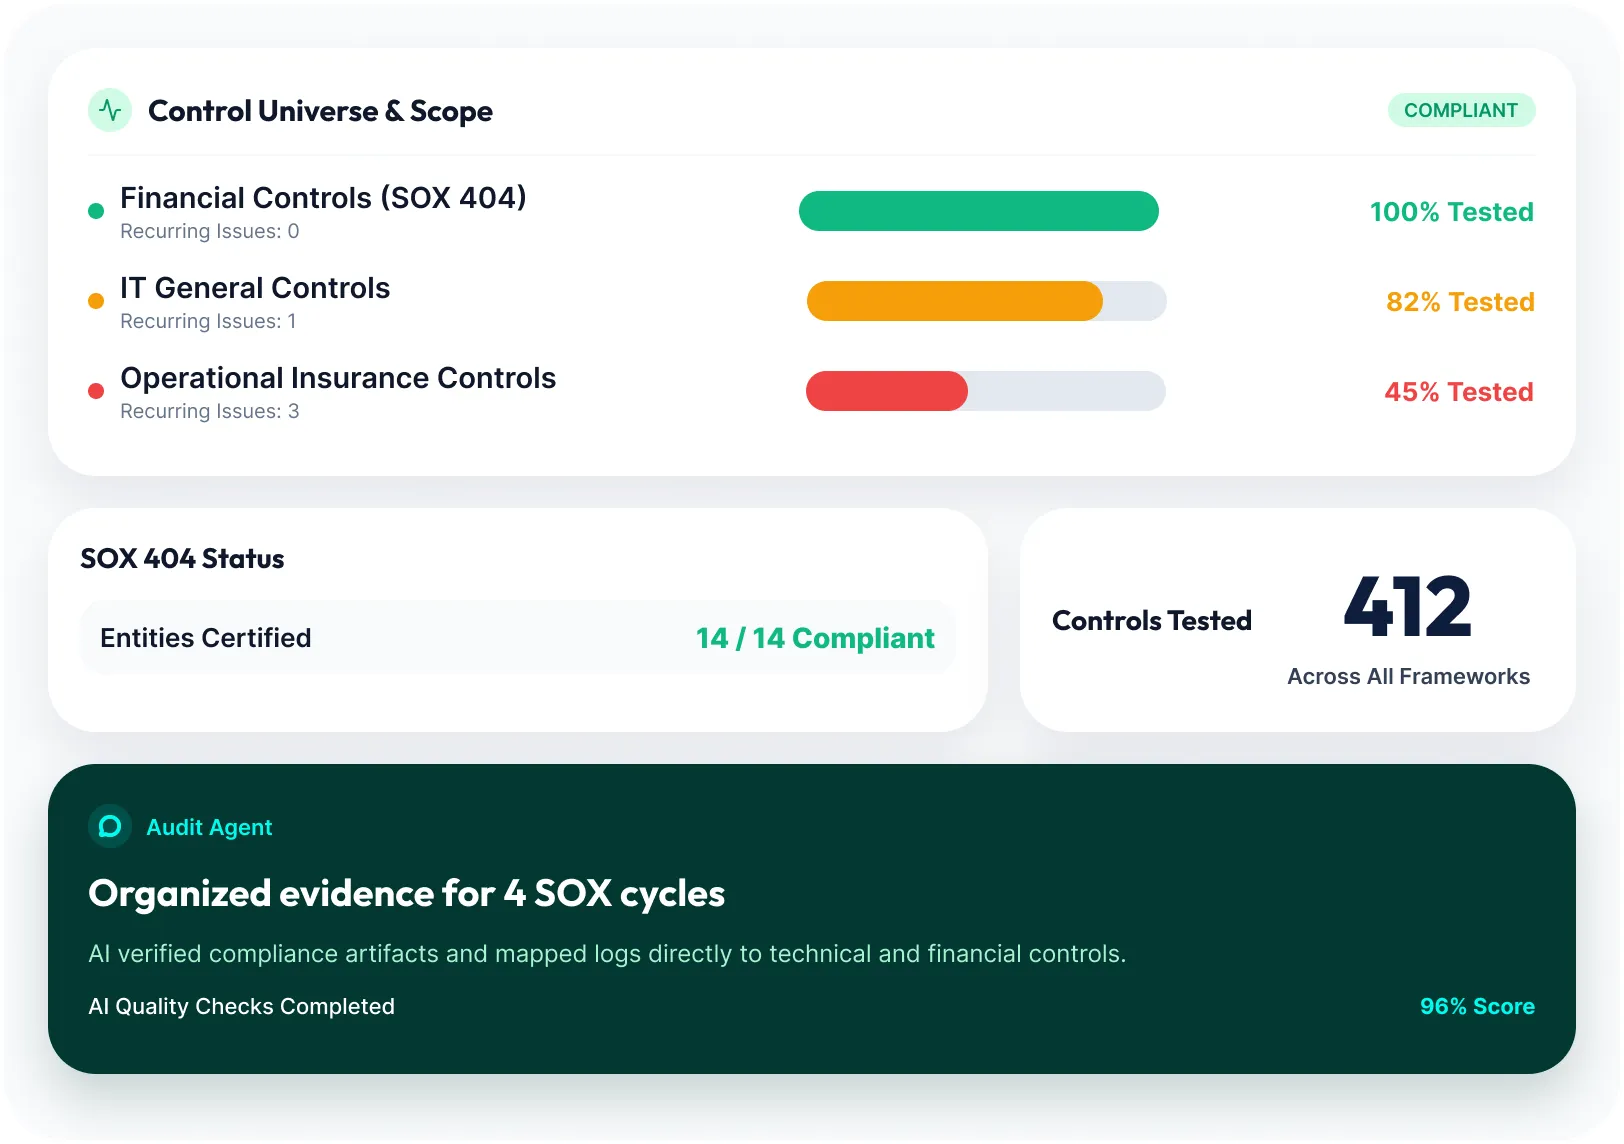
Risk, compliance, cyber, controls, and audit connect through a single shared information model, extending to SOX testing and certification. Audit Agents recommend scope, organize evidence, identify recurring issues, and check report quality, while control owners get sharper testing plans, so assurance stays continuous rather than a once-a-year exercise.
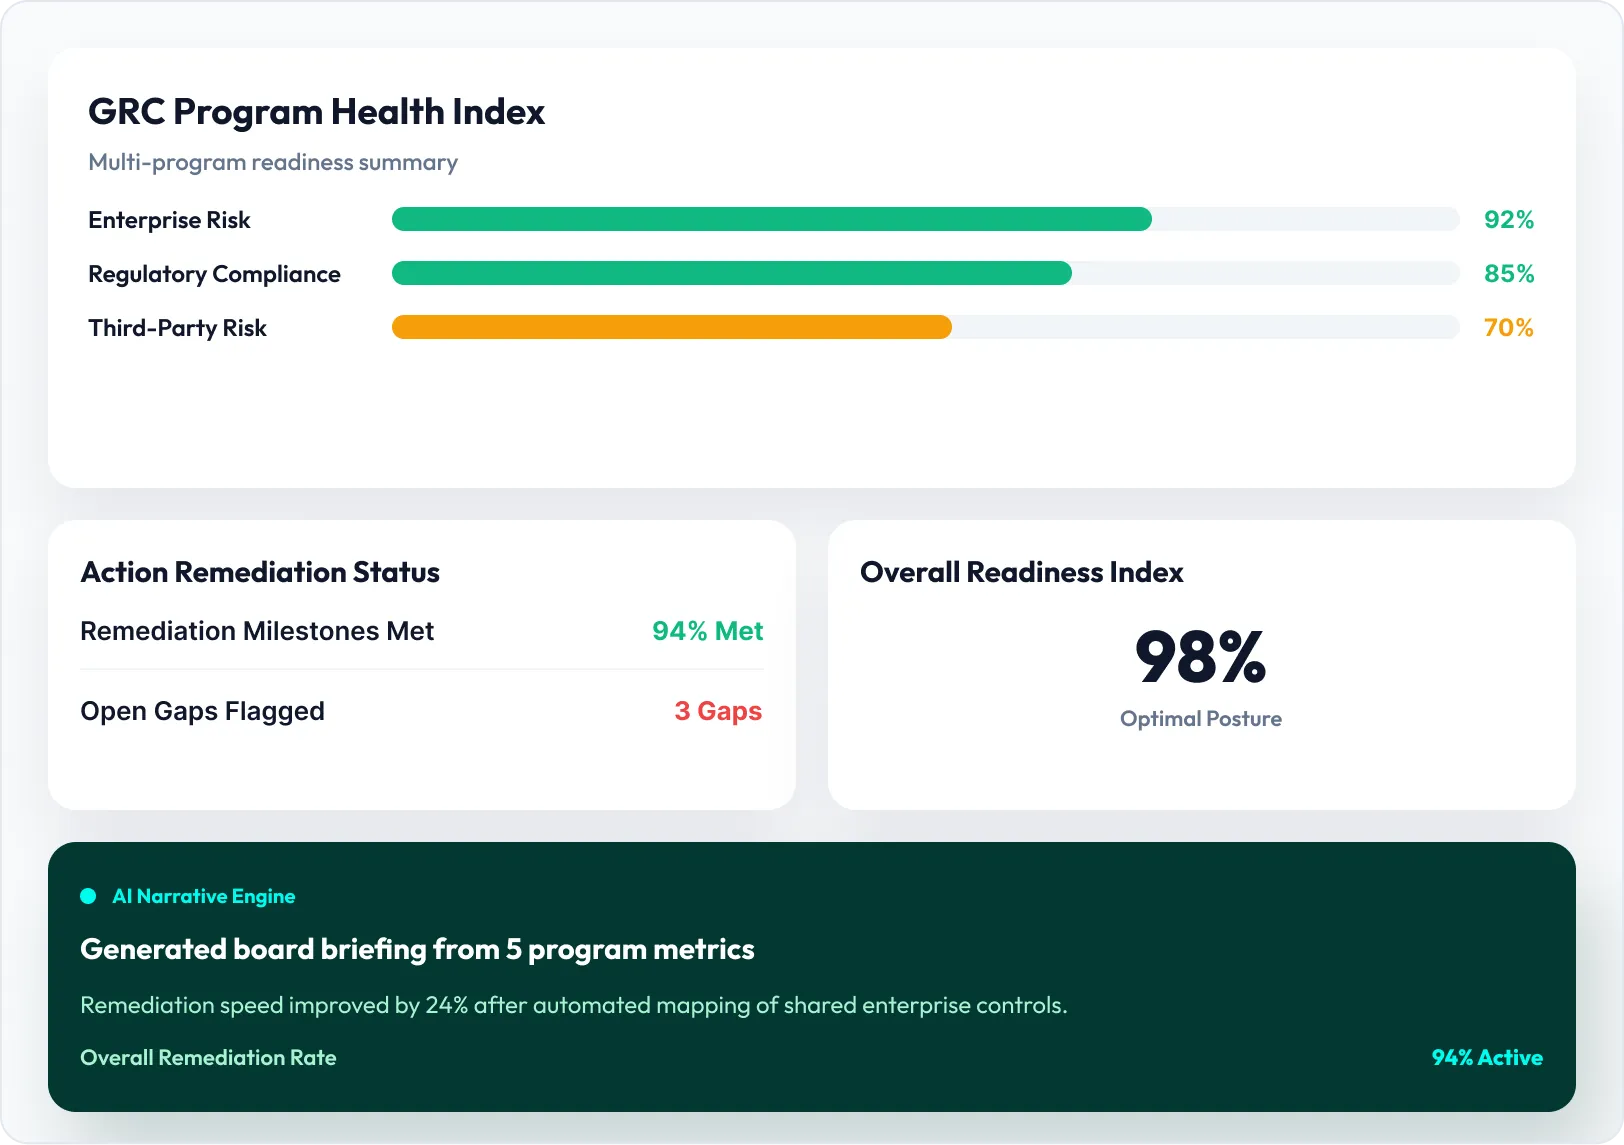
Use one current view across risk, compliance, cyber, third-party, and audit programs. AI-generated risk intelligence narratives turn metrics, controls, and losses into board-ready briefings, while issue and action tracking keep remediation visible in real time. CROs and executives now decide from one connected story, not a static report.
Regulation / Framework
01 / 06
What it requires
How MetricStream helps
Connects risk, controls, governance, assessments, issues, and reporting
Risk, compliance, cyber, and audit intelligence update continuously, with AI recommending and executing approved actions.
Consistently ranked among GRC leaders by analysts including Chartis, Gartner, Forrester, and IDC.
Global insurers trust MetricStream to strengthen GRC programs and earn stakeholder confidence.
Decades of hands-on GRC experience, with experts and AI engineers who deploy and support your program at every milestone.
AI assistants and agents built for your GRC requirements not just bolted on.
Standardize risk taxonomies, assessment templates, and workflows to match your products, entities, and jurisdictions.
Use our interactive ROI calculator, built by Forrester, to estimate what Enterprise GRC could deliver for your organization. Enter details such as annual revenue, number of GRC tools, and compliance exposure to see your potential savings, payback period, and return on investment.
Calculate My ROI
Analyst Report
Download the excerpt to see why MetricStream was recognized as a GRC Leader in 2025.
Download Now
eBook
A CISO's guide to outsmarting cyber risk before it outsmarts you.
Read More
Case Study
Read how a global bank enhanced business decision-making by successfully moving from a traditional approach to a single, connected GRC system.
Read More
Whitepaper
Learn how GRC leaders are adopting AI responsibly and proving measurable ROI at scale.
Read MoreInsurance providers face a complex and rapidly evolving risk landscape shaped by rising customer expectations, climate-related losses, economic uncertainty, and emerging digital risks. Digitization across underwriting, claims, distribution, and third-party ecosystems has expanded risk exposure, particularly in cyber risk, data privacy, model risk management, and fraud. Insurers must also navigate strict oversight from regulators such as state insurance commissions, EIOPA, and the NAIC, and comply with frameworks such as Solvency II and ORSA requirements.
MetricStream's AI-first Connected GRC solution helps insurance providers achieve operational resilience by unifying risk management, compliance, and cyber risk oversight in a single platform. The solution delivers real-time, enterprise-wide risk visibility and streamlines adherence to regulatory frameworks, enabling insurers to proactively manage risk and compliance across all lines of defense, from front-line business units to executive management and the board.
MetricStream's Regulatory Compliance solution helps insurance organizations stay compliant with federal and state regulations across multiple geographies and insured product types. The platform enables teams to proactively identify potential gaps by mapping policies to regulations, risks, and controls, and simplifies compliance management by supporting regulatory change tracking, compliance assessments, control testing, policy management, case investigations, and regulatory engagements.
MetricStream's Cyber GRC solution enables insurance organizations to identify, aggregate, analyze, and manage IT and cyber risks, threats, and vulnerabilities while ensuring compliance with regulatory requirements such as NAIC, PRA, and FCA, and industry standards including ISO 27001 and COBIT. The solution supports cyber risk quantification, evaluating risk exposure in monetary terms, and transforms raw risk data into actionable IT risk intelligence, giving insurers comprehensive visibility into the cyber risks most likely to affect the enterprise.
MetricStream's Enterprise and Operational Risk Management solution helps insurance companies implement an integrated and automated approach to managing enterprise risks. The platform strengthens risk management programs by improving risk identification, risk tolerance assessment, and risk appetite alignment. Organizations gain enhanced risk visibility and foresight, enabling them to transform risk into strategic advantage and make well-informed business decisions based on a clear understanding of risk exposure.
MetricStream's Third-Party Risk Management solution gives insurance organizations an integrated, real-time view of risks across all third parties, including vendors, suppliers, and contractors. The platform protects organizations from third-party and fourth-party risk exposure, manages third-party risks throughout the full lifecycle from onboarding to offboarding, and enables teams to leverage historical data on third parties to make more confident sourcing and negotiation decisions.
MetricStream enables integrated assurance by connecting compliance, audit, and risk management teams on a single platform, ensuring that findings and insights flow across functions rather than remaining siloed. This connected approach gives insurers a unified view of risk and compliance posture, supports better collaboration across lines of defense, and helps organizations demonstrate a robust, enterprise-level approach to risk management to regulators and executive management.
According to MetricStream customer responses and the GRC Journey Business Value Calculator, insurance organizations using MetricStream have achieved a 67% improvement in risk reporting visibility and efficiency for the executive management and board, a 90% compression in compliance management timelines, and a 60% improvement in response time to regulatory changes. These outcomes demonstrate the platform's impact on reducing compliance burden and improving risk governance at scale.
MetricStream's Regulatory Compliance solution enables insurers to respond more quickly to regulatory changes by centralizing compliance management and automating the process of tracking, mapping, and acting on new obligations. According to MetricStream customer responses and the GRC Journey Business Value Calculator, organizations have achieved a 60% improvement in response time to regulatory changes, giving compliance teams the speed and agility needed to adapt internal processes without disrupting operations.
AI capabilities in MetricStream's insurance GRC solution enable proactive risk detection, smarter controls, and automated compliance, reducing the manual burden on risk and compliance teams. The platform uses AI to accelerate routine GRC tasks, including predictive insights, automate risk assessments and regulatory tracking, and provide forward-looking visibility into the risks most likely to affect an insurer's financial stability and customer confidence. This allows insurance organizations to shift from reactive to proactive risk management.