Third-Party Risk Assistant
Get contextual answers across relationships, assessments, contracts, evidence, performance, incidents, and issues.
Map every vendor, supplier, and partner relationship and dependency with AI assistants and agents that tier third parties, tailor due diligence, and monitor them across risk domains.
Get contextual answers across relationships, assessments, contracts, evidence, performance, incidents, and issues.
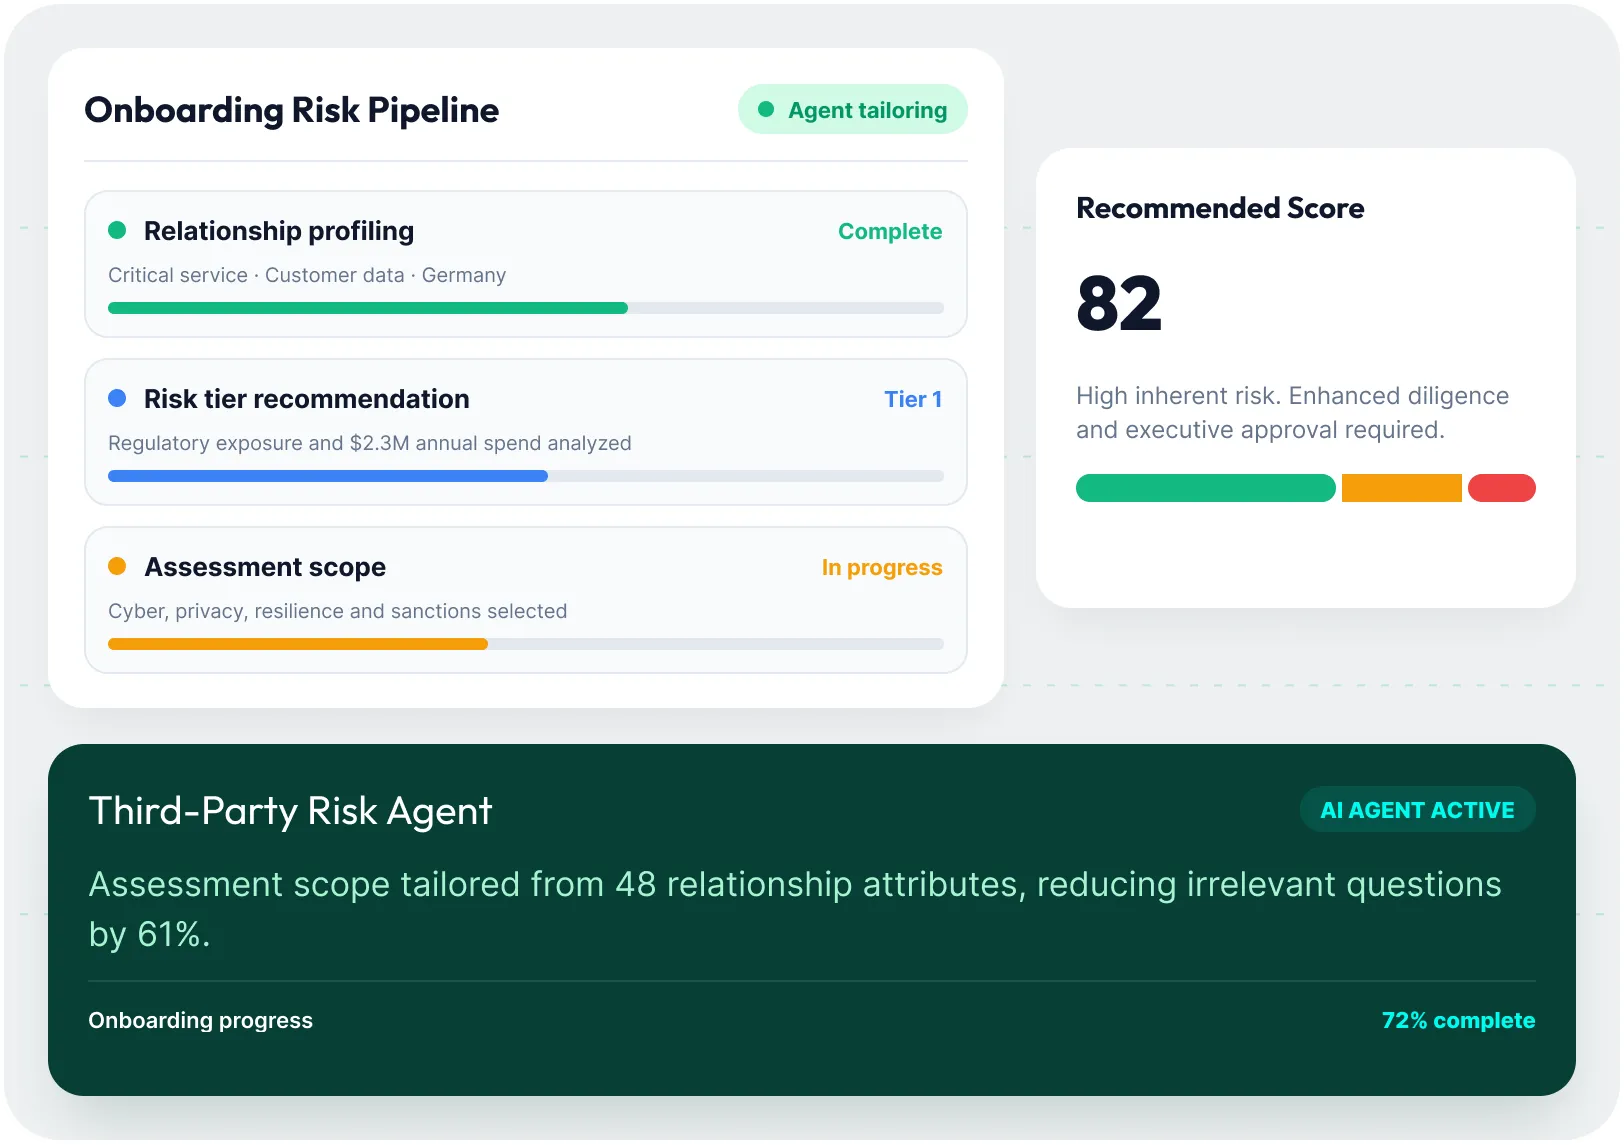
Purpose-built agents recommend tiers, tailor assessments, interpret evidence, monitor signals, and guide remediation.
Connect MetricStream agents with procurement, contract, security, finance, compliance, resilience, and partner systems.
60%
Faster third-party inventory and onboarding cycle time
60%
Faster due diligence and risk-assessment cycle time
60%
Improvement in third-party evidence and documentation management
Source: MetricStream’s Business Value Calculator
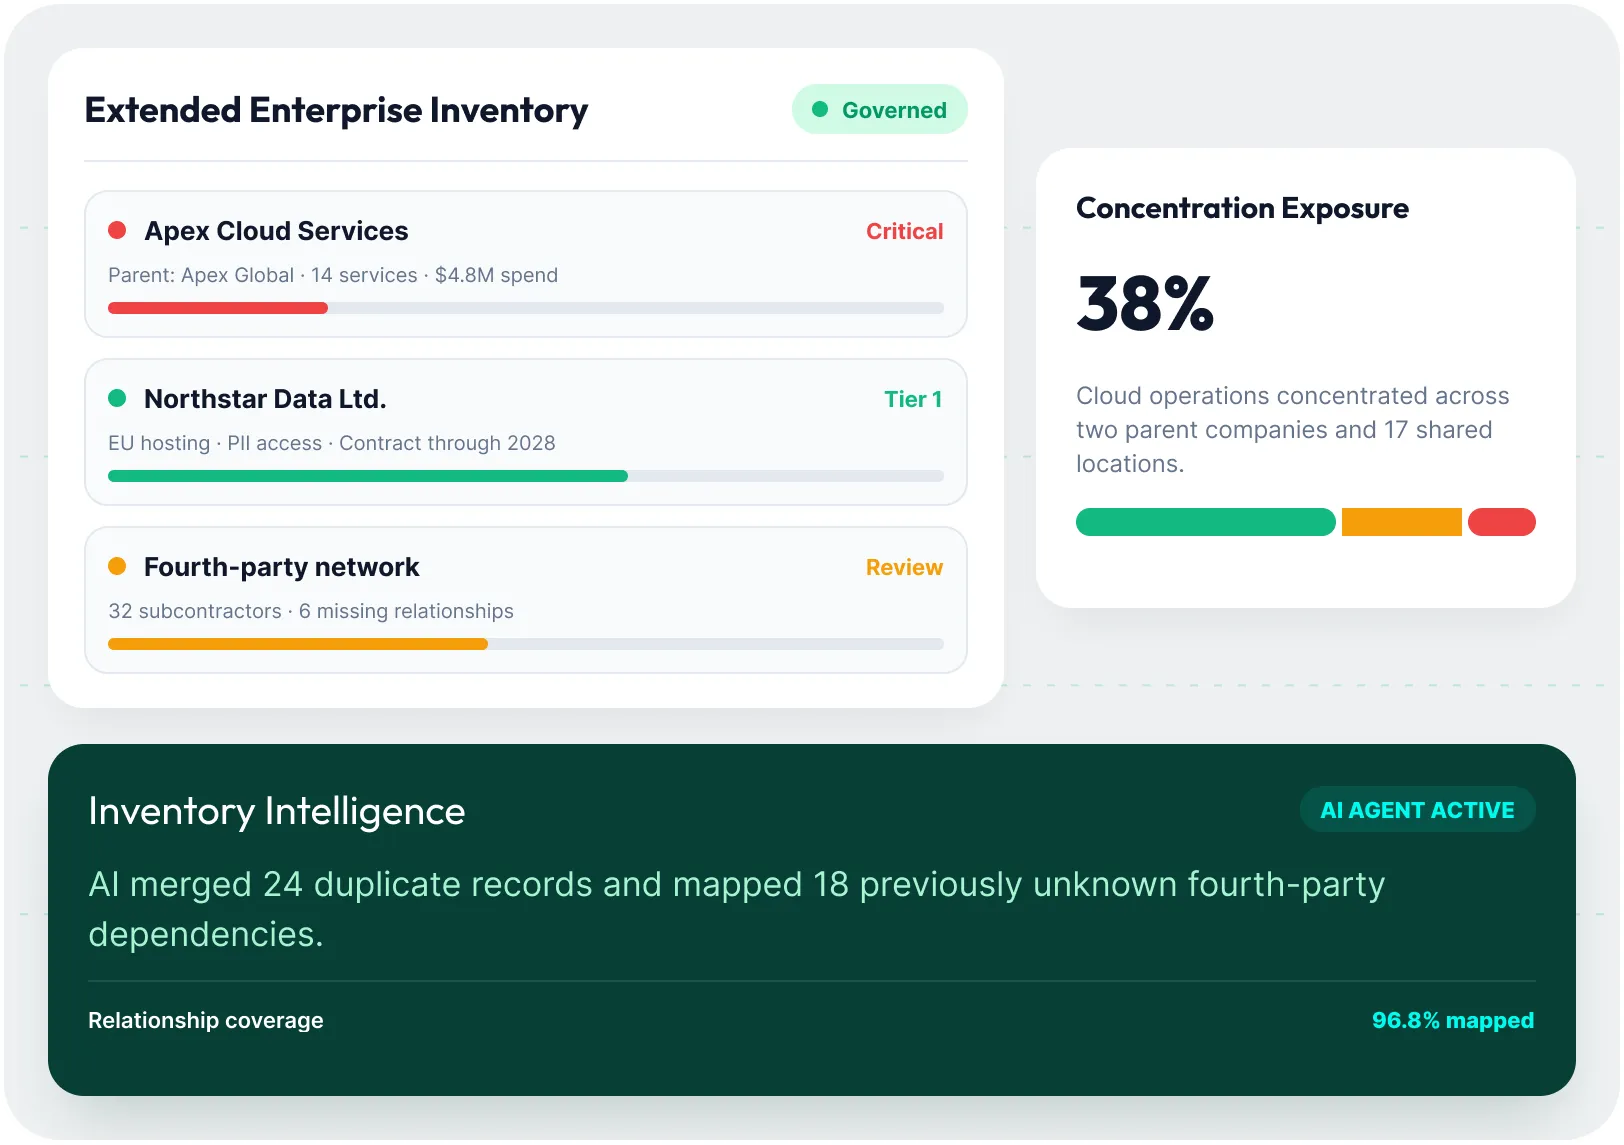
Stop searching across procurement systems, spreadsheets, and assessment tools to understand who your organization depends on. Connect third parties, vendors, parent companies, subcontractors, services, locations, contracts, spend, data access, performance, and issues in one governed inventory. AI helps identify duplicate records, missing relationships, concentration risk, and shared dependencies across business units and geographies, providing a complete view of your extended enterprise.
Third-Party Risk Capability
Traditional Third-Party Risk Management
MetricStream Agentic Third-Party Risk Management
Inventory
Incomplete and duplicated records
AI connects relationships and identifies missing context
Tiering
Rules applied manually
AI recommends defensible risk scores and tiers
Due diligence
One-size-fits-all questionnaires
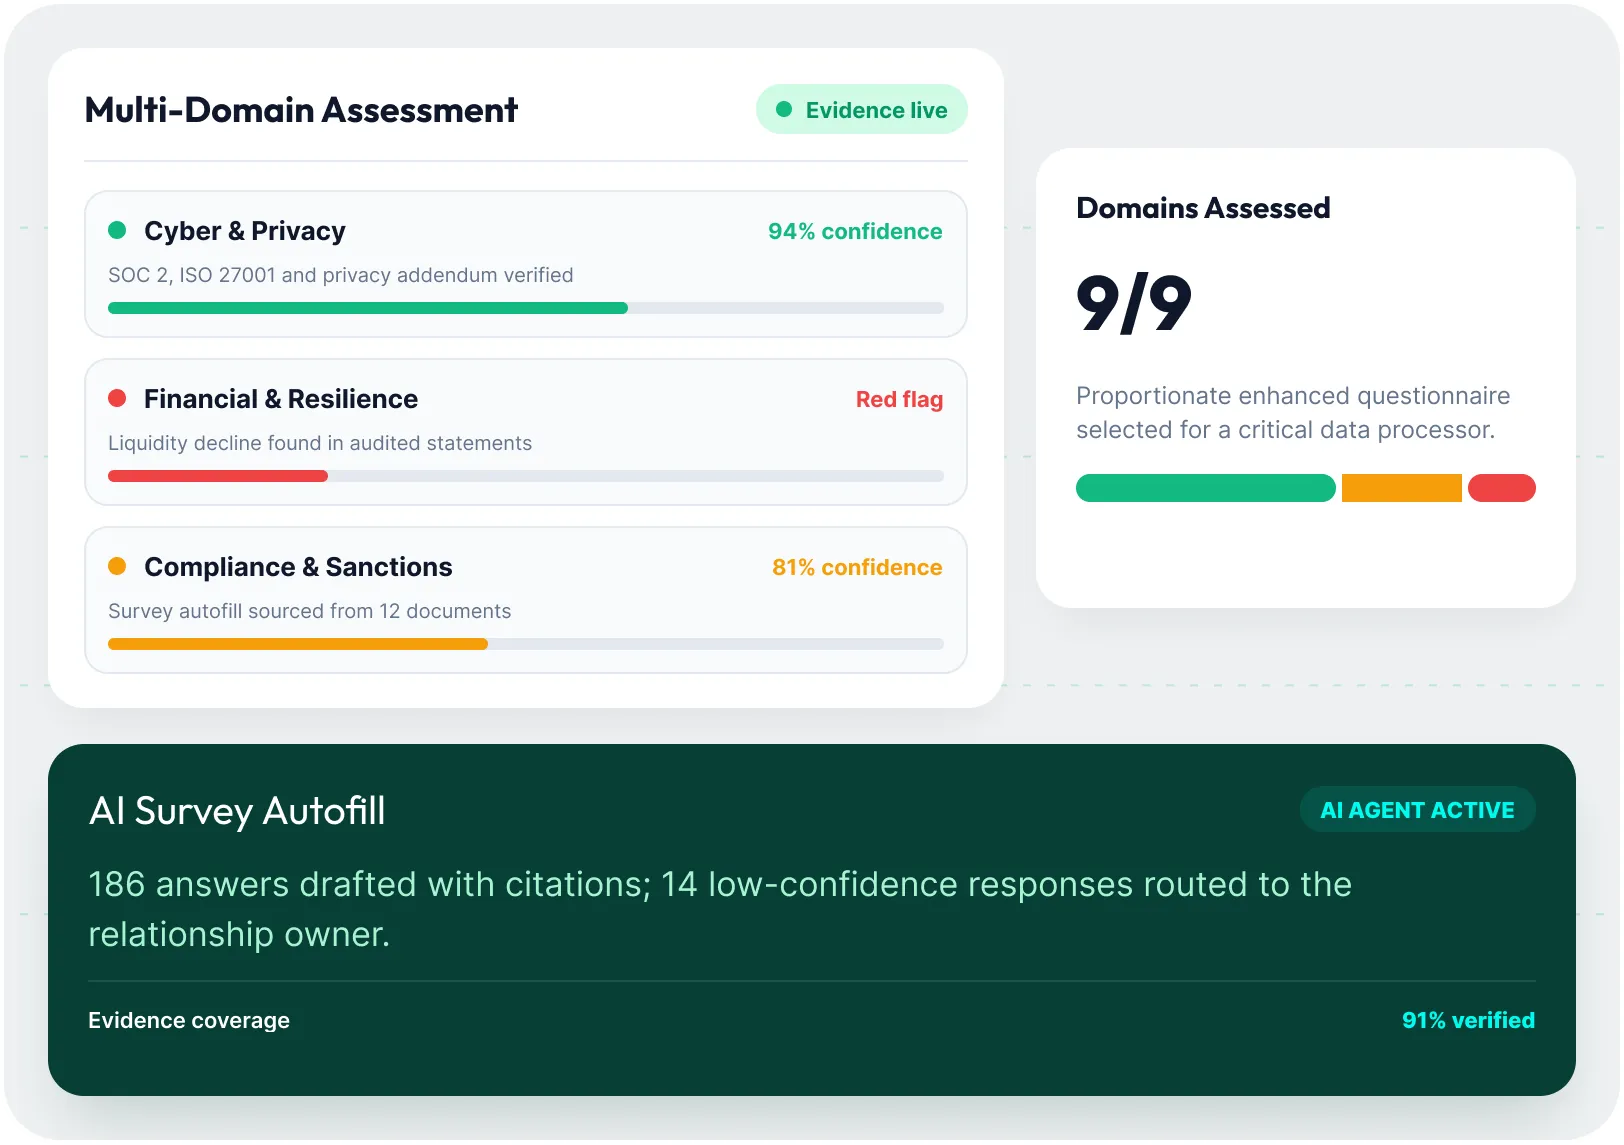
Agents tailor scope and AI drafts source-backed responses
Monitoring
Periodic snapshots
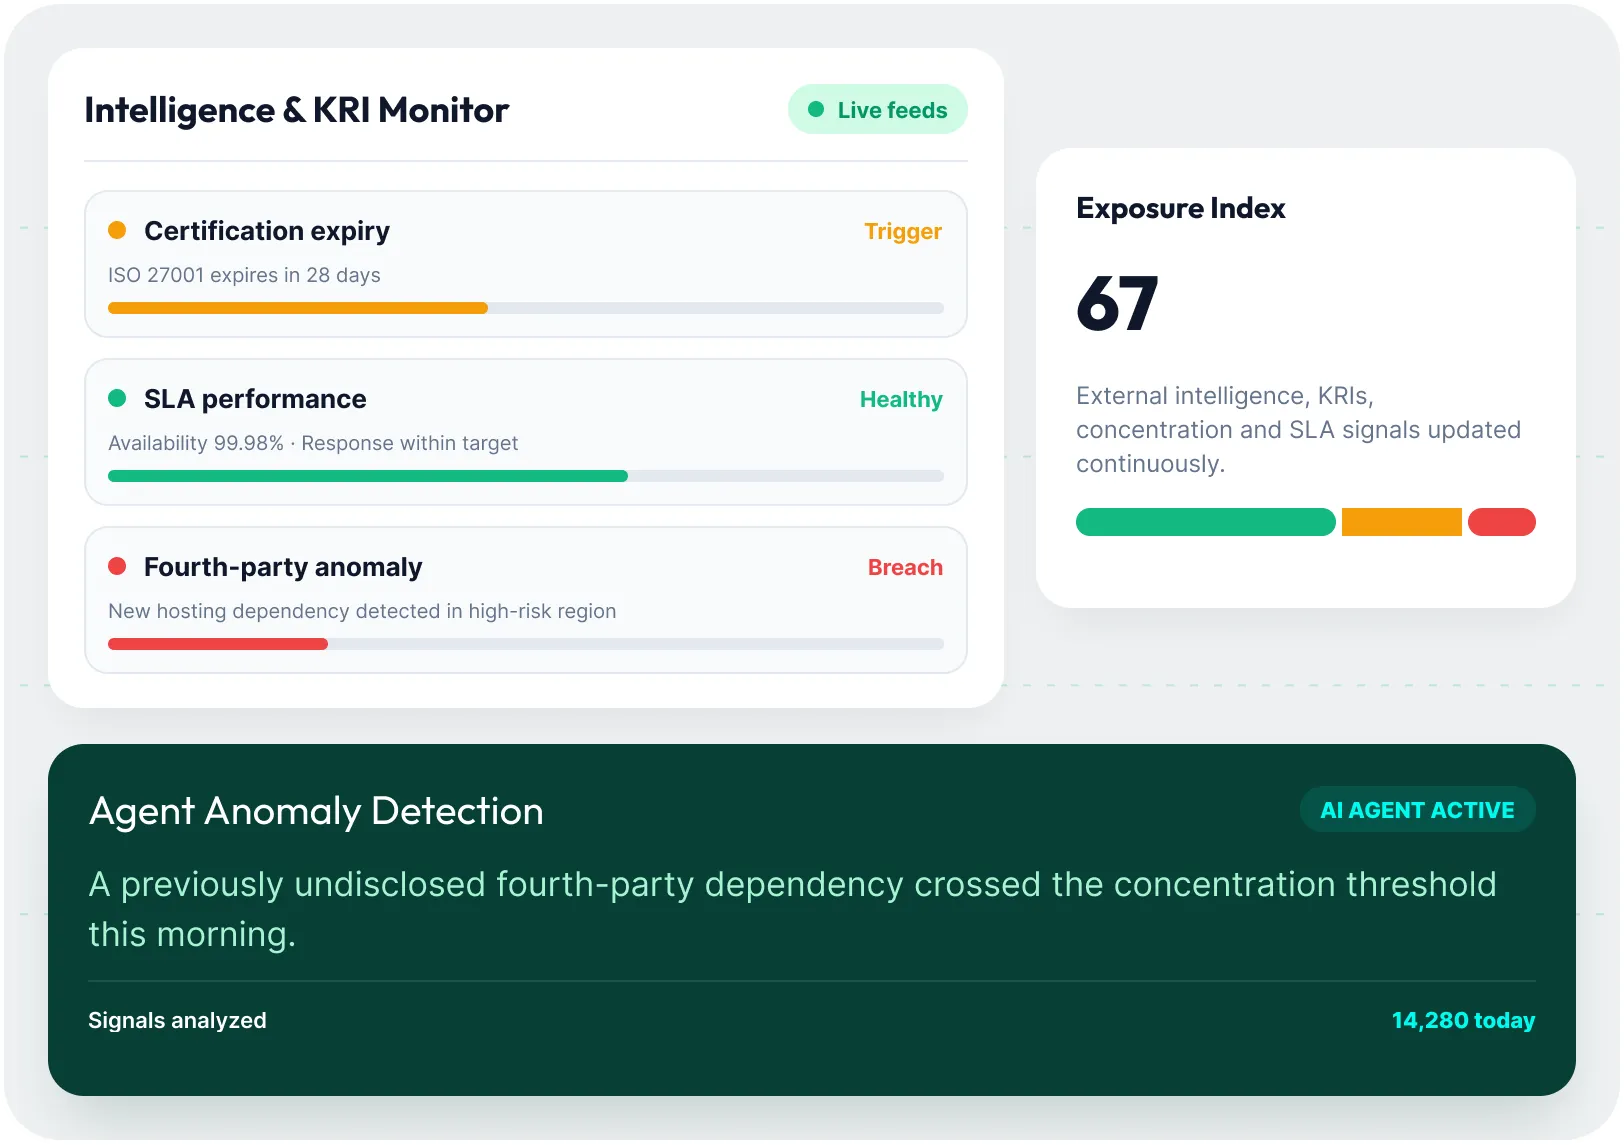
Continuous signals trigger reassessment and action
Fourth parties
Limited dependency visibility
Connected relationships expose extended risk
Contracting
Findings disconnected from contract terms
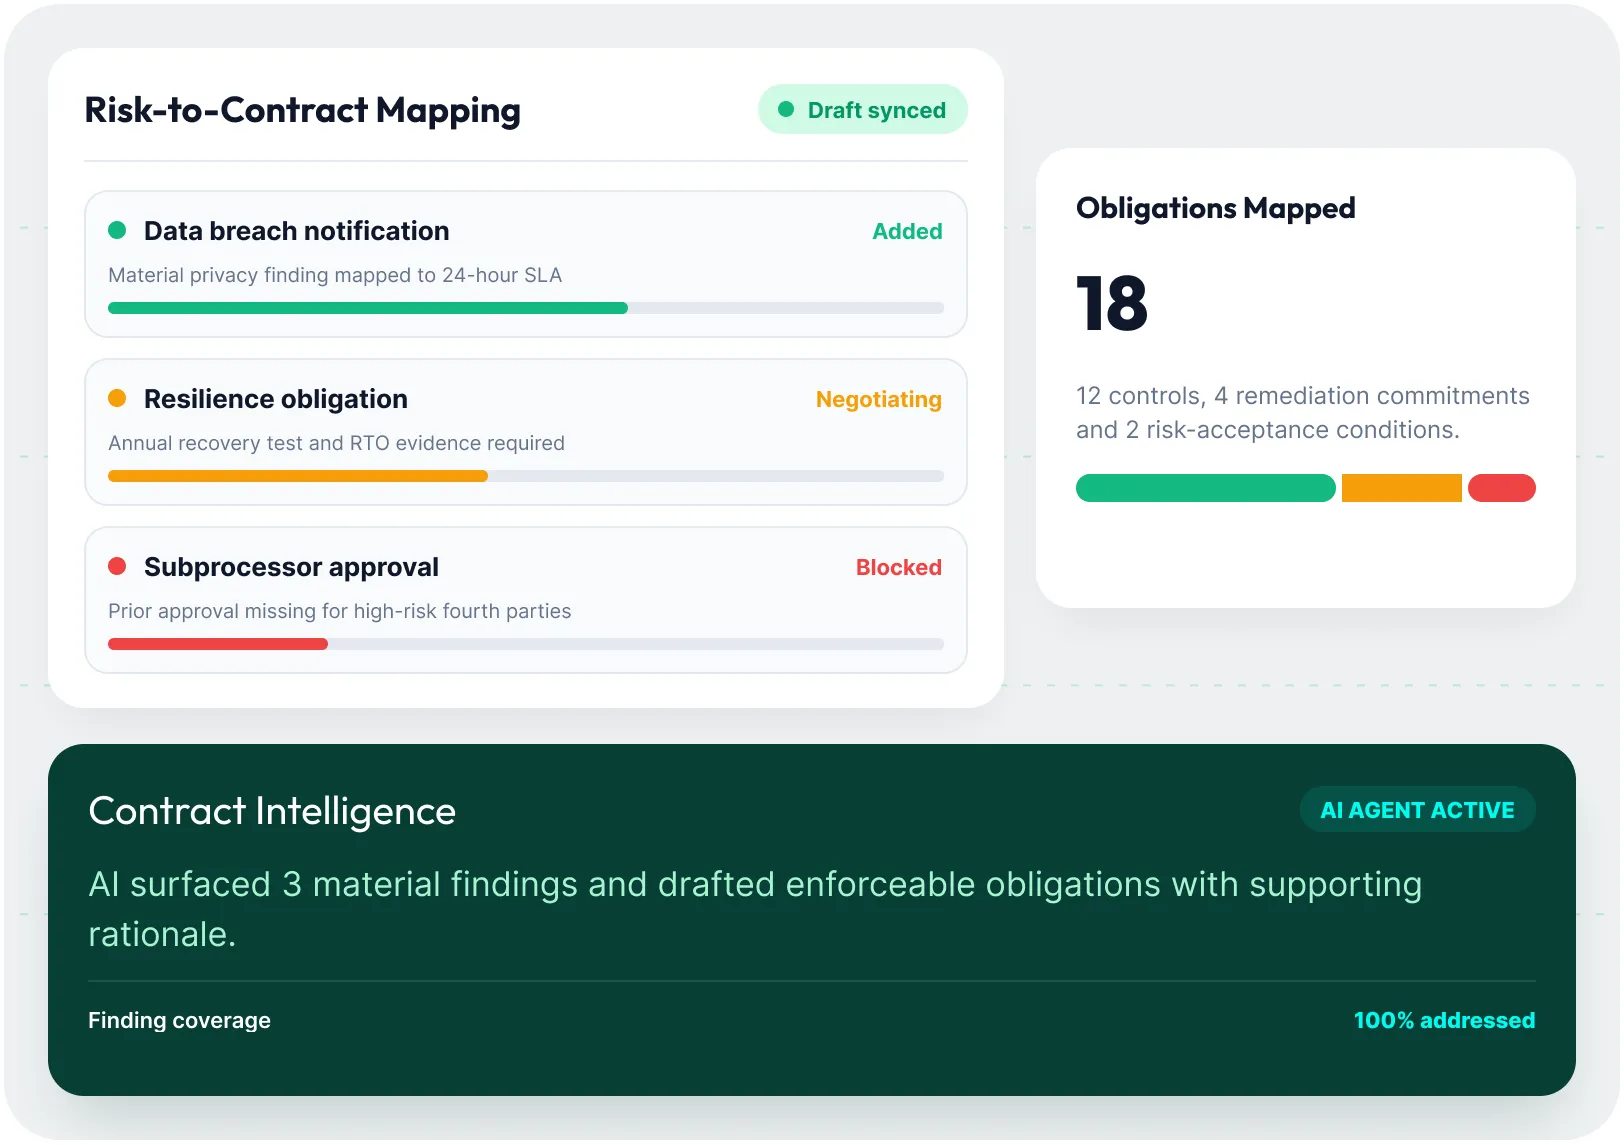
Risk intelligence informs obligations and conditions
Remediation
Findings chased manually
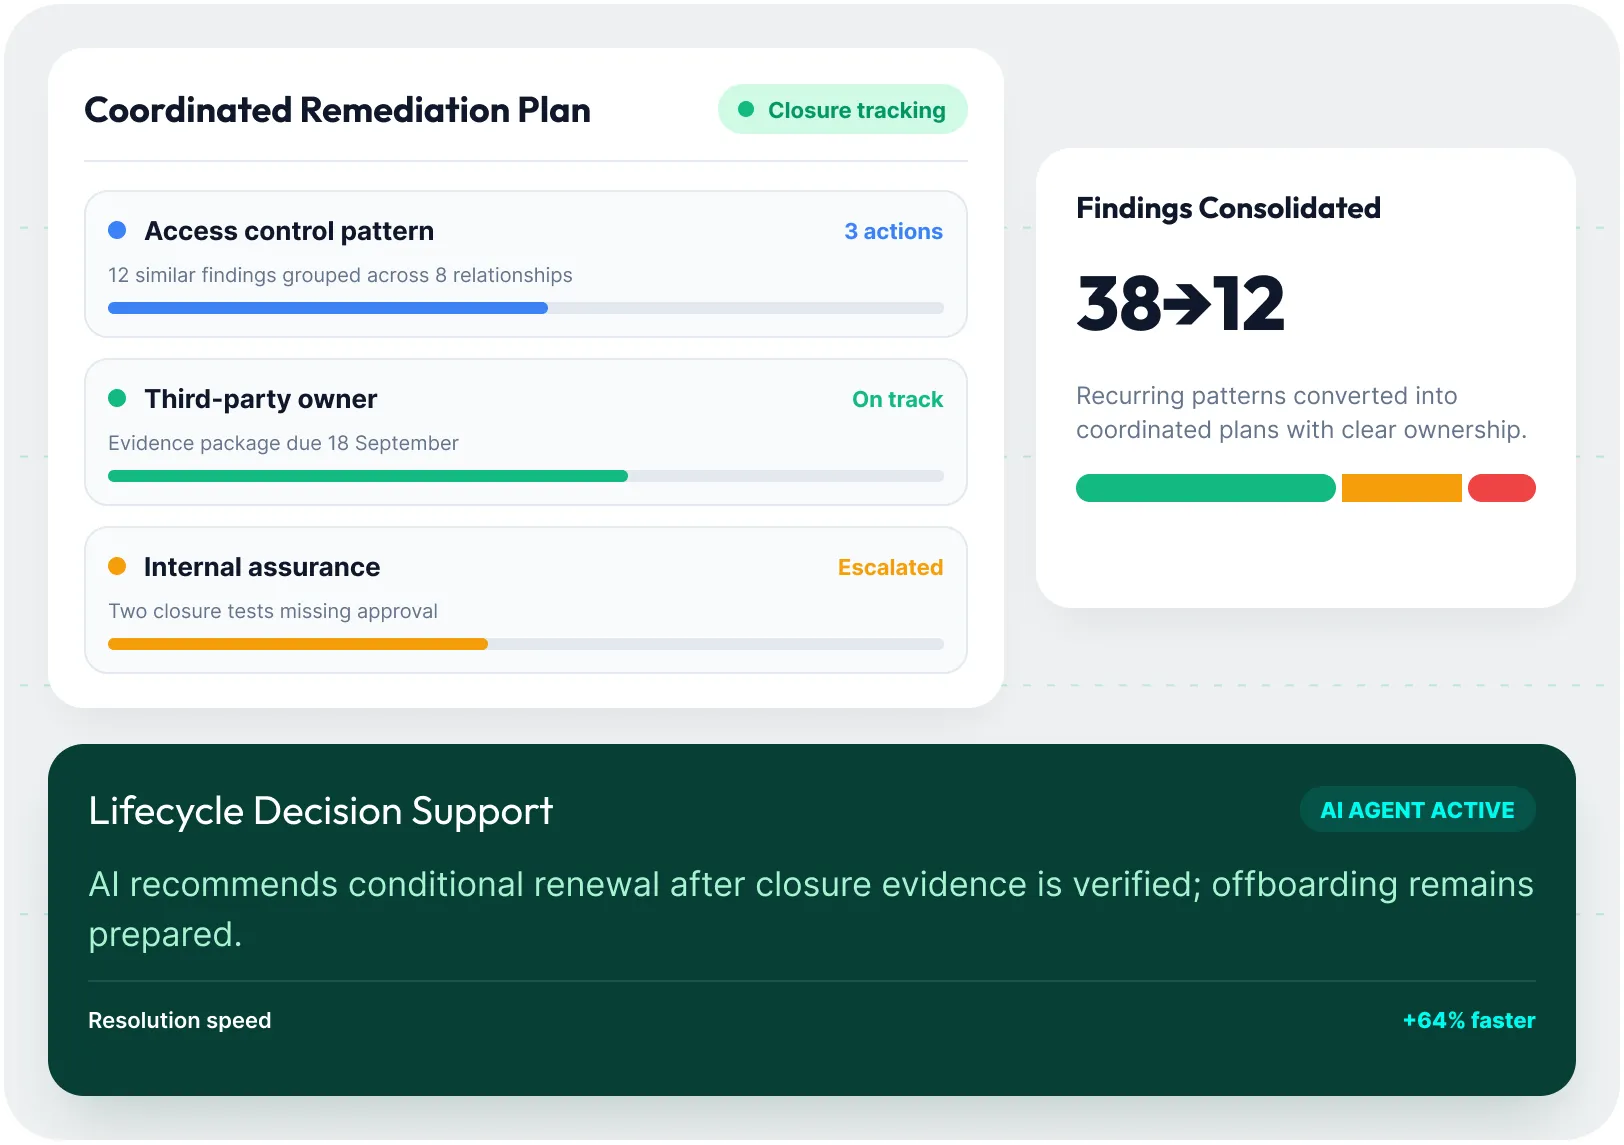
AI clusters issues and recommends coordinated action
Use our interactive ROI calculator, built by Forrester, to estimate what Enterprise GRC could deliver for your organization. Enter details such as annual revenue, number of GRC tools, and compliance exposure to see your potential savings, payback period, and return on investment.
Calculate My ROI
Assess cyber, financial, compliance, ESG, resilience, operational, and reputational exposure.
Understand third parties, fourth parties, services, dependencies, and concentration risk.
Accelerate tiering, due diligence, evidence review, monitoring, and remediation.
Configure questionnaires, scoring, workflows, thresholds, approvals, and risk domains.
Preserve citations, evidence, ownership, approvals, decisions, and complete audit trails.
Third-party risk and AI specialists support design, adoption, optimization, and measurable value.

Analyst Report
Download the excerpt to see why MetricStream was recognized as a GRC Leader in 2025.
Download Now
eBook
Why compliance automation matters, how to harness it effectively and what to keep in mind when using automated and AI powered solutions
Read More
Case Study
Read this case study to learn how MetricStream helped a leading stock exchange and financial information company unify its operational risk and resilience framework.
Read More
Whitepaper
Learn how GRC leaders are adopting AI responsibly and proving measurable ROI at scale.
Read MoreMetricStream Third-Party Risk Management is a comprehensive third-party risk management software solution that enables organizations to identify, assess, mitigate, and monitor risks posed by third and fourth parties. It provides packaged workflows, assessments, and risk intelligence to manage compliance, track performance, remediate issues, and improve business agility — all within a single, integrated platform.
Your third parties – such as your vendors, supplier and contractors – are an essential part of doing business, but also pose critical risks such as reputational risk, cybersecurity risk, and strategic risk. You assume the risks of your third parties when doing business with them – for example, if they suffer a data breach or act unethically, you too can be liable for financial loss, reputational damage, and much more. In today’s fast-changing world, assessing, managing and monitoring the risk of your third parties is vital to pre-empt risk and safeguard your business.
Yes. MetricStream’s Third-Party Risk Management product is a vendor risk management software designed to help you assess your third parties for risk from when you first start working with them – onboarding – till termination and off-boarding. The vendor risk management software equips you with intelligent dashboards and a user-friendly interface to empower you to conduct due diligence, assess risk, and continuously monitor for changes in risk profiles.
Absolutely. For maximum visibility into the background and risks of your third parties, MetricStream’s risk-based approach enables you to combine your internal data and scoring criteria with built-in scoring models and external content and intelligence (such as BitSight’s cybersecurity ratings, for example) to provide a complete view of risk. You can screen third parties for multiple aspects of risk, including cyber, financial health, anti-corruption, and other relevant criteria.
The challenge of many third-party risk assessment processes is that they’re manual. MetricStream enables you to automate your processes – for example, our built-in artificial intelligence flags anomalies for review, simplifying your scrutiny of security certification reports such as SOC2. Instead of using valuable analyst time, you can divert your resources to strategic, value-added activities and at the same time, manage and monitor more third parties. Remember that risk can come from any supplier – even small or under-the-radar vendors can put you at risk. Assessing as much of your base as possible limits your exposure – and technologies like AI make this possible.
You can explore the MetricStream Integrated Risk Management solution that empowers organizations to manage both current and emerging risks across geopolitical, digital, strategic, third-party, cybersecurity, and compliance areas. To request a demo, click here. Integrated risk management solution demo
Also, you can visit our Learn section to dive deeper into the GRC universe and the Insight section to explore our customer stories, webinars, thought leadership, and more.
MetricStream’s Third-Party Risk Management solution simplifies third-party intake across departments through a user-friendly portal. It automates risk evaluation for each third-party or engagement, enables risks to be mitigated before onboarding takes place, and integrates with alerts from reliable external sources to screen and verify third-party information. Requesters or approvers can also cancel a third-party or request based on business needs.
MetricStream’s Third-Party Risk Management solution automatically validates third-party information and identifies red flags using globally sourced content across multiple risk domains, including cybersecurity, finance, sustainability, regulations, disaster and hazard, corruption, reputation, sanction lists, Politically Exposed Persons (PEPs), Special Interest Persons (SIPs), state-owned enterprises, and adverse media listings. Organizations can subscribe to alerts based on the criticality of each third party, and upon reviewing those alerts, assign risk ratings and trigger further assessments.
Yes. As third-party risk management software, MetricStream’s Third-Party Risk Management solution leverages AI-powered regulatory report scanning to automatically scan and highlight anomalies in SOC 2 and SOC 3 reports, rating third parties accordingly. For issue management, AI/ML capabilities help quickly identify issues based on relationships and recommend issue classification. Internal and third-party users can also flag observations and report deviations through simplified forms and chatbot or conversational interfaces.
Organizations using MetricStream Third-Party Risk Management can expect faster onboarding, faster due diligence, and better control of third-party documentation. MetricStream reports up to 60% faster third-party inventory and onboarding cycle times, up to 60% faster due diligence and risk-assessment cycle times, and a 60% improvement in third-party evidence and documentation management. For risk and procurement teams, that means new third parties are onboarded sooner, assessments close in less time, and the evidence behind each risk decision is easier to find and maintain.