60
improvement across key Cyber GRC workflows with AI
MetricStream's GRC software for technology companies, powered by AI Assistants and Agents, continuously connects risk and compliance intelligence
AI, privacy, and security rules keep changing across markets, and missed exposures can cost customer trust. However, spreadsheets and point solutions can’t keep pace with new products, cloud environments, and acquisitions. Risk programs must move as fast as the business.
Technology companies carry risk across product development, customer data, vendors, and AI systems. MetricStream's GRC solution, powered by AI assistants and agents, absorbs that complexity, recommending actions and executing approved ones within guardrails the organization controls.
60
improvement across key Cyber GRC workflows with AI
40
reduction in risk assessments and control tests
50
lower costs through GRC tool consolidation
Source: MetricStream’s Business Value Calculator
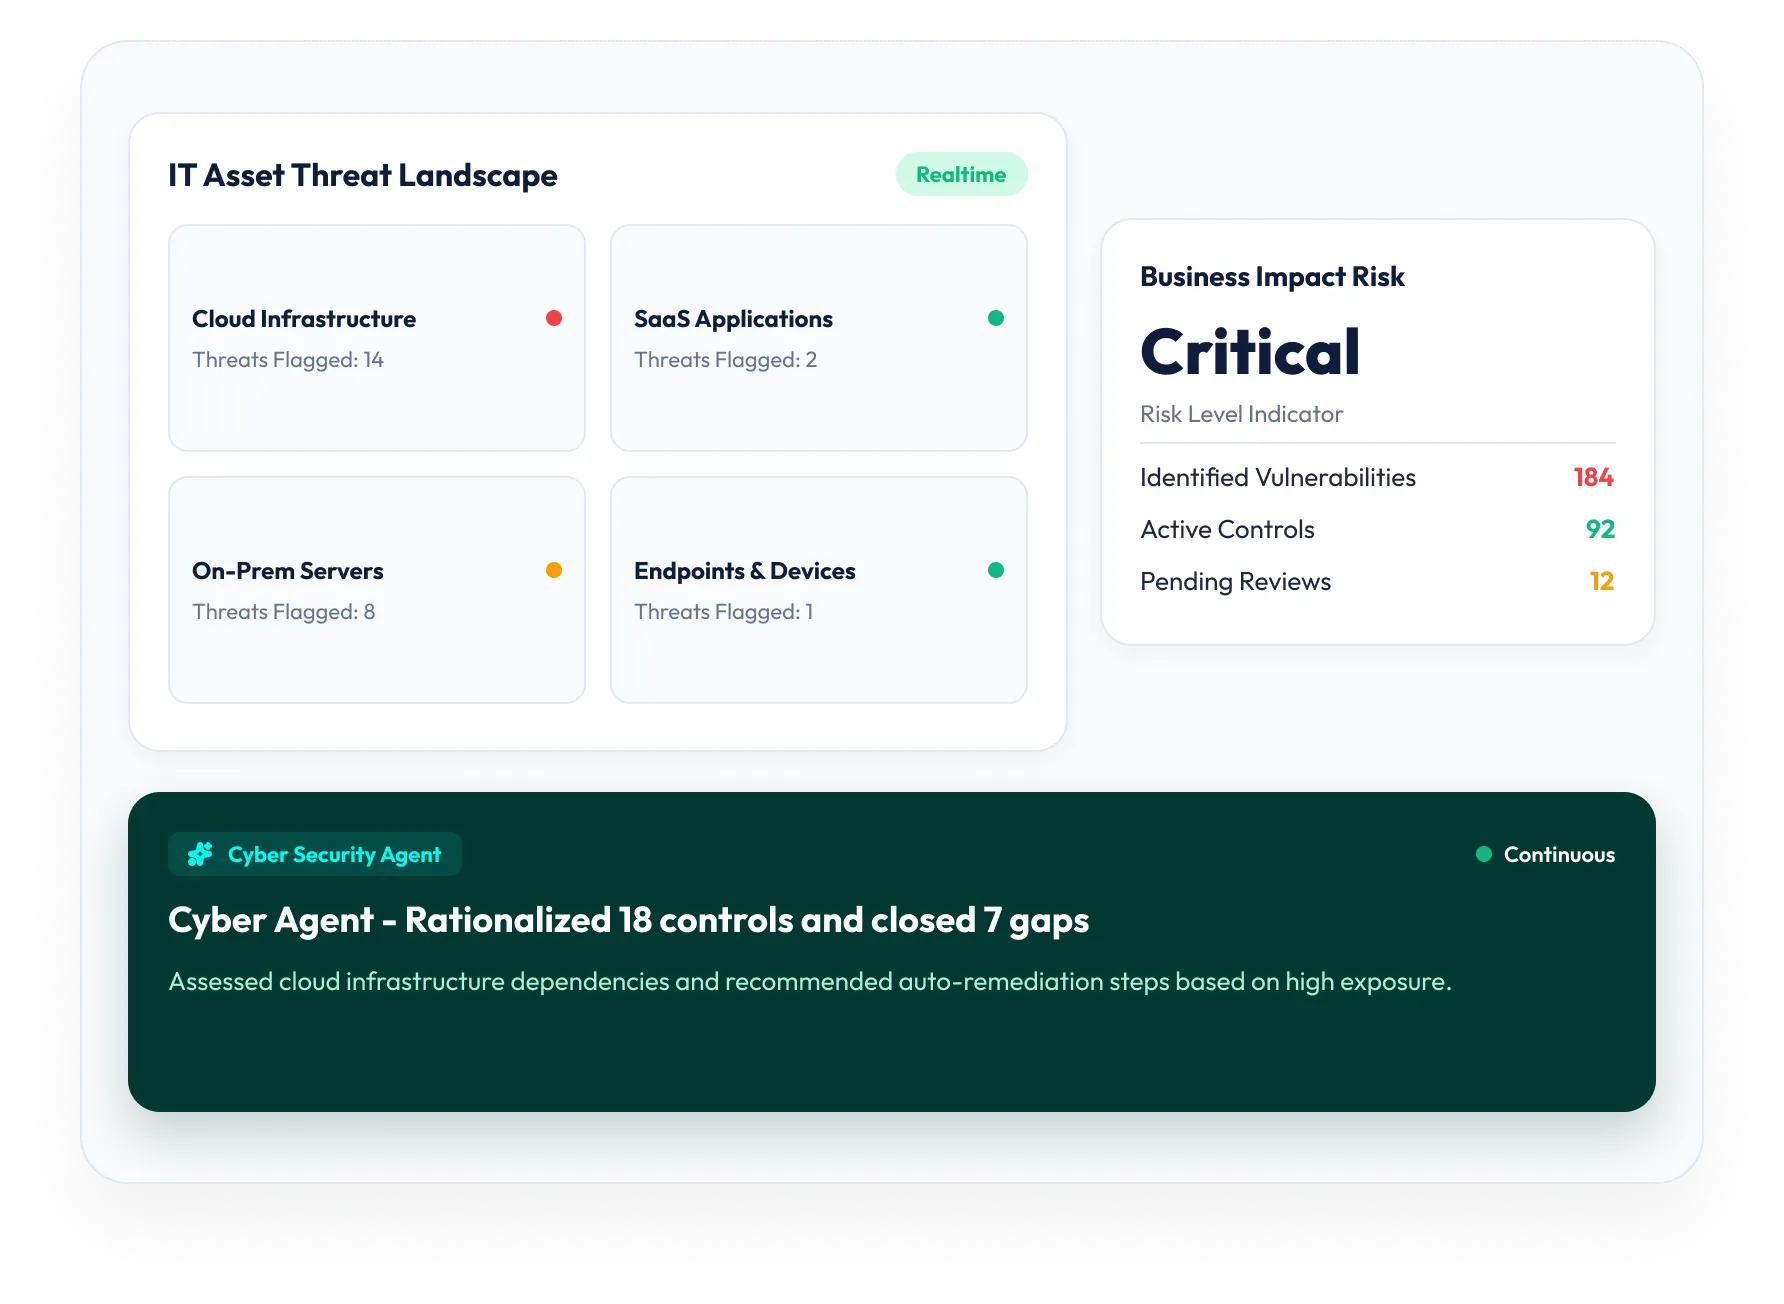
Strengthen cyber resilience with a connected view of IT assets, threats, vulnerabilities, controls, vendors, compliance, and dependencies. AI Assistants and Agents rationalize controls, identify gaps, accelerate assessments, and recommend actions based on business impact.
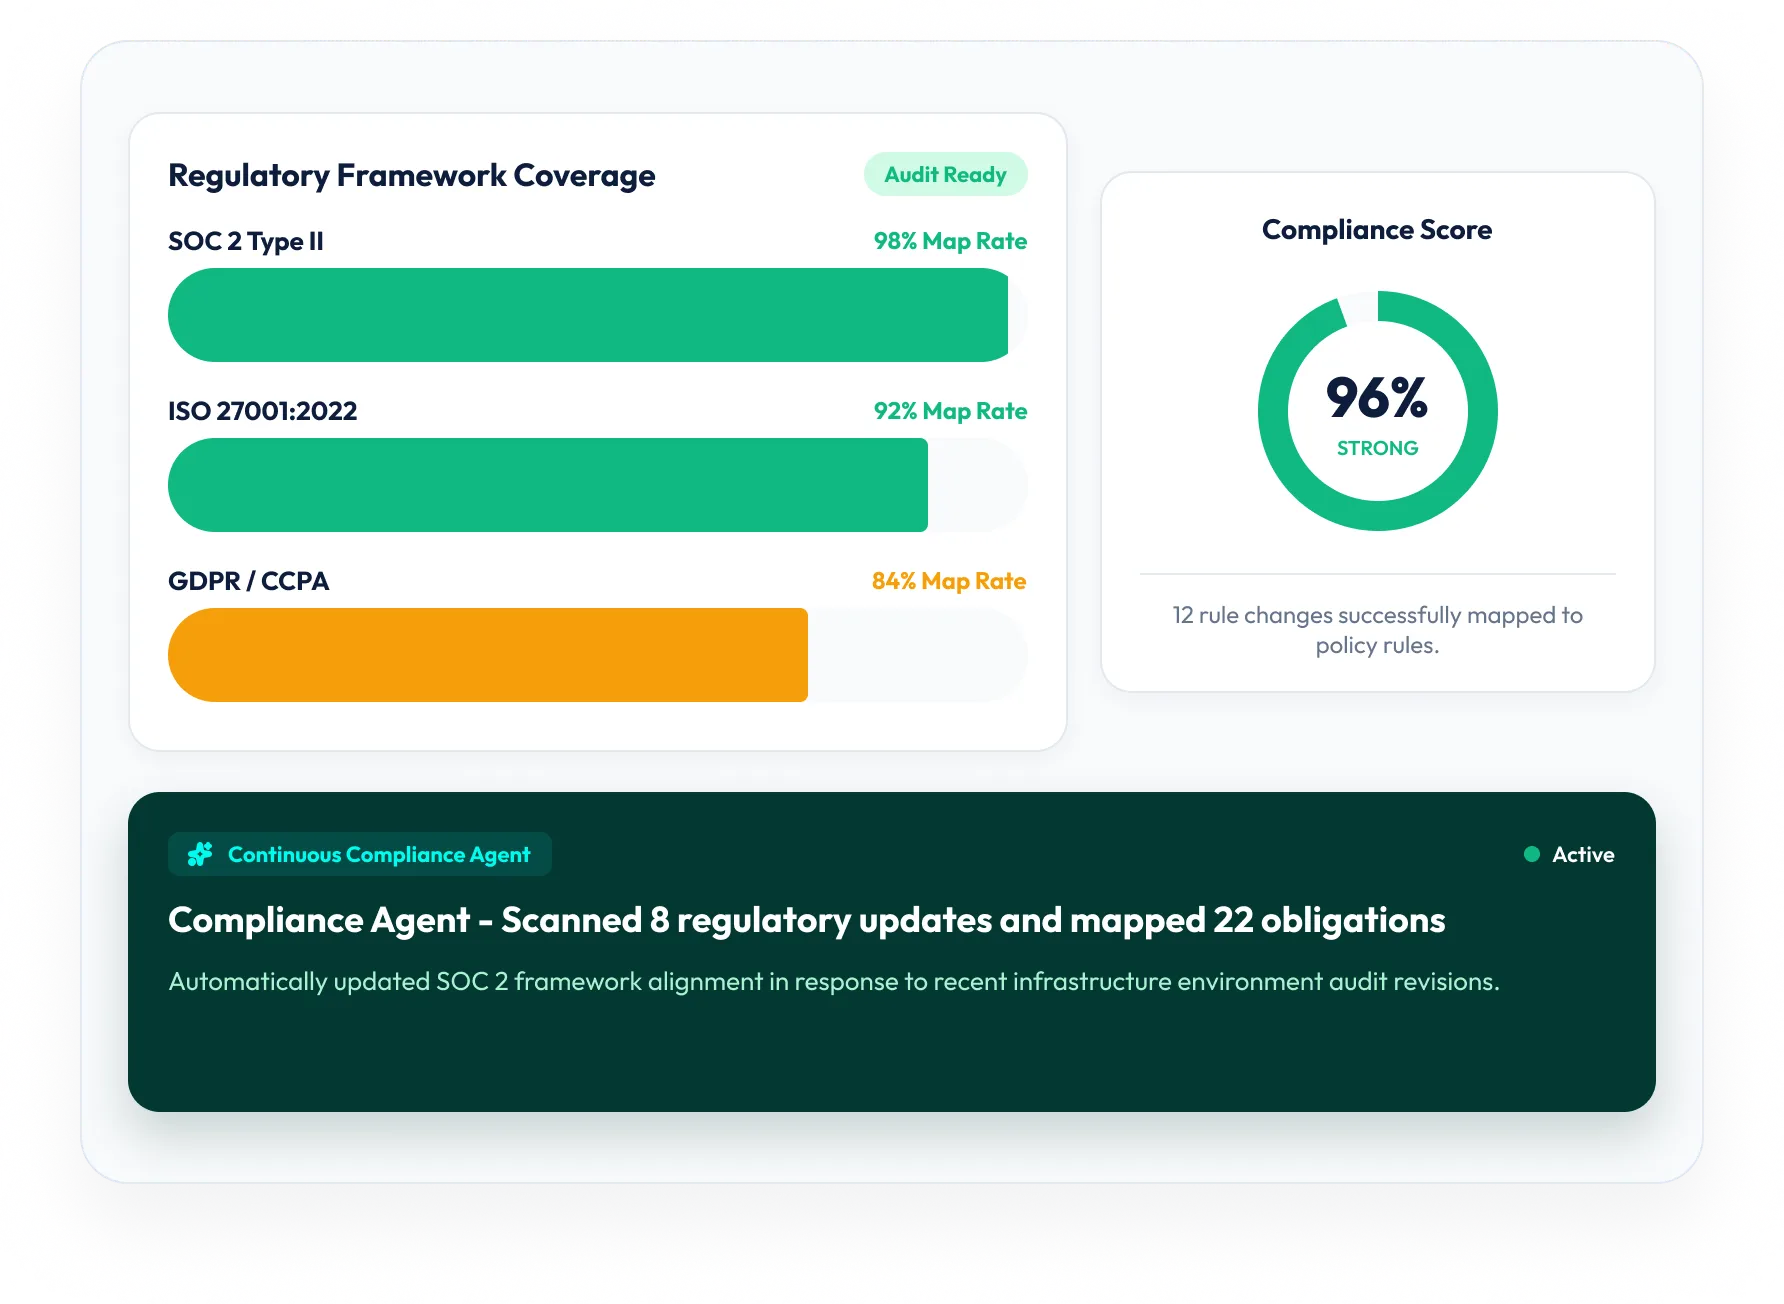
Maintain continuous compliance as regulations evolve across markets by using AI scanning and summarizing obligations to assess impacts, accelerate mapping, identify gaps, and guide actions. Speed up policy creation and communication adoption with Policy Assistant that summarizes and answers source-backed policy questions.
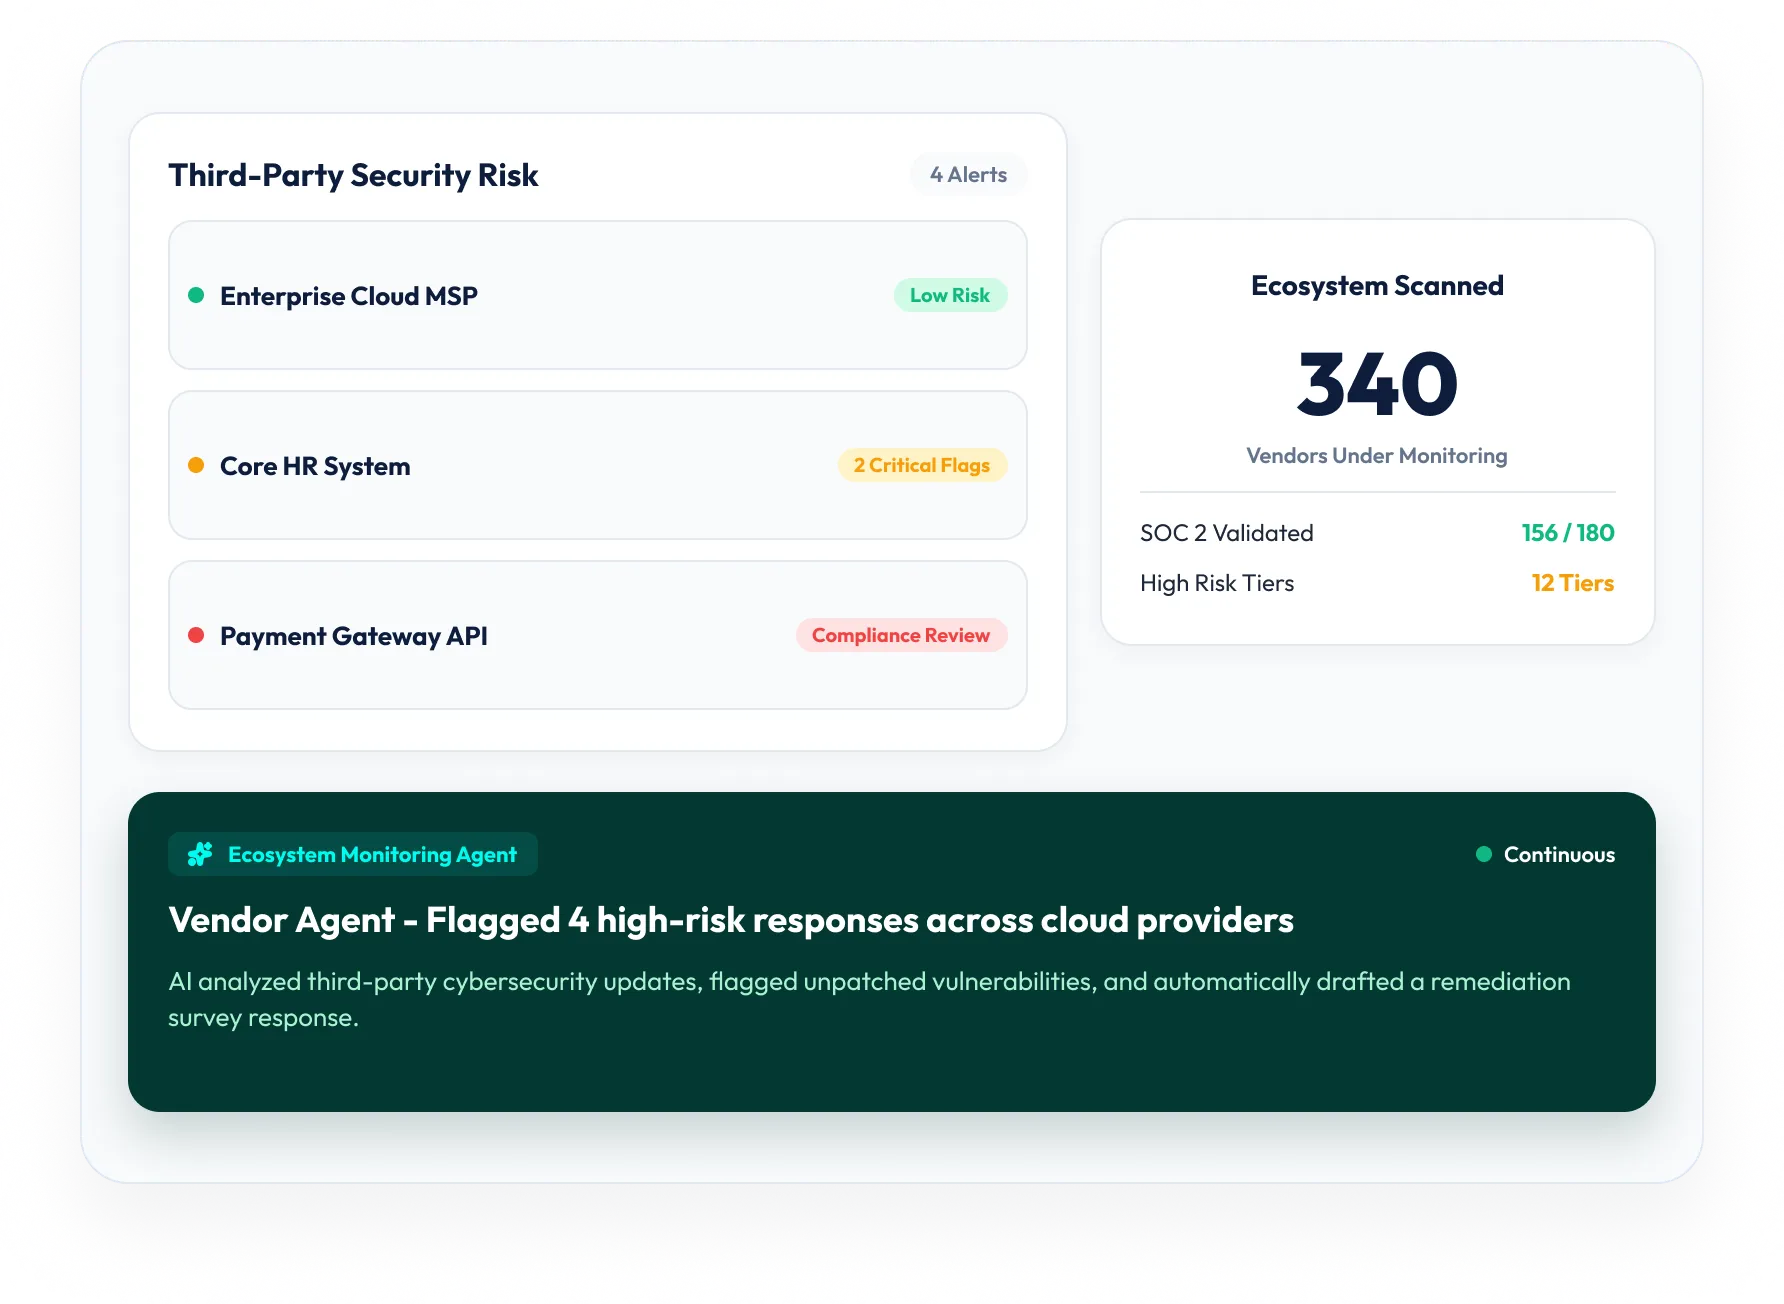
Govern technology vendors and cloud providers from onboarding through offboarding. Third-Party Agents recommend inherent-risk tiers, interpret evidence, flag high-risk responses, monitor external signals, and guide remediation across your vendor ecosystem.
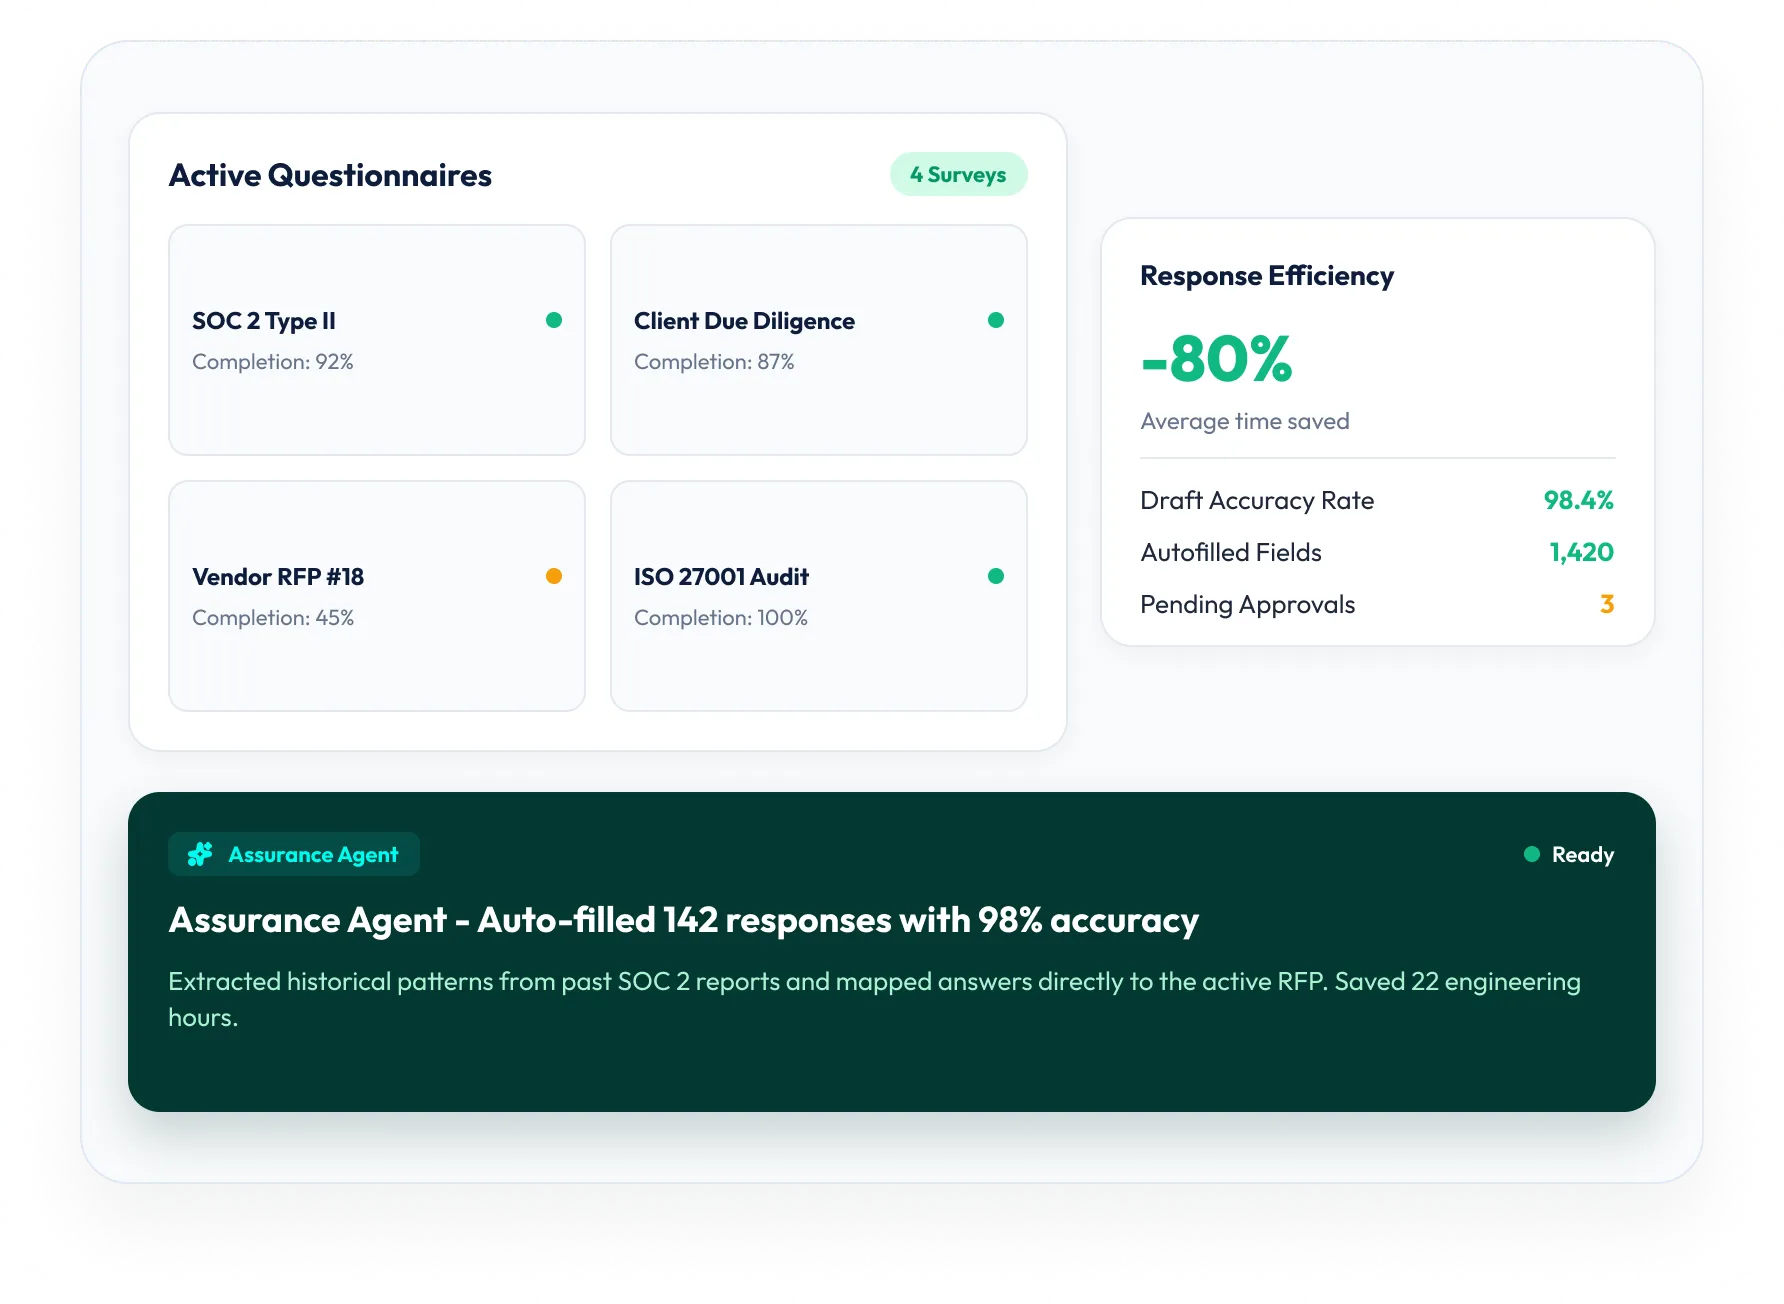
Survey and Questionnaire Autofill generates source-backed draft responses from policies, SOC reports, evidence, and prior submissions. Confidence indicators and citations help your team validate responses before submission, cutting repeated work across customer and compliance assessments.
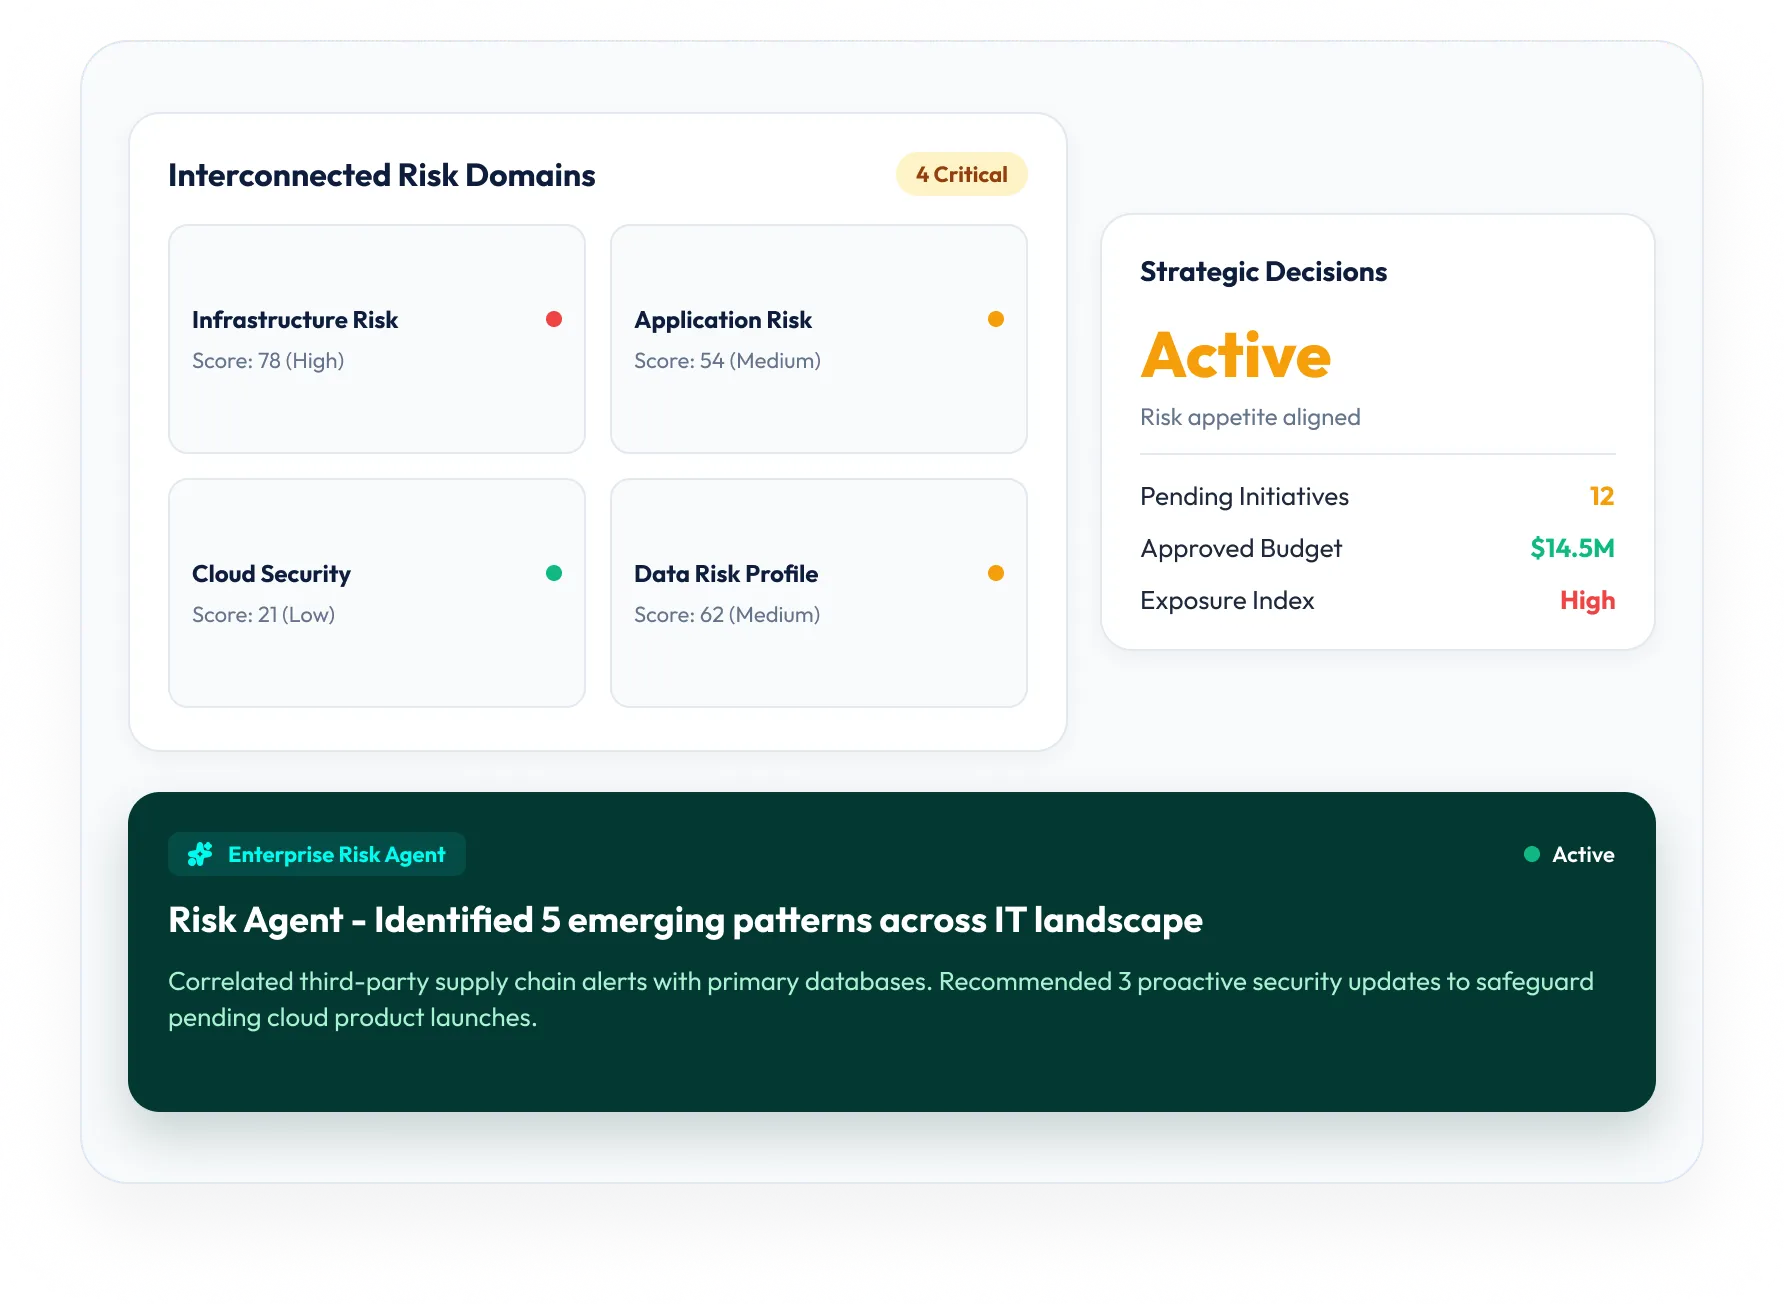
Turn fragmented risk data into actionable enterprise intelligence. Gain a single view of risks across project, operational, cyber, compliance, third-party, and environmental risk domains. A common risk and control taxonomy connects risks, controls, metrics, issues, and actions, while AI Risk Agents identify emerging exposure, assess impact, recommend actions, and deliver executive-ready insights.
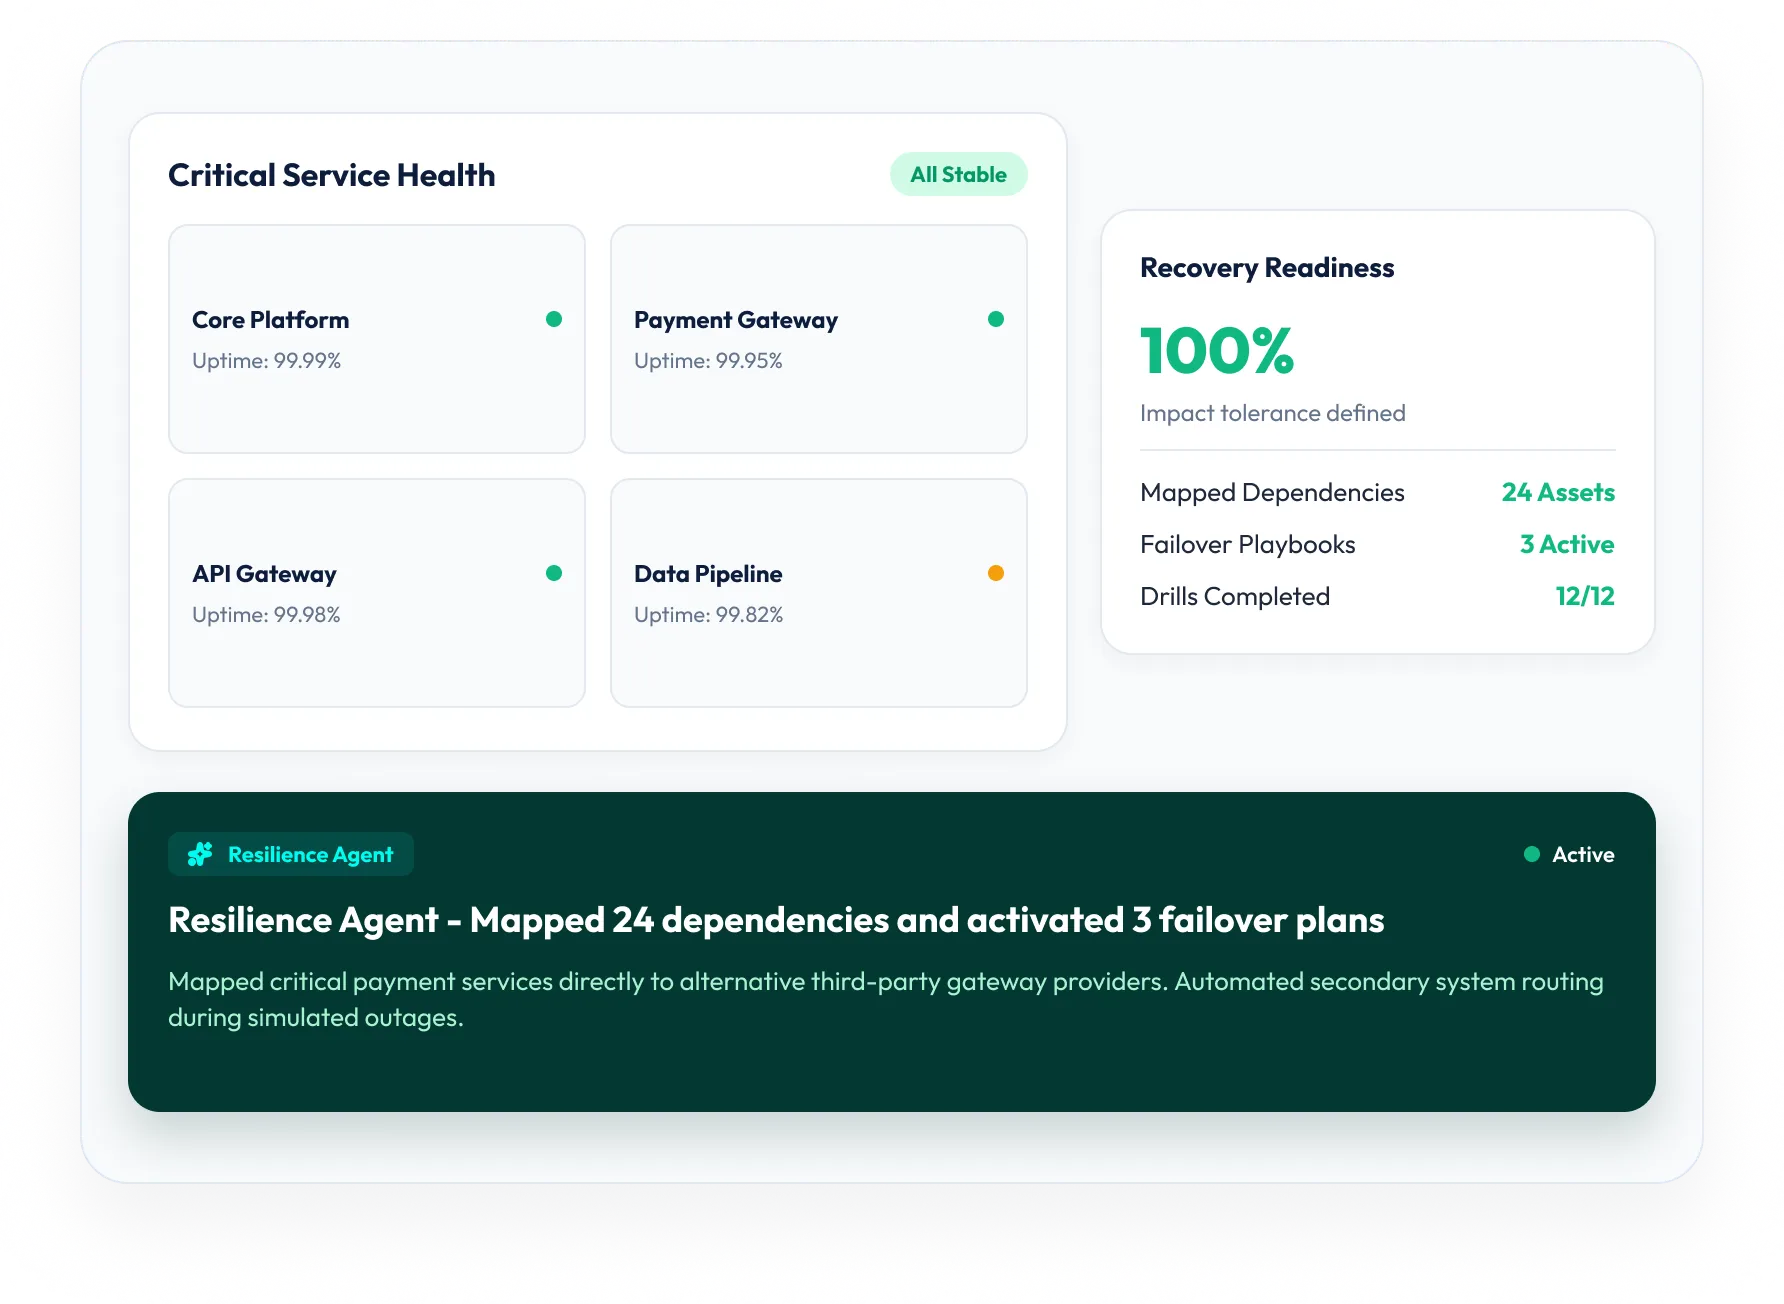
Map critical services to applications, infrastructure, data, people, cloud providers, and recovery resources. Understand dependency gaps, continuous test continuity plans, and manage crisis in a structured way. AI classifies issues and highlights duplicates, recommend improvements and action plans based on incidents, assessments, and exercises.
Relate security findings to applications, data, controls, customers, business services, owners, and potential impact.
Rationalize controls and reuse eligible testing results and approved evidence across overlapping assurance requirements.
Draft source-backed questionnaire responses with citations and confidence indicators while keeping reviewers in control.
Connect AI use cases to obligations, policies, risks, controls, evidence, issues, third parties, and accountable owners.
Understand how cloud providers, software vendors, data processors, and contractors affect security, compliance, and resilience.
Adapt risk methods, workflows, controls, integrations, and reporting as products, acquisitions, and markets change.
Use our interactive ROI calculator, built by Forrester, to estimate what Enterprise GRC could deliver for your organization. Enter details such as annual revenue, number of GRC tools, and compliance exposure to see your potential savings, payback period, and return on investment.
Calculate My ROI
Analyst Report
Download the excerpt to see why MetricStream was recognized as a GRC Leader in 2025.
Download Now
eBook
A CISO's guide to outsmarting cyber risk before it outsmarts you.
Read More
Case Study
Read how a global bank enhanced business decision-making by successfully moving from a traditional approach to a single, connected GRC system.
Read More
Whitepaper
Learn how GRC leaders are adopting AI responsibly and proving measurable ROI at scale.
Read MoreTechnology companies face GRC challenges driven by rapid innovation, shifting customer expectations, evolving regulatory policies, and continuous market disruption. Evolving requirements around data privacy, AI ethics, and cybersecurity are reshaping how tech companies operate. The growing complexity of third-party ecosystems, coupled with rising cyber threats, has heightened the urgency for a more resilient and transparent risk management approach, one that keeps pace with the speed of innovation without compromising governance or compliance.
MetricStream's Regulatory Compliance solution helps technology companies centralize data privacy and security compliance requirements across geographies, enabling faster adaptation to evolving regulations. The platform supports tracking and management of changing regulatory obligations, implementation of controls to ensure compliance, and timely compliance assessments, helping tech organizations stay on top of requirements such as GDPR, CCPA, and sector-specific cybersecurity mandates without disrupting operations or innovation cycles.
MetricStream's Cyber GRC solution enables technology companies to adopt a risk-based approach to cybersecurity, implementing a unified real-time view of risk and compliance posture with connected risk, audit, and compliance programs. Organizations can quickly prioritize investments and action plans to reduce risk exposure, align with strategic goals and business objectives, and embed best practices and frameworks, including ISO 27001, NIST CSF, and NIST SP800-53, for rapid implementation and strengthened cyber resilience.
MetricStream's Enterprise Risk Management solution enables technology companies to shift from working in silos, using error-prone spreadsheets and multiple point solutions, to a connected, scalable, and efficient GRC platform. The solution consolidates risk management across all business functions and provides a 360-degree view of enterprise risks in one place, including strategic, cyber, third-party, product, and compliance risks. Organizations can make informed, data-driven decisions that enhance resilience and support sustainable growth in a competitive market.
MetricStream's Third-Party Risk Management solution helps technology companies effectively manage risk associated with their vendor ecosystem and ensure vendor compliance with industry standards and regulatory requirements. The platform automates end-to-end vendor risk management processes, including information gathering, onboarding, real-time monitoring, risk and compliance assessments, and risk mitigation, enabling tech organizations to innovate faster, decrease costs, and increase agility while maintaining strong governance over their supply chain.
MetricStream helps technology companies demonstrate risk and compliance maturity and successfully pass audits by adopting an integrated approach to risk, resilience, and compliance management. The platform connects risk, audit, and compliance programs into a single framework with consistent controls, enabling real-time visibility and proactive issue resolution. This unified approach reduces audit preparation effort, strengthens the audit trail, and gives auditors and regulators a clear picture of the organization's governance posture.
According to MetricStream customer responses and the GRC Journey Business Value Calculator, technology companies using MetricStream have achieved a 90% reduction in the time taken to manage compliance activities, a 50% savings in time and costs for third-party assessments and risk identification, and a 67% improvement in risk reporting visibility and efficiency for the executive management and board. These outcomes reflect the platform's ability to streamline governance and free up risk teams to focus on strategic priorities.
MetricStream enables technology companies to balance rapid innovation with strong governance by connecting data, processes, and teams across risk, compliance, cyber, and third-party functions in a single platform. By providing real-time visibility, automated workflows, and consistent controls, MetricStream empowers enterprises to mitigate risks, improve governance maturity, and drive innovation securely — ensuring that speed to market does not come at the cost of compliance or security posture.
AI capabilities within MetricStream's technology industry GRC solution accelerate risk-based decision-making and governance across the enterprise. AI automates risk identification, assessment, and reporting workflows, reducing the time and cost of managing complex compliance programs. AI capabilities across the platform surface emerging risks, flag control deficiencies, and recommend actions, enabling technology risk and compliance teams to operate more proactively and efficiently at scale.
As technology companies adopt AI across their products and operations, governance requirements around AI ethics, fairness, transparency, and accountability are increasing. MetricStream's integrated GRC platform helps organizations track and manage AI-related regulatory obligations, map AI ethics policies to controls, and perform compliance assessments against emerging AI governance frameworks. This enables tech companies to demonstrate responsible AI practices to customers, regulators, and board members.