67%
improvement in risk reporting visibility
Move from siloed GRC to continuous intelligence across operational risk, regulatory change, and compliance, powered by MetricStream AI Assistants and Agents, trusted by 100+ banking and financial institutions.
Built to simplify the complexity of financial services while amplifying outcomes, MetricStream's GRC solution, powered by AI assistants and agents, advises, recommends, and executes approved actions within guardrails you control.
67%
improvement in risk reporting visibility
90
reduction in time spent managing compliance activities
80
decrease in third-party onboarding time
Source: MetricStream's Business Value Calculator
With obligations from OFAC, SEC, OCC, FINRA, FCA, PRA, and more, banks can’t afford blind spots. Yet years of point solutions for risk, compliance, vendors, and cybersecurity have left a siloed view. Banks and financial institutions need to change how they manage risk.
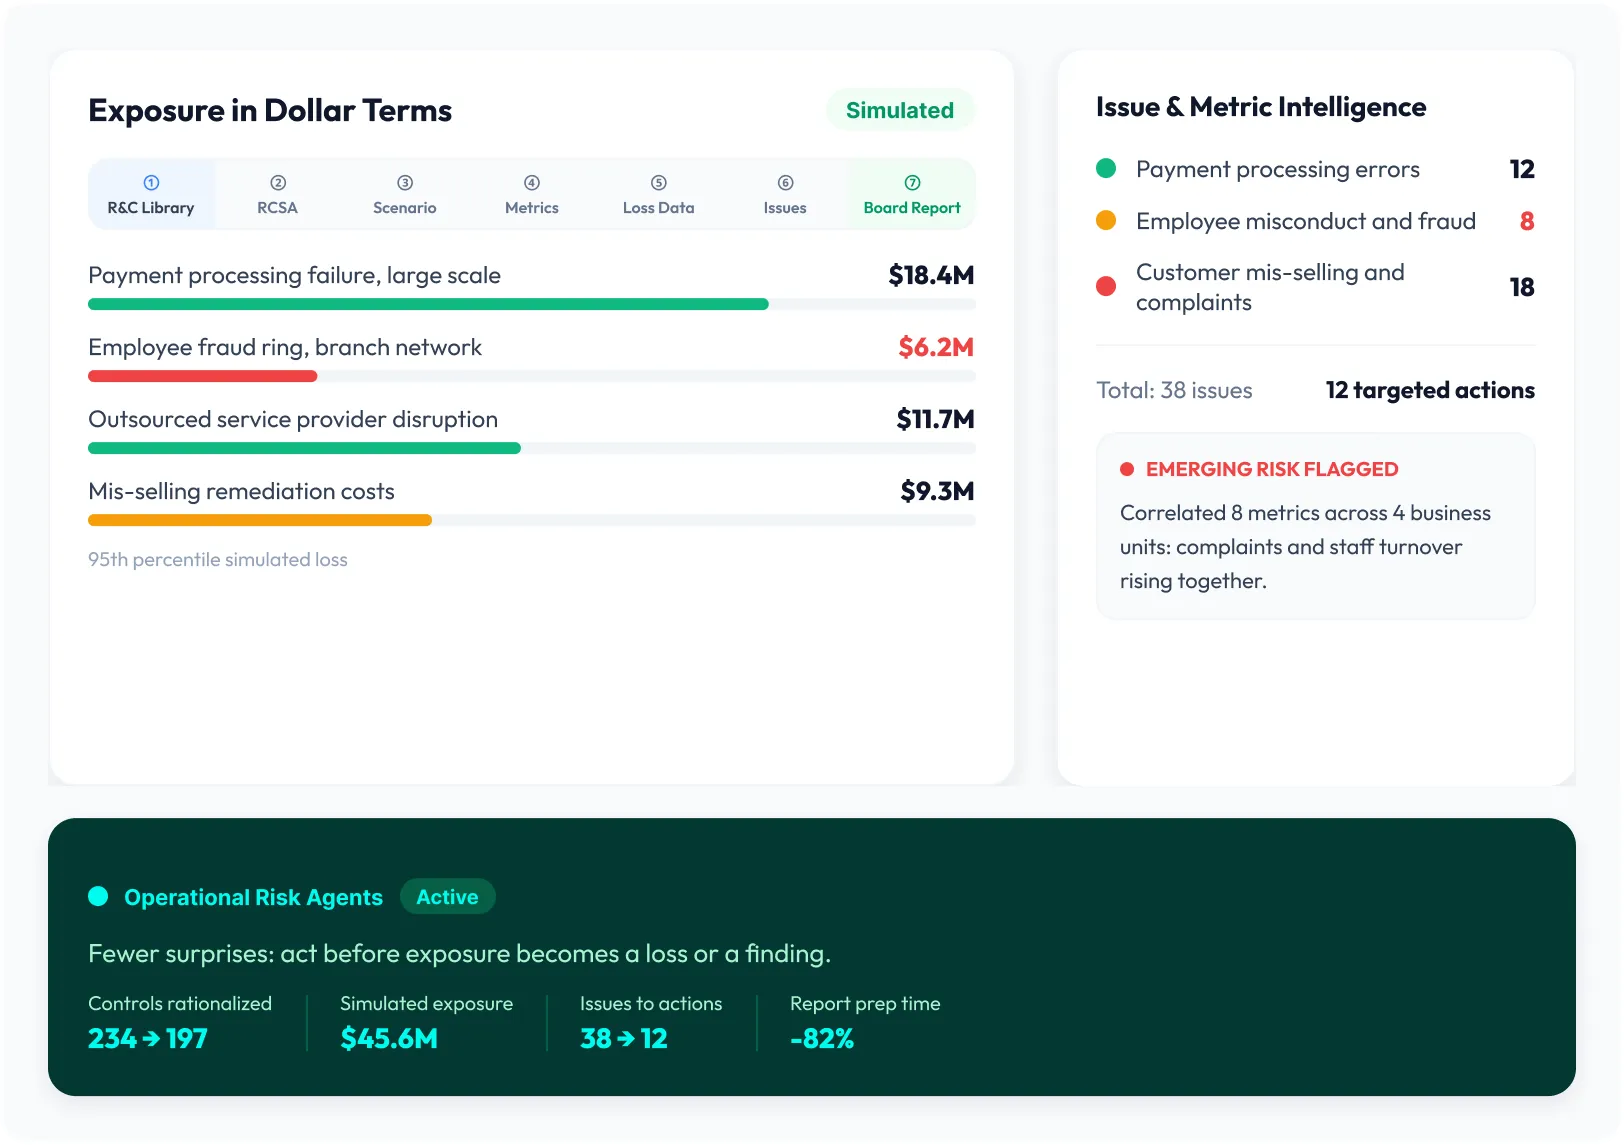
MetricStream Operational Risk Management with AI assistants and agents gives you a single view of risk. AI runs through the entire flow: a unified risk and control library, Risk and Control Self-Assessments (RCSA), scenario analysis, metrics monitoring, loss data management, issue and action management, and board and regulator reporting. It rationalizes controls, quantifies exposure through scenario simulations, correlates metrics to flag emerging risks, classifies and clusters issues by root cause, and generates risk-intelligence narratives. Banks and financial services can now operate with fewer surprises, quantify risk in dollar terms, and act before exposure becomes a loss or a finding.
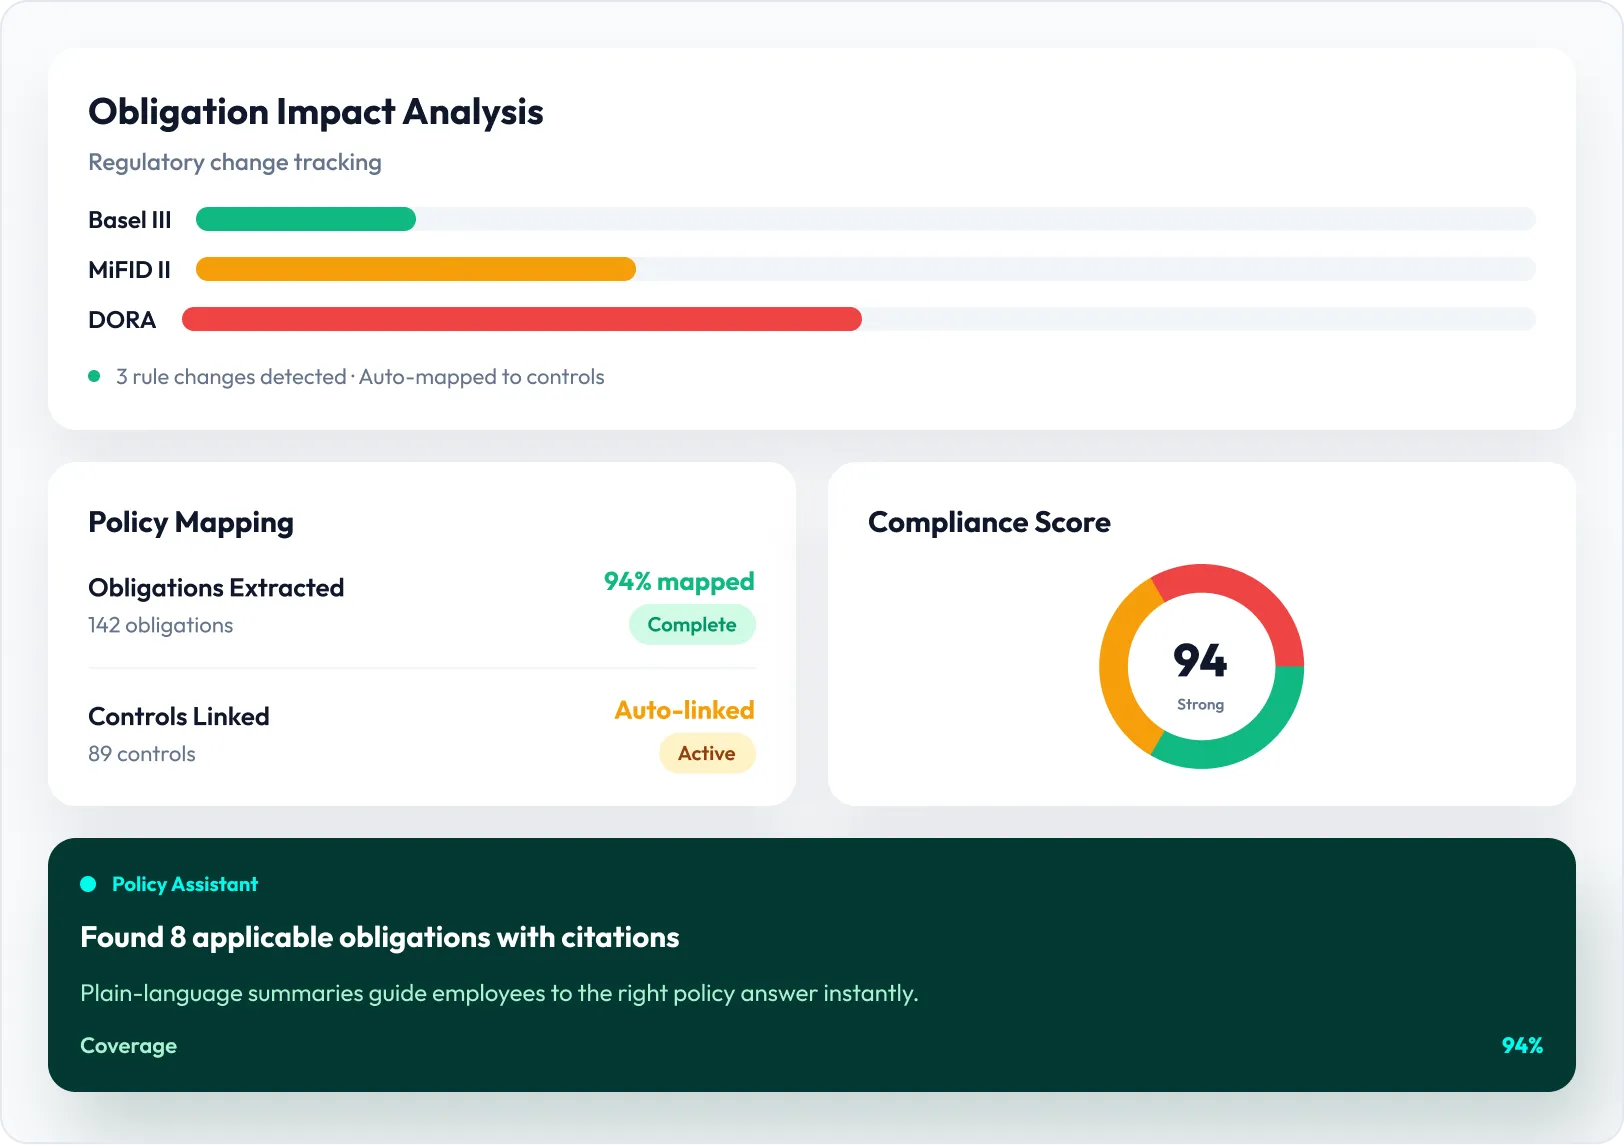
AI extracts obligations from trusted sources, assesses applicability to your bank, and maps each obligation to the policies and controls it affects. Impact analysis flags what changes occur the moment a rule is triggered, while AI tests control effectiveness, gathers evidence, and routes remediation automatically. Compliance teams manage cases, incidents, and exams from a single workflow, replacing several disconnected systems. The Policy Assistant finds the right policy with citations attached, summarizes it in plain language, and guides employees to an answer, with assisted data capture speeding each update.
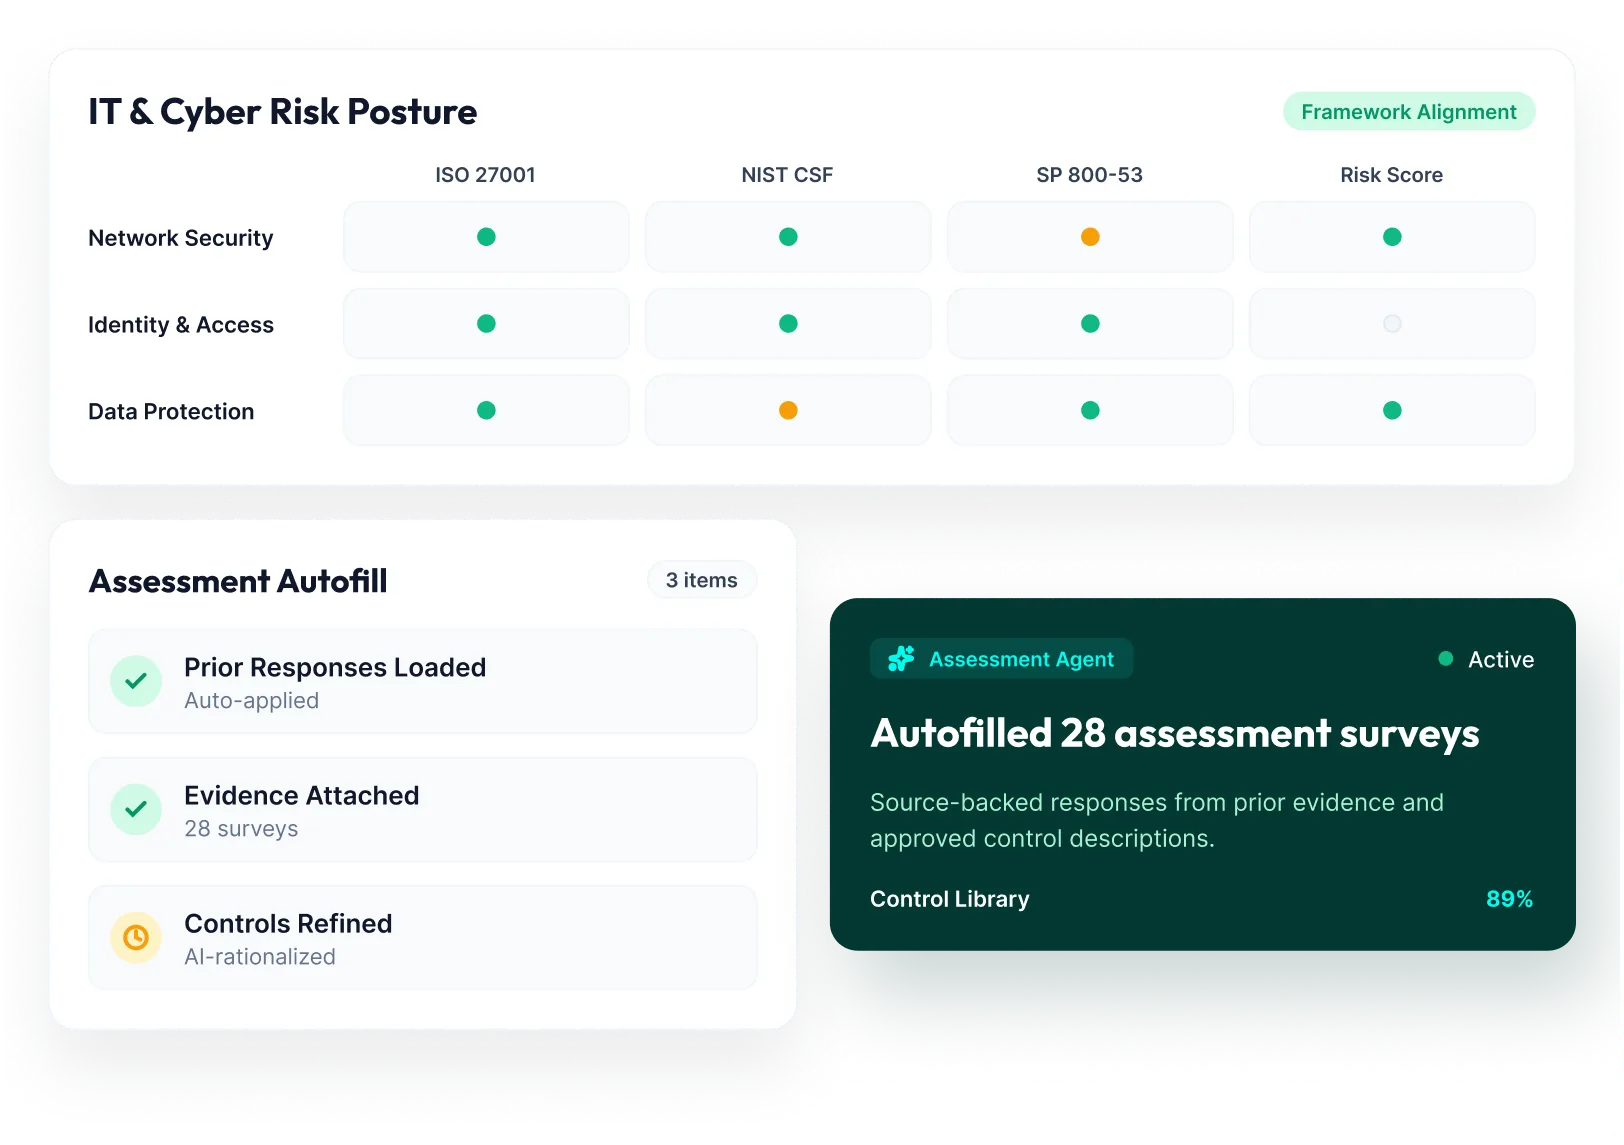
See your IT and cyber risk posture in a single, connected view, and prioritize security investments based on the exposure they reduce. AI autofills assessment surveys using prior responses and evidence, rationalizes your IT control library, and automatically refines control descriptions. Guided navigation and contextual help walk teams through each assessment, built on frameworks including ISO 27001, NIST CSF, and NIST SP 800-53.
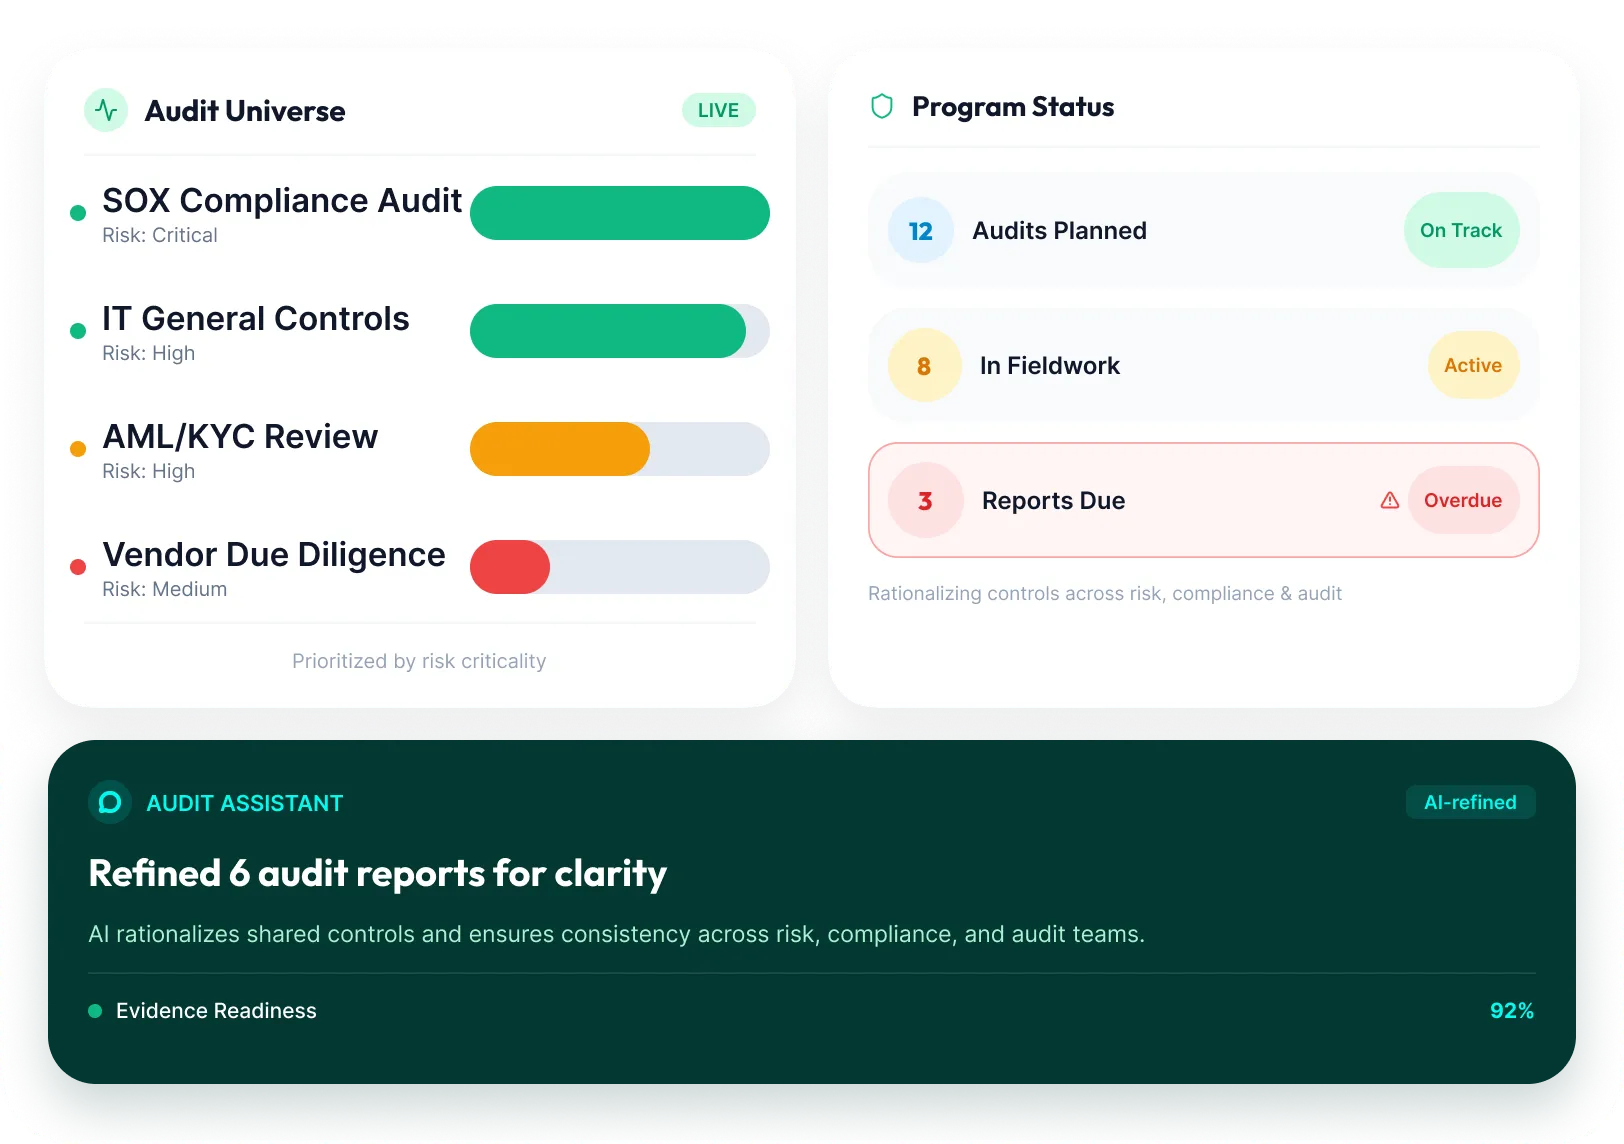
Manage audit projects, risks, and controls from a single place, and prioritize each audit by risk criticality, replacing fixed cycles. AI refines audit reports for clarity and consistency, and rationalizes controls shared across risk, compliance, and audit teams. Real-time dashboards give auditors a live picture of program status. Evidence stays ready between exams, and teams respond to auditors with confidence rather than scrambling to assemble proof. Contextual help, guided navigation, and assisted data capture speed up planning, scheduling, and fieldwork.
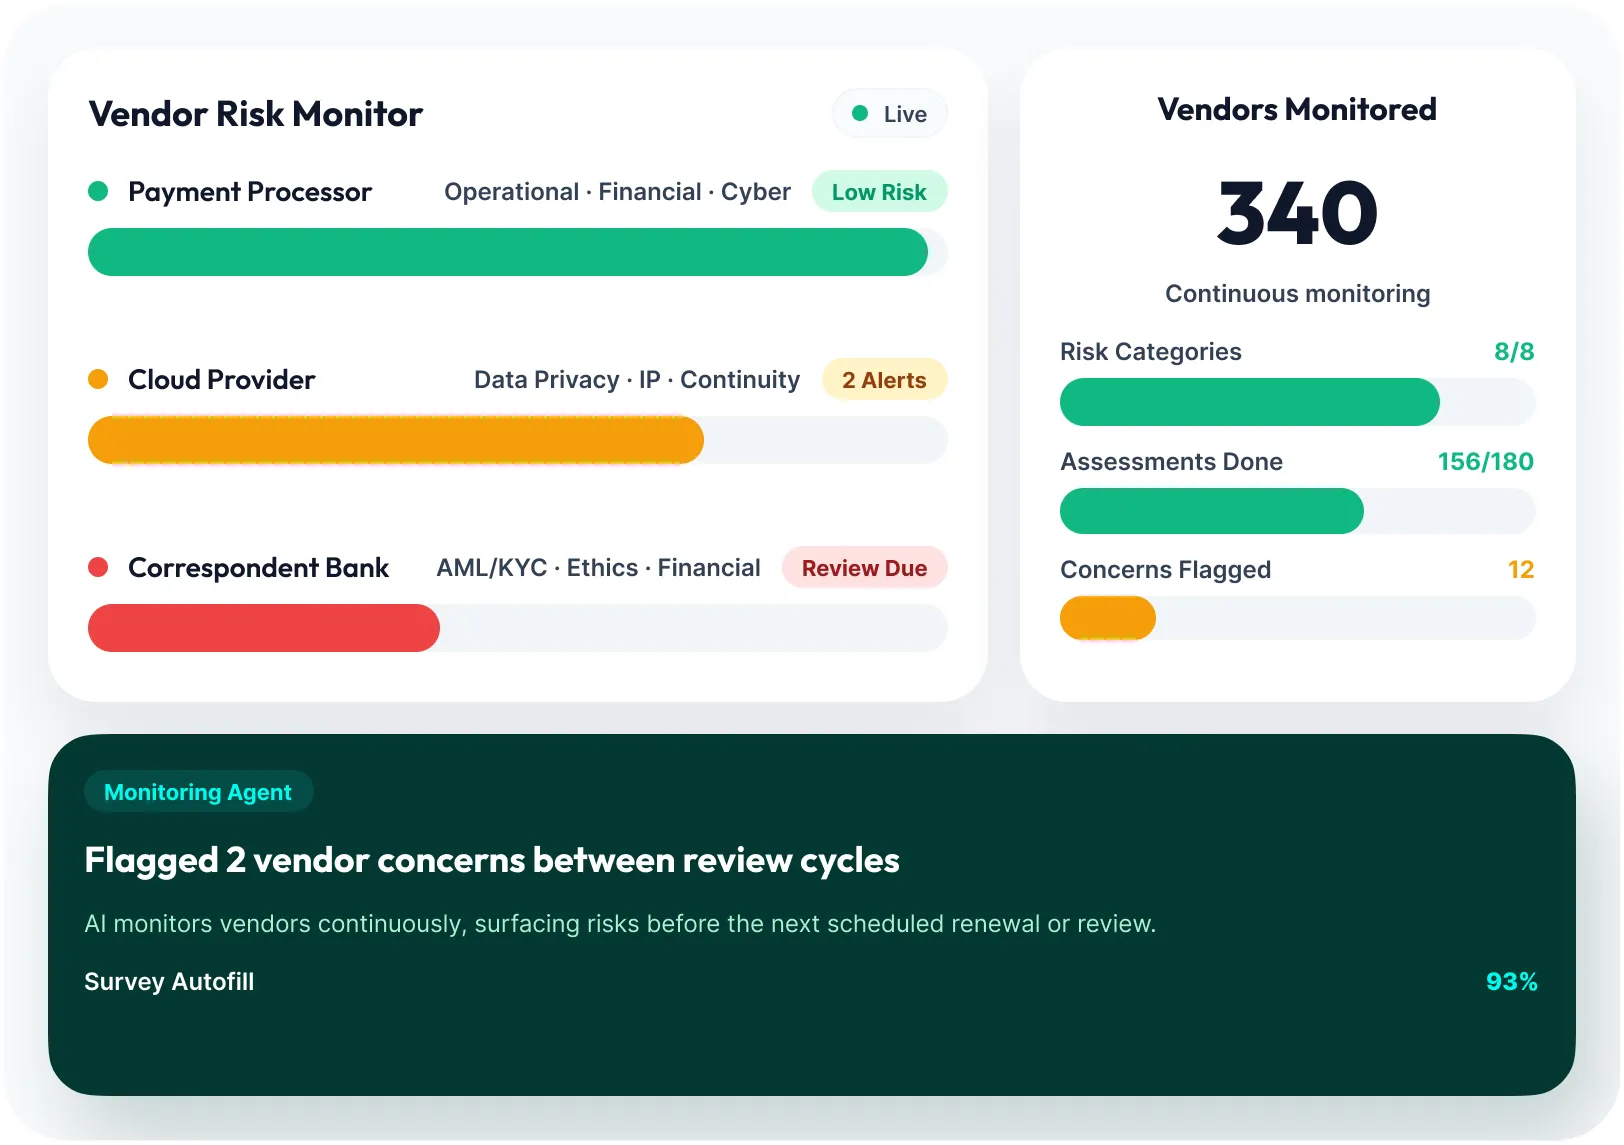
Track risk across your third-party ecosystem with a single, real-time view, spanning operational, data privacy, ethics, and corporate compliance, intellectual property, business continuity, cybersecurity, anti-bribery and anti-corruption, and financial risk. AI continuously monitors vendors and correspondents, flagging concerns between review cycles rather than at renewal. Survey autofill pulls prior responses and evidence into each assessment, while contextual help, guided navigation, and assisted data capture speed scoring, reporting, and mitigation.
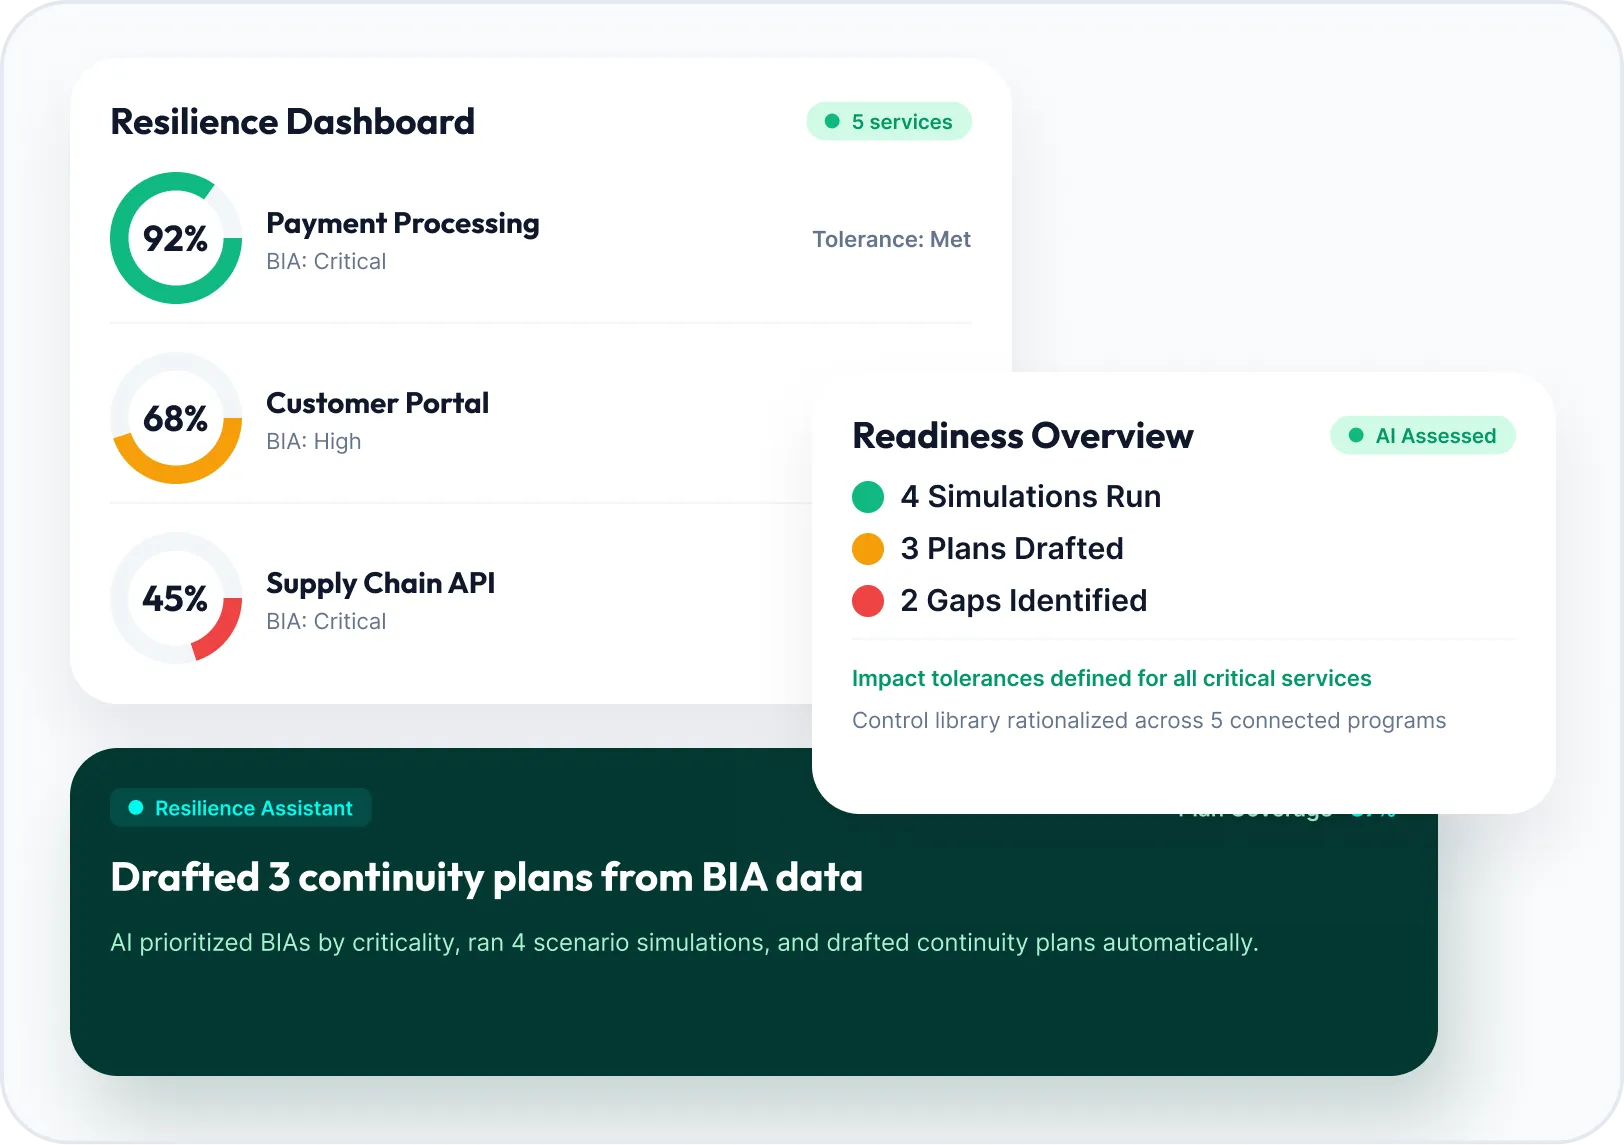
A single platform connects operational, cyber, technology, third-party, and business resilience into a unified view of readiness. Critical processes and services get identified and mapped in advance, with risk appetite, impact tolerances, and scenario simulations run before disruption hits, not after. The Resilience Assistant prioritizes BIAs by criticality, runs scenario simulations, and drafts continuity plans, while control rationalization keeps the underlying risk and control library current across each connected program.
Regulation / Framework
01 / 11
What it requires
Categorize losses by business line and event type; hold capital against operational risk
How MetricStream helps
AI classifies loss events and rationalizes the risk and control library
Risk, compliance, audit, and resilience intelligence update continuously, with AI recommending and executing approved actions in the moment.
Constantly recognized by industry analysts including Chartis, Gartner, Forrester, IDC, and others.
Fortune 500 banks and financial services trust MetricStream to strengthen GRC programs and deliver value.
Decades of hands-on banking GRC experience, with experts and AI engineers who deploy and support your program at every milestone.
Purpose-built assistants and agents for Basel, multi-regulator compliance, SOX, resilience, third-party, and cyber risk.
Easily configure risk taxonomies, assessment templates, and workflows to match your GRC programs, organizational processes, and hierarchy.
Use our interactive ROI calculator, built by Forrester, to estimate what Enterprise GRC could deliver for your organization. Enter details such as annual revenue, number of GRC tools, and compliance exposure to see your potential savings, payback period, and return on investment.
Calculate My ROI
Analyst Report
Download the excerpt to see why MetricStream was recognized as a GRC Leader in 2025.
Download Now
eBook
A CISO's guide to outsmarting cyber risk before it outsmarts you.
Read More
Case Study
Learn how MetricStream helped a leading credit asset management firm transform and streamline operational risk, third-party, and business continuity management programs.
Read More
Whitepaper
Learn how GRC leaders are adopting AI responsibly and proving measurable ROI at scale.
Read MoreBanking and financial services organizations face some of the most complex governance, risk, and compliance (GRC) challenges across any industry. These include navigating stringent regulatory requirements from bodies such as OFAC, SEC, OCC, FINRA, FFIEC, CFPB, FRB, EBA, FCA, BOE, APRA, and PRA, while simultaneously managing escalating cyber threats, growing third-party ecosystems, and increasing expectations around ESG performance and operational resilience.
MetricStream supports operational resilience by providing a unified platform that integrates workflows for managing operational risk, cyber risk, compliance risk, third-party risk, and business continuity planning. Financial institutions can identify and analyze critical operations, determine risk appetite, set risk tolerances, and run scenario analysis and simulations, helping them prepare for and prevent potential disruptions before they affect service delivery or regulatory standing.
MetricStream provides access to a broad library of international, federal, and state regulations relevant to financial services, enabling organizations to track regulatory changes, establish compliance management workflows, update and communicate policy changes, and manage regulatory exams and case incidents. The solution helps compliance teams spend less time on manual tracking and more time responding strategically to evolving obligations from regulators such as the FCA, SEC, EBA, and APRA.
AI capabilities in MetricStream's banking and financial services solution automate and streamline several high-effort tasks. These include AI-powered data mapping that identifies gaps, missing linkages, and redundancies in risk and control data; AI-driven cognitive insights that flag control deficiencies and overlaps; semantic analytics that identify and recommend actions for issues; and intelligent summarization for real-time audit insights. Together, these capabilities enable faster, data-backed decisions across risk, audit, and compliance functions.
MetricStream's Third-Party Risk Management solution provides financial institutions with an integrated, real-time view of risks across their vendor and supplier ecosystem. Organizations can perform assessments, scoring, reporting, and risk mitigation across multiple risk domains, including operational risk, data privacy, cybersecurity, anti-bribery and anti-corruption, financial risk, and business continuity. This approach enables proactive identification and mitigation of third-party and fourth-party risks throughout the full supplier lifecycle.
MetricStream's Cyber GRC solution helps financial institutions gain enterprise-wide visibility into IT and cyber risk posture, prioritize cybersecurity investments, and adopt industry best-practice frameworks, including ISO 27001, NIST CSF, and NIST SP800-53. The solution enables advanced cyber risk quantification, expressing risk exposure in monetary terms, so security and risk teams can make cost-effective decisions about which risks to accept, mitigate, or transfer.
MetricStream's Internal Audit solution helps banking organizations centrally manage all audit projects and execute a risk-based approach that prioritizes audit tasks and resources based on risk criticality. Audit planning, scheduling, and execution are streamlined through intuitive dashboards, real-time data access, and AI capabilities that manage audit issues. The result is improved auditor productivity, better collaboration across audit teams, and a clearer picture of audit posture across the business.
According to MetricStream customer responses and the GRC Journey Business Value Calculator, banking and financial services organizations using MetricStream have achieved a 67% improvement in risk reporting visibility and efficiency for executive management and the board, a 90% reduction in the time taken to manage compliance activities, and an 80% decrease in third-party onboarding time. These outcomes reflect the platform's impact on reducing manual effort, accelerating risk decisions, and improving governance maturity.
MetricStream's Operational Risk Management solution supports Basel Accord requirements by enabling organizations to manage internal risk events and losses in compliance with industry regulations. The platform supports categorizing and classifying business lines and loss events based on Basel standards, and provides AI-infused issue and action workflows that use semantic analytics to identify, flag, and recommend actions for operational risk issues, helping banks meet both quantitative and qualitative Basel expectations.
MetricStream's GRC platform is designed for the full spectrum of banking and financial services organizations, including retail and commercial banks, investment management firms, capital markets institutions, insurance-linked financial groups, and financial holding companies operating across multiple geographies. Organizations such as Standard Chartered Bank and LSEG (London Stock Exchange Group) have implemented MetricStream solutions to strengthen risk management, compliance, and operational resilience at an enterprise scale.