133
return on investment over three years
Know where risk sits across research, manufacturing, and patient safety to drive informed decisions and actions, and ensure continuous compliance with MetricStream's life sciences GRC powered by AI assistants and agents.
Patient safety, product quality, and data integrity face constant scrutiny, so oversight gaps put patients and products at risk. Meanwhile, control evidence sits scattered across quality, clinical, and supplier systems. Risk management must be defensible by design.
Life sciences organizations carry risk across clinical research, manufacturing, suppliers, and patient data. MetricStream's GRC solution, powered by AI assistants and agents, helps streamline the complexity, recommending actions, and executing approved ones within guardrails that the organization controls.
133
return on investment over three years
$8.4M
three-year, risk-adjusted present-value benefits
<6 mo
payback period
Source: The Total Economic Impact™ of MetricStream Enterprise GRC, a commissioned study conducted by Forrester Consulting, March 2026.
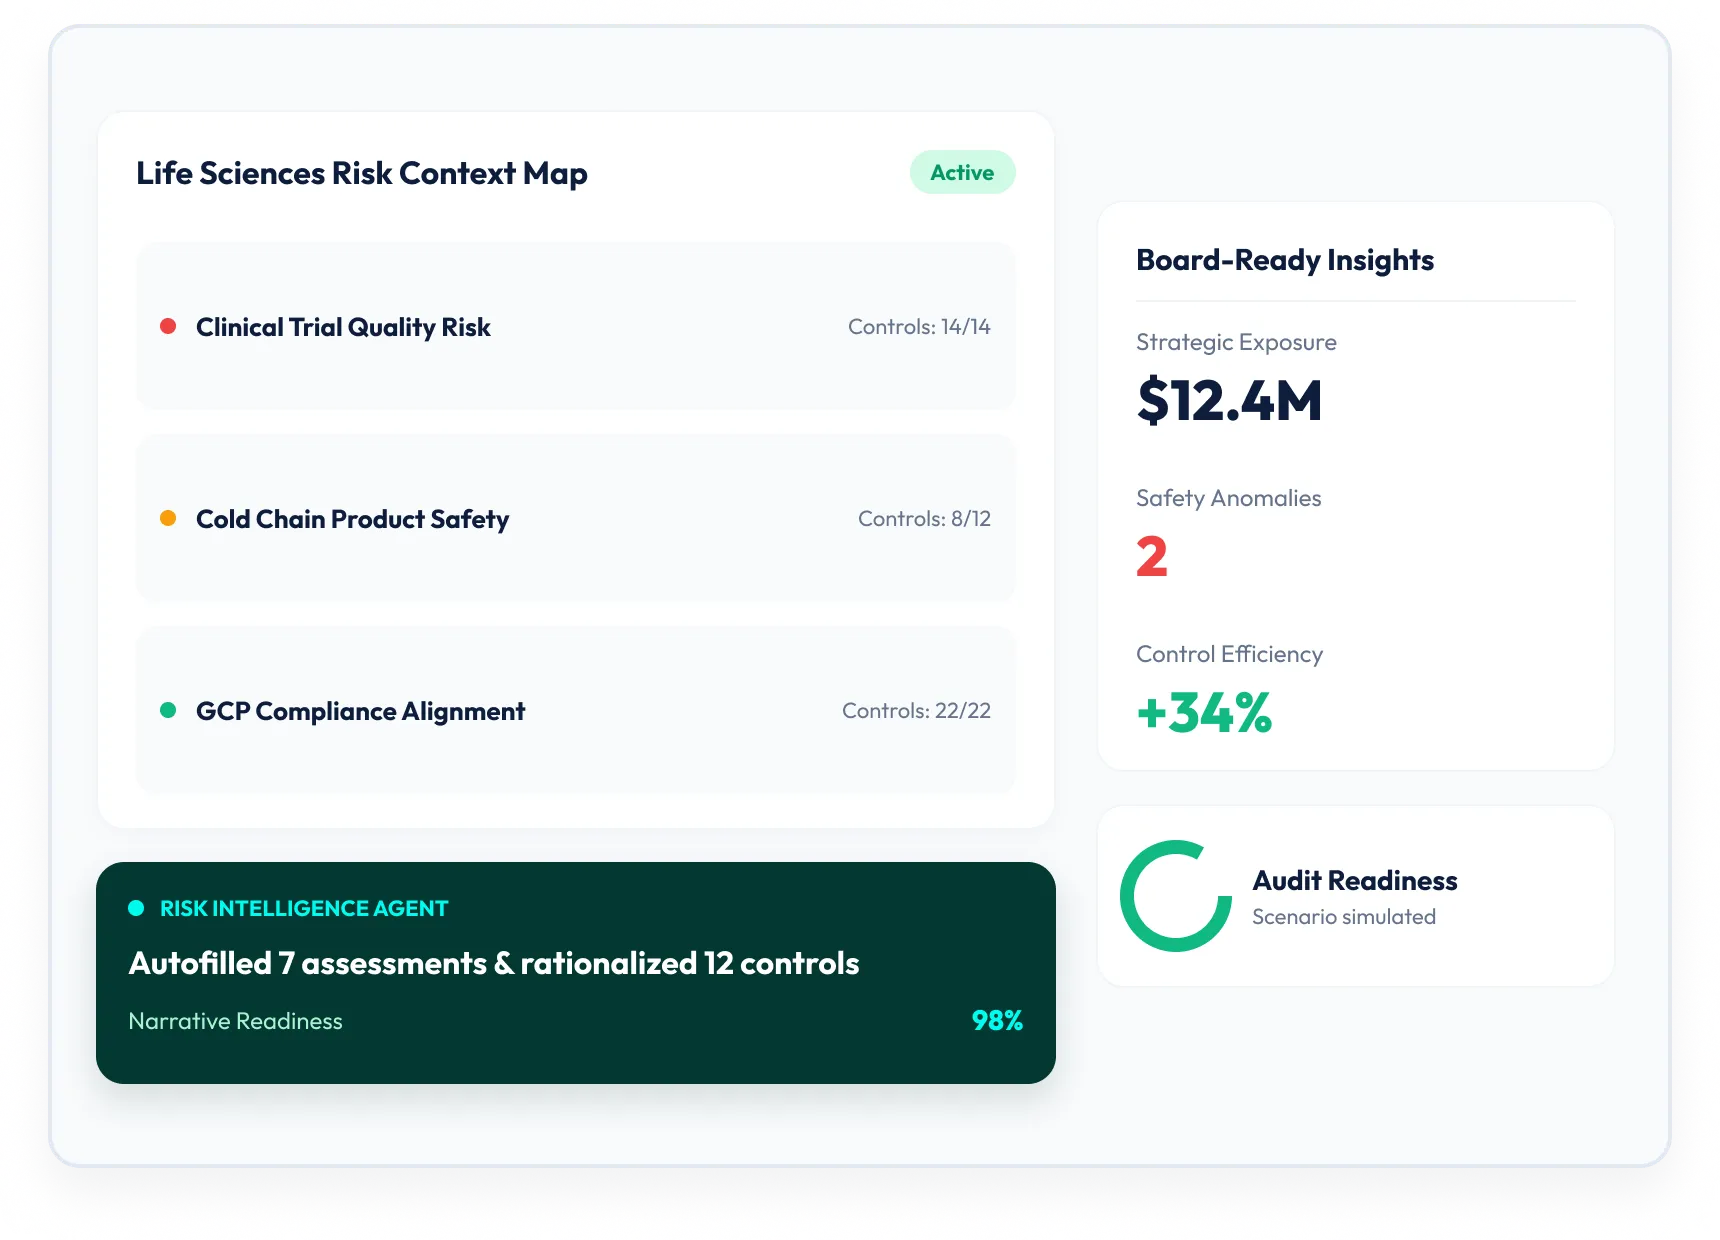
Understand and act quickly on key risks with AI-powered risk intelligence across risk areas such as strategic, product, quality, safety, operational, cyber, supplier, and emerging risks, in a single governed environment. Risk Assistants answer contextual questions, while Risk Agents autofill assessments based on provided evidence, rationalize controls by addressing control gaps, and standardize controls across control environments. Intelligent Risk Narratives equip you with board-reporting insights and support faster risk decisions.
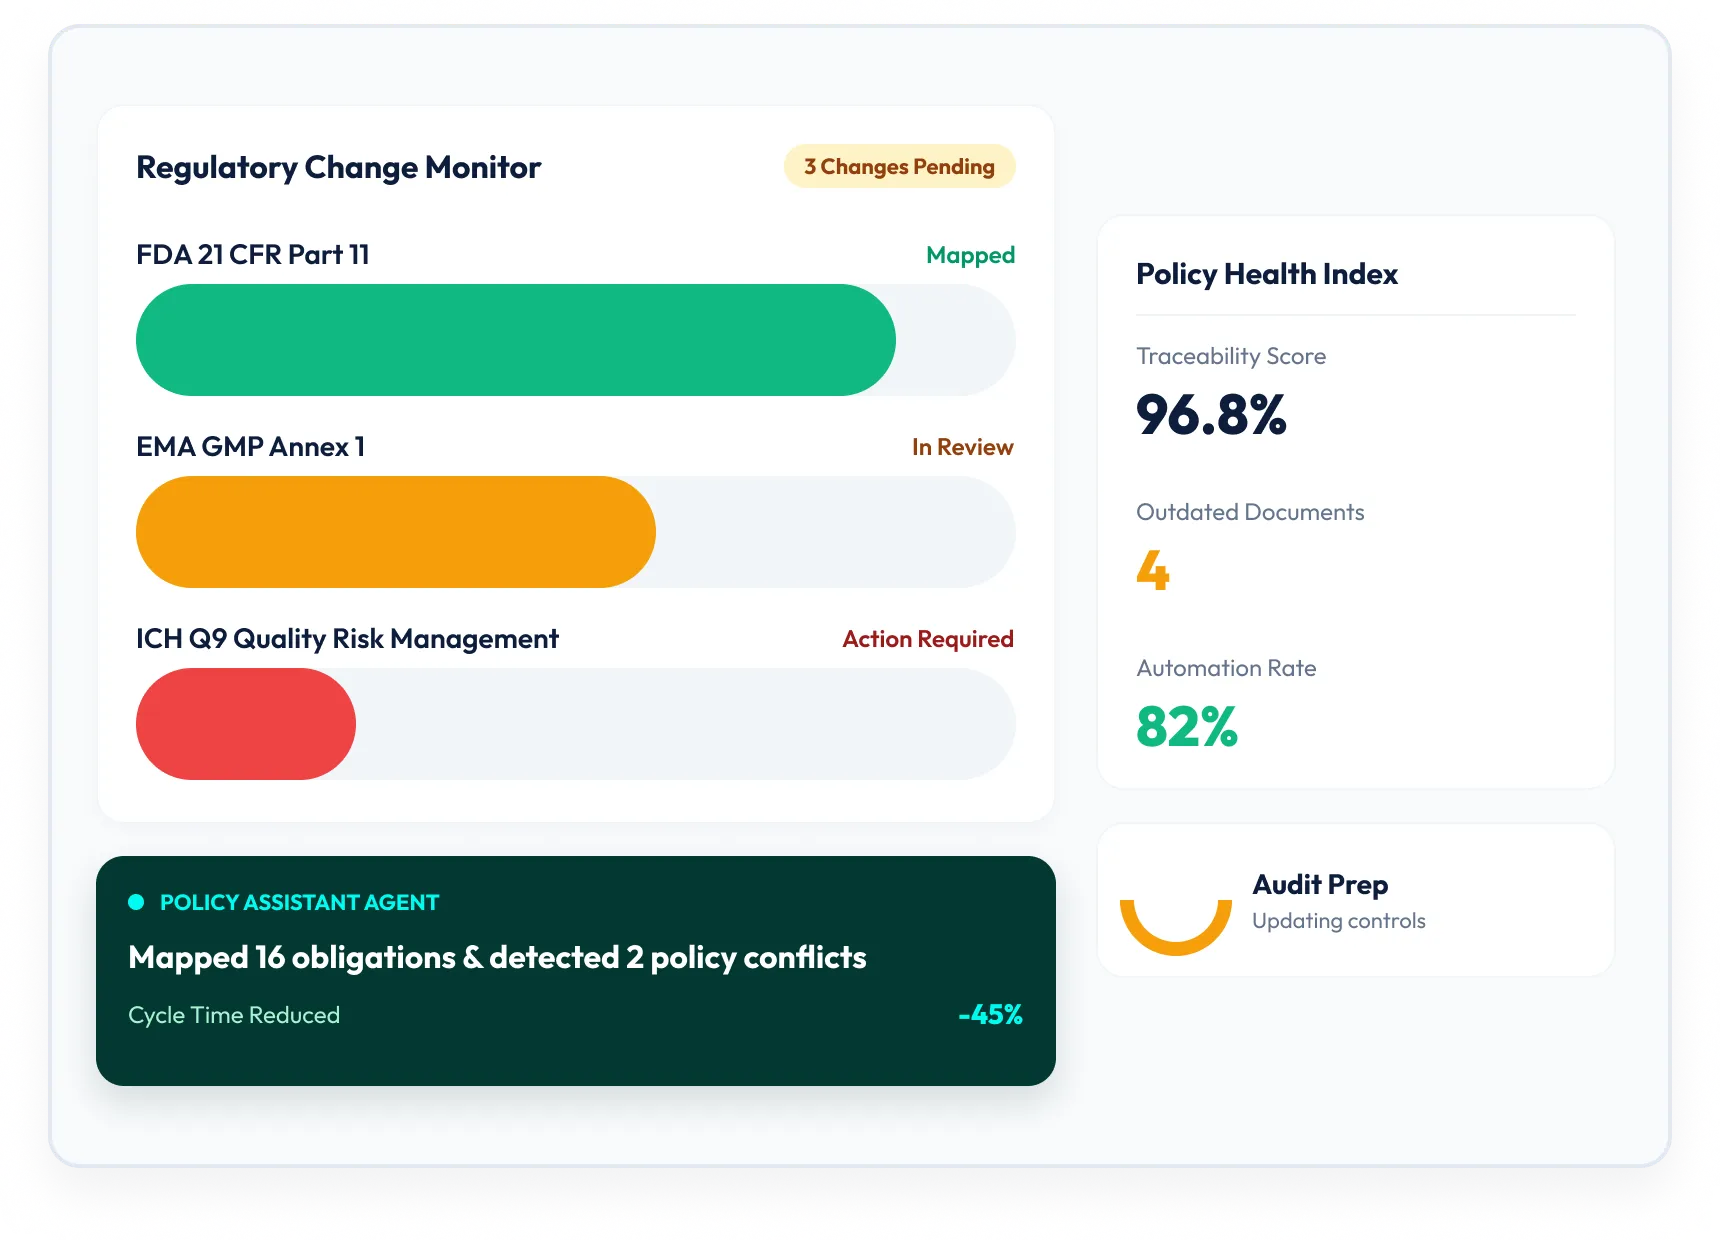
Continuous monitoring of regulatory changes, automated mapping of applicable obligations to relevant data elements, and summarization cut down the regulatory change cycle time, giving more time to streamline controls, policies, and procedures. Achieve end-to-end policy lifecycle management with Policy Assistants, which deliver citation-backed answers from approved content, while AI-powered comparison, impact analysis, conflict detection, and mapping recommendations help maintain consistent, traceable documentation.
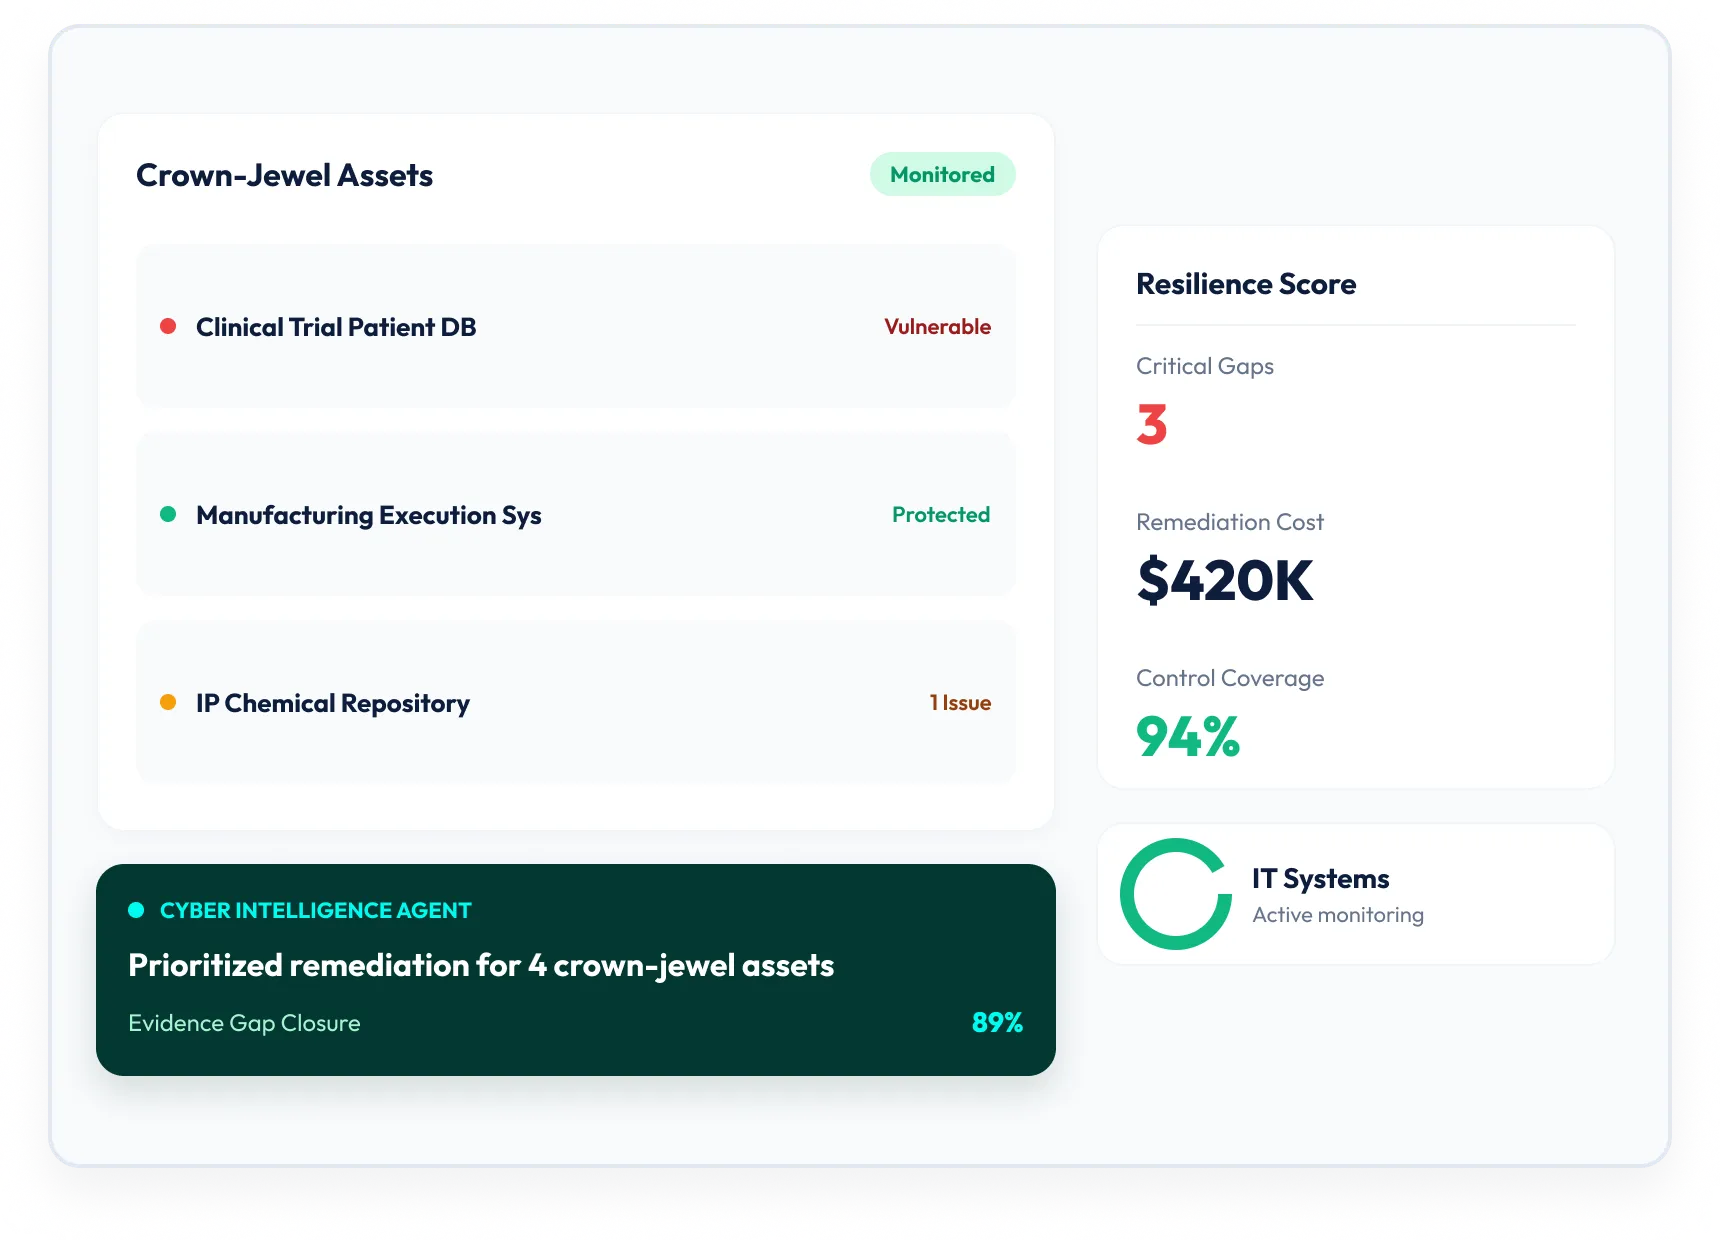
Make security decisions grounded in business and regulatory impact to protect sensitive clinical, patient, manufacturing, and intellectual property data. Connect data, applications, assets, threats, vulnerabilities, controls, suppliers, and critical services in a single Cyber GRC context. Cyber Assistants identify relevant insights, while Risk Assessment and Control Testing Agents assemble the assessment context, identify control and evidence gaps, and prioritize remediation for crown-jewel assets.
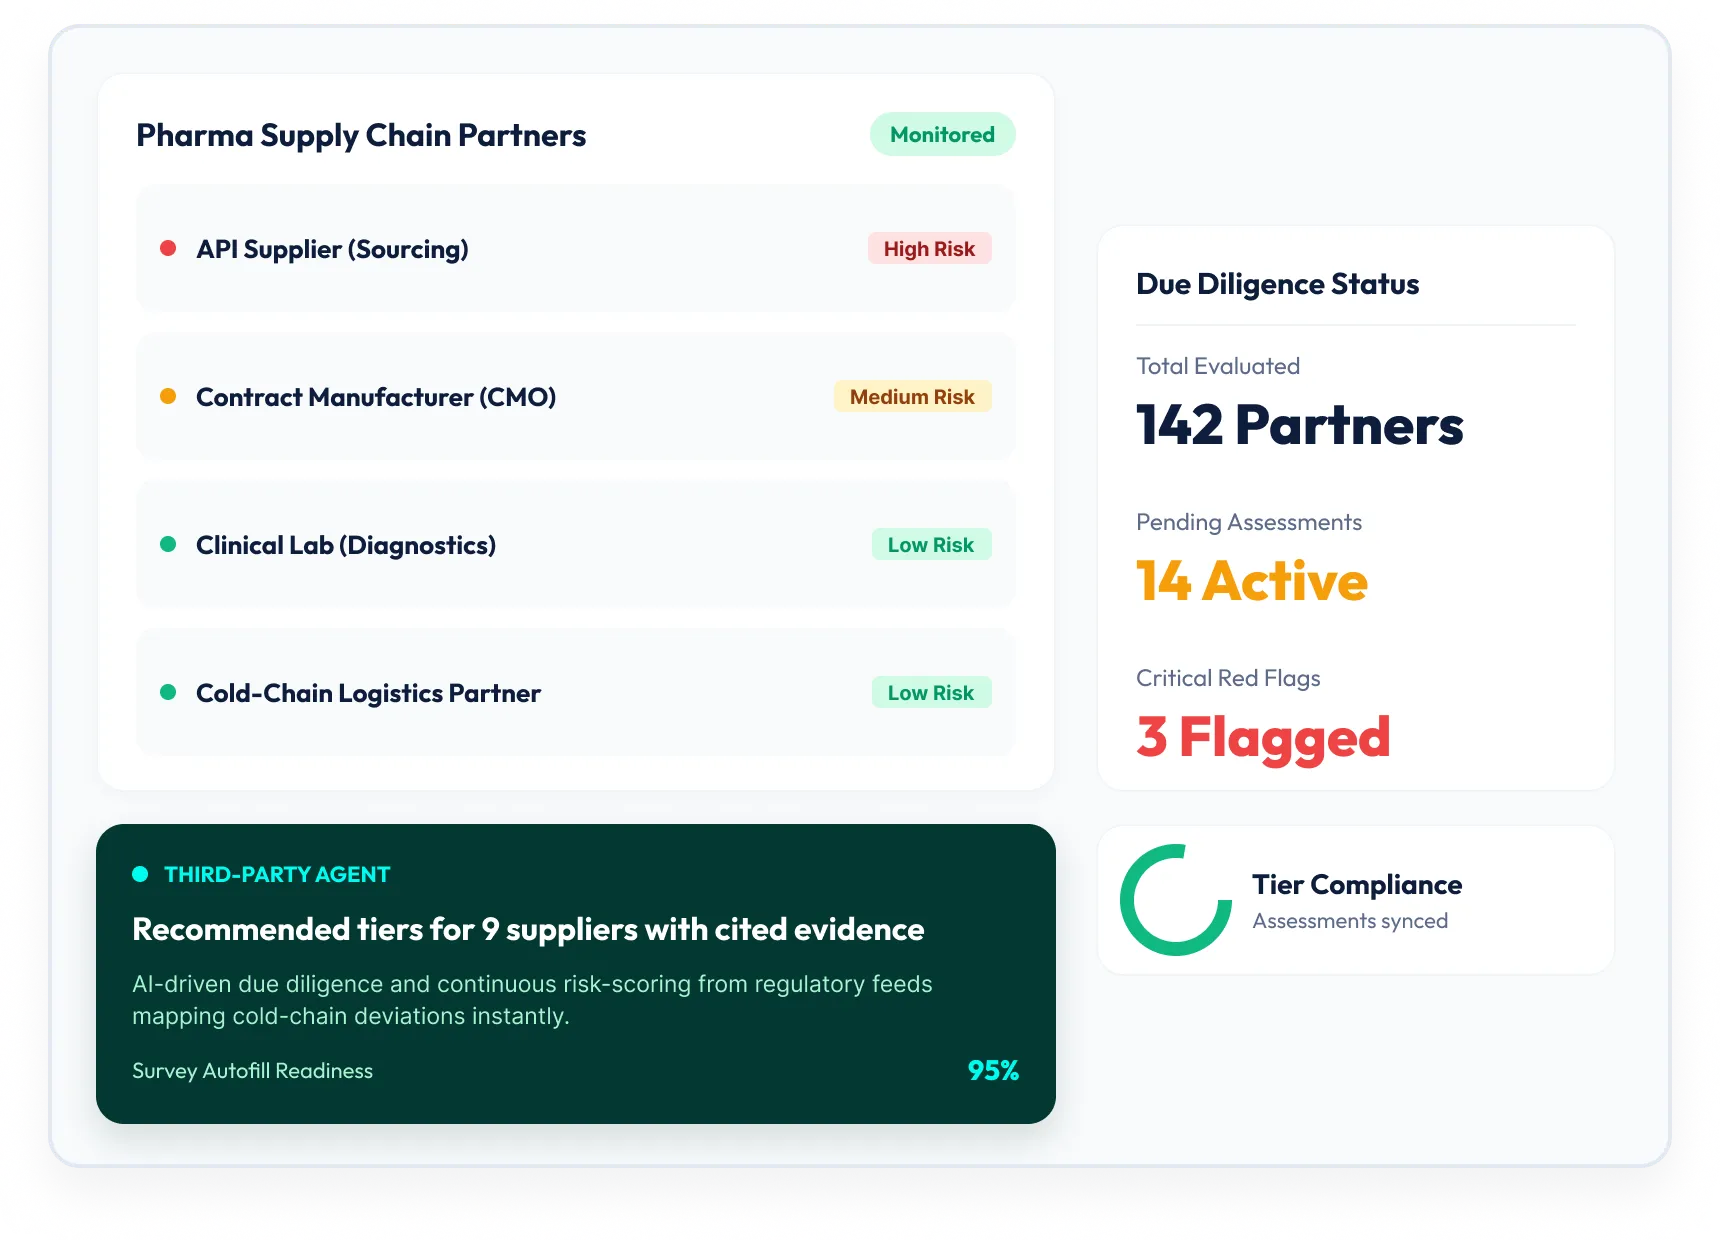
Reduce the risk that suppliers, laboratories, contract manufacturers, logistics providers, and data processors pose to regulated activities and product availability. Govern third parties from onboarding through offboarding with connected profiles, assessments, evidence, performance, incidents, and issues. Third-Party Risk Agents recommend risk tiers, tailor due diligence, interpret evidence, and monitor changing signals, while AI survey autofill drafts source-backed responses with citations and confidence indicators.
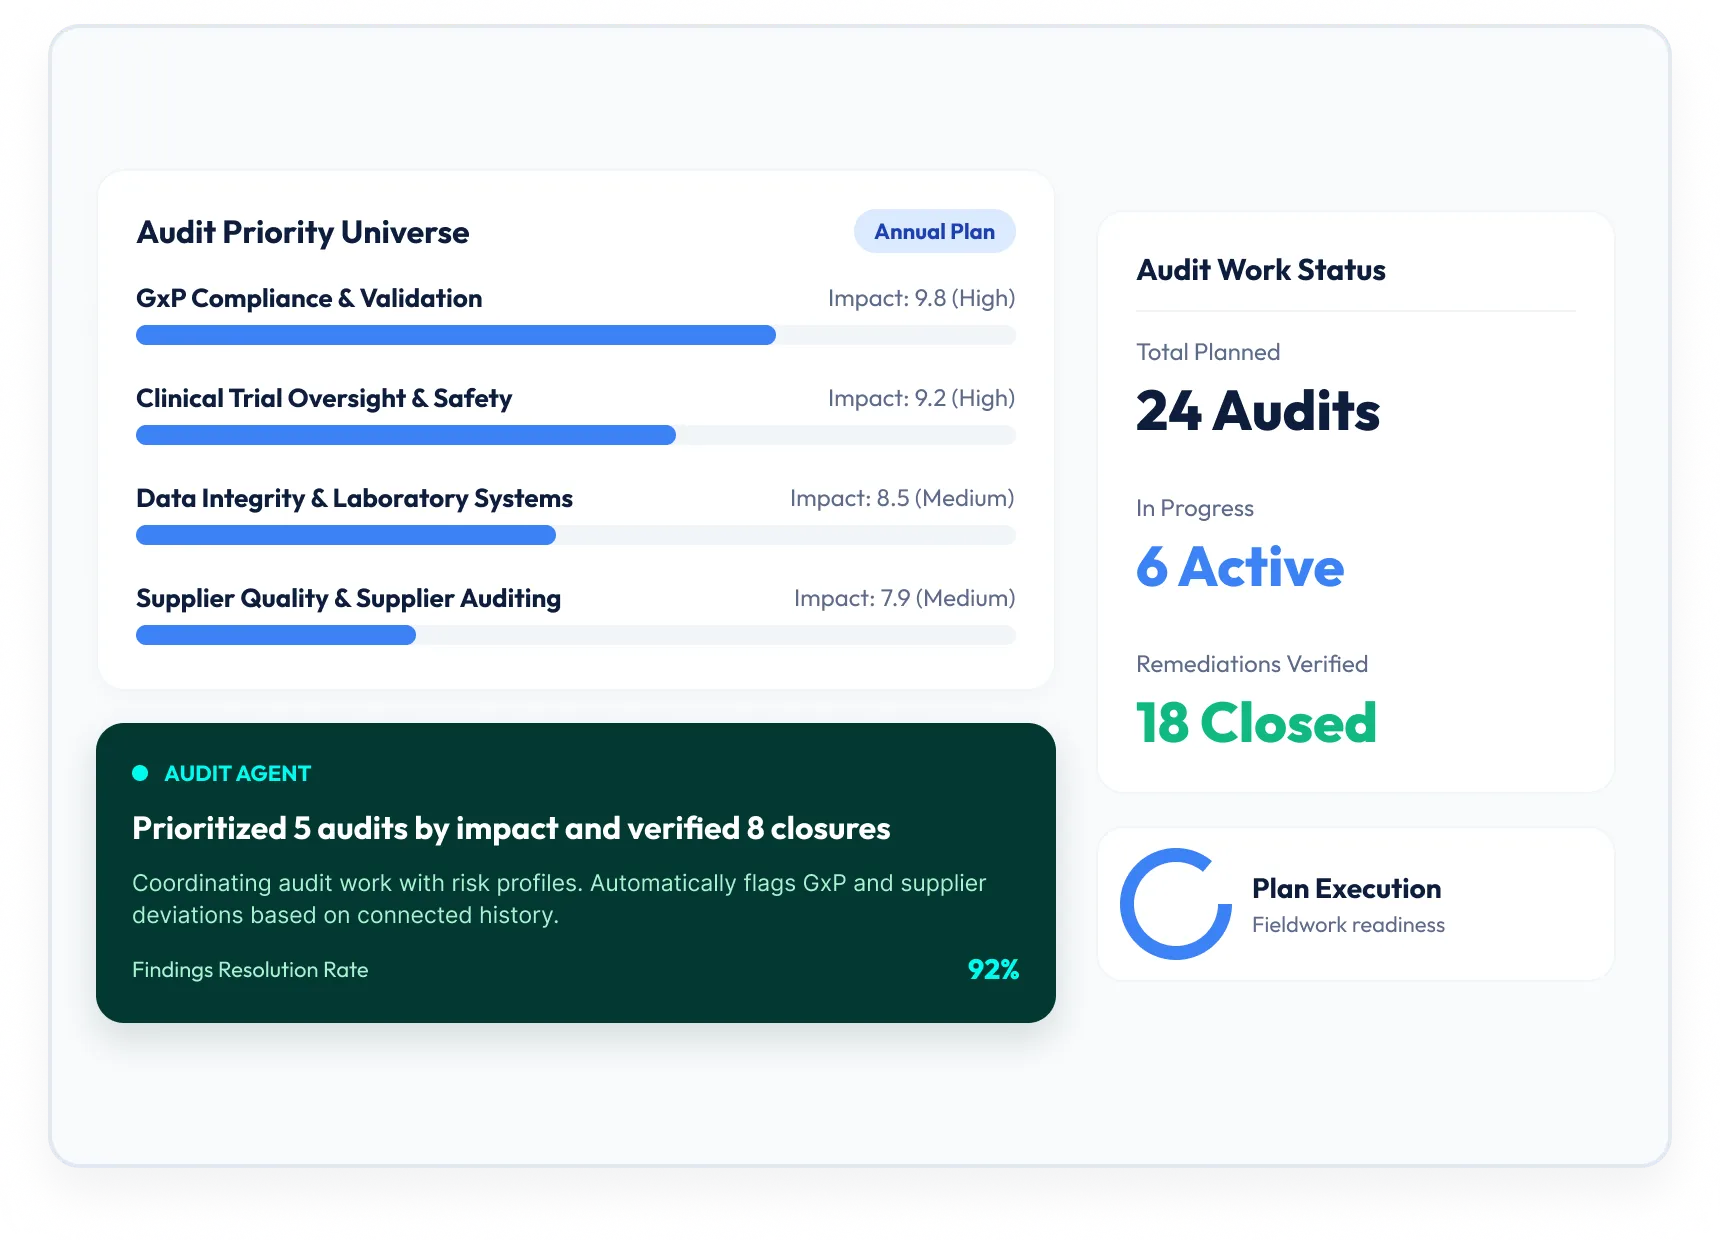
Direct audit resources to the areas with the greatest potential impact rather than spreading them evenly across all audits. Use connected risk, compliance, control, supplier, issue, and audit data to prioritize scope and manage fieldwork, evidence, findings, and follow-up. Audit Assistants and Agents pull together relevant context, highlight control gaps, support evidence review, improve report quality, and recommend coordinated remediation through verified closure.
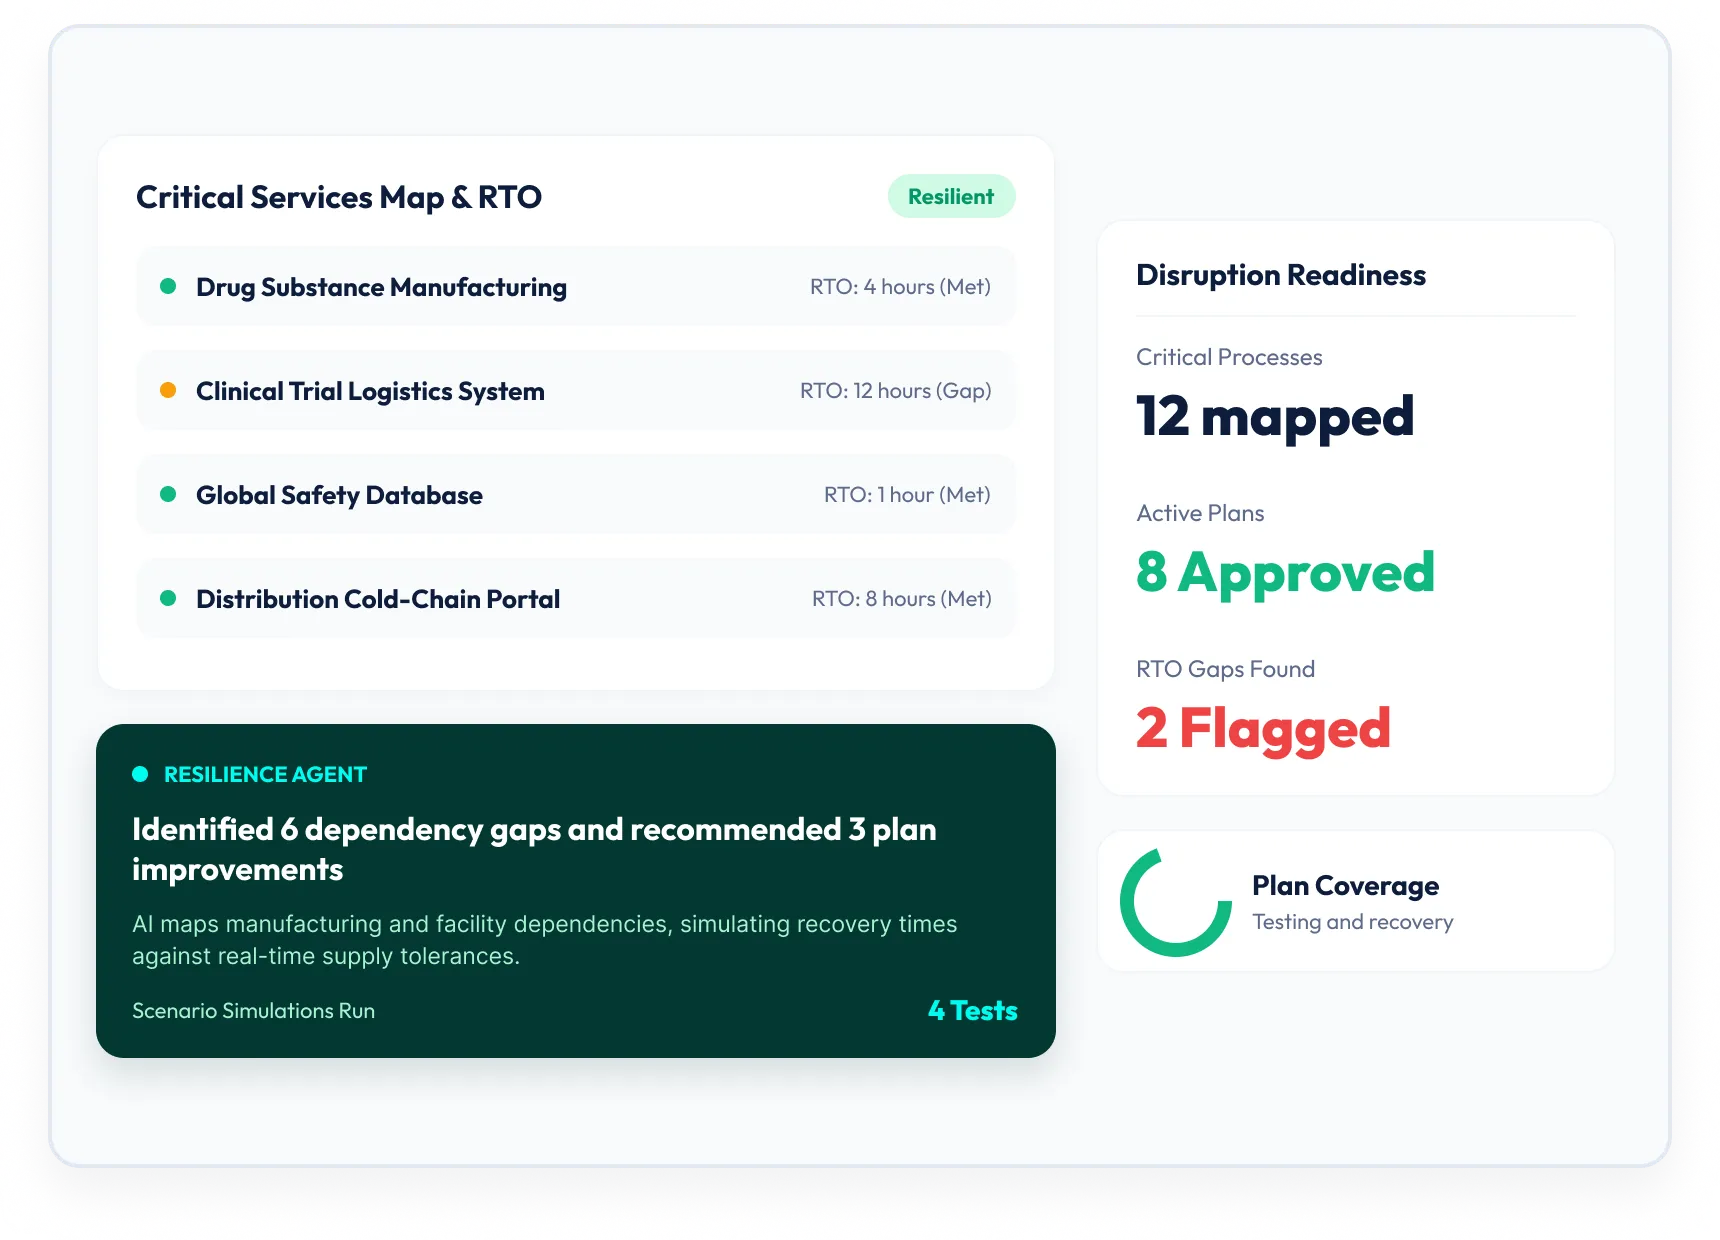
Protect critical operations to keep disruptions across clinical operations, manufacturing, technology, facilities, or suppliers from delaying products or affecting patients. Map critical services to systems, facilities, data, people, suppliers, manufacturing dependencies, and recovery resources. AI assistants and agents identify dependency gaps, summarize complex plans, and recommend improvements to preparedness based on incidents, assessments, supplier reviews, and recovery tests.
Research, clinical, quality, cyber, and supplier risk intelligence updates continuously, with AI recommending and executing approved actions in the moment.
Industry analysts, including Gartner, Forrester, and IDC, consistently recognize MetricStream.
Pharmaceutical, biotechnology, medical device, and clinical research organizations rely on us to strengthen their GRC programs and protect patient trust.
Decades of hands-on life sciences GRC experience, with experts and AI engineers who support GRC programs at every milestone.
AI assistants and agents embedded directly into GRC workflows, not layered on top of them.
Configure taxonomies, workflows, responsibilities, evidence, and reporting across products, entities, functions, and jurisdictions.
Use our interactive ROI calculator, built by Forrester, to estimate what Enterprise GRC could deliver for your organization. Enter details such as annual revenue, number of GRC tools, and compliance exposure to see your potential savings, payback period, and return on investment.
Calculate My ROI
Analyst Report
Download the excerpt to see why MetricStream was recognized as a GRC Leader in 2025.
Download Now
eBook
A CISO's guide to outsmarting cyber risk before it outsmarts you.
Read More
Case Study
Read how a global bank enhanced business decision-making by successfully moving from a traditional approach to a single, connected GRC system.
Read More
Whitepaper
Learn how GRC leaders are adopting AI responsibly and proving measurable ROI at scale.
Read MoreLife sciences organizations, including pharmaceutical, biotechnology, and medical device companies, face GRC challenges that span multiple dimensions: complex regulatory environments related to pricing, marketing, quality, and safety; growing dependence on suppliers and third-party vendors that increases financial and operational risk exposure; sophisticated OT-based cyberattacks; and the need to govern advanced technologies like AI while addressing ethical, privacy, and security concerns. According to the 2024 Ponemon Healthcare Cybersecurity Report, 92% of healthcare organizations faced at least one cyberattack in the past year.
MetricStream's Regulatory Compliance solution helps life sciences organizations navigate the complex web of regulatory requirements governing the industry. The platform enables teams to track and manage regulatory changes, adopt an integrated approach to compliance obligations, simplify and streamline policy management, perform compliance assessments, and manage cases and regulatory audits. This reduces the cost of compliance, eliminates process inefficiencies and redundancies, and helps organizations demonstrate regulatory readiness to auditors and regulators.
MetricStream's Enterprise Risk Management solution enables life sciences companies to manage and mitigate multiple risk types, including enterprise risk, compliance risk, quality risk, device risk, and marketing risk, through a comprehensive risk strategy. The platform automates risk identification, assessment, monitoring, and acceptance across all business units and functions, improves risk visibility and foresight, and enables organizations to prioritize investments and actions based on the quantified impact of risks.
MetricStream's Cyber GRC solution gives life sciences organizations a 360-degree, real-time view of IT and cyber risks, threats, vulnerabilities, and associated controls. The platform simplifies identification and analysis of risks in IT operations and contextualizes IT risks based on associated processes, business units, and IT assets. Organizations can align with compliance frameworks such as ISO 27001, NIST CSF, and NIST SP800-53, all within a single, unified solution that minimizes potential issues and strengthens cyber resilience.
MetricStream's Third-Party Risk Management solution provides life sciences companies with an integrated, real-time view of risks across all third parties, including vendors, suppliers, and contractors. The platform monitors and manages risks associated with the extended enterprise, protects against existing and potential threats from third and fourth parties, and simplifies managing risk and compliance across the full third-party lifecycle, from onboarding and due diligence through continuous monitoring, performance management, and offboarding.
MetricStream's AI-first GRC approach enhances resilience for life sciences organizations by accelerating routine GRC tasks, enabling predictive insights, automating regulatory compliance workflows, and delivering combined assurance to senior management, boards, and regulators. With real-time data connections and advanced AI capabilities, the platform enables life sciences companies to proactively identify emerging risks and optimize controls across the enterprise, supporting both regulatory adherence and operational excellence.
MetricStream helps life sciences organizations reduce compliance violations and fines by providing a robust, integrated approach to risk, resilience, and compliance management. The platform enables organizations to proactively identify compliance gaps, streamline compliance assessments, strengthen control frameworks, and demonstrate a consistent compliance posture to regulators. This builds confidence with executive management and regulatory bodies while minimizing the financial and reputational costs of non-compliance.
According to MetricStream customer responses and the GRC Journey Business Value Calculator, life sciences organizations using MetricStream have achieved a 90% reduction in the time taken to manage compliance activities, an 80% improvement in risk and control framework-related operational efficiency, and a 67% improvement in risk reporting visibility and efficiency for the executive management and board. These outcomes reflect the platform's ability to streamline compliance, strengthen risk governance, and improve executive decision-making.
As life sciences companies shift from product-centric to patient-centric models and accelerate personalized medicine and therapies, they face new challenges across supply chains, clinical trials, manufacturing, and regulatory compliance. MetricStream's integrated GRC platform helps organizations manage these evolving risks by connecting data, processes, and teams across compliance, cyber, and third-party risk functions, ensuring that governance keeps pace with scientific innovation and patient safety remains the top priority.
MetricStream's GRC platform is designed for pharmaceutical companies, biotechnology firms, medical device manufacturers, clinical research organizations, and other life sciences entities operating in complex regulatory environments. Organizations that depend heavily on third-party suppliers, manage significant IT and OT risk exposure, or are adopting AI and advanced analytics in their operations benefit most from MetricStream's connected, AI-first approach to governance, risk, and compliance management.