IT & Cyber Risk Assistant
Get instant guidance across assets, threats, vulnerabilities, assessments, controls, KRIs, and actions.
Strengthen IT and cyber risk decisions with AI-powered assistants and agents that connect technical findings to business exposure, moving beyond vulnerability lists and periodic assessments.
Get instant guidance across assets, threats, vulnerabilities, assessments, controls, KRIs, and actions.
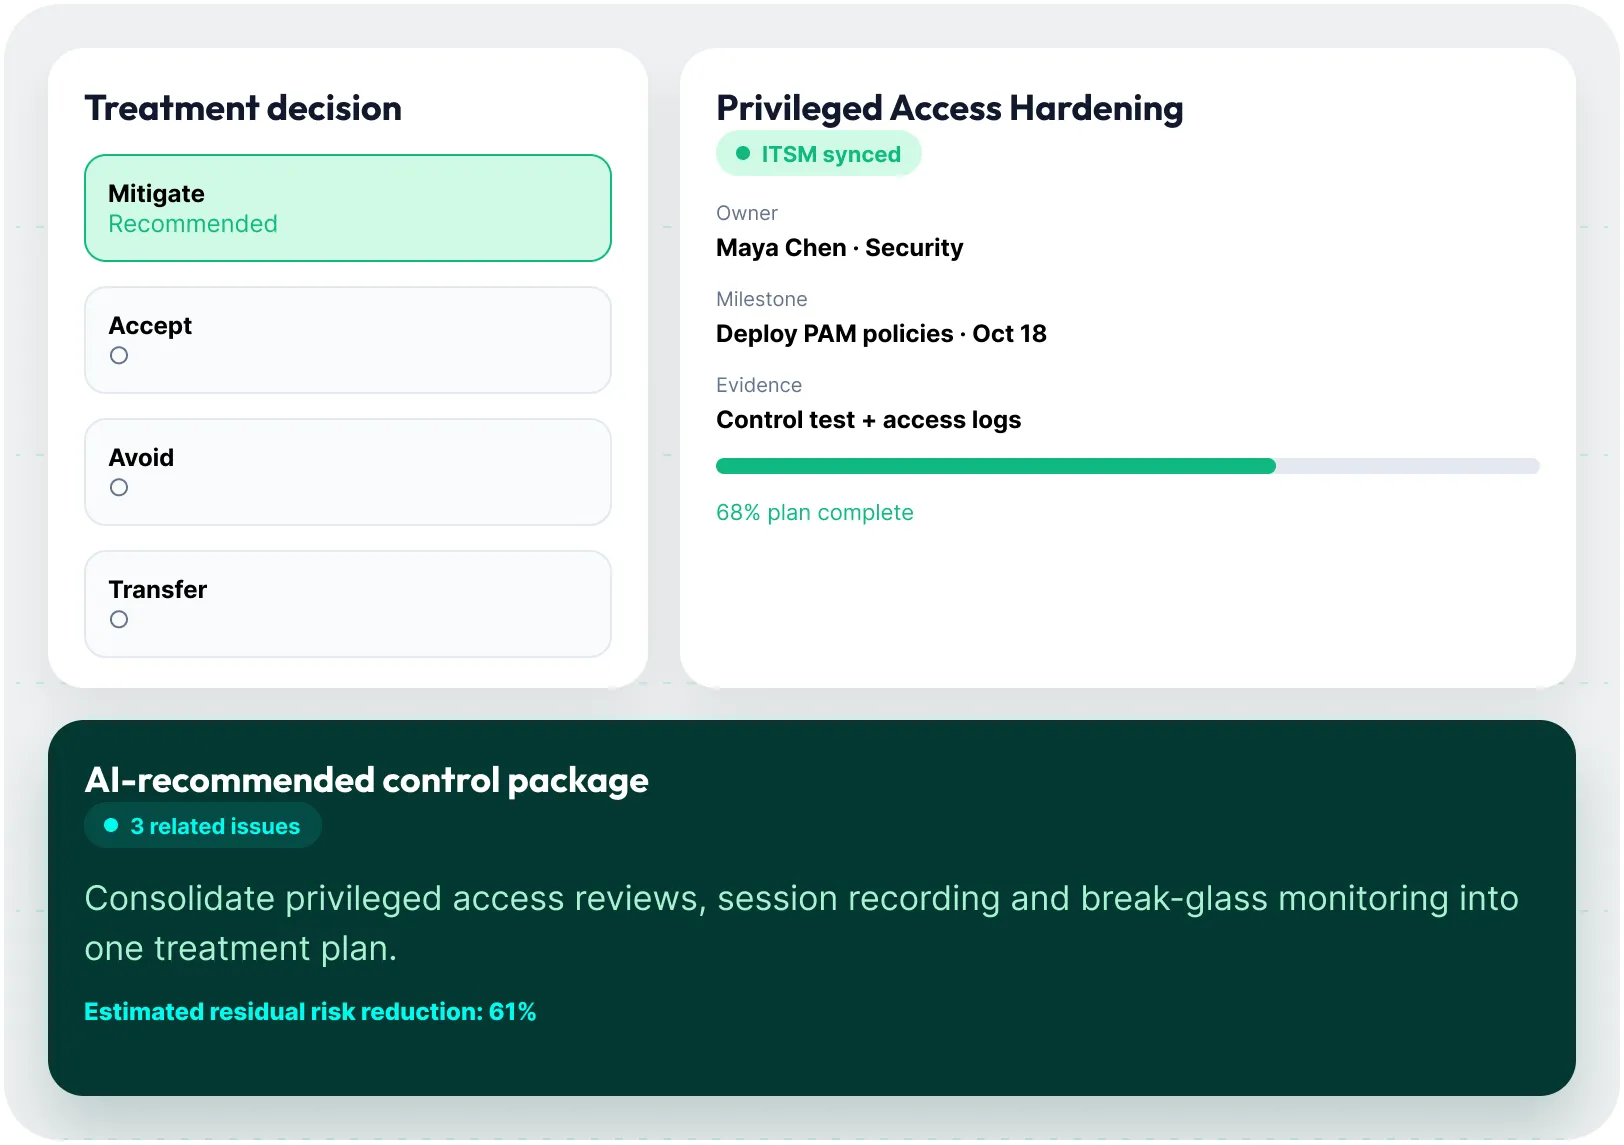
Purpose-built agents assemble assessment context, recommend risks and controls, evaluate residual exposure, and guide treatment.
Build and deploy IT & Cyber risk agents tailored to your cyber needs with MetricStream and partners.
60%
Improvement across key IT and cyber risk workflows with AI
60%
Faster cyber quantification and investment-prioritization cycle time
50%
Lower costs associated with managing regulatory audit findings
Source: MetricStream’s Business Value Calculator
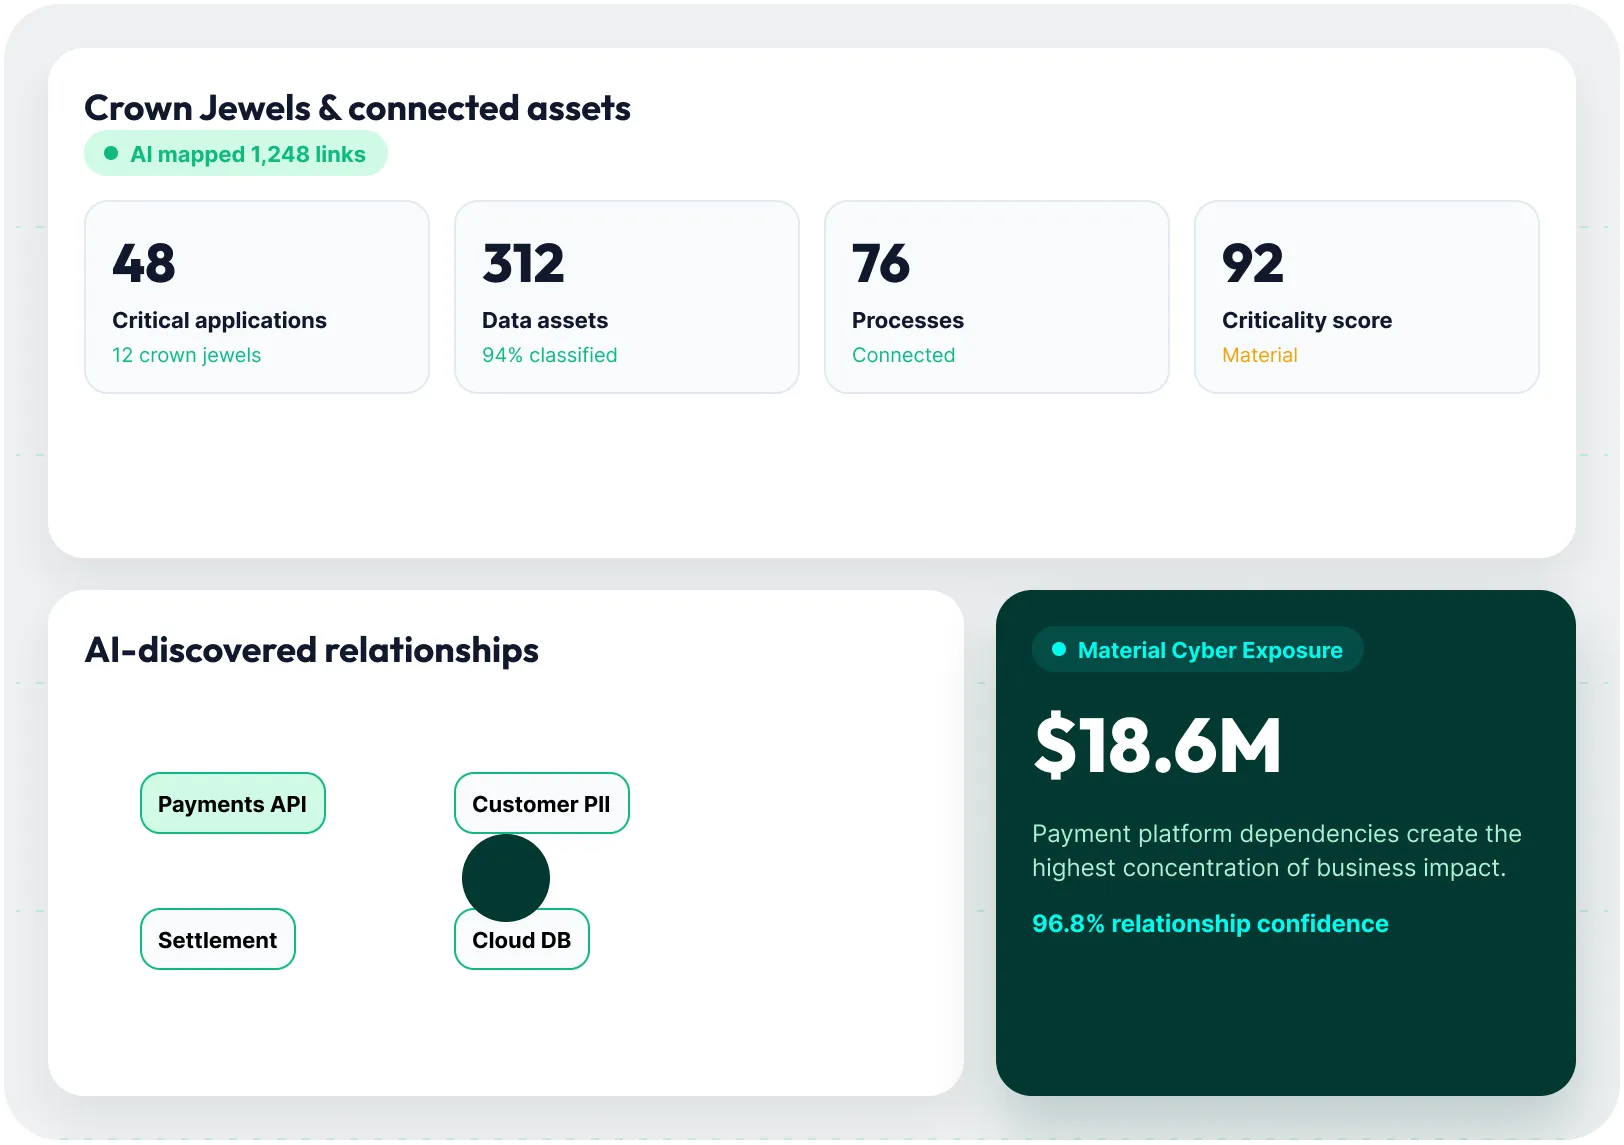
Know what to prioritize before deciding what to protect. Bring assets, applications, data, business processes, risks, controls, threats, vulnerabilities, and owners into one governed library. Classify your most important systems and data as Crown Jewels. AI helps uncover missing relationships and relevant risk-and-control connections, giving you a complete view of material IT and cyber exposure.
Cyber Risk Capability
Traditional IT & Cyber Risk Management
MetricStream Agentic IT & Cyber Risk Management
Asset context
Separate and incomplete inventories
AI connects assets with risks, threats, controls, and processes
Vulnerability prioritization
Driven primarily by technical severity
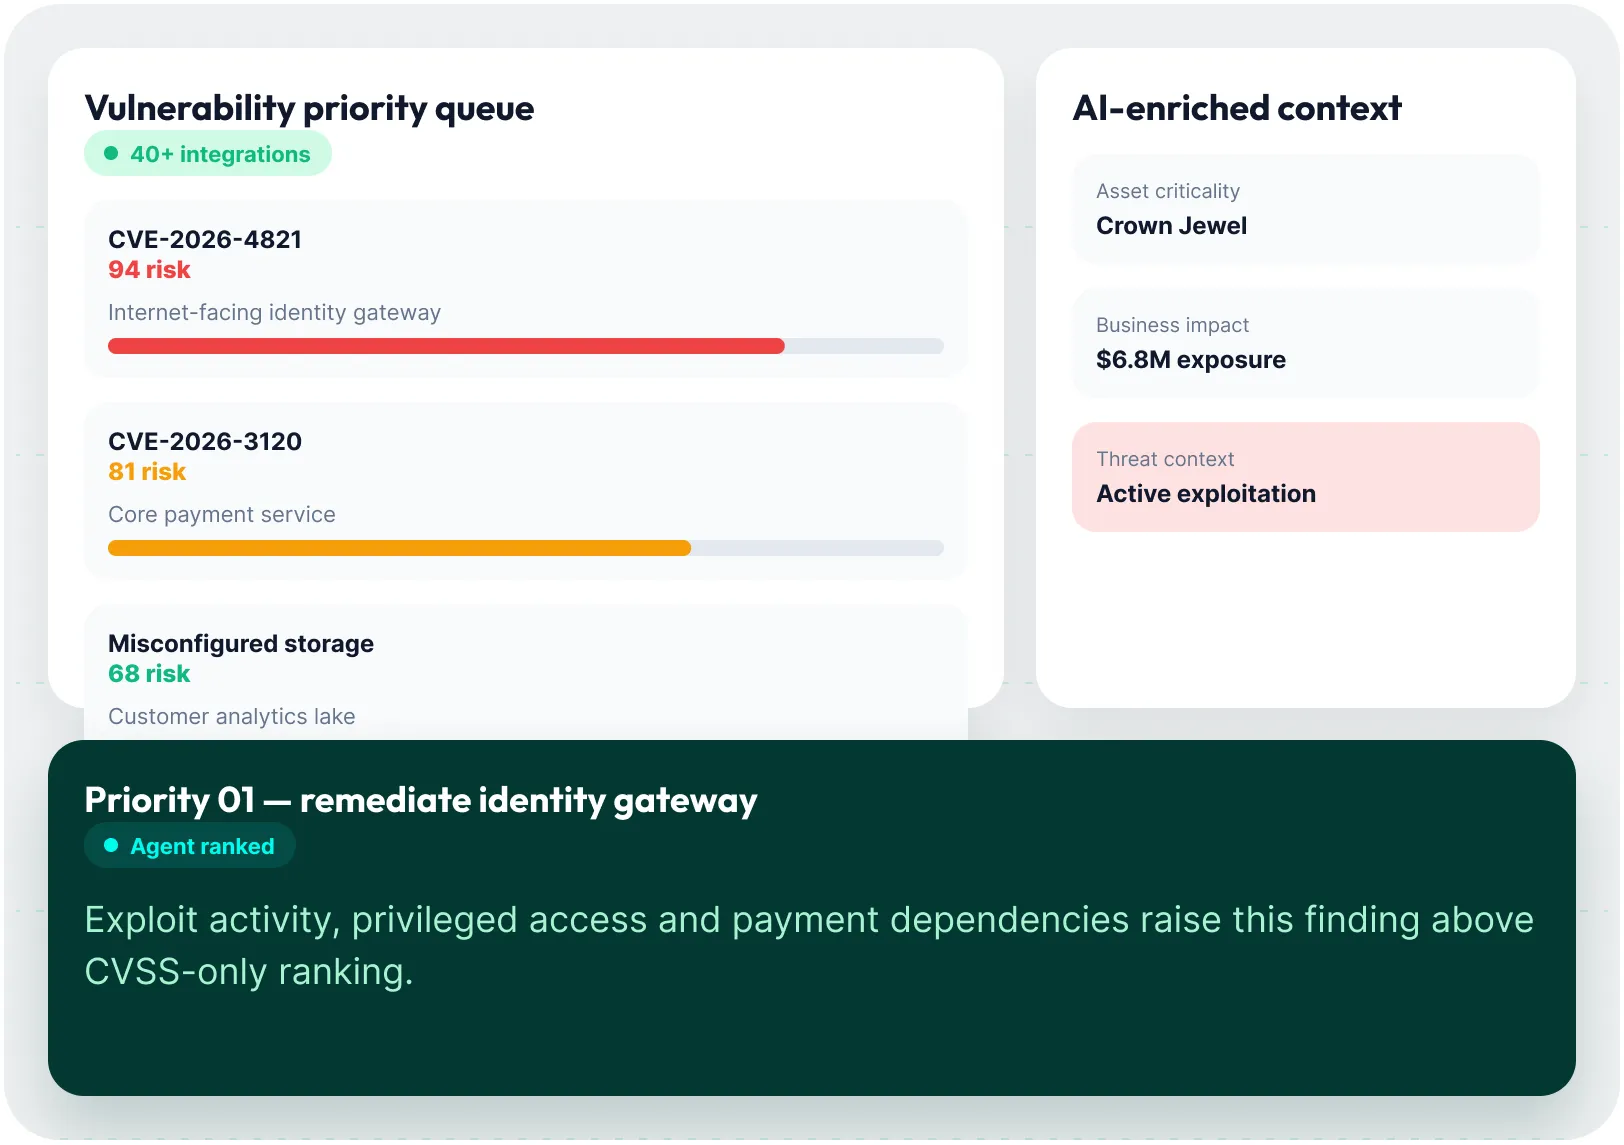
AI adds asset criticality, control effectiveness, and business impact
Risk assessments
Context gathered manually
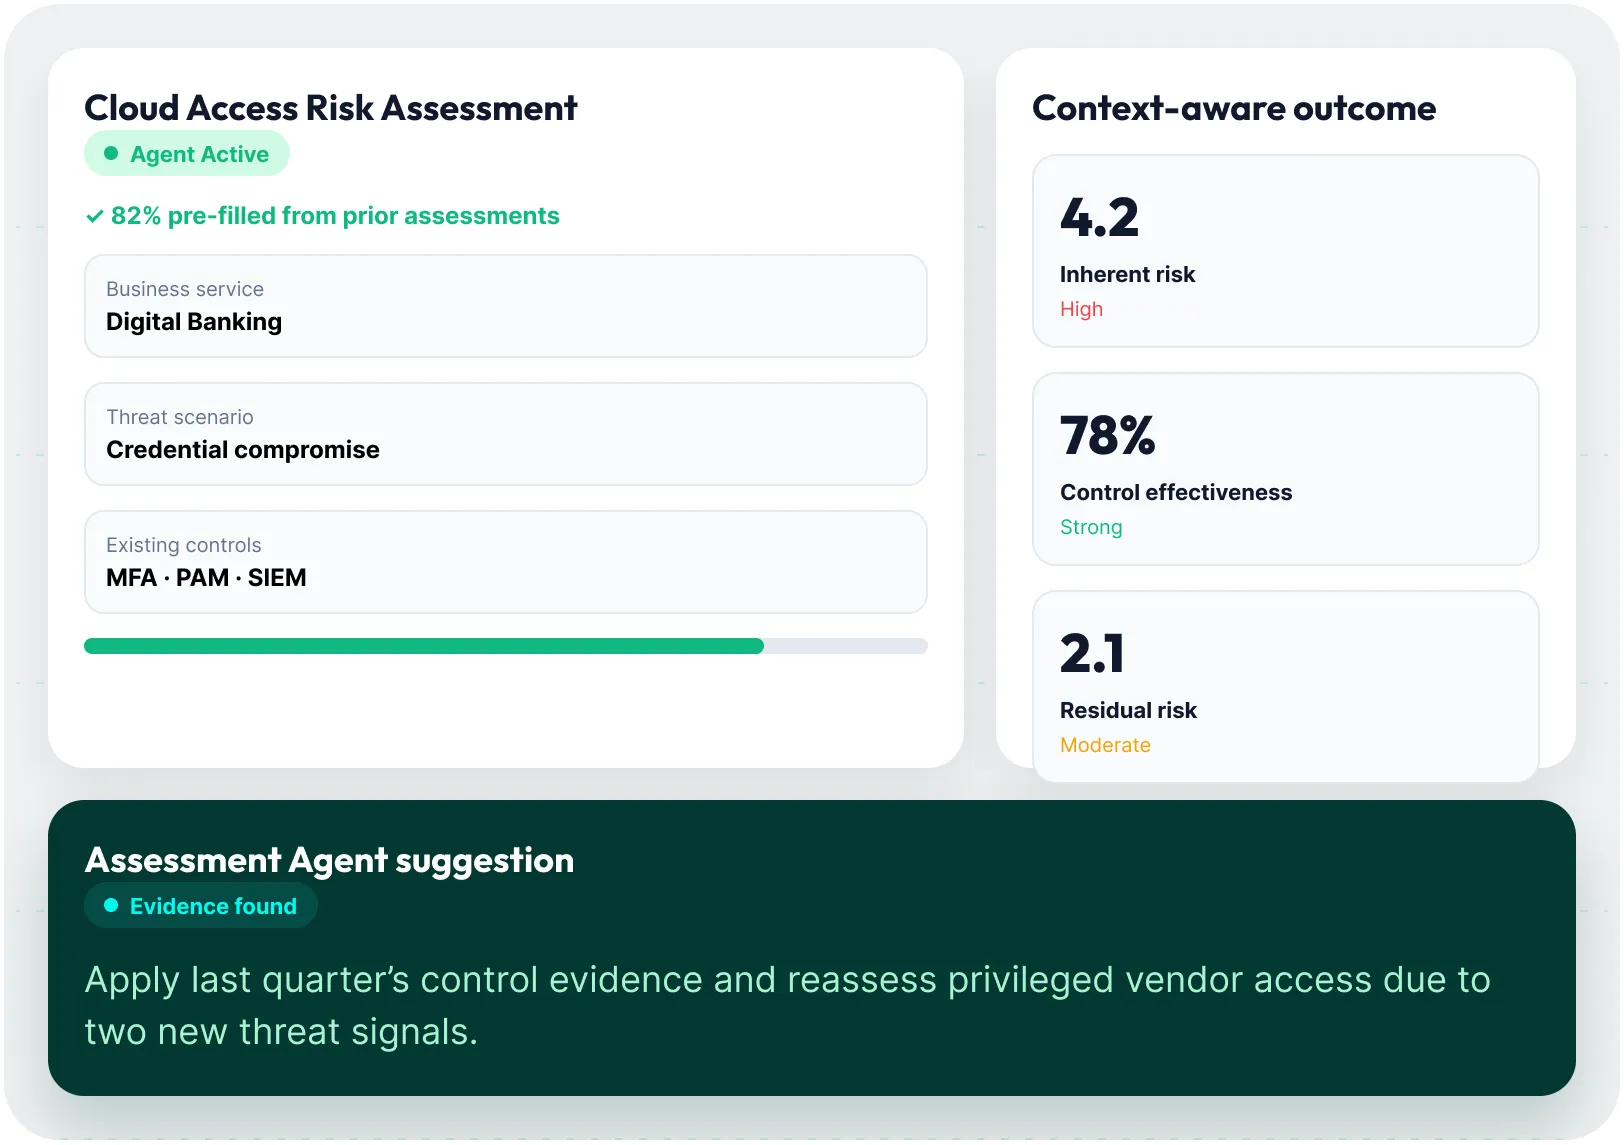
Agents pre-populate assessments from connected cyber data
Risk quantification
Red, amber, and green ratings
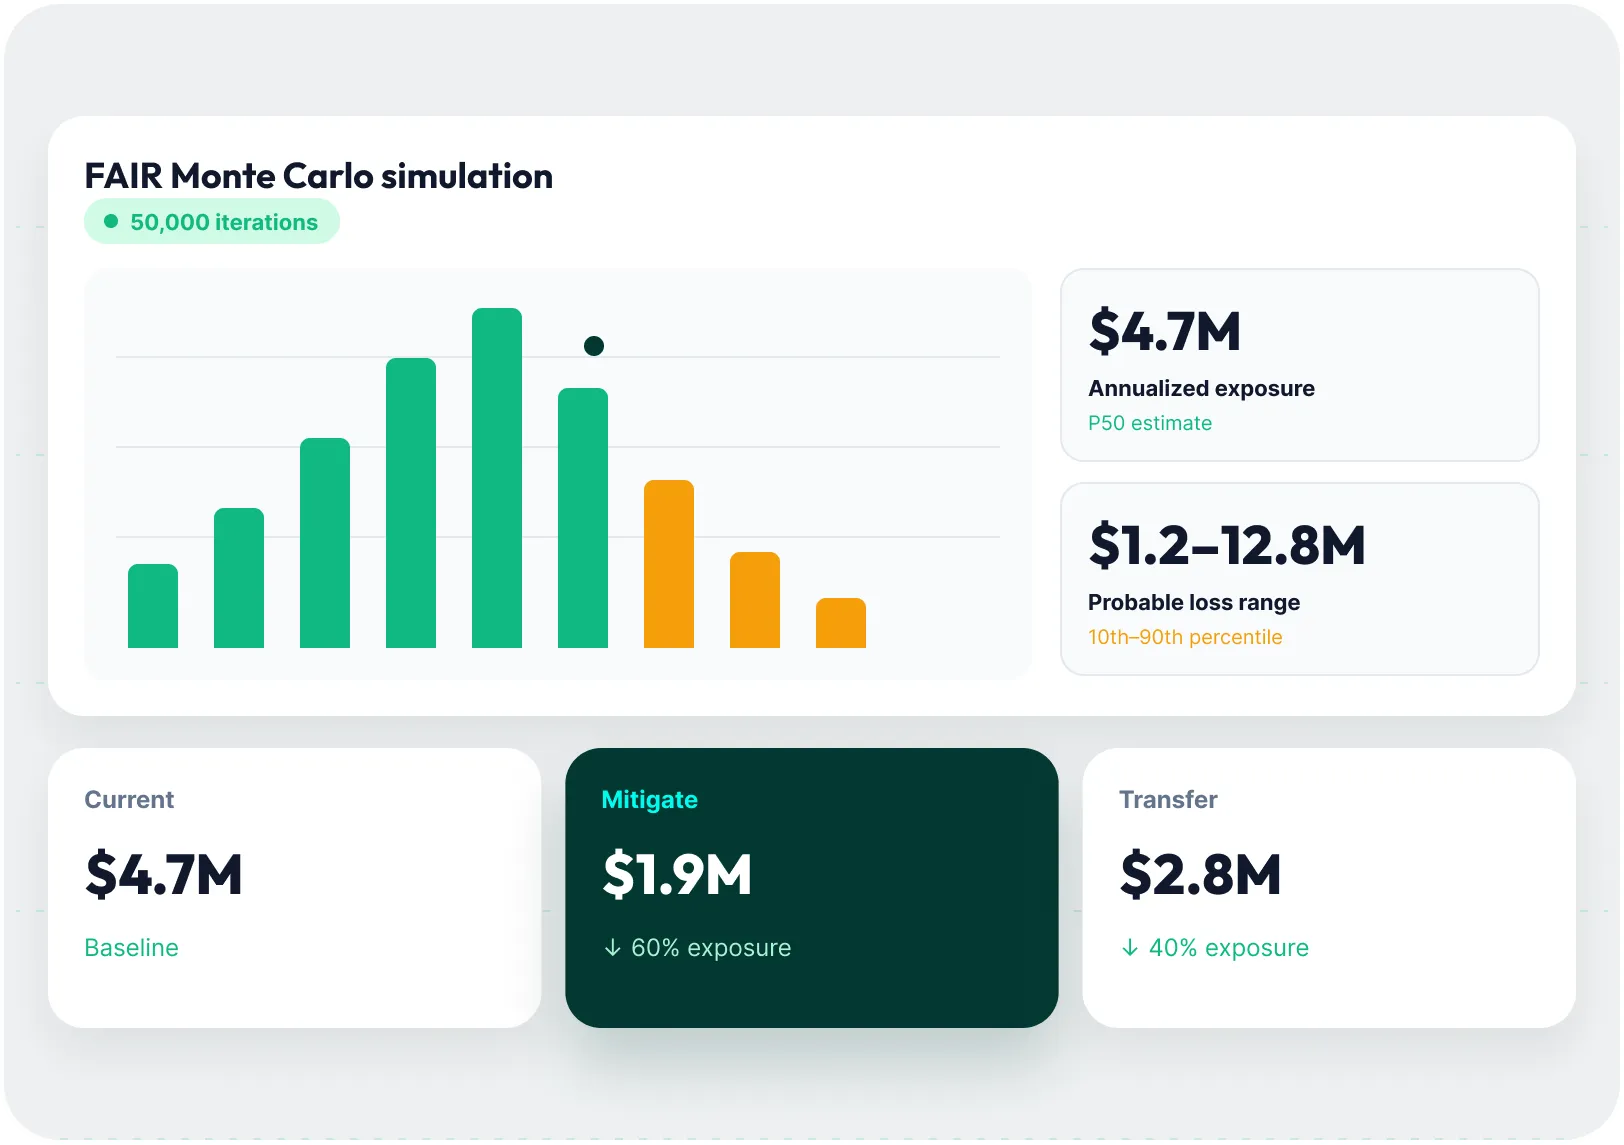
FAIR-based models express exposure in monetary terms
Risk treatment
Actions tracked in disconnected tools
Treatment remains connected to issues, owners, evidence, and approvals
Monitoring
Periodic risk reviews
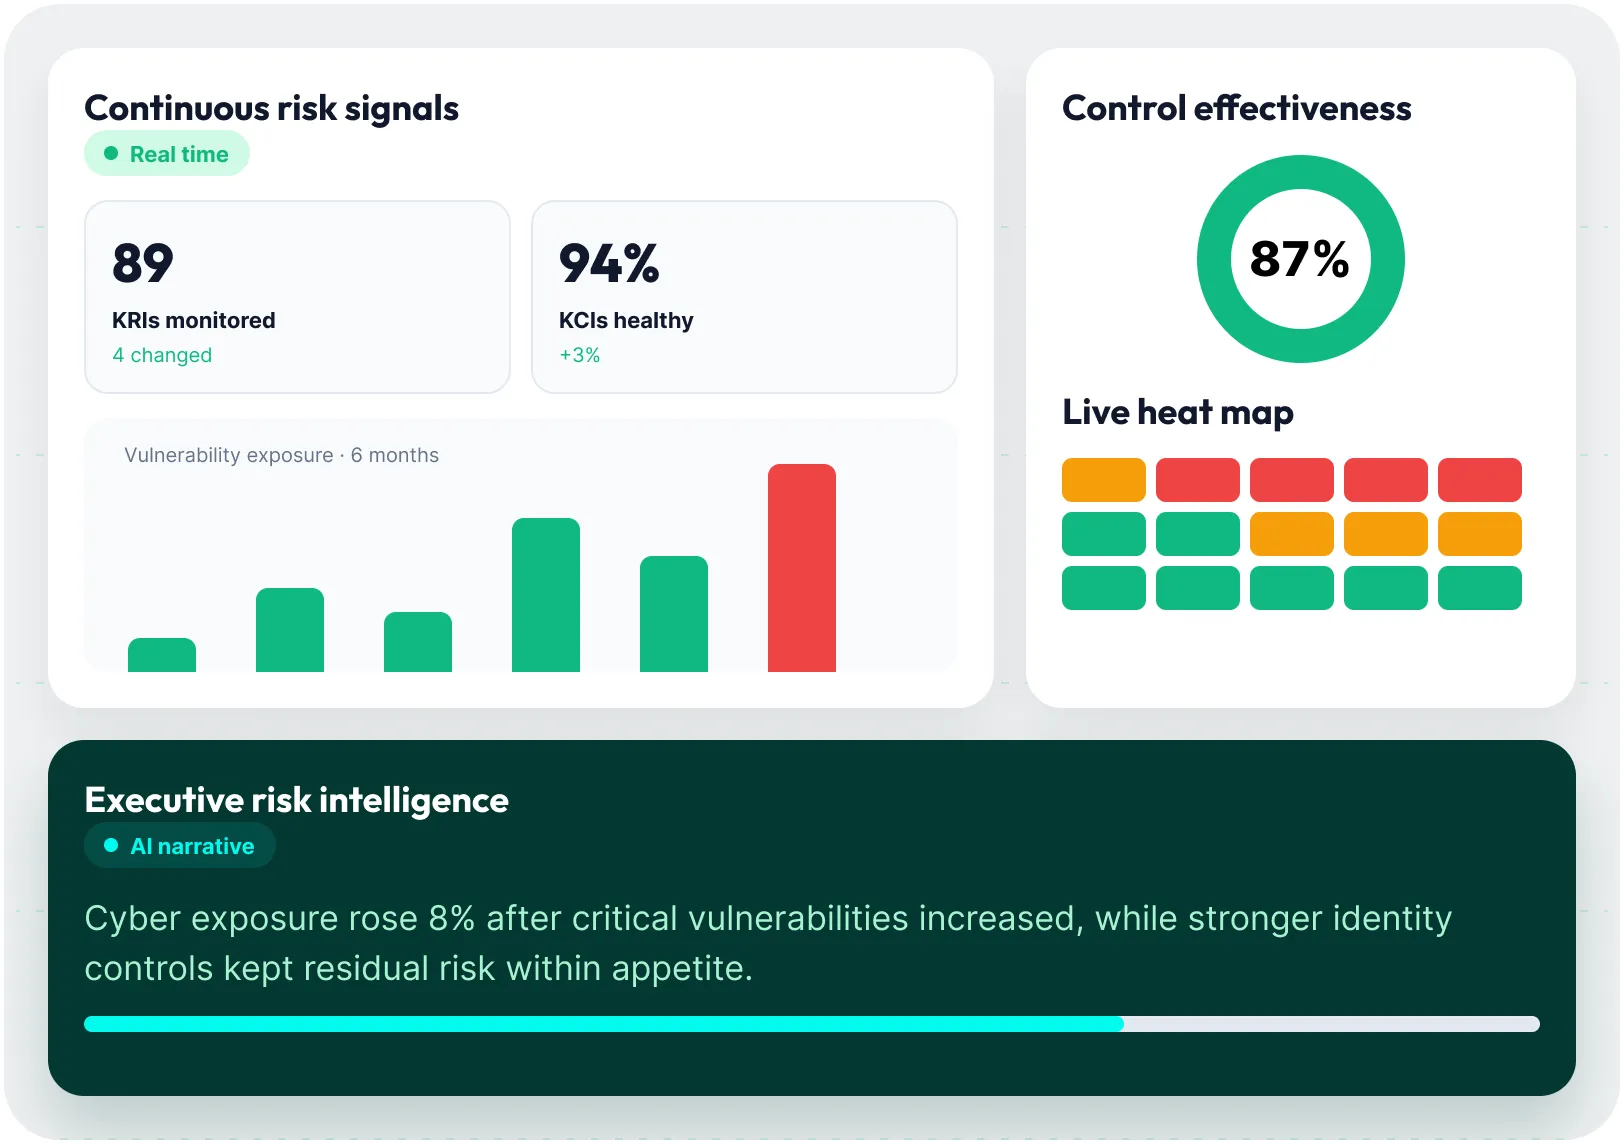
Connected indicators reveal changes in exposure and control effectiveness
Reporting
Static technical summaries
AI generates contextual, executive-ready cyber risk narratives
Use our interactive ROI calculator, built by Forrester, to estimate what Enterprise GRC could deliver for your organization. Enter details such as annual revenue, number of GRC tools, and compliance exposure to see your potential savings, payback period, and return on investment.
Calculate My ROI
Bring assets, threats, vulnerabilities, controls, processes, issues, and business impact into one governed model.
Use FAIR and Monte Carlo simulations to compare financial exposure and potential treatment outcomes.
Connect security findings and operational workflows with Cyber GRC context and accountable ownership.
Adapt assessments, scoring, treatment, appetite, thresholds, approval workflows, and reporting to your program.
Preserve human judgment through role-based access, traceability, citations, review, approval, and override controls.
Work with specialists experienced in IT and cyber risk programs across complex and highly regulated global enterprises.

Analyst Report
Download the excerpt to see why MetricStream was recognized as a GRC Leader in 2025.
Download Now
eBook
Take a proactive approach to cyber resilience. Explore this guide to learn more on the current cyber GRC challenges and how to create a robust IT and cyber risk mitigation framework.
Read More
Case Study
Learn how MetricStream helped an oil and gas giant automate cyber risk and compliance management processes and improved its overall cyber maturity and resilience.
Read More
Whitepaper
Learn how GRC leaders are adopting AI responsibly and proving measurable ROI at scale.
Read MoreMetricStream IT and Cyber Risk Management is an AI-native IT risk management software product that enables organizations to identify, assess, quantify, monitor, and mitigate IT and cyber risks in a business-driven, integrated manner. It integrates with IT security tools and intelligence feeds to prioritize risk exposure across IT assets, and provides sophisticated analytics—including cyber risk expressed in dollar values—to transform raw risk data into actionable intelligence for security and executive teams.
MetricStream’s Business Value Calculator models up to a 60% improvement across key IT and cyber risk workflows with AI, a 60% improvement in the cyber-risk quantification and investment-prioritization cycle, and a 50% reduction in costs associated with managing regulatory audit findings.
MetricStream IT and Cyber Risk Management imports vulnerability data from multiple third-party scanning tools and generates a combined risk rating for each IT asset based on both vulnerability severity and the asset's business criticality. This combined rating supports risk-based vulnerability management, allowing security teams to prioritize remediation efforts based on actual business impact rather than technical severity alone, ensuring that the highest-risk vulnerabilities are addressed first and that available resources are directed to the areas of greatest need.
kMetricStream IT and Cyber Risk Management imports vulnerability data from multiple third-party scanning tools and generates a combined risk rating for each IT asset based on both vulnerability severity and the asset's business criticality. This combined rating allows security teams to prioritize remediation efforts based on actual business impact rather than technical severity alone, ensuring that the highest-risk vulnerabilities are addressed first and that available resources are directed to the areas of greatest need.
MetricStream IT and Cyber Risk Management includes Cyber Risk Quantification capabilities that express cyber risk exposure in dollar values. Using the FAIR (Factor Analysis of Information Risk) model, the product calculates the monetary impact of cyber risks such as data breaches, identity theft, and infrastructure downtime. This financial framing allows organizations to fulfill regulatory requirements for financial disclosure of cyber risk factors and helps executives prioritize cyber investments based on quantified business impact.
MetricStream IT and Cyber Risk Management supports industry-standard IT and cyber risk assessment frameworks including ISO 27001, FAIR, and NIST CSF. Organizations can configure risk scoring methodologies, roll up scores to assessed entities or the broader organization, and define logic for computing both inherent and residual risk scores. Flexible heat maps allow teams to visualize and analyze risk scores at multiple levels of granularity.
MetricStream IT and Cyber Risk Management integrates with multiple endpoint IT security and infrastructure management tools, Configuration Management Databases (CMDBs), and security intelligence feeds. IT assets consolidated from CMDB integrations can be mapped to business entities and associated threats and vulnerabilities within the platform. This integration approach allows organizations to leverage their existing security investments while gaining a unified risk view across all data sources.
MetricStream IT and Cyber Risk Management provides user-configurable risk reports, risk heat maps, and role-based executive dashboards that aggregate IT and cyber, threat, and vulnerability data into clear, actionable intelligence. A 360-degree view of the risk environment through the platform's data browser allows CISOs and security managers to communicate cyber risk posture to regulators and executive leadership with accuracy and confidence, and to align cyber investment decisions with quantified risk exposure.
MetricStream IT and Cyber Risk Management enables a closed-loop issue management process that begins with the identification and documentation of issues from IT and cyber risk assessments. AI and ML capabilities recommend issue classification and help identify related issues from prior assessments. Organizations can define rules to auto-detect vulnerability patterns and auto-trigger remediation workflows. Issues are tracked through investigation, root cause analysis, and remediation to closure, with all activity recorded in an audit trail.
MetricStream IT and Cyber Risk Management supports both the first line (business units and IT operations) and the second line (risk management and compliance functions) through role-based dashboards and data access controls. First-line users can report vulnerabilities, track remediation actions, and view their assigned risk posture, while second-line functions gain a consolidated enterprise-wide view of IT risk. This shared platform eliminates the information gaps between lines of defense that often delay effective risk response.