Cybersecurity Risk Management Solution
Strengthen Cybersecurity Risk and Compliance Across Your Digital Enterprise
Move beyond fragmented security findings. Our cybersecurity compliance software connects cyber exposure, compliance frameworks, vendors, business impact, and resilience through AI assistants and agents.
Cyber Assistant
Ask about assets, vulnerabilities, controls, compliance, vendors, continuity, or remediation and receive contextual guidance.
Cyber Agents
Agents support risk assessment, control testing, evidence gathering, gap identification, treatment, and executive reporting.
Cyber Agent Ecosystem
Build and deploy agents tailored to your business with MetricStream and partners.
Measurable Impact of Smarter Cybersecurity Compliance & Risk Management
60
improvement across key Cyber GRC workflows with AI
40
reduction in risk assessments and control tests
50
lesser costs through GRC tool consolidation
Source: MetricStream’s Business Value Calculator
Amplifying Outcomes Across Cybersecurity and Compliance
Cybersecurity Risk Solution for Governed Cyber Resilience
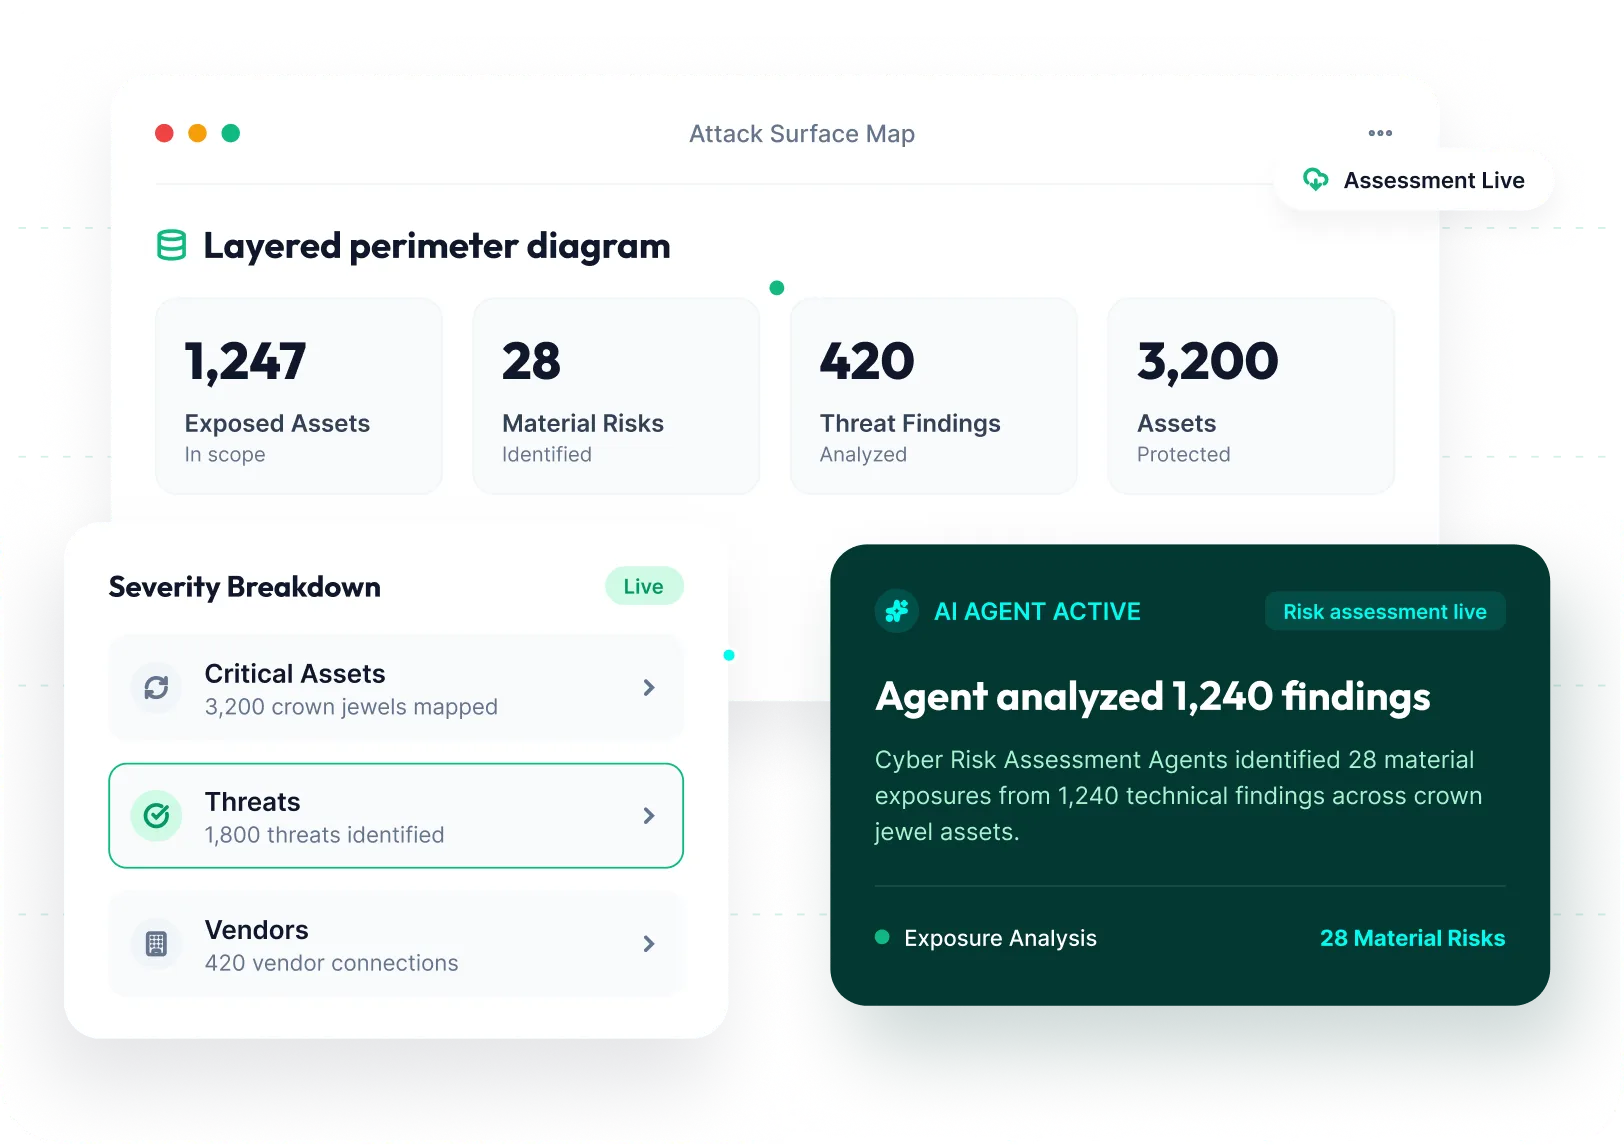
Identify Cyber Security Risk in Business Context for Prioritized Action
Identify cyber risks in a compliance context by connecting vulnerabilities, assets, controls, and business services, rather than reviewing each one in isolation. Connect Crown Jewel assets, risks, threats, vulnerabilities, controls, processes, vendors, and accountable owners in one environment. Cyber Risk Assessment Agents bring the right context into each assessment, helping you understand which technical findings create material exposure and which assets and services require attention first.
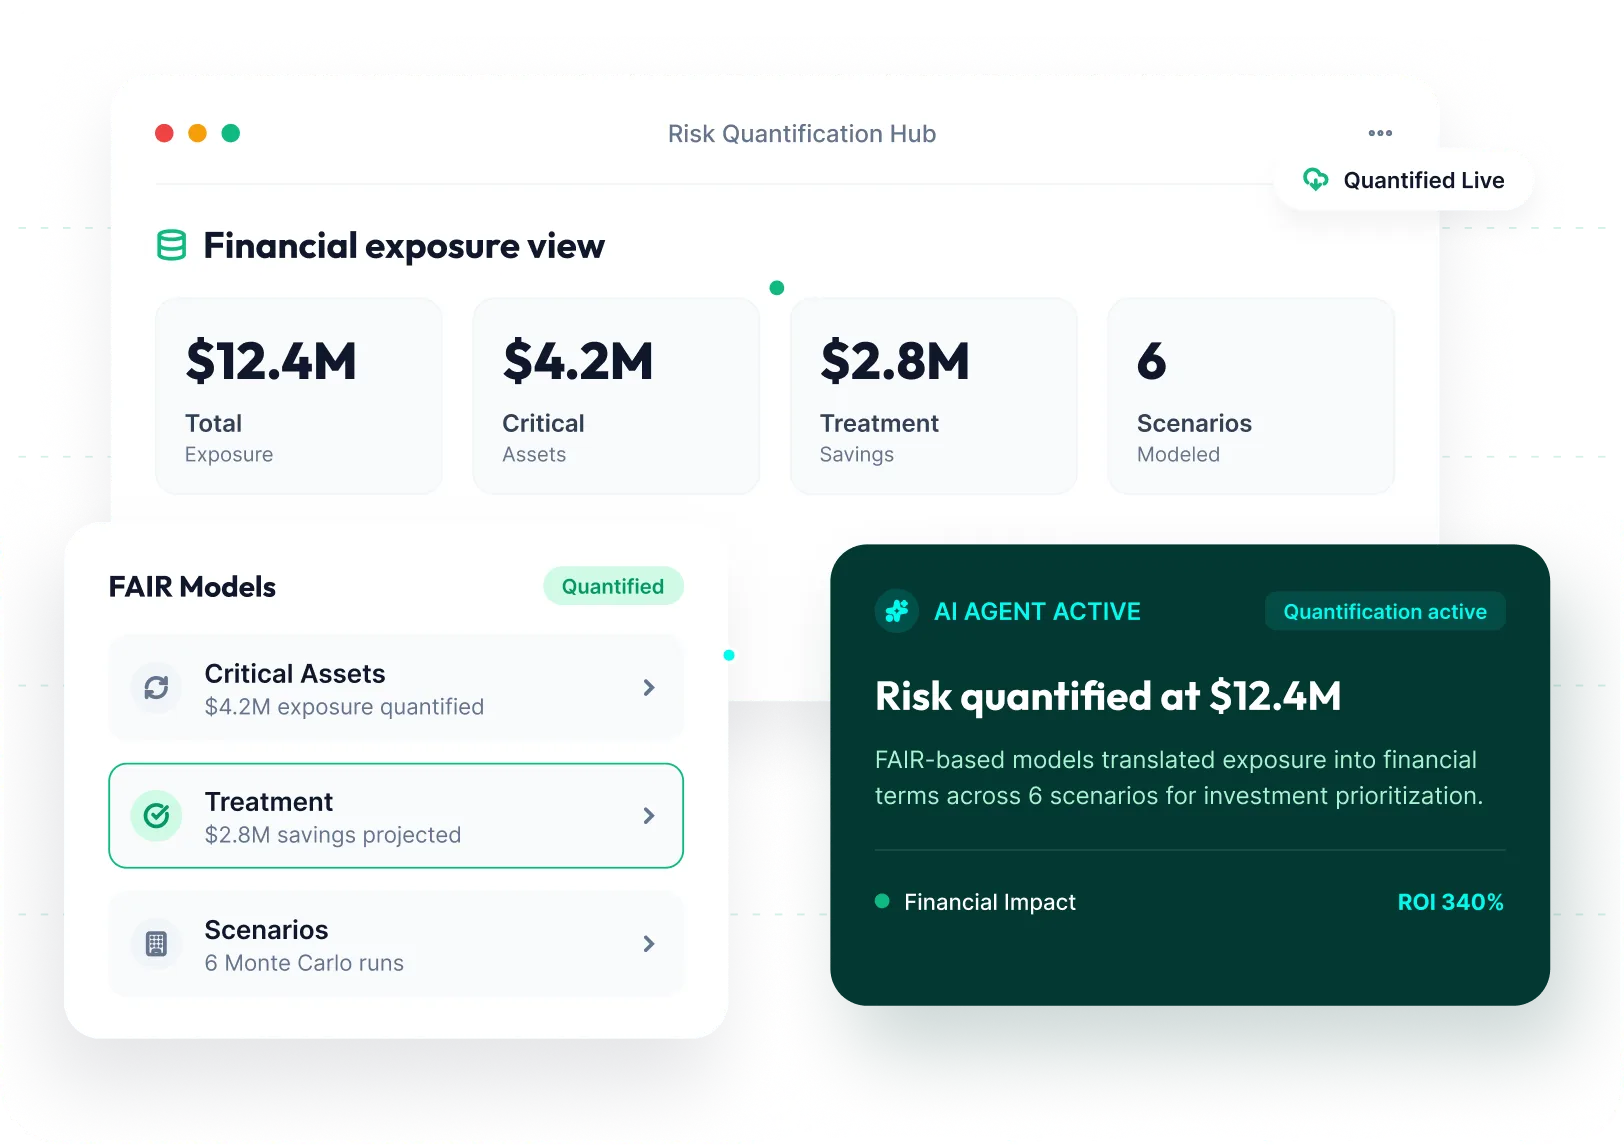
Target Action by Quantifying Cyber Risks in Financial Terms
Technical severity alone does not tell you where to invest. AI adds asset criticality, threat context, control effectiveness, and business impact to security findings. FAIR-based models and Monte Carlo simulations translate exposure into financial terms. Compare treatment scenarios, evaluate security investments, and explain cyber risk to executives and boards in a common business language.
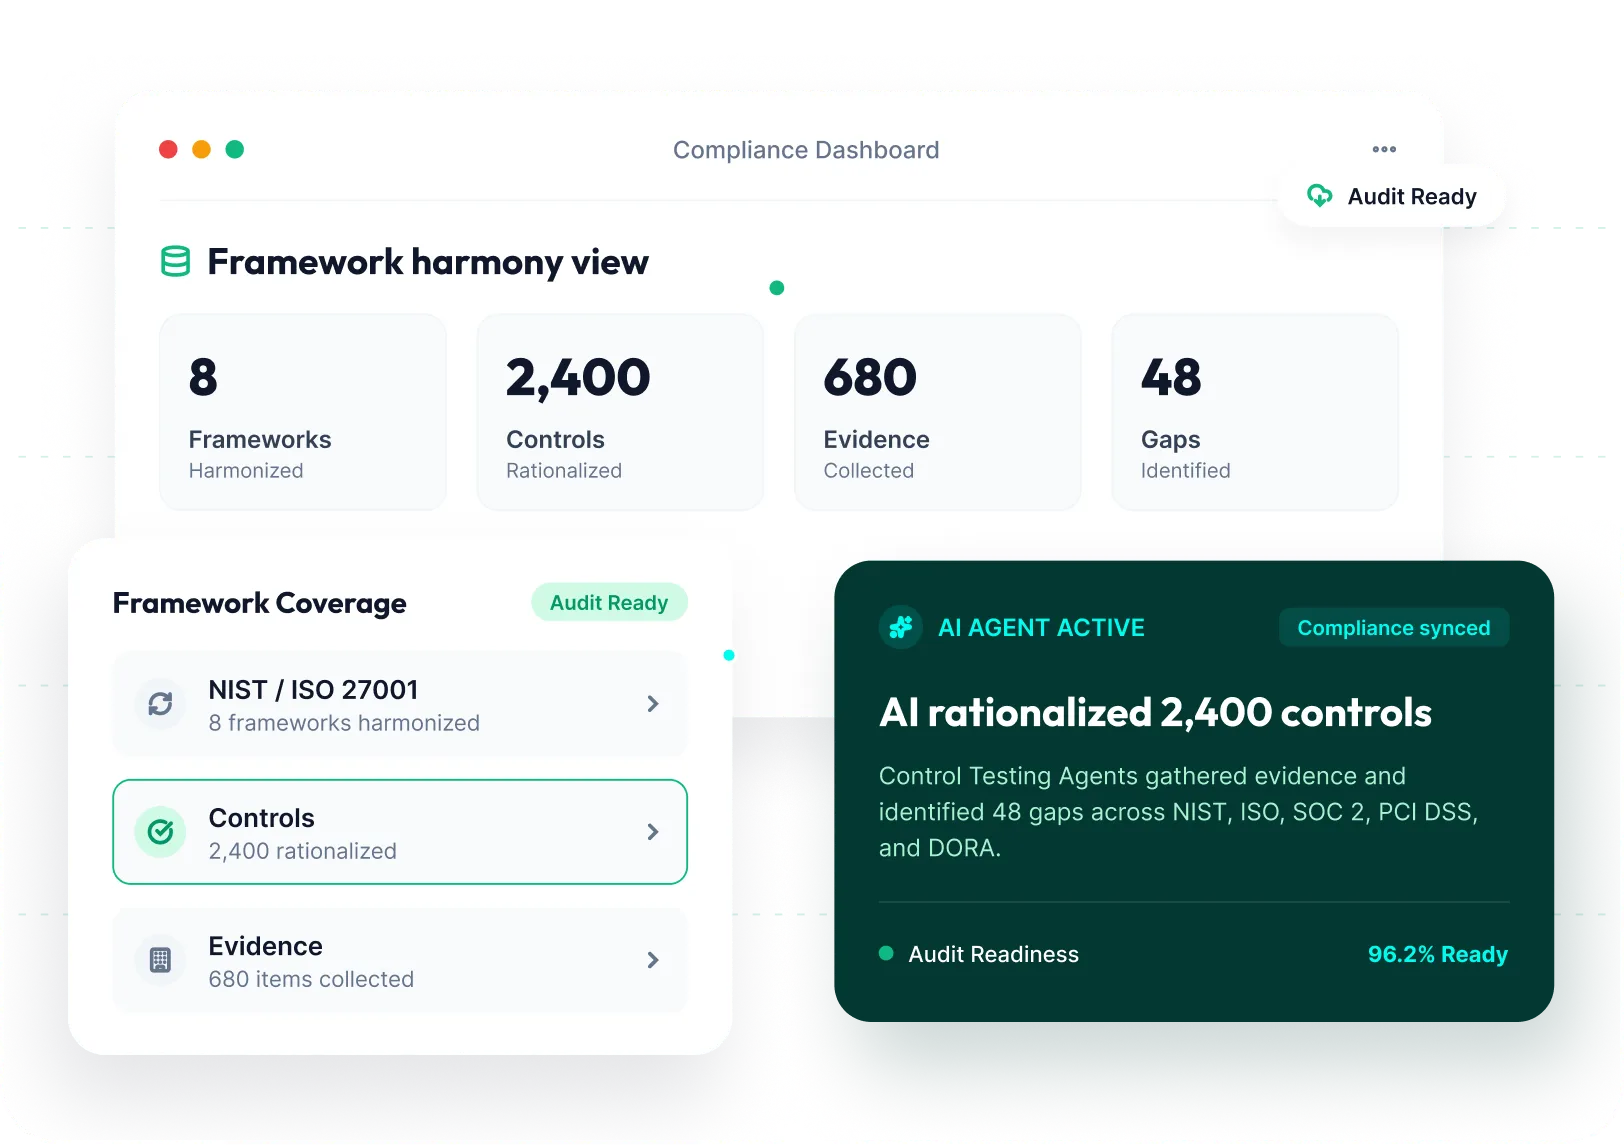
IT & Cyber Security Compliance Across Frameworks for Audit Readiness
Maintain compliance across all frameworks simultaneously by building assessments and collecting evidence across frameworks. Harmonize controls across NIST, ISO 27001, SOC 2, PCI DSS, HIPAA, GDPR, DORA, and other standards. AI rationalizes controls, drafts source-backed survey responses, and identifies gaps. Control Testing Agents gather evidence and summarize results, helping you stay audit-ready with less duplicate work.
Policy Assistants and Agents for Trusted Guidance
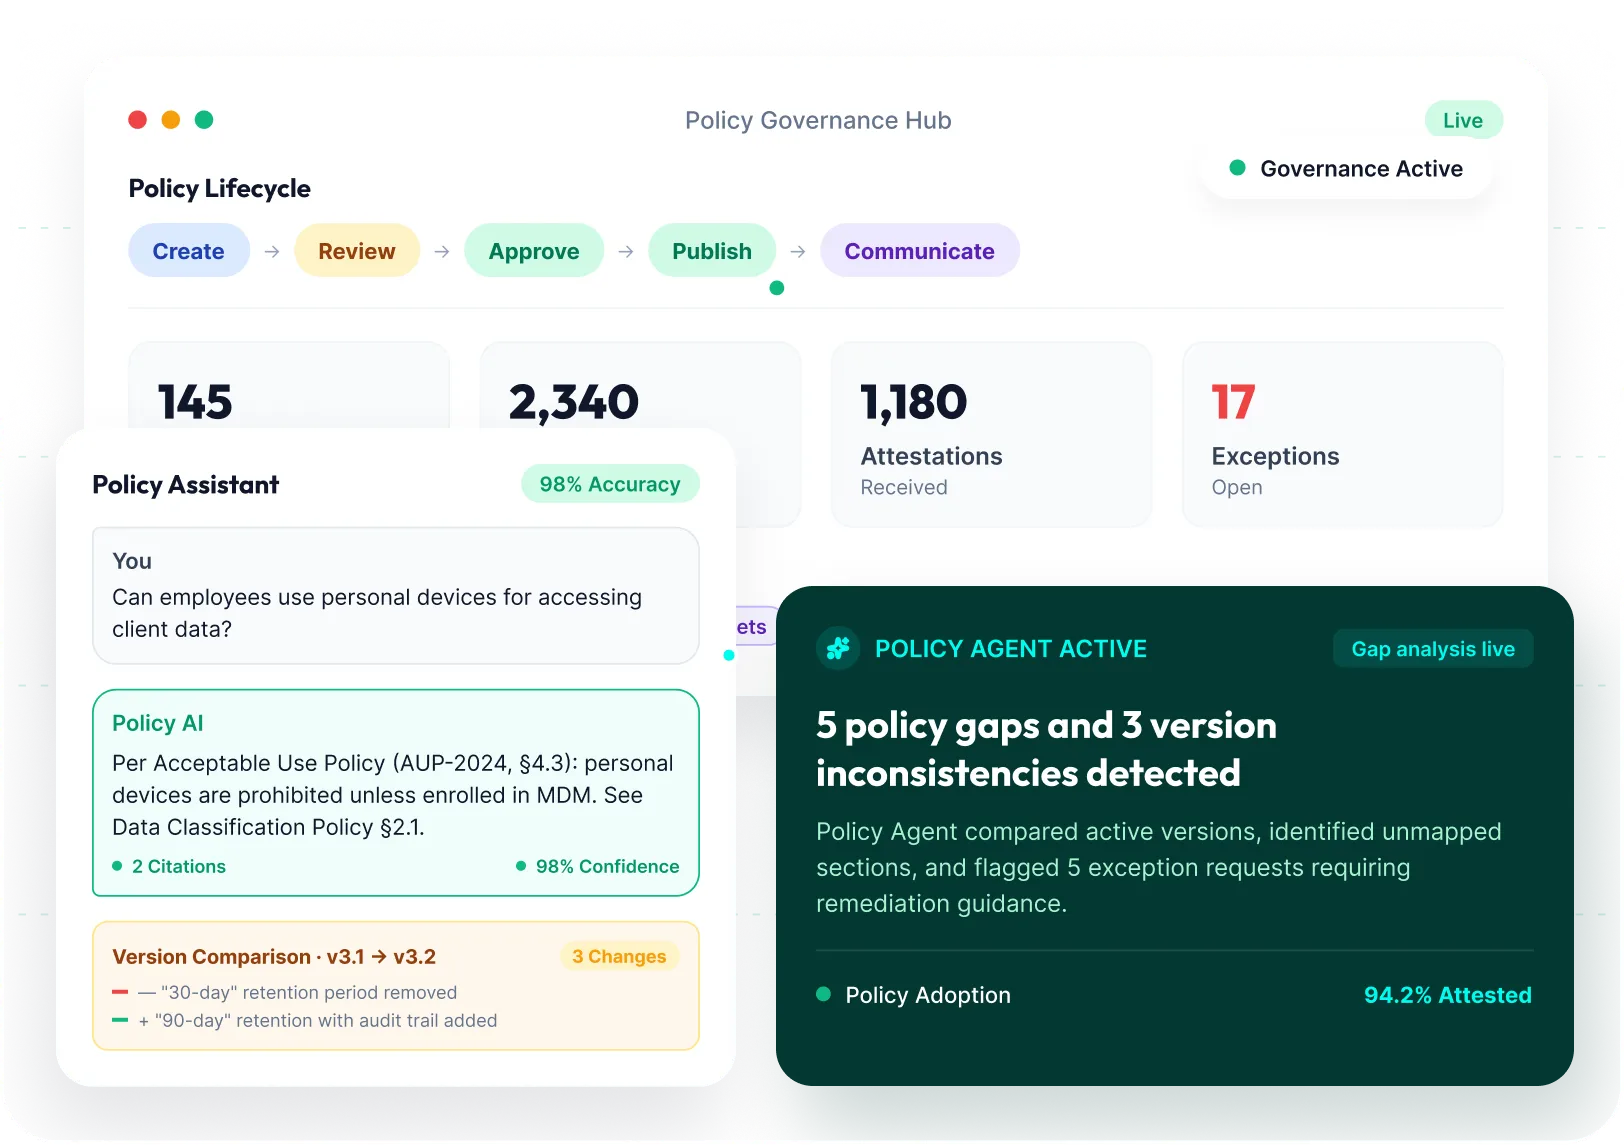
Create, map, review, approve, publish, and communicate IT and cyber policies within a single governed environment. Track attestations and exceptions while connecting policies to requirements, risks, controls, assets, processes, and business entities. Policy Assistant gives employees trusted, citation-backed answers from approved content. Policy Agents help compare versions, identify gaps and inconsistencies, and guide exception handling and remediation, strengthening policy adoption and continuous compliance.
Continuous Vendor Risk Monitoring for Proactive Action
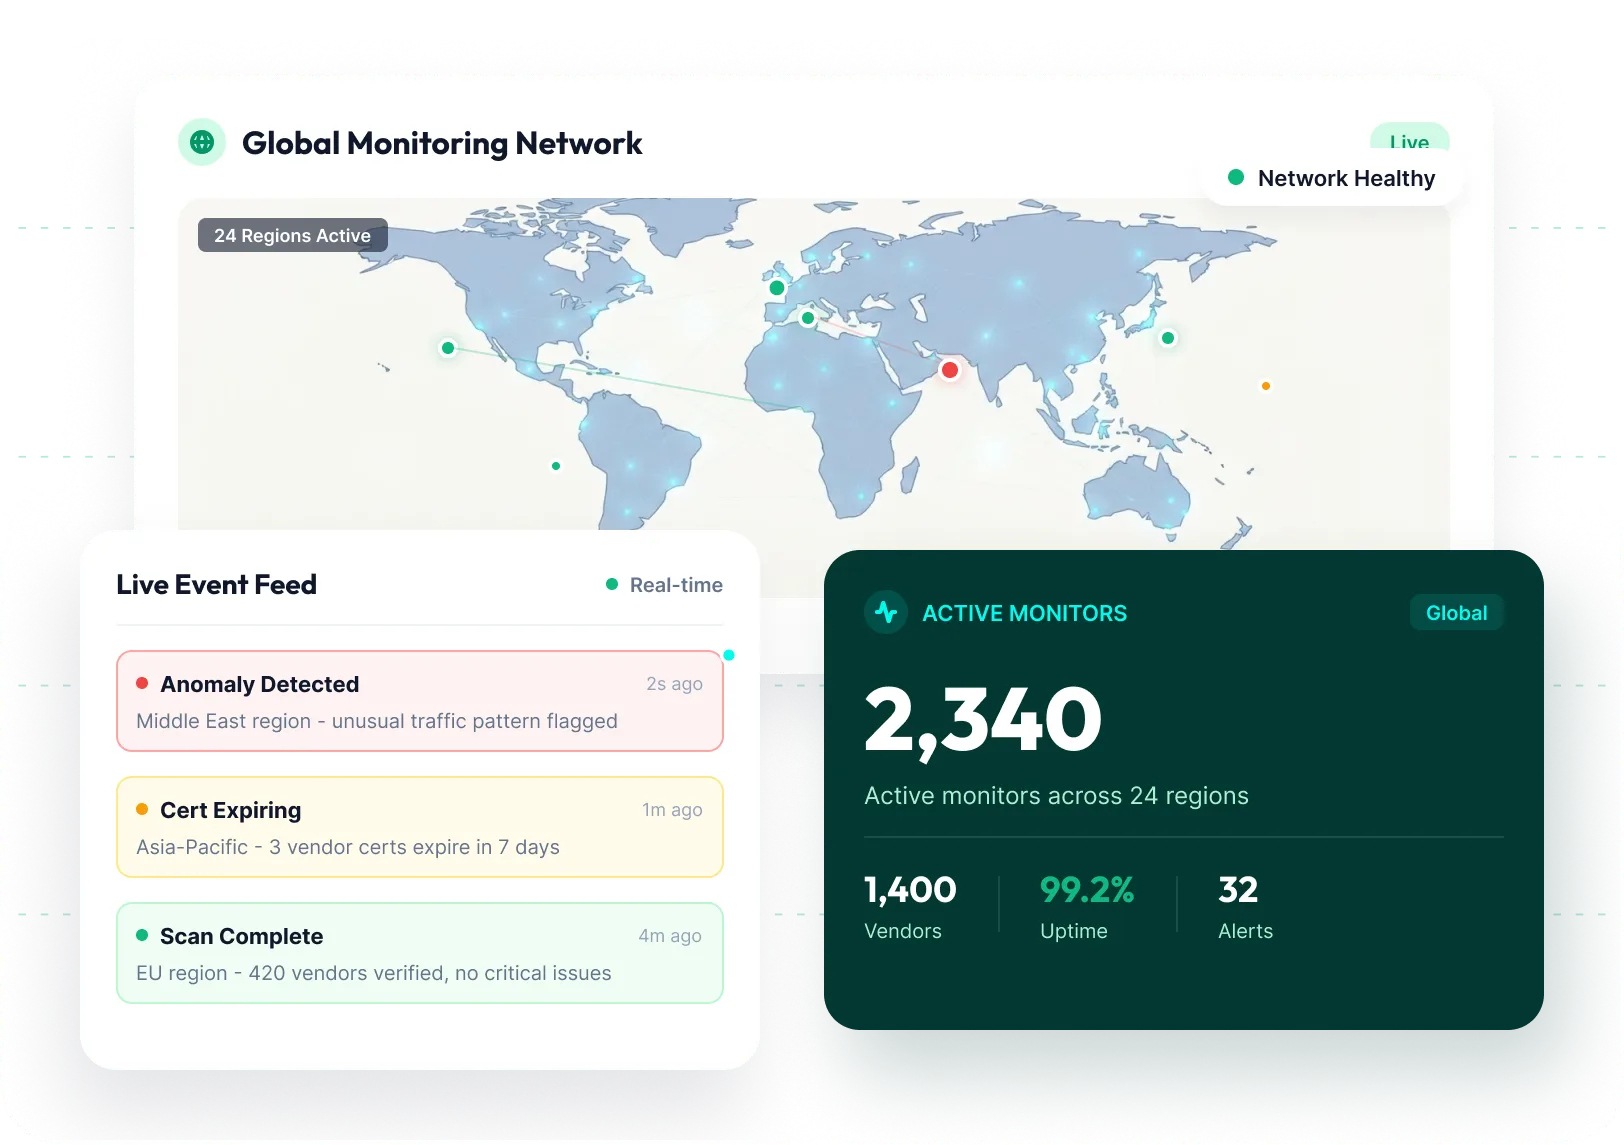
Vendor risk is connected to the assets, applications, data, critical services, and business processes that each relationship supports. Apply risk-based tiering, tailor assessments, interpret evidence, monitor external intelligence, and track certifications, incidents, performance, issues, and remediation throughout the vendor lifecycle. Vendor Risk Agents detect material changes and recommend appropriate action. Cyber leaders gain a current view of technology dependencies and vendor exposure—from onboarding and due diligence through monitoring, renewal, and secure offboarding.
Build Resilience and Protect Business Continuity
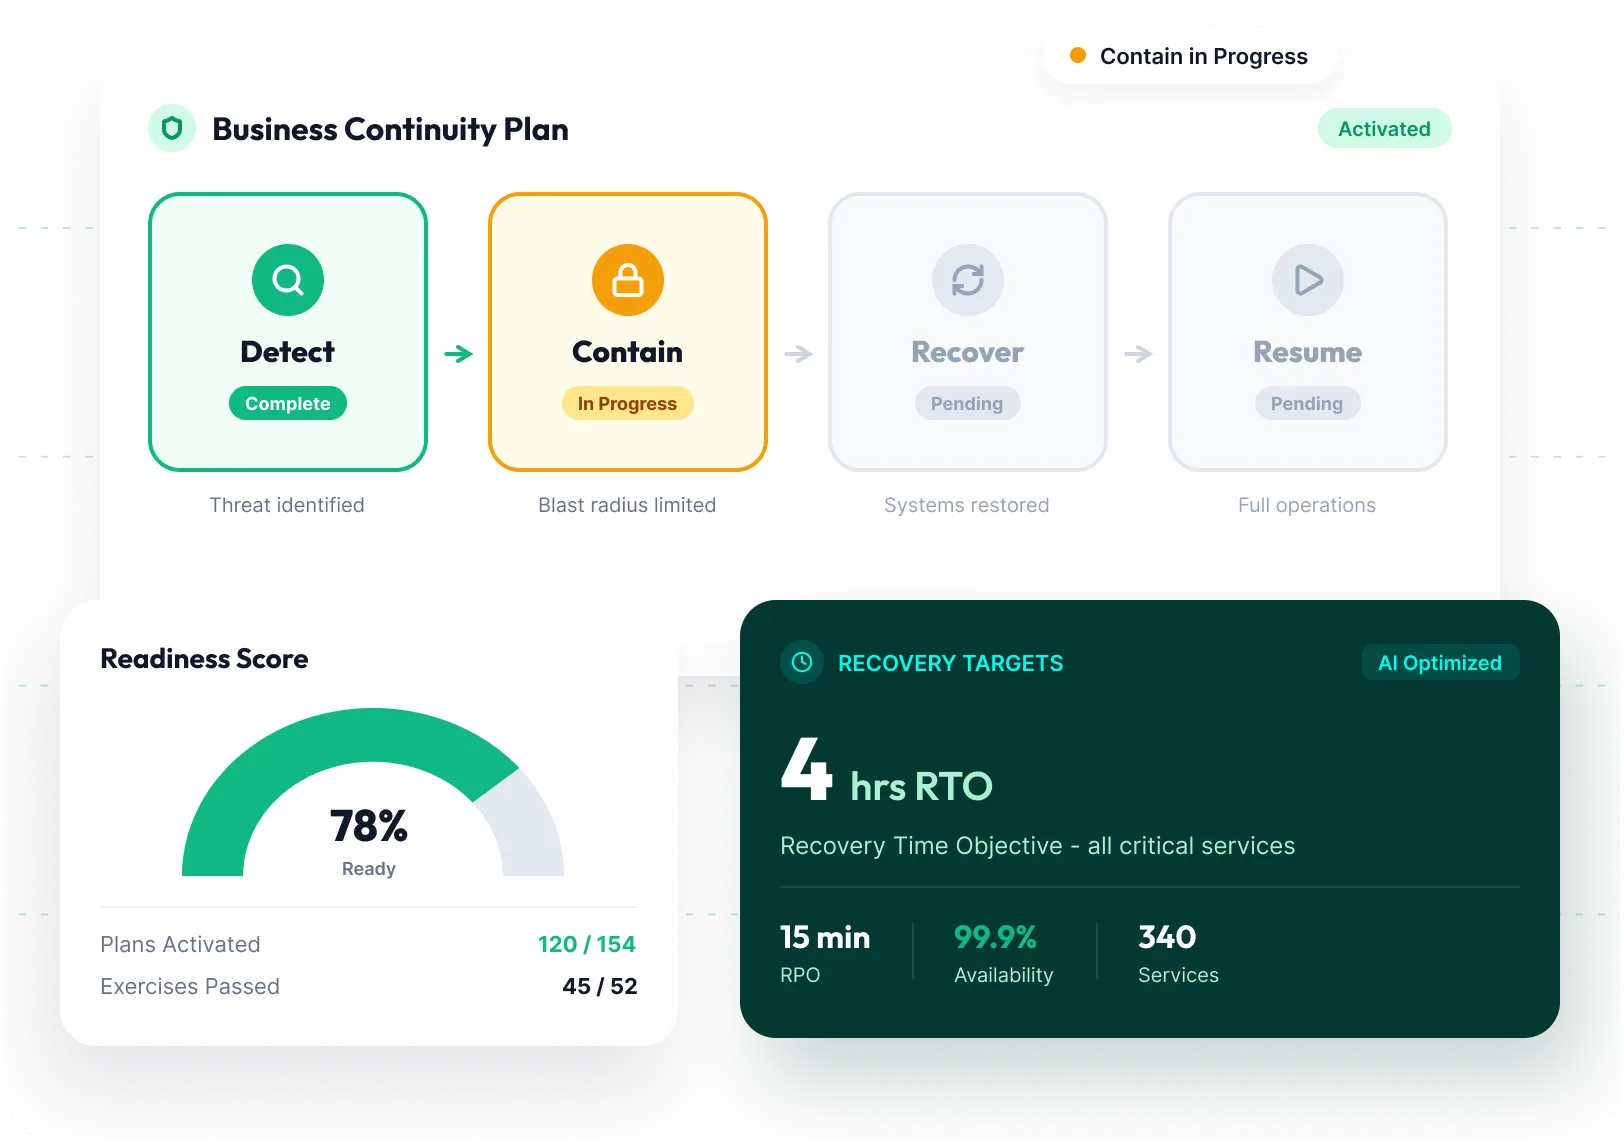
Connect cyber risk to the services your business must keep running. Map critical assets, processes, vendors, dependencies, recovery objectives, continuity plans, exercises, and crisis communications. AI-powered plan summaries and resilience intelligence enable you to identify gaps and coordinate response, strengthening readiness before disruption and supporting faster recovery of critical operations.
Resolve Issues and Report Outcomes With Confidence
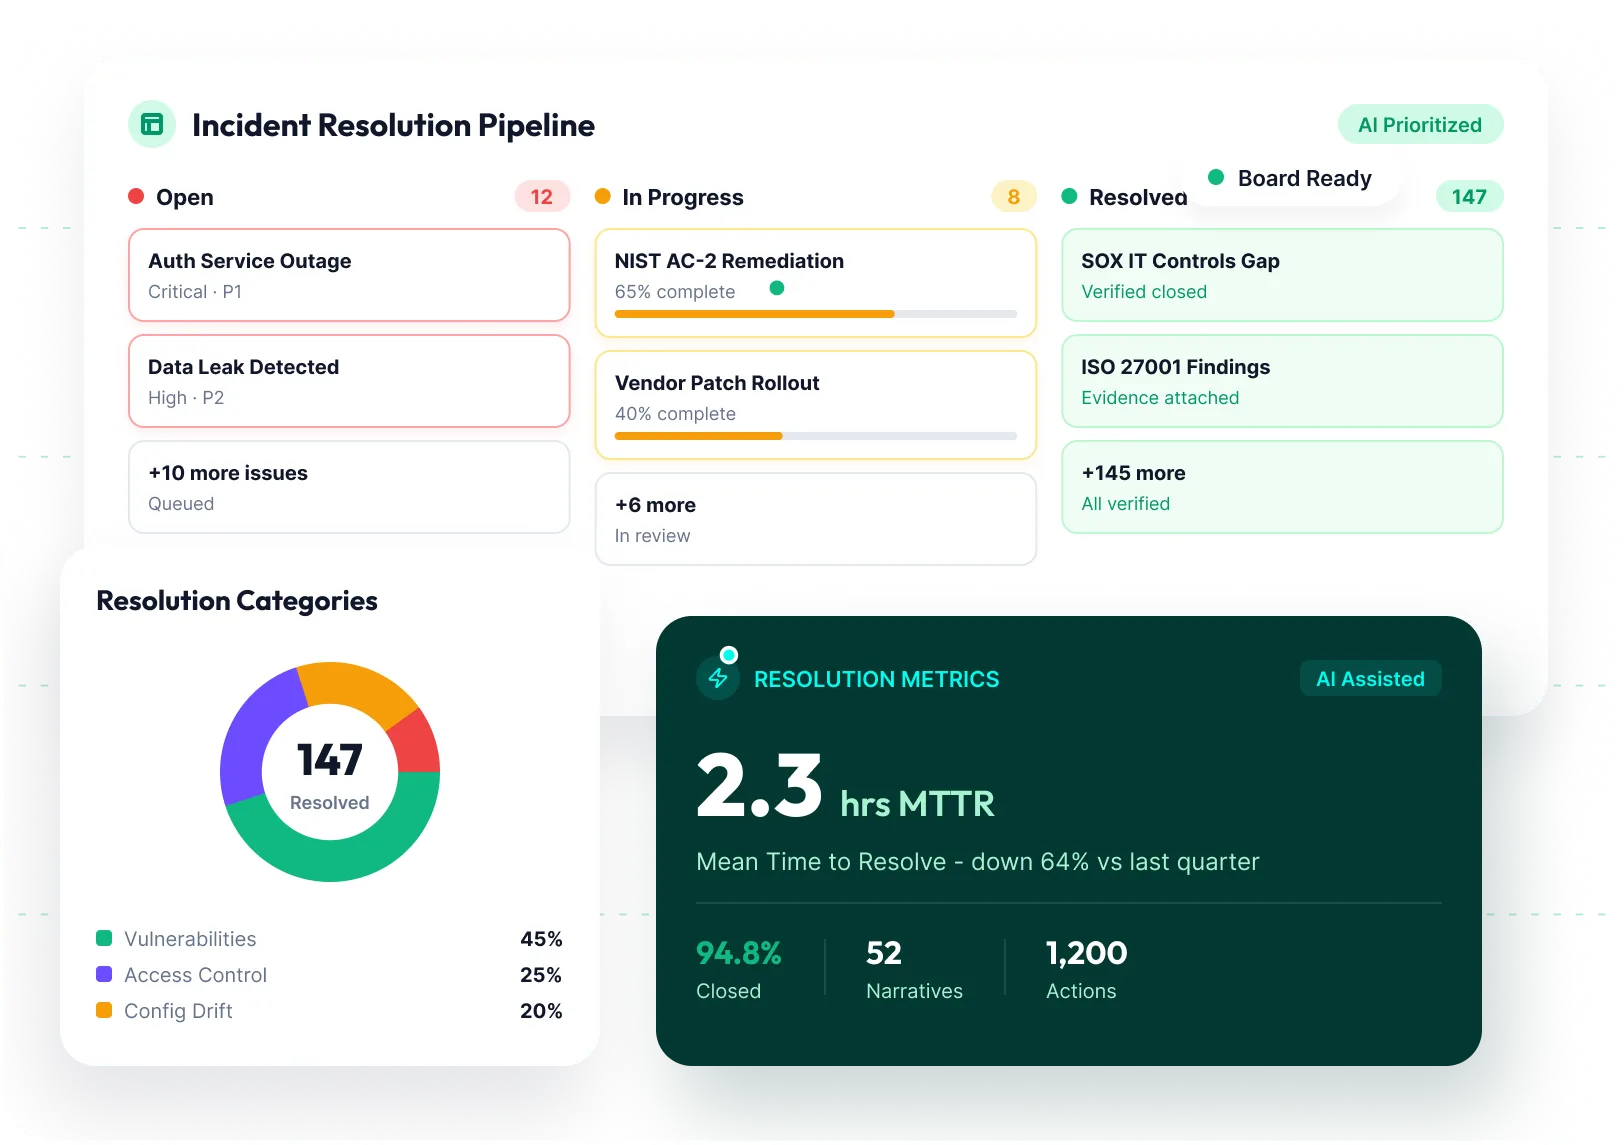
Turn vulnerabilities, control failures, evidence gaps, policy exceptions, and vendor findings into coordinated action. AI groups related issues and recommends remediation plans, while accountable owners manage deadlines, escalations, evidence, and verified closure. AI-generated narratives explain exposure, remediation progress, and remaining risk, giving CISOs a clear, defensible story for executives, auditors, regulators, and boards.
Traditional Cybersecurity Risk Management vs. MetricStream's AI-Powered Solution
Embraced by the Business. Trusted by the Board. Aligned with Auditor and Regulator Expectations.
-
Compliance-Aligned Cyber Risk
Connect compliance obligations, technical security findings to critical assets, services, obligations, dependencies, and business outcomes.
-
Cybersecurity Risk and Enterprise Integrations
Bring security, IT, asset, identity, threat, vendor, and operational data into governed workflows.
-
Cyber Risk Quantification
Communicate cyber exposure, mitigation choices, insurance considerations, and investment priorities in financial terms.
-
Continuous Cyber Risk Assurance
Monitor controls, evidence, compliance, vendors, issues, remediation, and changes in risk posture.
-
Integrated Cyber Resilience
Connect cyber risk with technology vendors, important services, business continuity, crisis response, and recovery.
-
Deep Cybersecurity Risk and AI Expertise
Work with specialists experienced in Cyber GRC, cybersecurity risk, resilience, compliance, and agentic AI.
See What MetricStream GRC Could Be Worth to Your Organization
Use our interactive ROI calculator, built by Forrester, to estimate what Enterprise GRC could deliver for your organization. Enter details such as annual revenue, number of GRC tools, and compliance exposure to see your potential savings, payback period, and return on investment.
Calculate My ROIInsights on AI and GRC

Analyst Report
MetricStream Named a Leader in IDC MarketScape 2025 Worldwide GRC Software Report
Download the excerpt to see why MetricStream was recognized as a GRC Leader in 2025.
Download Now
eBook
7 Key Strategic Priorities for Banking and Financial Services in 2026
Key priorities guiding BFS leaders through AI risk, regulation, and global volatility
Read More
Case Study
Financial Services Major Automates IT Control Assessments for Faster, Better Insights on Compliance
Learn how one of the world’s leading financial services companies enhances visibility into IT compliance risks by maintaining a federated approach to IT compliance management.
Read More
Whitepaper
Unlocking AI Value in GRC
Learn how GRC leaders are adopting AI responsibly and proving measurable ROI at scale.
Read MoreCybersecurity Risk Management Solution FAQs
MetricStream's Cybersecurity Solution provides a single platform for managing cybersecurity-related risk and compliance activities including IT and cyber risk management, compliance management, policy management, and IT vendor risk management. It aggregates and integrates data on IT and cyber risks, threats, compliance obligations, policies, and controls across enterprise silos, and delivers a 360-degree, real-time view of the organization's cyber risk and compliance posture through powerful dashboards and reports.
Cybersecurity compliance software must support GDPR, HIPAA, PCI DSS, SOC 2, NIST CSF, and other frameworks. MetricStream harmonizes controls and evidence across all standards simultaneously, reducing duplicate work.
Cybersecurity compliance software is a tool that helps organizations show that their security controls meet regulatory requirements, industry standards, and internal policies. It maps controls to those requirements, collects evidence, and tracks gaps through to remediation. Instead of keeping this information in spreadsheets and separate security tools, teams work from a shared record that compliance, security, and risk owners can use.
According to customer responses and the GRC Journey Business Value Calculator, MetricStream's Cybersecurity Solution has delivered a 66% reduction in time taken to complete risk assessments, a 38% reduction in the cost of managing vulnerabilities and their impact, and a 30% reduction in the number of work days required to manage a scaled-up level of vulnerability management.
MetricStream's Cybersecurity Solution helps CISOs anticipate and mitigate cyber risks by providing a continuous, integrated view of IT risks, threats, vulnerabilities, and controls across the enterprise. AI-powered issue identification surfaces related risks before they escalate, Cyber Risk Quantification capabilities express exposure in dollar terms to support investment decisions, and role-based executive dashboards communicate the cyber risk posture clearly to the board and regulators. This enterprise-wide visibility allows security leaders to act proactively rather than reactively.
MetricStream's Cybersecurity Solution manages compliance with IT regulations and governance standards—including SOX, FFIEC mandates, PCI-DSS, HIPAA, NERC-CIP, NIST, and ISO 27001/2—through a central compliance hierarchy that links regulations, processes, assets, risks, controls, and audits. Integration with the Unified Compliance Framework (UCF) maps over 9,300 IT control statements to more than 1,200 regulations. Automated alerts notify teams when regulatory standards change so they can respond quickly.
MetricStream's Cybersecurity Solution proactively aggregates and correlates threats and vulnerabilities across business-critical information assets. IT assets are consolidated from Configuration Management Databases (CMDBs) and mapped to associated threats and vulnerabilities. Integrations with endpoint IT security and infrastructure management tools and security intelligence feeds allow organizations to identify and prioritize risks across their full asset portfolio. Real-time graphical dashboards with drill-down capabilities report on threats and vulnerabilities by asset, severity, and business unit.
MetricStream's Cybersecurity Solution includes a dedicated IT Vendor Risk Management capability that provides a single point of reference for identifying, assessing, mitigating, and monitoring IT vendor risks. Vendor registration and onboarding are accelerated through automated workflows. Pre-defined questionnaires simplify vendor due diligence, and powerful analytics help management teams make informed decisions based on vendor risk, compliance, and performance data. This is especially important given that vendor IT systems often represent significant points of cyber risk exposure.
MetricStream's Cybersecurity Solution communicates cyber risk to the board using Cyber Risk Quantification capabilities that express risk exposure in dollar values, using the FAIR model. This financial framing translates technical cyber risk data into business-relevant metrics that boards and C-suite executives can readily understand and act on. Role-based dashboards with drill-down capabilities and customizable reports allow security teams to tailor board communications to specific audiences and regulatory requirements.
MetricStream's Cybersecurity Solution includes a Policy and Document Management capability that enables systematic management of IT policies across business units, divisions, and global locations. A centralized policy portal stores, manages, and provides access to IT policies. Policies are linked to regulations, risks, controls, and legal requirements, and automated notifications alert the target audience when policies are published or revised. Attestation workflows confirm that employees have read and understood each policy.
MetricStream's Cybersecurity Solution includes Business Continuity Management capabilities with pre-embedded plan templates, configurable scoring logic for calculating Recovery Time Objectives (RTO) and Recovery Point Objectives (RPO), and integration with Emergency Mass Notification Systems (EMNS). Multiple recovery strategies can be tracked through Gantt charts, and configurable dashboards highlight gaps between recovery requirements and current readiness. These capabilities ensure that cyber incidents are managed within a broader resilience framework.
MetricStream's Cybersecurity Solution reduces vulnerability management costs by consolidating vulnerability data from multiple scanning tools, prioritizing remediation based on combined risk ratings that weigh both vulnerability severity and business asset criticality, and automating the creation and tracking of remediation action plans. This structured, risk-based prioritization approach ensures that resources are directed to the most impactful vulnerabilities, reducing the overall volume of remediation work and its associated costs.