IT & Cyber Policy Assistant
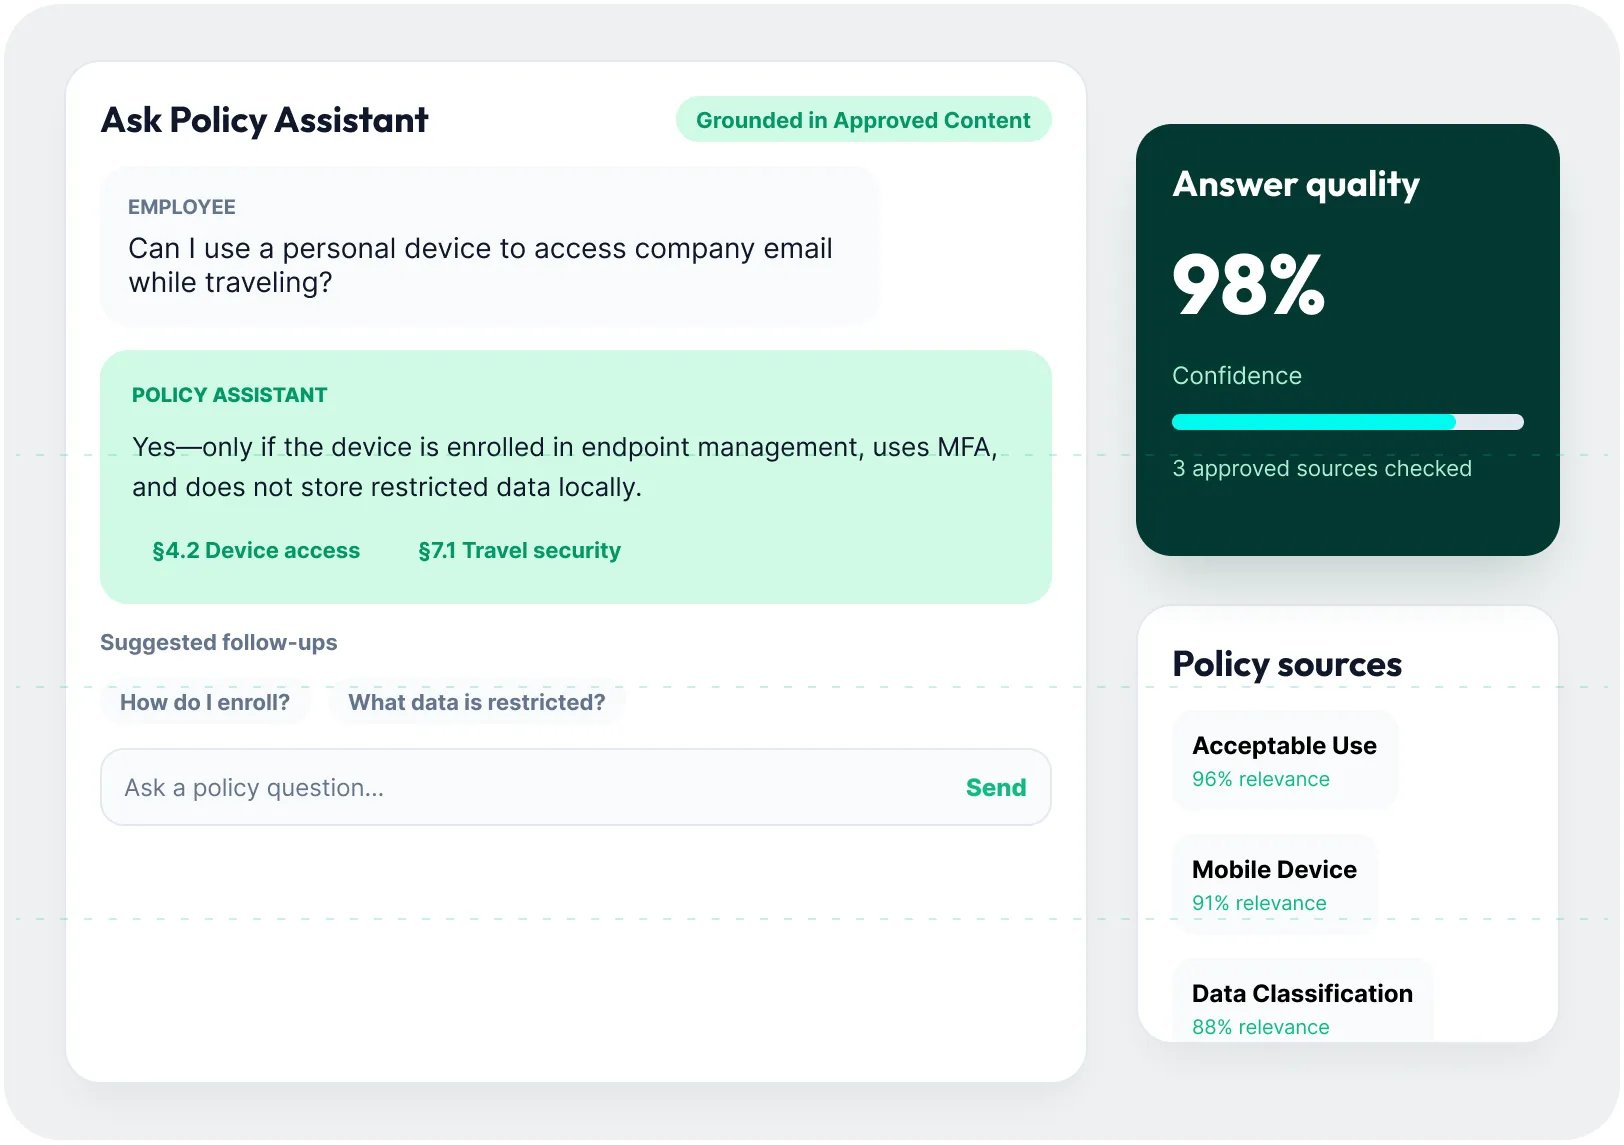
Give employees instant, citation-backed answers from approved cyber policies and guide them to the right action.
Empower teams with cited answers from approved IT & cyber policy content, with AI assistants and agents handling authoring, mapping, attestation, and exceptions.
Give employees instant, citation-backed answers from approved cyber policies and guide them to the right action.
Purpose-built agents support policy authoring, mapping, comparison, attestation, exception handling, and remediation.
Build and deploy agents tailored to your IT & cyber policy needs with MetricStream and partners.
60%
Improvement in IT and cyber policy governance and enforcement workflows
50%
Lower costs through consolidation of siloed tools
50%
Lower costs associated with regulatory audit findings
Source: MetricStream’s Business Value Calculator
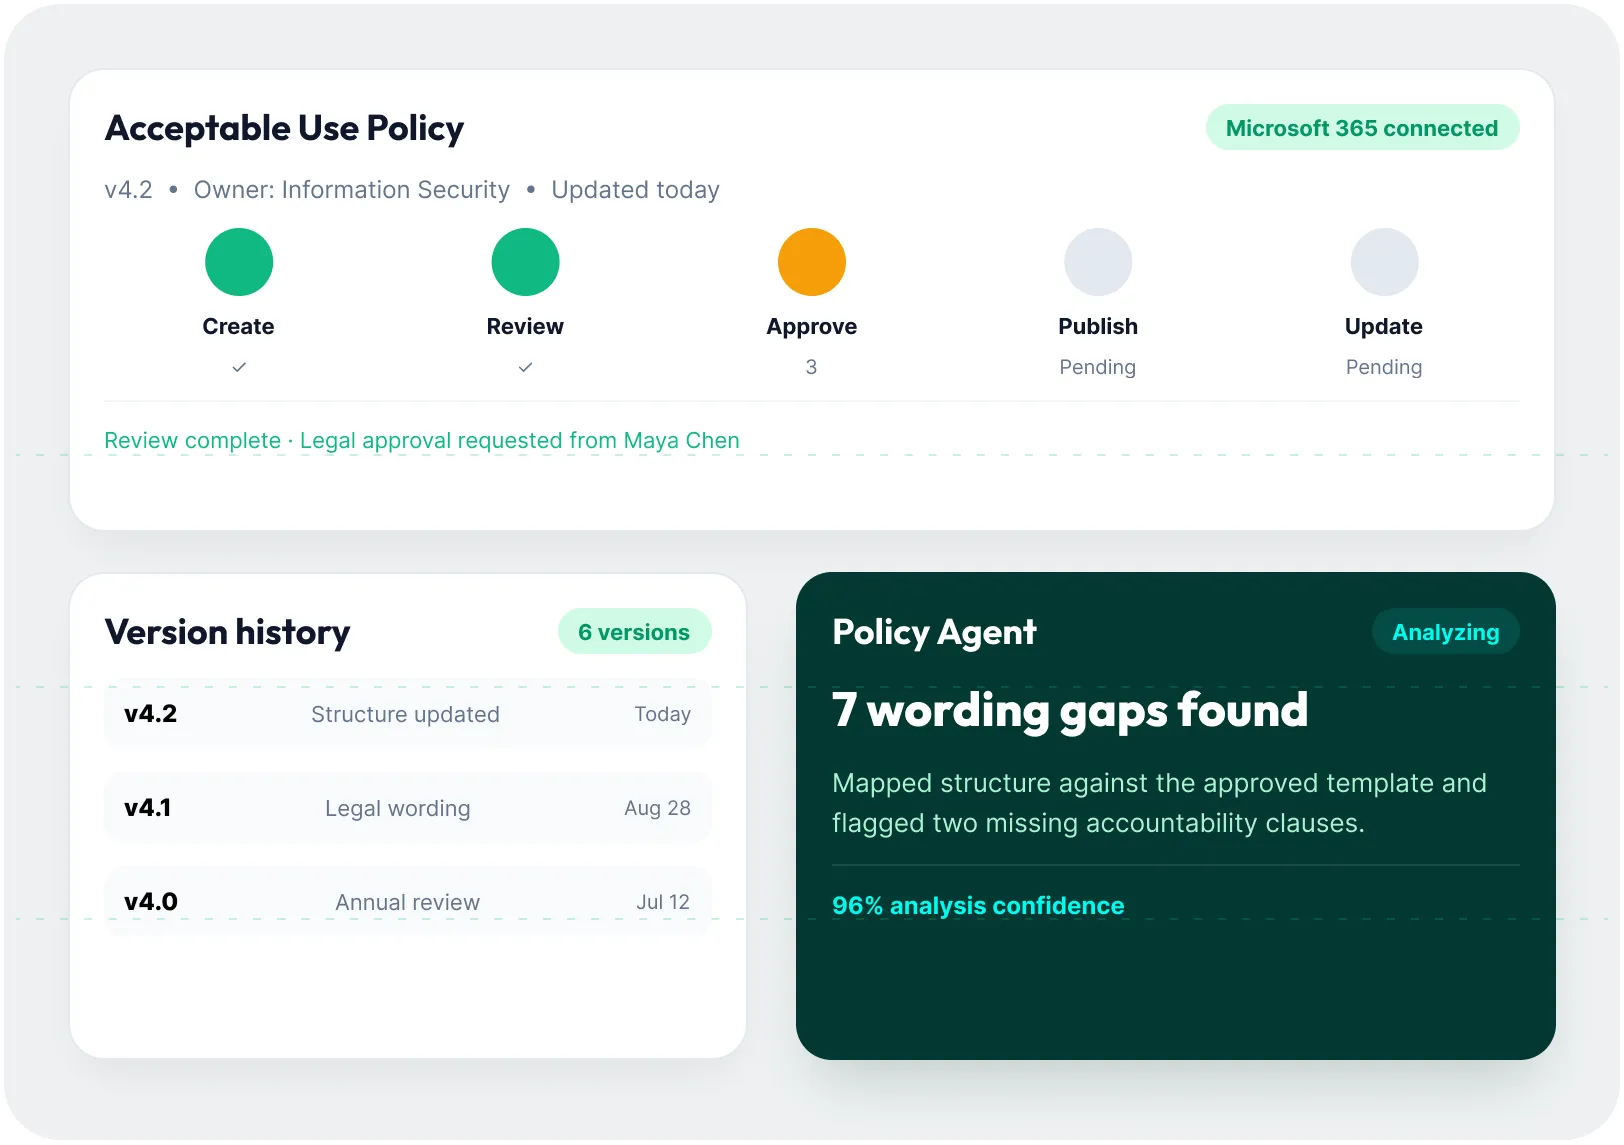
Stop managing IT, cybersecurity, and information security policies through disconnected documents, email reviews, and manual trackers. Create, upload, structure, review, approve, publish, and update policies through governed workflows. Microsoft 365 collaboration and reusable templates help you work faster. Policy Agents analyze wording, structure, complexity, and gaps, then recommend improvements while preserving ownership, versions, and approval history.
Policy Capability
Traditional IT & Cyber Policy Management
MetricStream Agentic IT & Cyber Agentic Policy Management
Policy discovery
Manual searches through documents
Policy Assistant delivers cited answers from approved content
Policy authoring
Disconnected drafting and review
Agents recommend clearer, more consistent policy content
Policy mapping
Relationships maintained manually
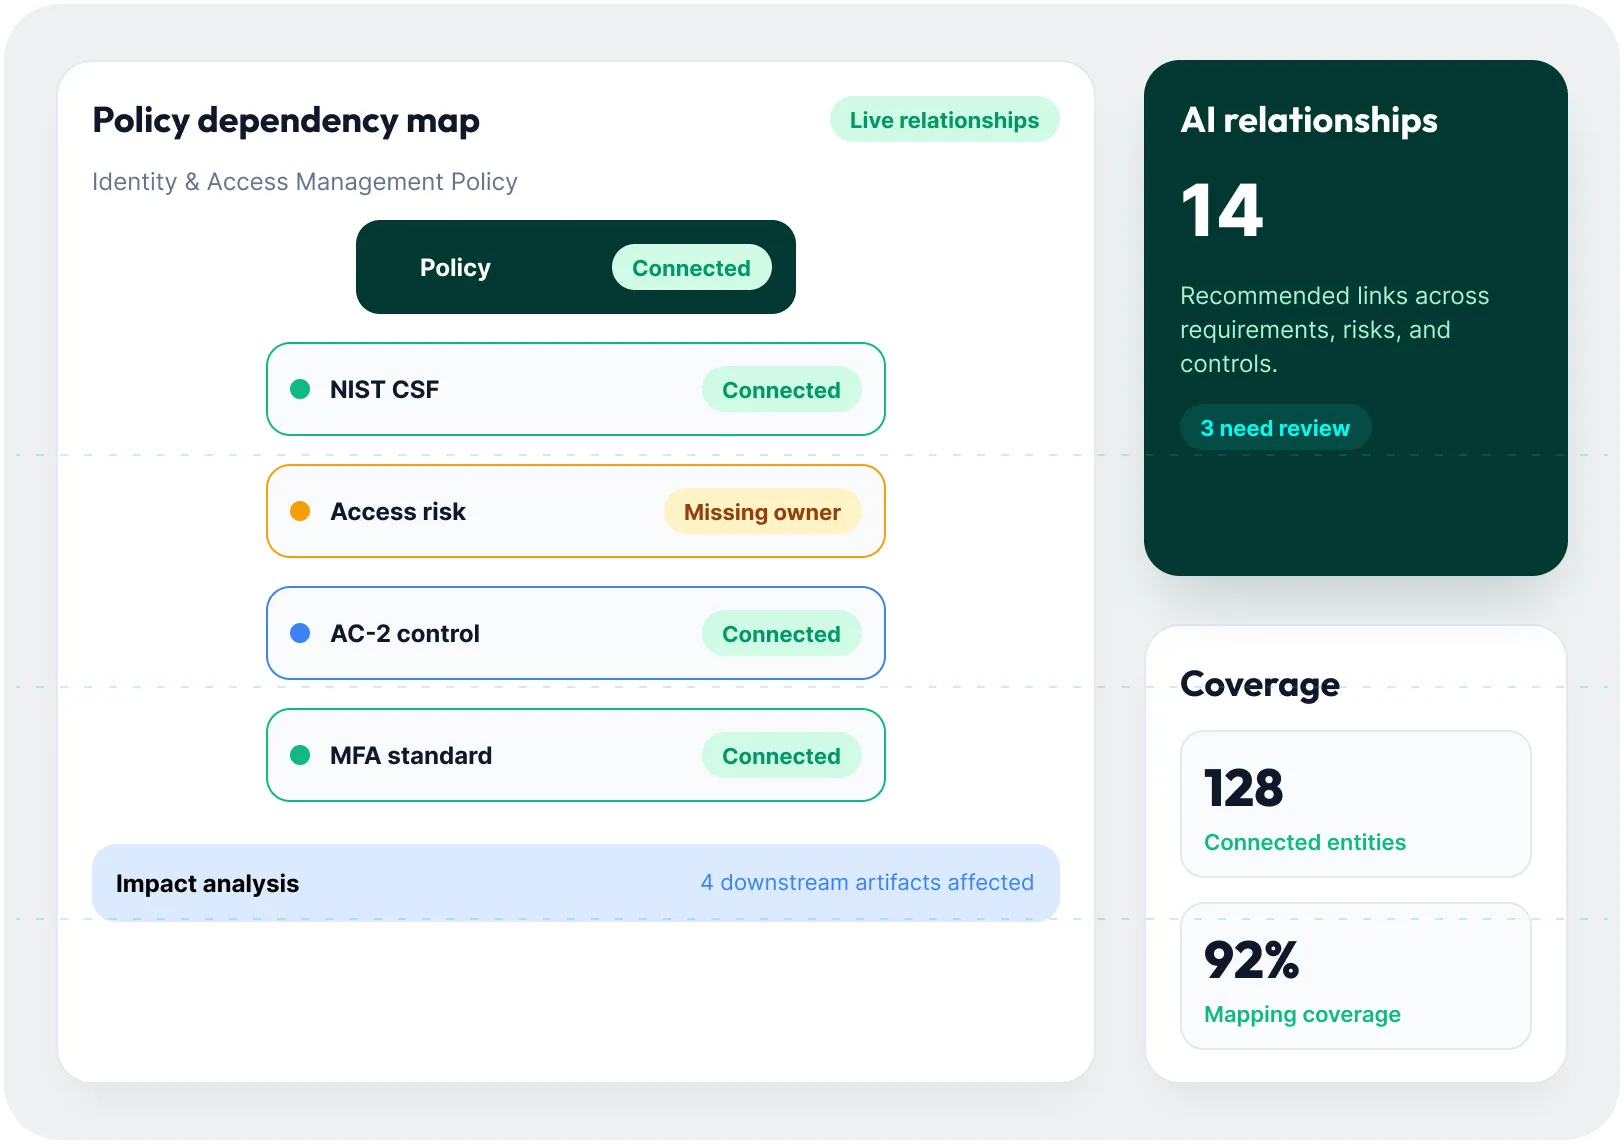
AI recommends links to requirements, risks, and controls
Version review
Line-by-line comparison
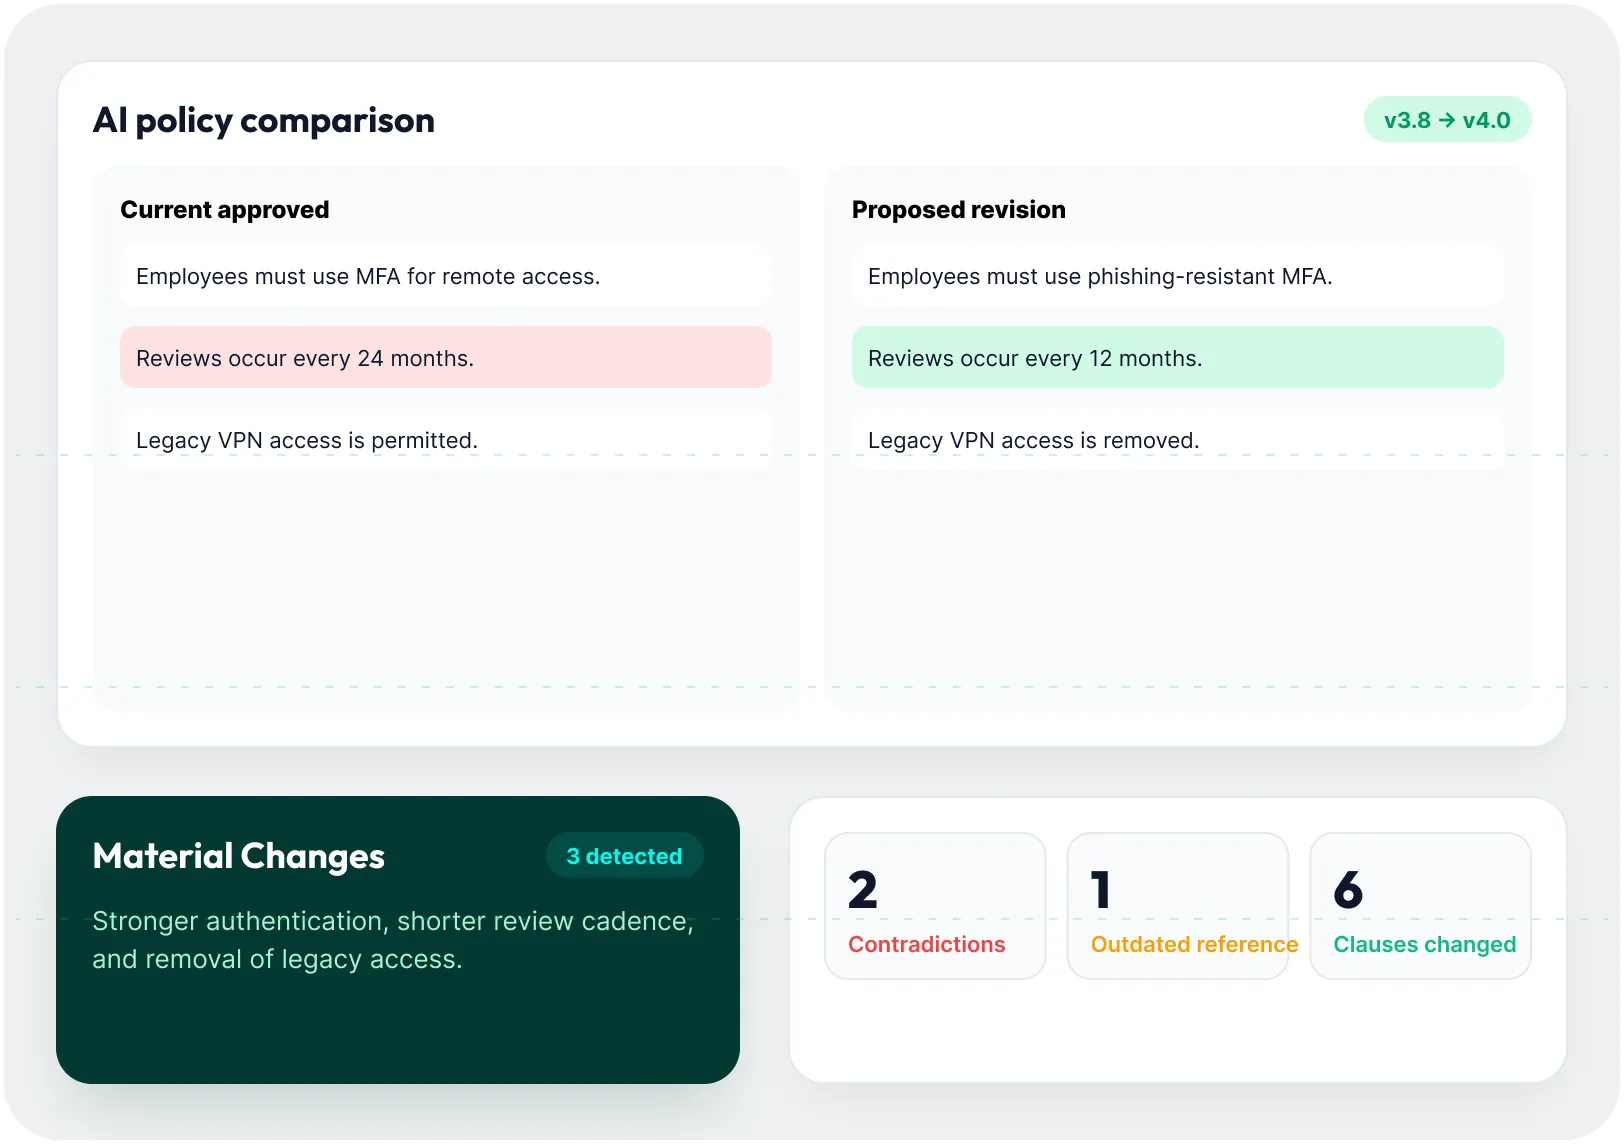
AI-powered redlining highlights relevant changes
Policy consistency
Conflicts discovered during review or audit
AI identifies overlaps, contradictions, and outdated references
Attestation
Email reminders and spreadsheets
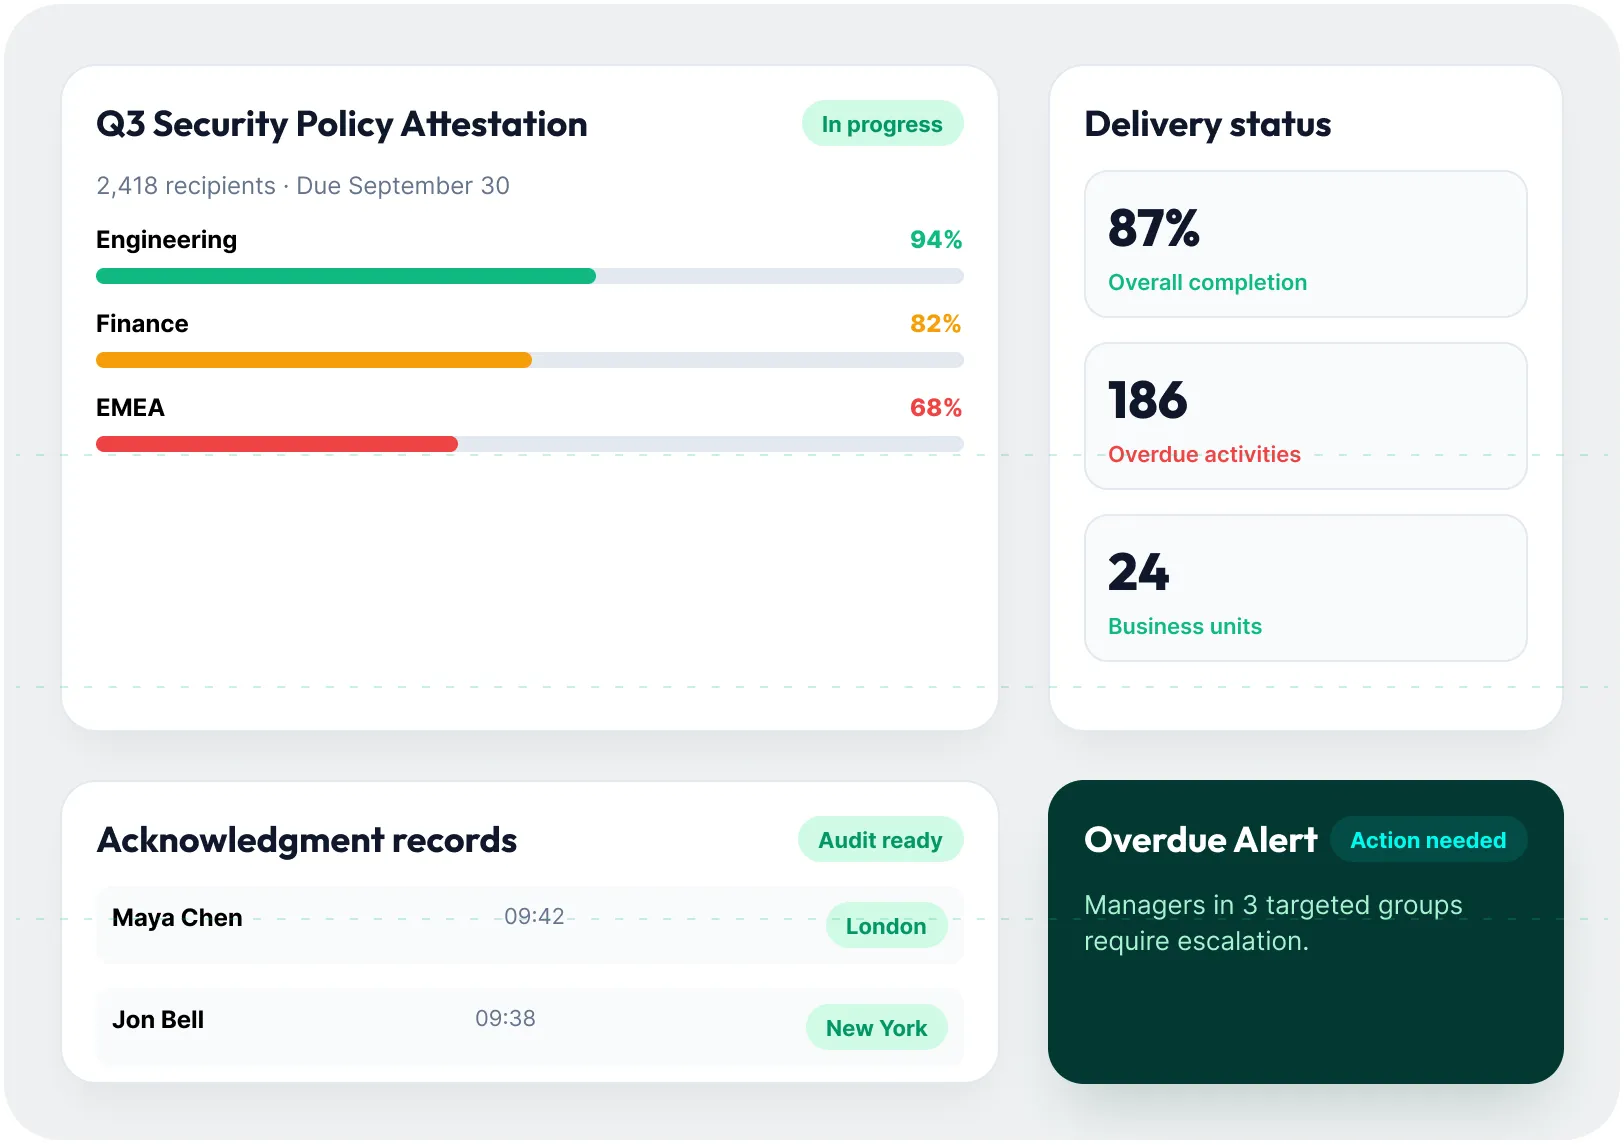
Agentic workflows monitor completion and preserve evidence
Exceptions
Limited visibility across requests
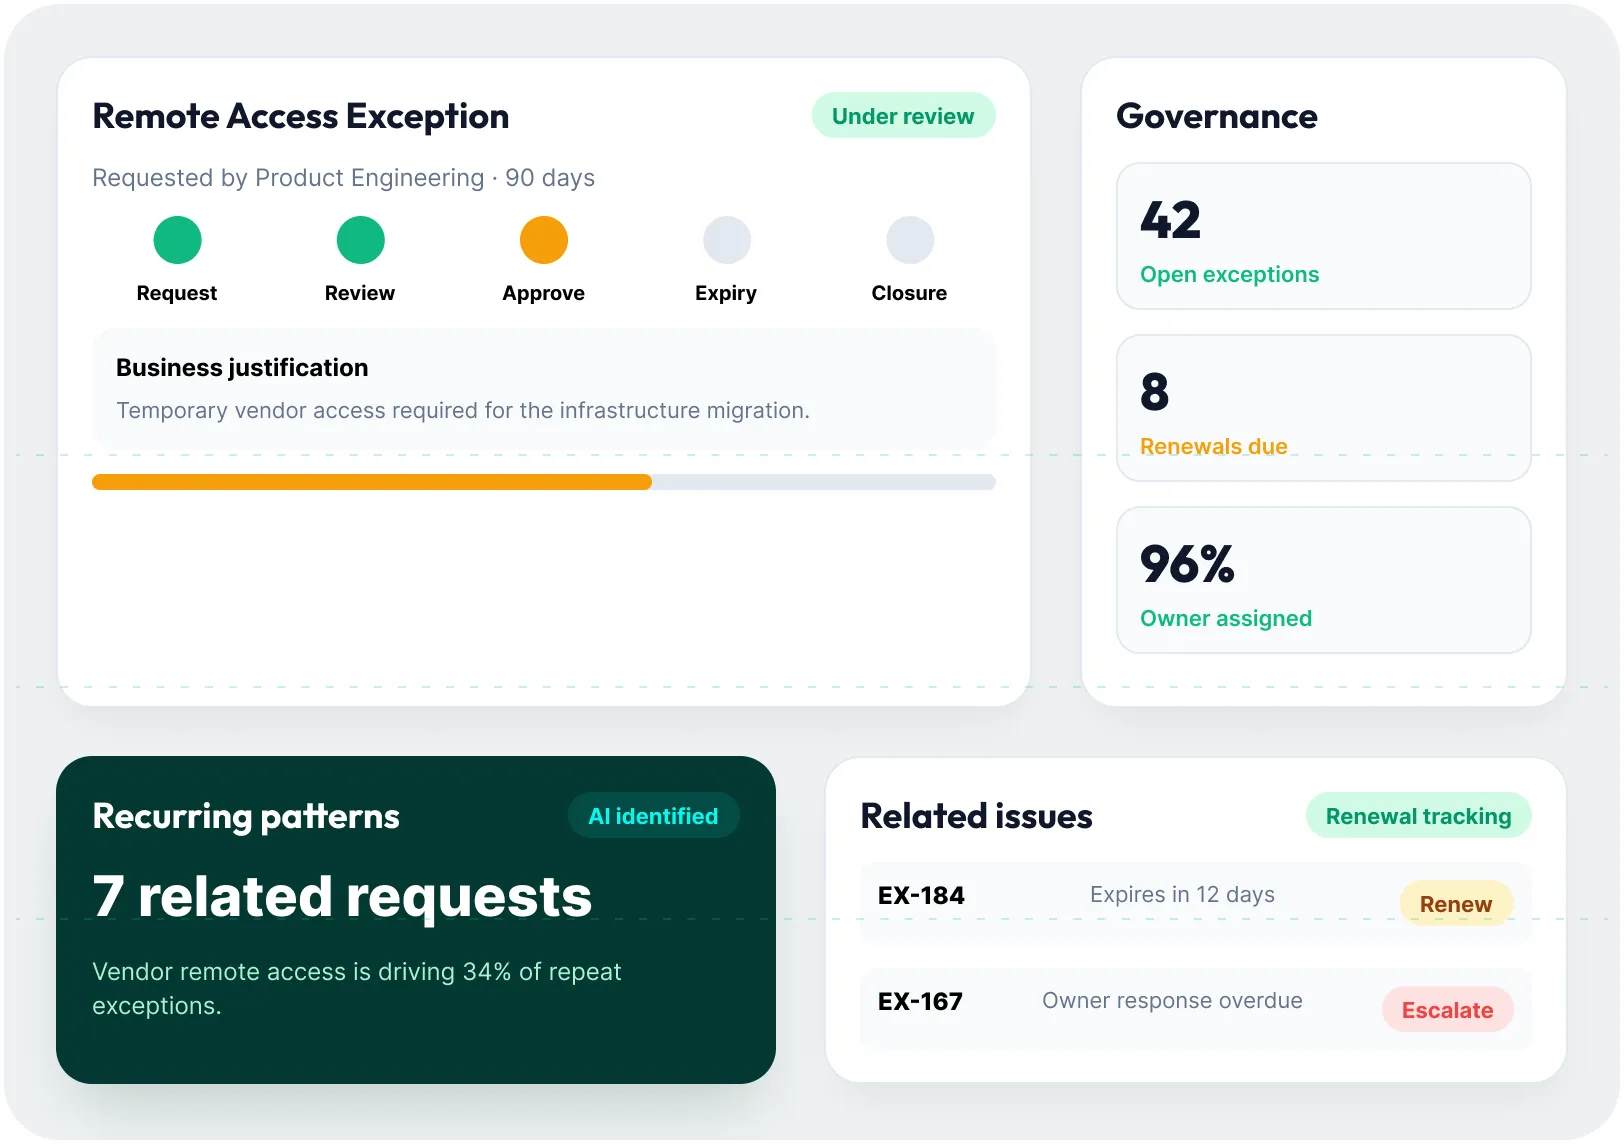
AI identifies patterns and recommends appropriate action
Use our interactive ROI calculator, built by Forrester, to estimate what Enterprise GRC could deliver for your organization. Enter details such as annual revenue, number of GRC tools, and compliance exposure to see your potential savings, payback period, and return on investment.
Calculate My ROI
IT & Cyber Policy Assistant grounds answers in approved, accessible policy content and provides citations for verification.
Link policies with regulations, requirements, controls, risks, assets, processes, and organizational entities.
Manage authoring, review, approval, publishing, communication, attestation, exceptions, and remediation in one place.
Configure IT & cyber policy templates, routing, reviewers, audiences, attestations, exceptions, workflows, and dashboards.
Preserve citations, versions, approvals, acknowledgments, exceptions, decisions, actions, and complete IT & cyber policy history.
Work with IT & cyber policy, compliance, cyber, and AI specialists throughout implementation and ongoing program development.

Analyst Report
Download the excerpt to see why MetricStream was recognized as a GRC Leader in 2025.
Download Now
eBook
Why compliance automation matters, how to harness it effectively and what to keep in mind when using automated and AI powered solutions
Read More
Case Study
Learn how MetricStream helped an oil and gas giant automate cyber risk and compliance management processes and improved its overall cyber maturity and resilience.
Read More
Whitepaper
Learn how GRC leaders are adopting AI responsibly and proving measurable ROI at scale.
Read MoreMetricStream IT and Cyber Policy Management is an AI-native IT policy management software product that enables organizations to simplify and strengthen IT governance by streamlining the creation, communication, attestation, and lifecycle management of IT and cyber policies. It centralizes policy documentation, automates review and approval workflows, maps policies to regulatory and compliance requirements, and provides real-time visibility across the policy lifecycle. The product integrates with Microsoft 365 for collaborative policy authoring.
MetricStream’s 2026 Business Value Calculator models up to a 60% improvement in IT and cyber policy governance workflows with AI. It also models 50% lower technology costs through tool consolidation and 50% lower costs associated with regulatory audit findings as broader Cyber GRC benefits.
MetricStream IT and Cyber Policy Management includes an intent-based policy search capability powered by natural language processing (NLP). Employees can search for IT and cyber policies using natural language queries through the centralized policy portal, intranet widgets, or a conversational chatbot interface. The search also surfaces related risk and compliance information, helping frontline employees quickly find the specific policy guidance they need without manually browsing a document library.
MetricStream IT and Cyber Policy Management enables attestation workflows for IT and cyber policies at the level of individual users or user groups. Attestation tasks appear on the policy portal, and the system requires each user to scroll through the entire policy document before attesting—ensuring policies are read, not just acknowledged. Policy exception requests can also be submitted directly from the portal, with configurable workflows to manage and track each exception through approval.
MetricStream IT and Cyber Policy Management supports collaborative policy creation through its integration with Microsoft 365, which allows multiple stakeholders to simultaneously view and edit IT and cyber policy documents. Built-in automated workflows route policies for review and approval, with the option to send individual sections to different reviewers. Multiple approvers can collaborate on the review process and add comments or feedback before a policy is published.
As cybersecurity management software, MetricStream IT and Cyber Policy Management allows organizations to map entire IT and cyber policies, or specific sections within them, to relevant regulations, risks, controls, legal requirements, processes, and organizational units. This mapping means that when a regulation changes, compliance teams can quickly identify which policies are affected and need to be updated. Automated notifications alert relevant stakeholders when IT policy changes are made, reducing the risk of policies falling out of alignment with regulatory requirements.
MetricStream IT and Cyber Policy Management provides real-time visibility into policy status, exceptions, and attestations through dynamic dashboards and drill-down reports. Compliance managers can view statistics on policy type, approval status, audit history, in-process documents, and links to compliance and related risks. This level of transparency ensures that policy owners, compliance teams, and executive leadership all have a shared, accurate view of the organization's policy management posture.
MetricStream IT and Cyber Policy Management allows employees to request exceptions to IT and cyber policies directly from the policy portal by specifying the reason and the duration of the requested exception. Configurable workflows route exception requests to the appropriate approvers, and the status of all exceptions is tracked in real time. This structured approach to exception management ensures that deviations from policy are documented, reviewed, and governed rather than informally managed.
MetricStream IT and Cyber Policy Management strengthens IT governance by ensuring that IT and cyber policies are consistently created, reviewed, approved, communicated, and attested across the enterprise. The platform's automated workflows eliminate manual policy management steps that are prone to delays and inconsistencies. By maintaining a centralized, up-to-date policy library with a full audit trail, organizations can demonstrate to regulators and auditors that their IT governance processes are mature, systematic, and well-controlled.
MetricStream IT and Cyber Policy Management is designed for IT governance professionals, compliance officers, CISOs, and their teams who are responsible for maintaining the organization's IT and cyber policy framework. Business unit managers and frontline employees interact with the platform to read policies, submit attestations, and request exceptions. External stakeholders, including auditors and regulators, can be granted time-limited access to view specific policy documents and their associated compliance records.