IT Vendor Risk Assistant
Get contextual answers across technology vendors, assessments, evidence, controls, issues, and performance.
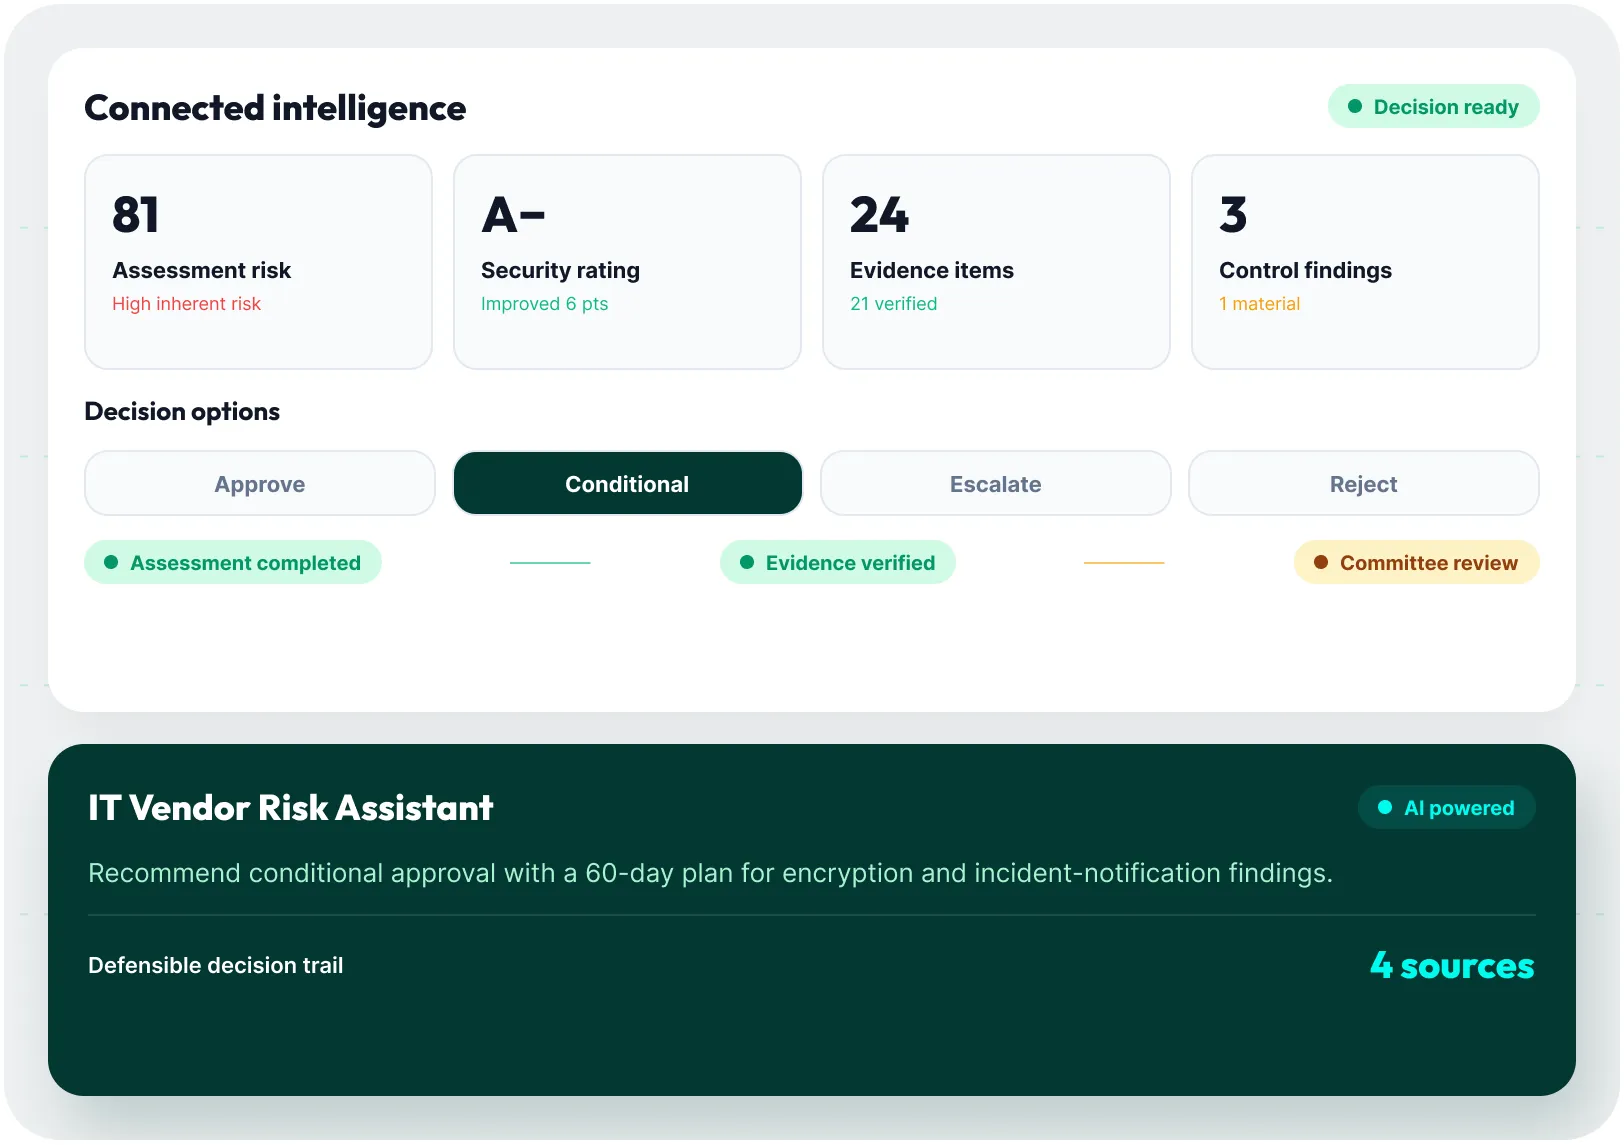
Replace annual questionnaires and stale vendor ratings with AI-powered vendor risk monitoring across onboarding, assessments, monitoring, remediation, and offboarding.
Get contextual answers across technology vendors, assessments, evidence, controls, issues, and performance.
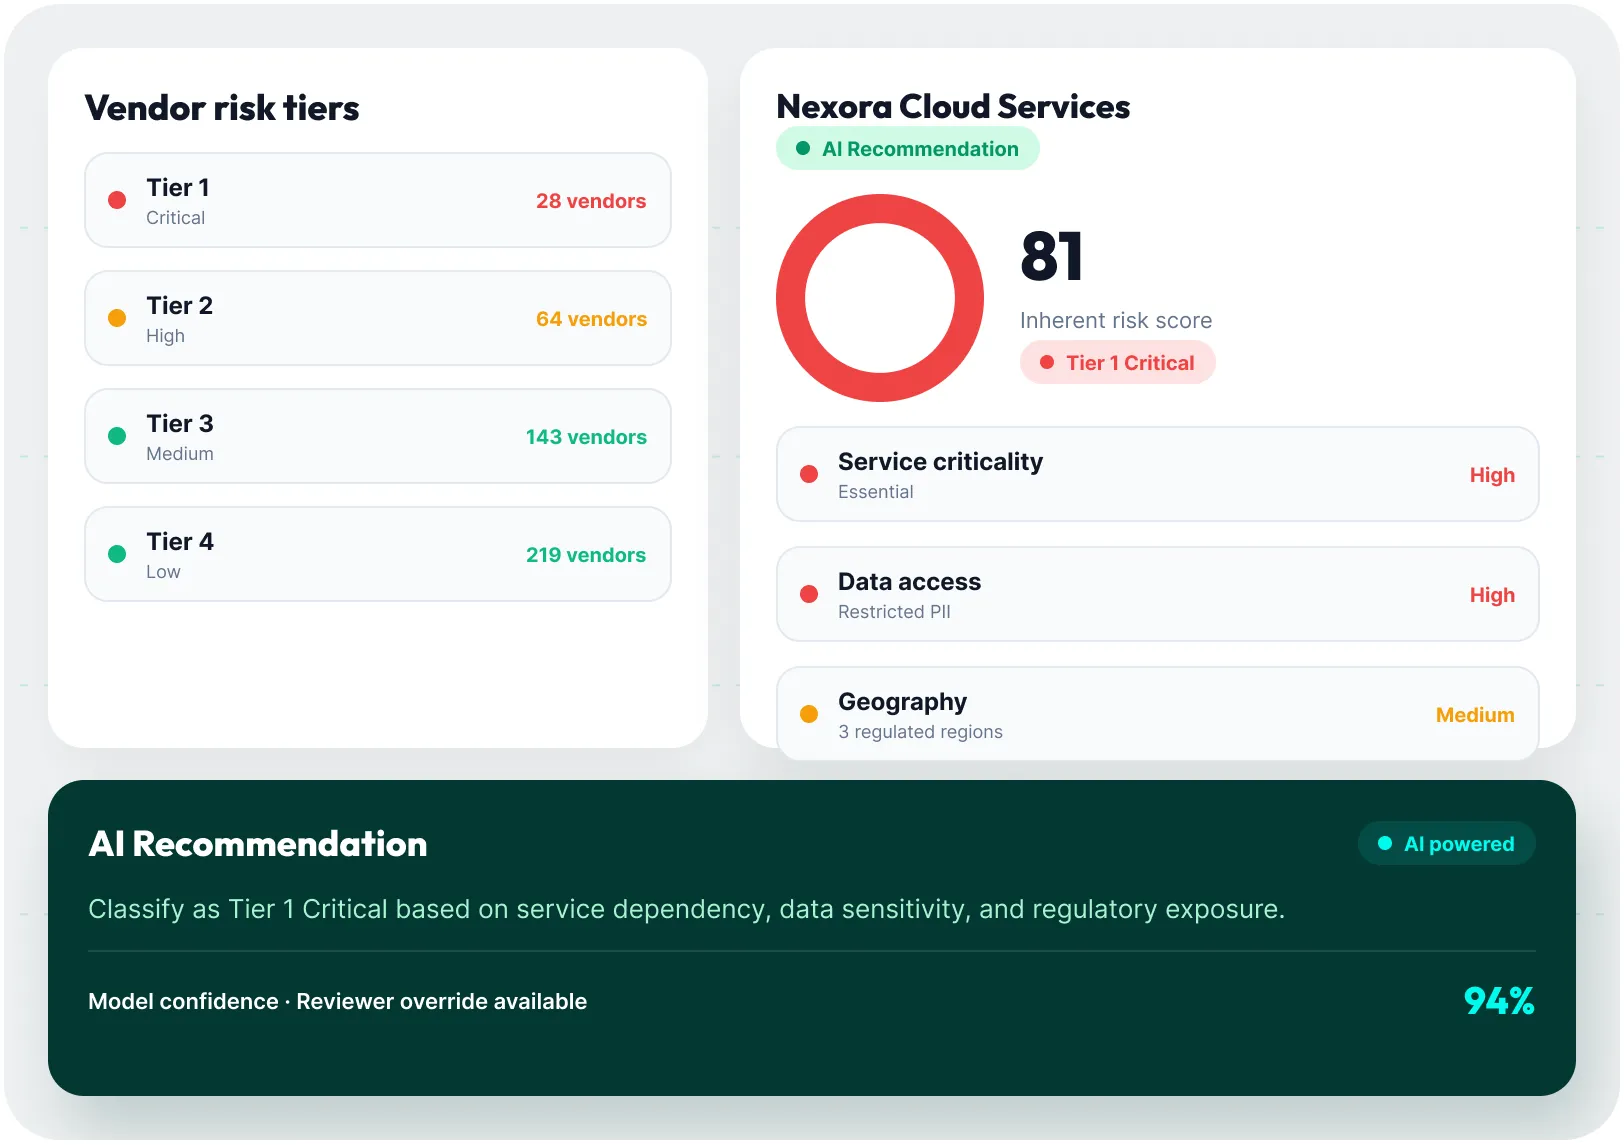
Purpose-built agents recommend tiers, scope assessments, evaluate evidence, monitor signals, and guide remediation.
Build and deploy agents tailored to your vendor risk needs with MetricStream and partners.
60%
Improvement across vendor lifecycle
40%
Reduction in risk and control assessments through rationalization and continuous monitoring
50%
Lower costs associated with managing regulatory audit findings
Source: MetricStream’s Business Value Calculator
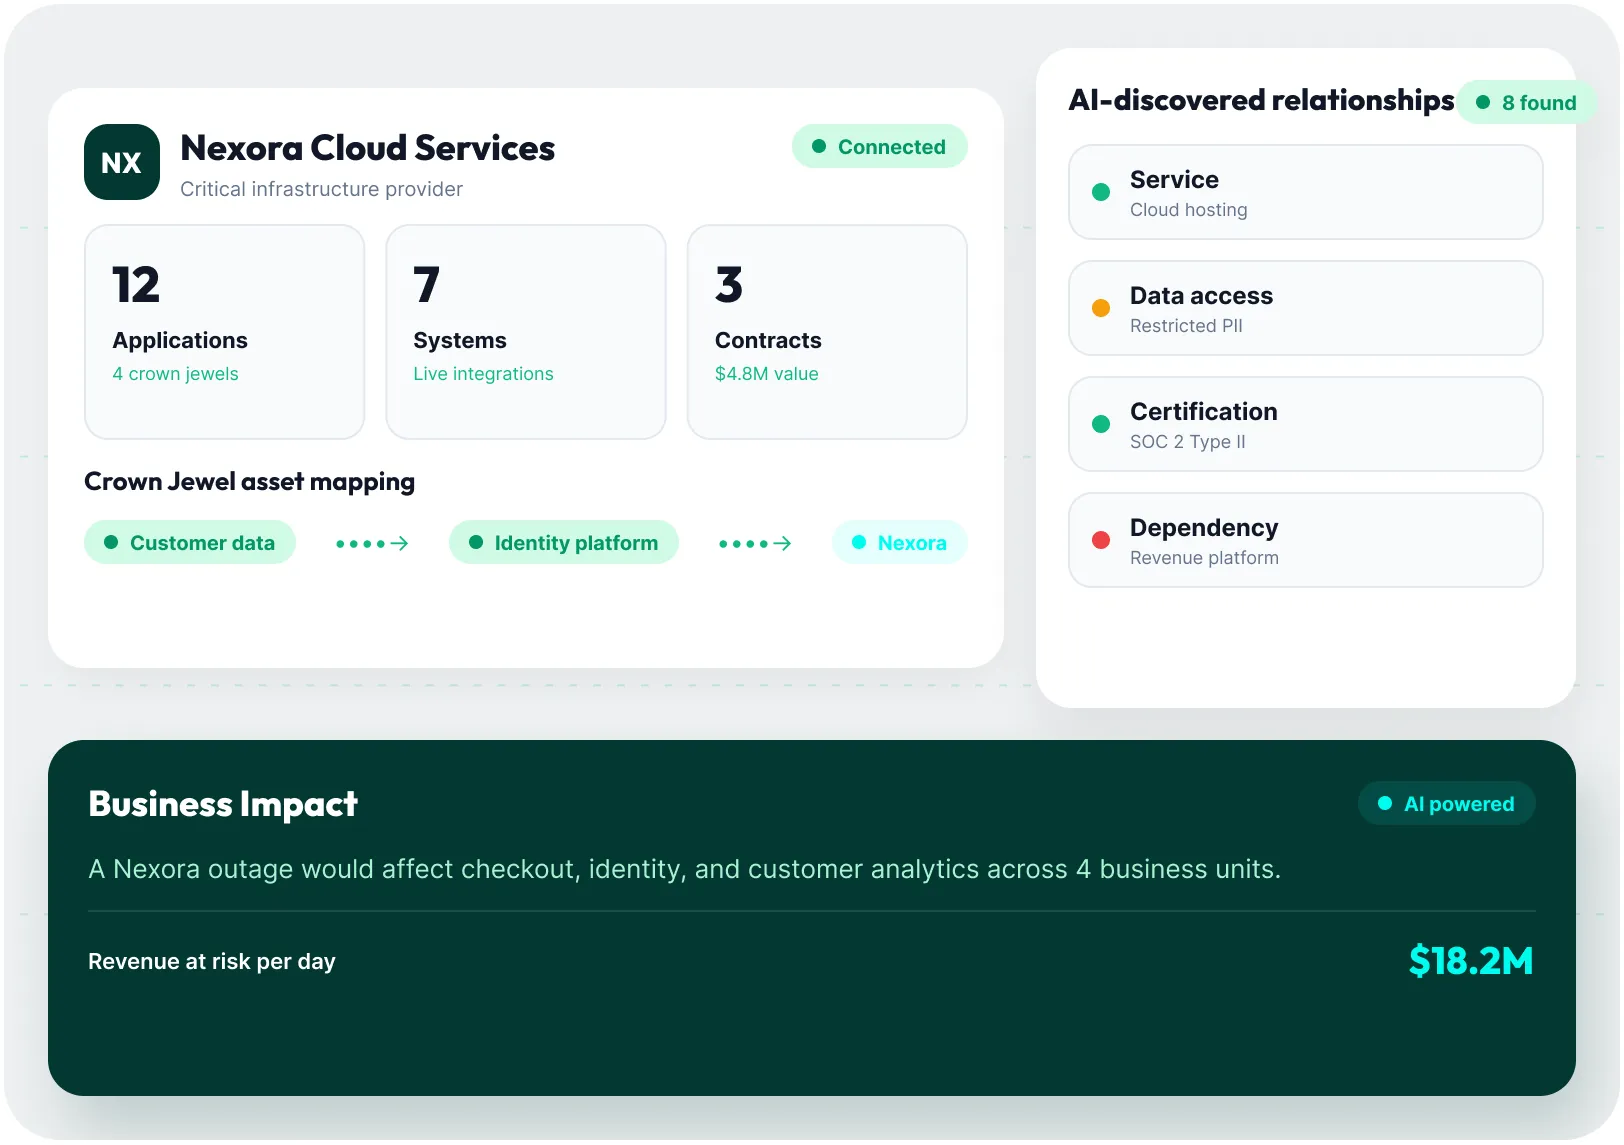
Know which vendors support the organization’s critical technology, what they can access, and where they create business dependencies. Maintain vendor services, applications, systems, data access, contracts, certifications, assessments, risks, and issues within a single connected vendor profile. Map vendors to Crown Jewel assets, critical processes, and business services. AI helps uncover missing relationships and reveal the potential business impact of vendor disruption.
Vendor Risk Capability
Traditional IT Vendor Risk
MetricStream Agentic IT Vendor Risk
Vendor inventory
Disconnected vendor and technology records
AI connects vendors with assets, services, data, and business owners
Tiering
Rules applied manually
AI recommends defensible inherent risk scores and tiers
Assessments
Long and repetitive questionnaires
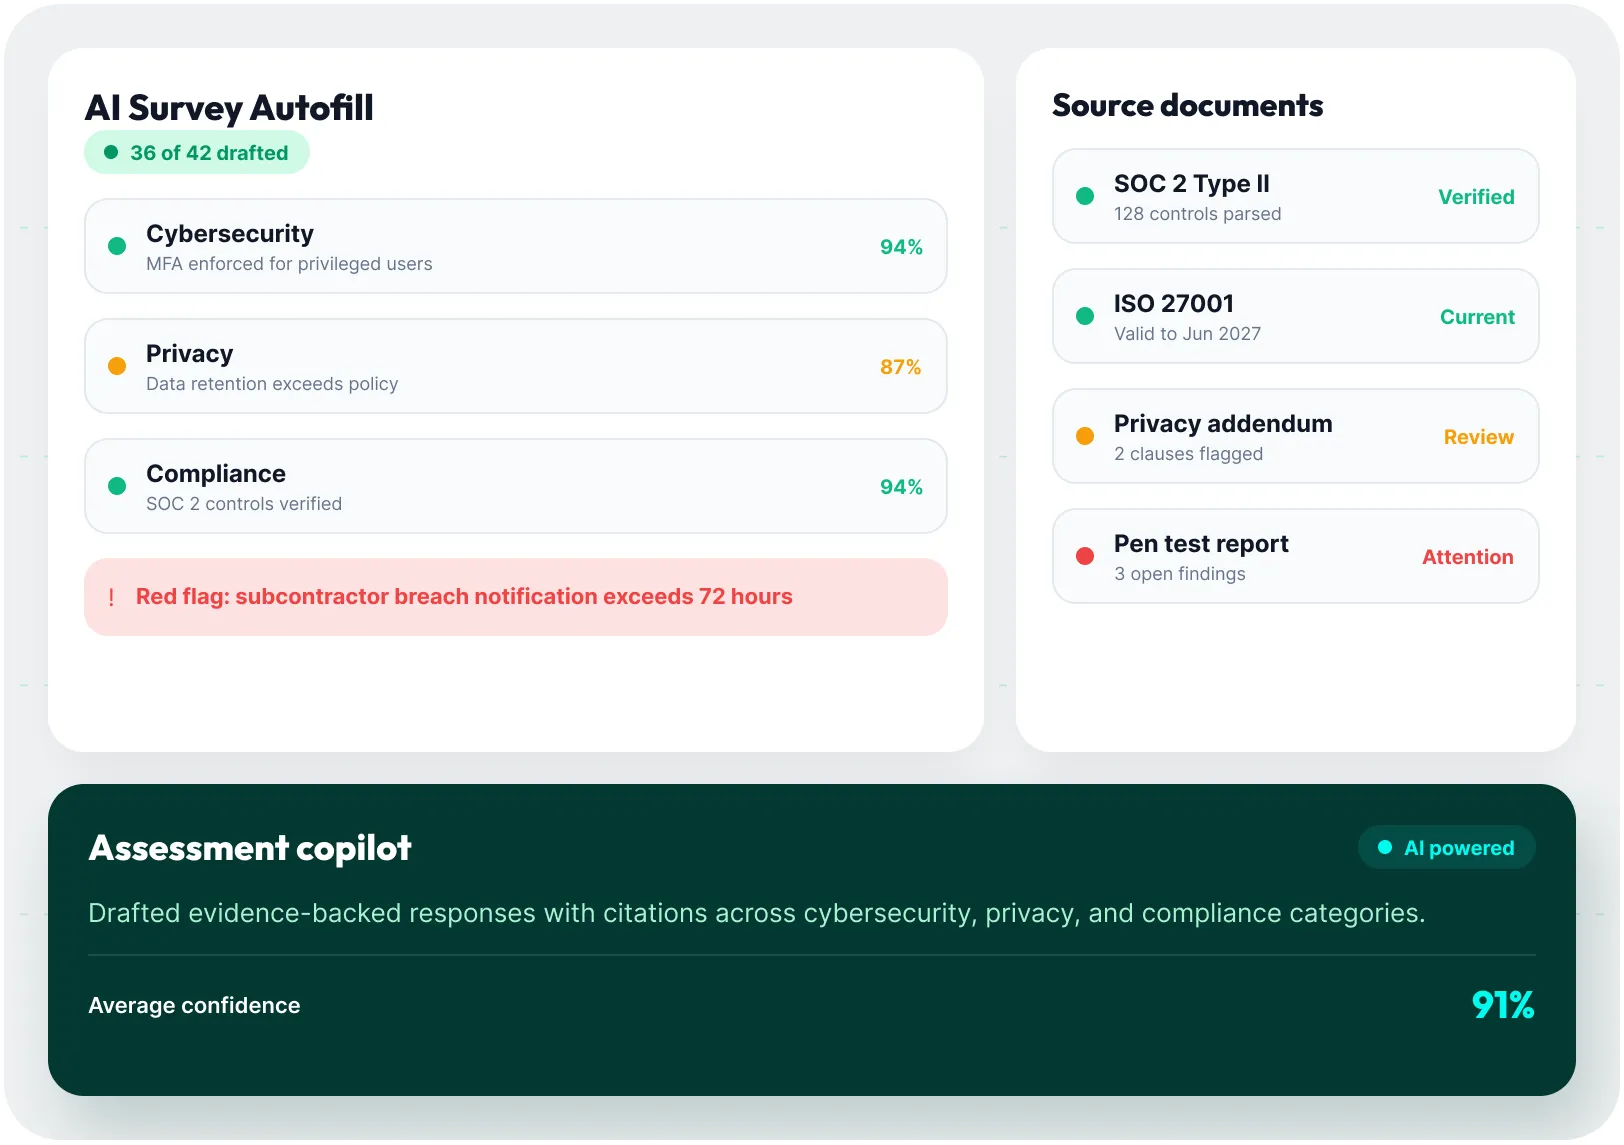
Agents tailor assessments and AI drafts source-backed responses
Evidence
Reviewed document by document
AI interprets relevant evidence and identifies gaps
Monitoring
Annual or periodic snapshots
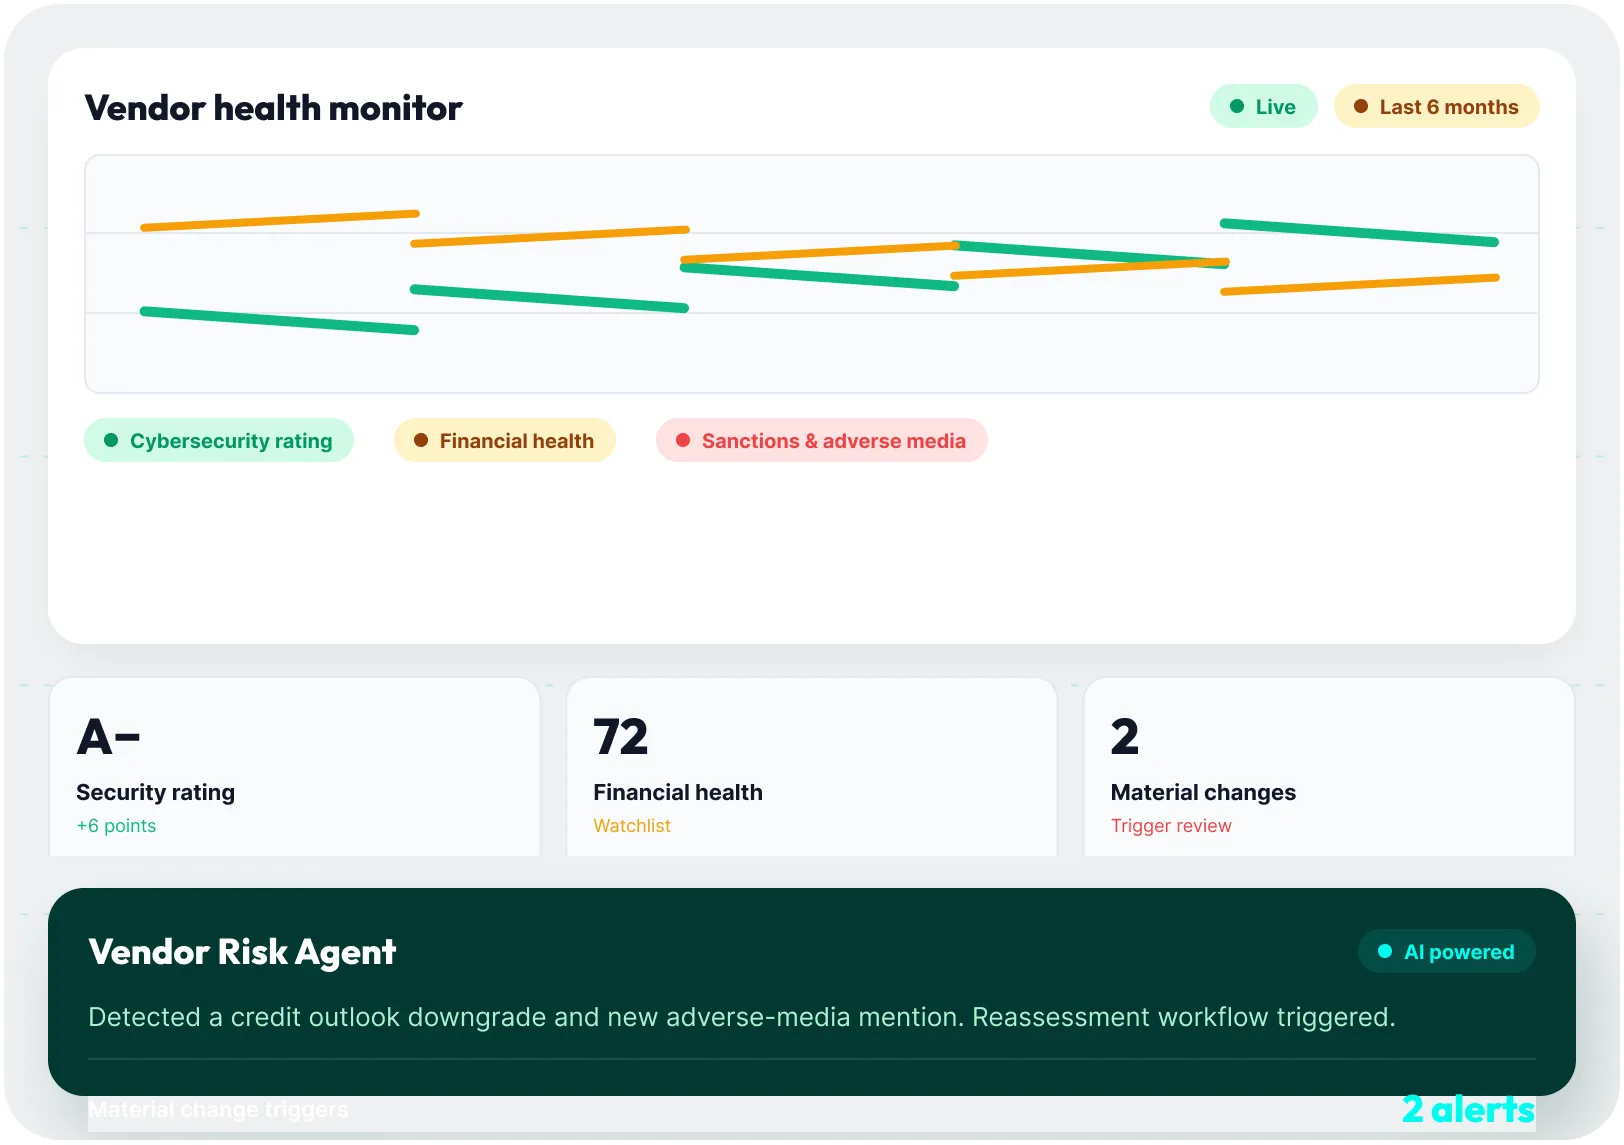
Agents monitor changing internal and external signals
Issues
Findings chased through email
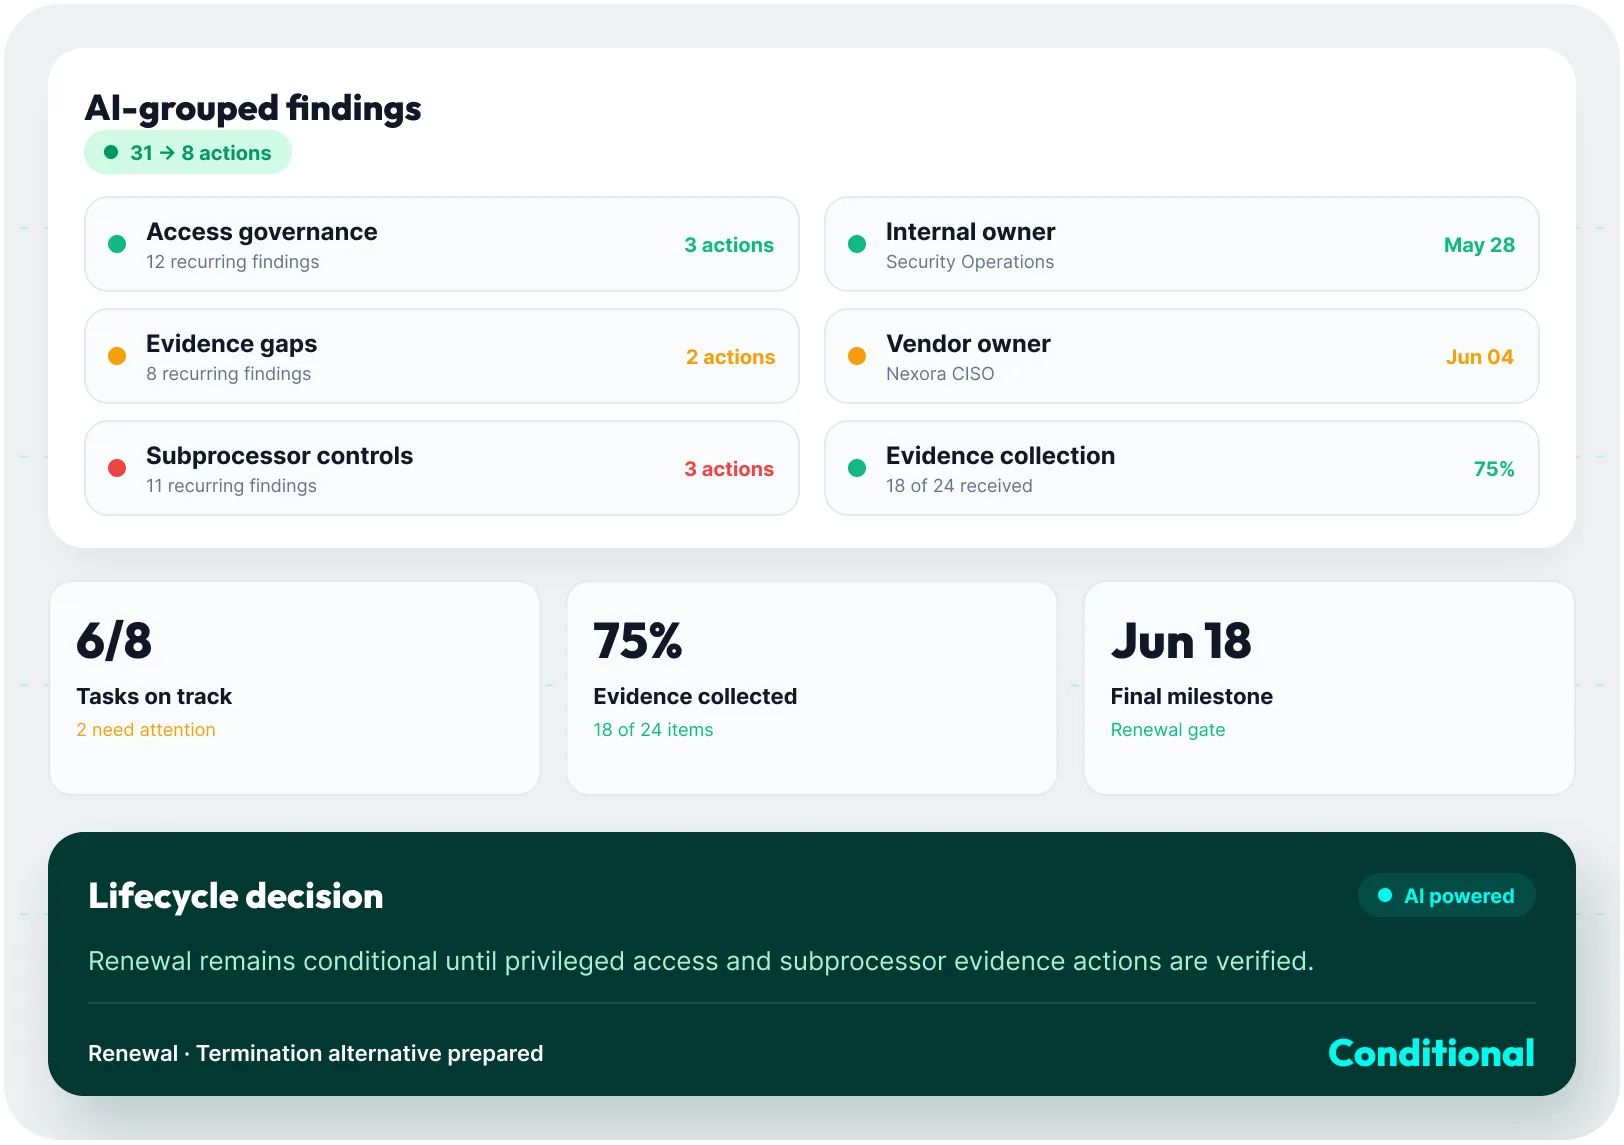
AI clusters related findings and recommends remediation
Renewal and exit
Based on outdated assessments
Current risk and performance guide renewal and offboarding
Use our interactive ROI calculator, built by Forrester, to estimate what Enterprise GRC could deliver for your organization. Enter details such as annual revenue, number of GRC tools, and compliance exposure to see your potential savings, payback period, and return on investment.
Calculate My ROI
Govern technology vendors from initial request and due diligence through monitoring, renewal, and secure offboarding.
Link IT vendors with applications, assets, systems, data, controls, processes, services, and accountable owners.
Enrich decisions with trusted cybersecurity, financial, compliance, sanctions, and reputational information.
Support decisions with citations, confidence indicators, documented rationale, review, approval, and audit history.
Adapt tiers, questionnaires, assessments, monitoring, thresholds, approvals, issues, and remediation to your program.
Vendor risk, cybersecurity, and AI specialists support implementation, adoption, integration, and optimization.

Analyst Report
Download the excerpt to see why MetricStream was recognized as a GRC Leader in 2025.
Download Now
eBook
Why compliance automation matters, how to harness it effectively and what to keep in mind when using automated and AI powered solutions
Read More
Case Study
Learn how MetricStream helped an oil and gas giant automate cyber risk and compliance management processes and improved its overall cyber maturity and resilience.
Read More
Whitepaper
Learn how GRC leaders are adopting AI responsibly and proving measurable ROI at scale.
Read MoreMetricStream IT Vendor Risk Management is an AI-native IT vendor risk management software product that provides comprehensive, real-time visibility into the IT vendor ecosystem, enabling organizations to manage vendor risks in a streamlined and consistent manner. It automates vendor information management, onboarding, continuous monitoring, risk and compliance assessments, and risk mitigation across the full vendor lifecycle—from initial registration through offboarding.
MetricStream’s Business Value Calculator models up to a 60% improvement across vendor onboarding, assessment, monitoring, performance, and offboarding workflows with AI. It also models 40% fewer risk and control assessments through rationalization and continuous monitoring, and 50% lower costs associated with managing regulatory audit findings.
MetricStream IT Vendor Risk Management automates screening and onboarding processes for different types of IT vendors, simplifying vendor intake and due diligence. Risk profiles are evaluated for each vendor before onboarding is completed, and vendor information and ratings are validated using alerts from reliable external content sources. The frequency of ongoing assessments is defined based on each vendor's risk profile, ensuring that higher-risk vendors receive more frequent scrutiny.
MetricStream IT Vendor Risk Management deepens vendor risk visibility by integrating with authoritative intelligence sources including Dow Jones, Dun & Bradstreet (D&B), BitSight, SecurityScorecard, and others. These integrations provide real-time data on vendor cybersecurity posture, financial health, anti-bribery and anti-corruption risk, and ESG ratings. This external intelligence enriches vendor profiles and reduces the manual research effort required during due diligence.
MetricStream IT Vendor Risk Management uses AI in its Issue and Action Management capability to quickly identify issues based on their relationship to other vendor findings and recommend appropriate issue classifications. The product also automatically analyzes SOC 2 reports for anomalies, reducing the manual review effort required when assessing vendor compliance documentation. Vendor offboarding workflows are also streamlined through built-in AI-assisted checklists.
MetricStream IT Vendor Risk Management evaluates and tracks key performance indicator (KPI) scores for IT vendors, enriching internal scores with data from internal systems, audit and assessment results, and content providers. Vendor scorecards allow organizations to monitor performance over time and proactively identify potential points of failure. Vendors can also access their own performance dashboards and progress reports through the platform's self-service portal.
As vendor risk monitoring software, MetricStream IT Vendor Risk Management uses feeds from industry content providers to continuously validate IT vendor information and maintain up-to-date risk and compliance profiles. Organizations can subscribe to vendor-specific alerts based on each vendor's criticality, and the platform automatically triggers risk assessments or logs issues when pre-defined risk thresholds are breached. This continuous monitoring approach replaces periodic, point-in-time reviews with an ongoing, dynamic view of vendor risk.
MetricStream IT Vendor Risk Management includes built-in workflows and checklists for vendor offboarding triggered by contract breaches or expirations, incidents of non-compliance, or vendor performance dissatisfaction. AI-assisted offboarding checklists ensure that all required steps—such as revoking system access, recovering assets, and documenting the offboarding rationale—are completed in a structured, auditable manner.
MetricStream IT Vendor Risk Management provides powerful reports, analytics, and business intelligence capabilities that help management teams make better-informed sourcing and negotiation decisions based on historical and real-time data on vendor risks, compliance status, and performance. Vendor assessment scores can be captured and compared across product or service types, giving procurement and risk teams objective evidence to support vendor selection, retention, and renegotiation decisions.
MetricStream IT Vendor Risk Management is designed for IT risk managers, third-party risk officers, procurement professionals, and CISOs at organizations with significant vendor ecosystems. It is especially valuable as vendor risk compliance software for organizations in regulated industries—such as financial services, healthcare, and technology—where regulatory requirements mandate formal oversight of IT vendors, particularly those with access to sensitive data or critical infrastructure. Individual vendors can also access the platform through a self-service portal to update their profiles and respond to assessments.