Digital Operational Resilience Act (DORA) Solution
Achieve DORA Compliance With Agentic Cyber Governance, Risk, and Compliance
Run Digital Operational Resilience Act (DORA) compliance across ICT risk, incidents, resilience testing, third parties, and recovery, with AI assistants and agents that turn requirements into action.
Assistants
Get guidance across DORA obligations, ICT risks, incidents, resilience tests, providers, evidence, and critical services.
Purpose-built Agents
Agents coordinate regulatory analysis, risk assessments, control testing, provider oversight, incident response, and recovery
Agent Ecosystem
Build and deploy agents tailored to your business with MetricStream and partners
Measurable Impact of DORA Compliance
60
improvement across key Cyber GRC workflows with AI
40
reduction in risk assessments and control tests
60
faster third-party due diligence and risk assessment cycles
Source: MetricStream’s Business Value Calculator
Amplifying Outcomes for the Modern Enterprise
Turn DORA Requirements Into Resilient Business Outcomes
Simplify DORA Compliance With One Intelligent, Connected Program
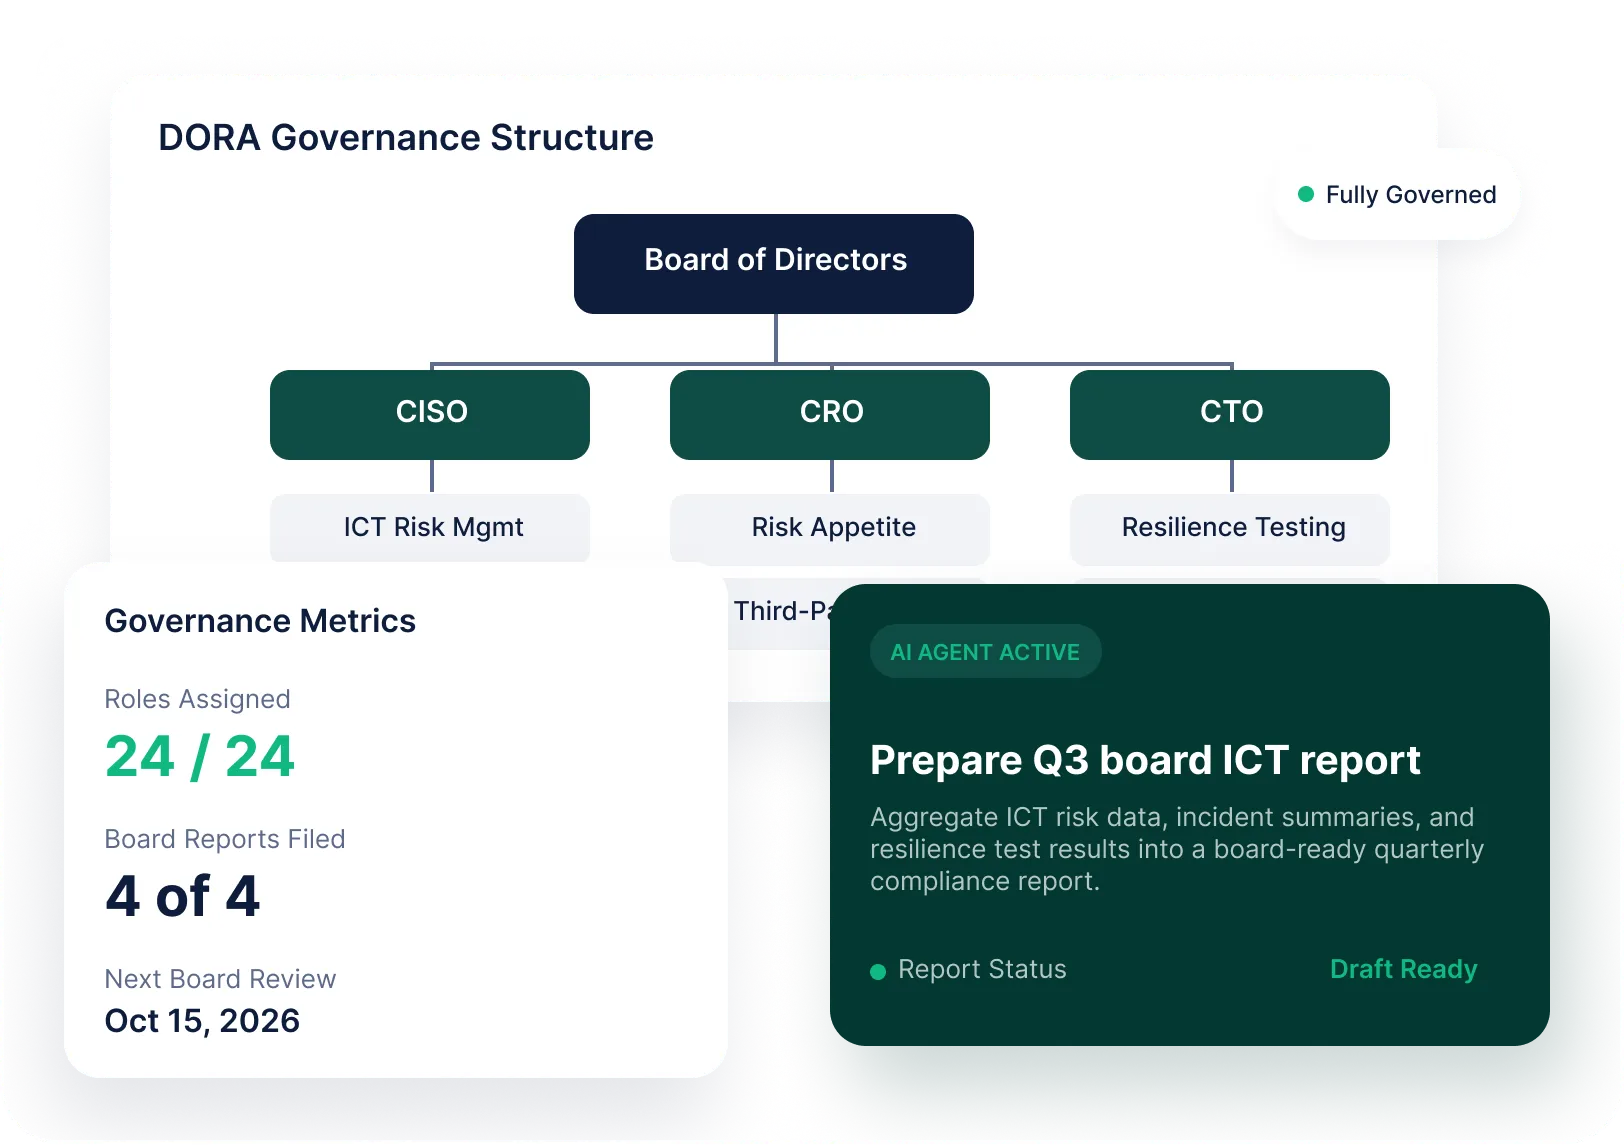
Stop managing DORA obligations, controls, policies, evidence, and owners across separate tools. Connect applicable requirements to legal entities, critical or important functions, ICT assets, providers, risks, and controls in a single program. AI extracts obligations, assesses applicability, and identifies missing relationships, helping teams understand what applies, who is accountable, and where action is required.
Assess ICT Risk with Agentic Intelligence to Build Resilient Business Services
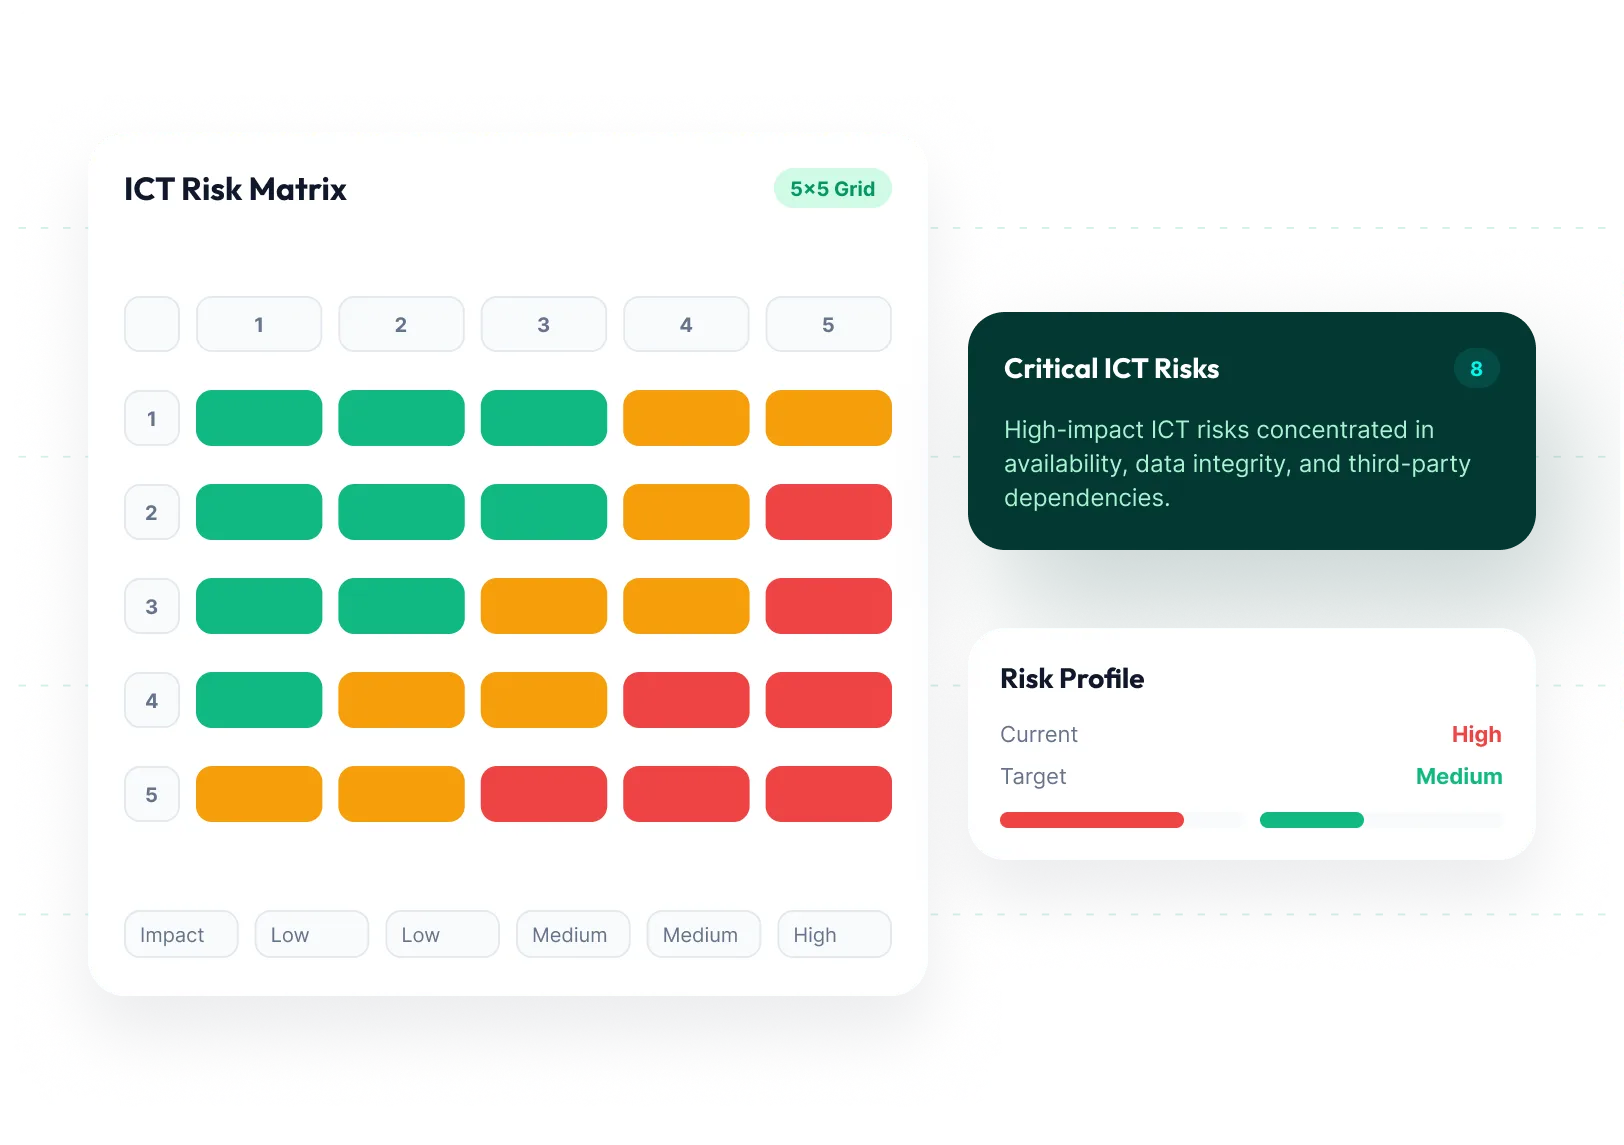
Understand how ICT risks could disrupt the functions your organization must protect. Connect assets, Crown Jewels, processes, providers, threats, vulnerabilities, controls, and service dependencies in a single view. Risk Assessment Agents bring prior results, KRIs, control performance, and unresolved issues into each assessment, helping teams evaluate exposure and prioritize treatment with greater speed and context.
Stay Resilient Through Major ICT Incidents With AI-Powered Classification
Connect ICT incident response with DORA requirements from initial detection through closure. Link incidents to affected functions, assets, entities, customers, controls, and third-party providers. AI supports classification, impact analysis, and recommended actions, while governed workflows coordinate escalation, investigation, evidence, approvals, remediation, and the preparation of regulatory reporting outputs within required timelines.
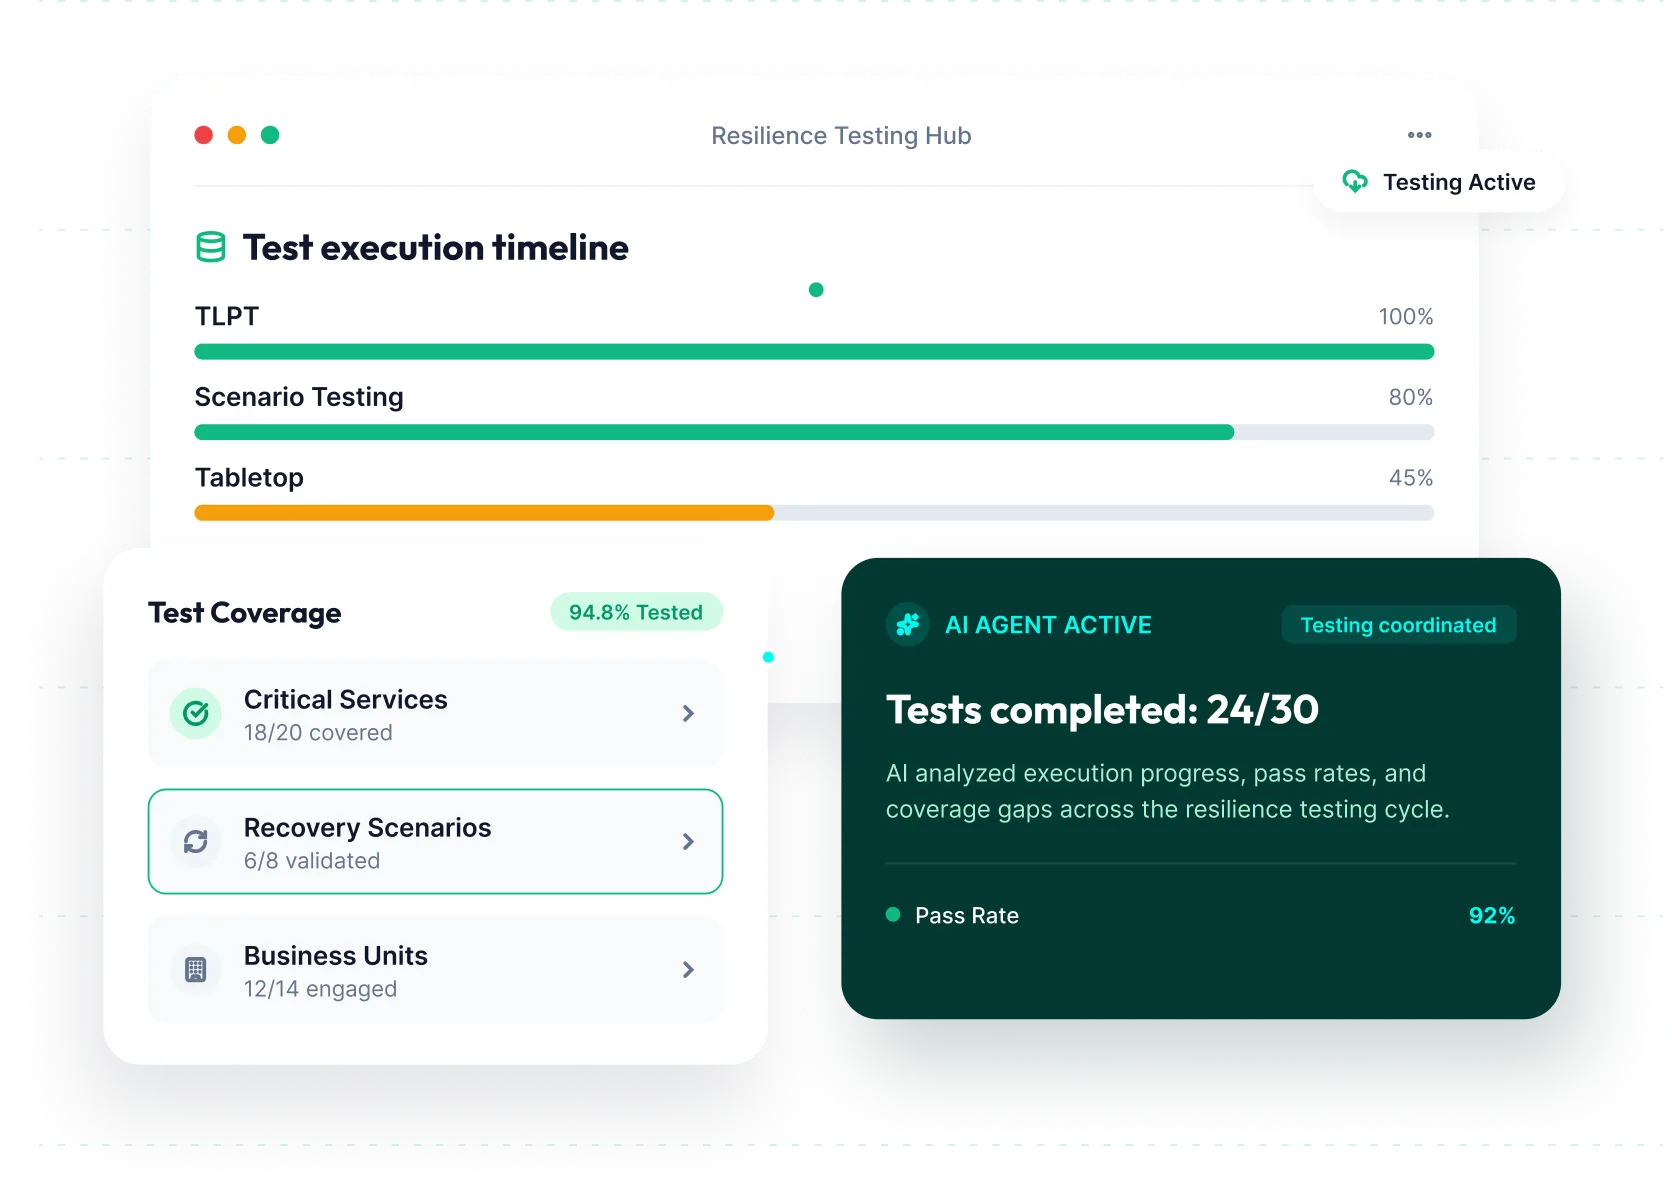
Close the Loop Faster on Digital Operational Resilience Testing From Scope to Closure
Coordinate scenario exercises, control tests, vulnerability assessments, recovery tests, and threat-led penetration testing across ICT assets, important functions, and providers. Manage scope, responsibilities, schedules, evidence, findings, remediation, and retesting in one single workflow. Agents identify recurring weaknesses and recommend coordinated actions, helping you turn testing results into stronger digital operational resilience.
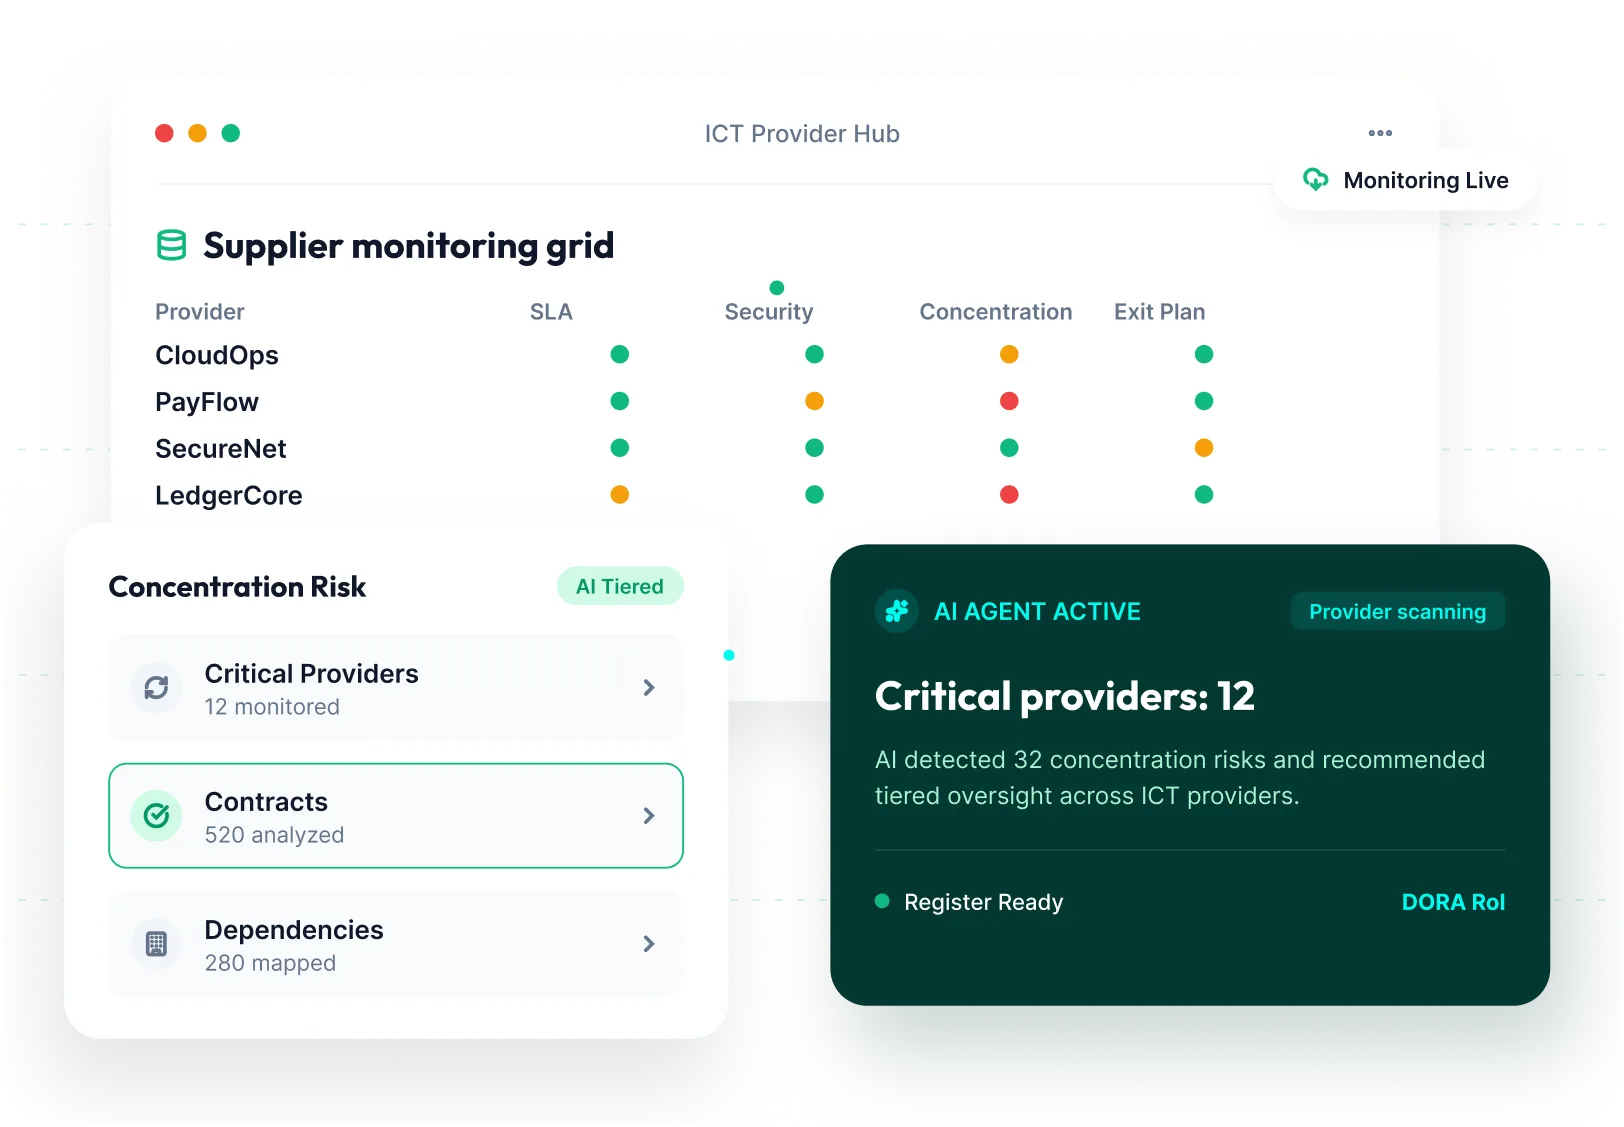
Catch Concentration Risk by Overseeing ICT Third-Party Risk Continuously
Replace fragmented provider records and annual reviews with the most current view of ICT third-party risk. Bring together services, contracts, criticality, assessments, dependencies, risk ratings, issues, concentration exposure, and exit strategies. Third-Party Risk Agents recommend tiers, tailor due diligence, interpret evidence, and monitor changing signals, while centralized data supports your DORA Register of Information requirements.
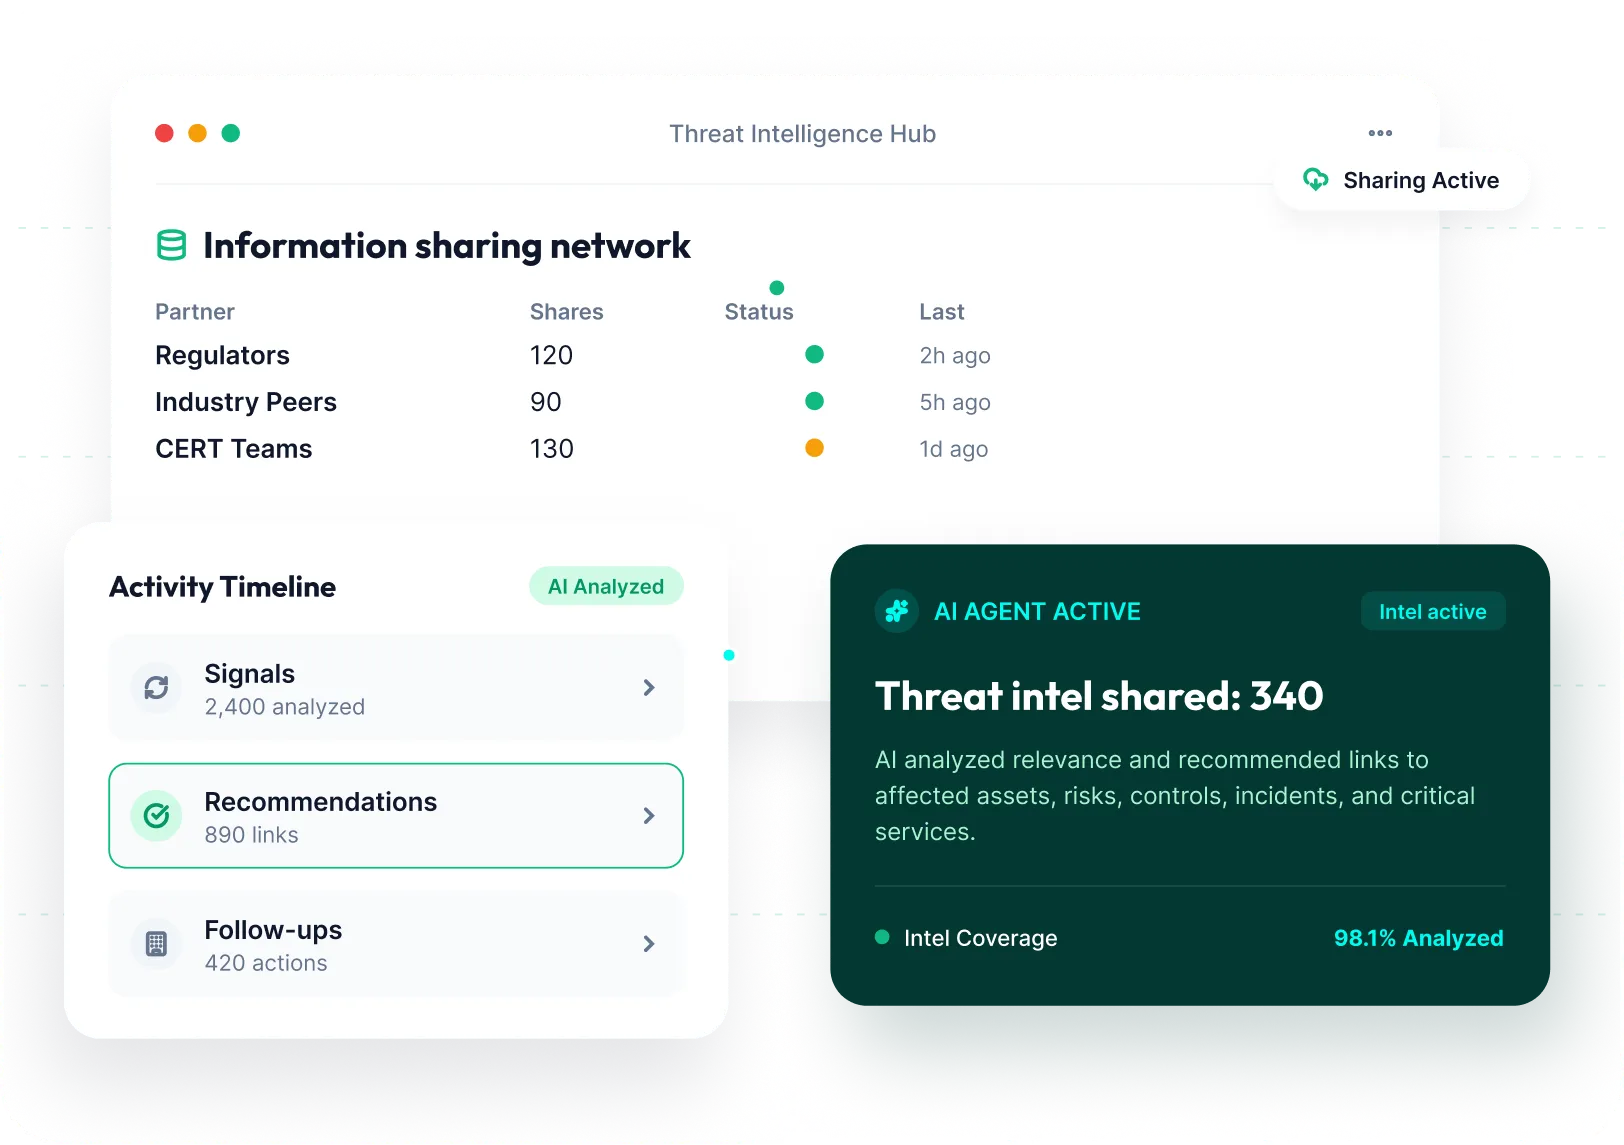
Connect Threat Intelligence to Risks, Services, and Decisions for Faster Action
Move threat intelligence beyond technical teams and into your broader DORA program. Bring together relevant signals from security tools, internal teams, trusted content providers, and information-sharing systems. AI analyzes relevance and recommends links to affected assets, risks, controls, incidents, providers, and critical services. Assign follow-up actions and preserve a traceable record of what was reviewed, shared, escalated, and addressed.
Accelerate Critical Business Service Recovery With AI-Powered Resilience
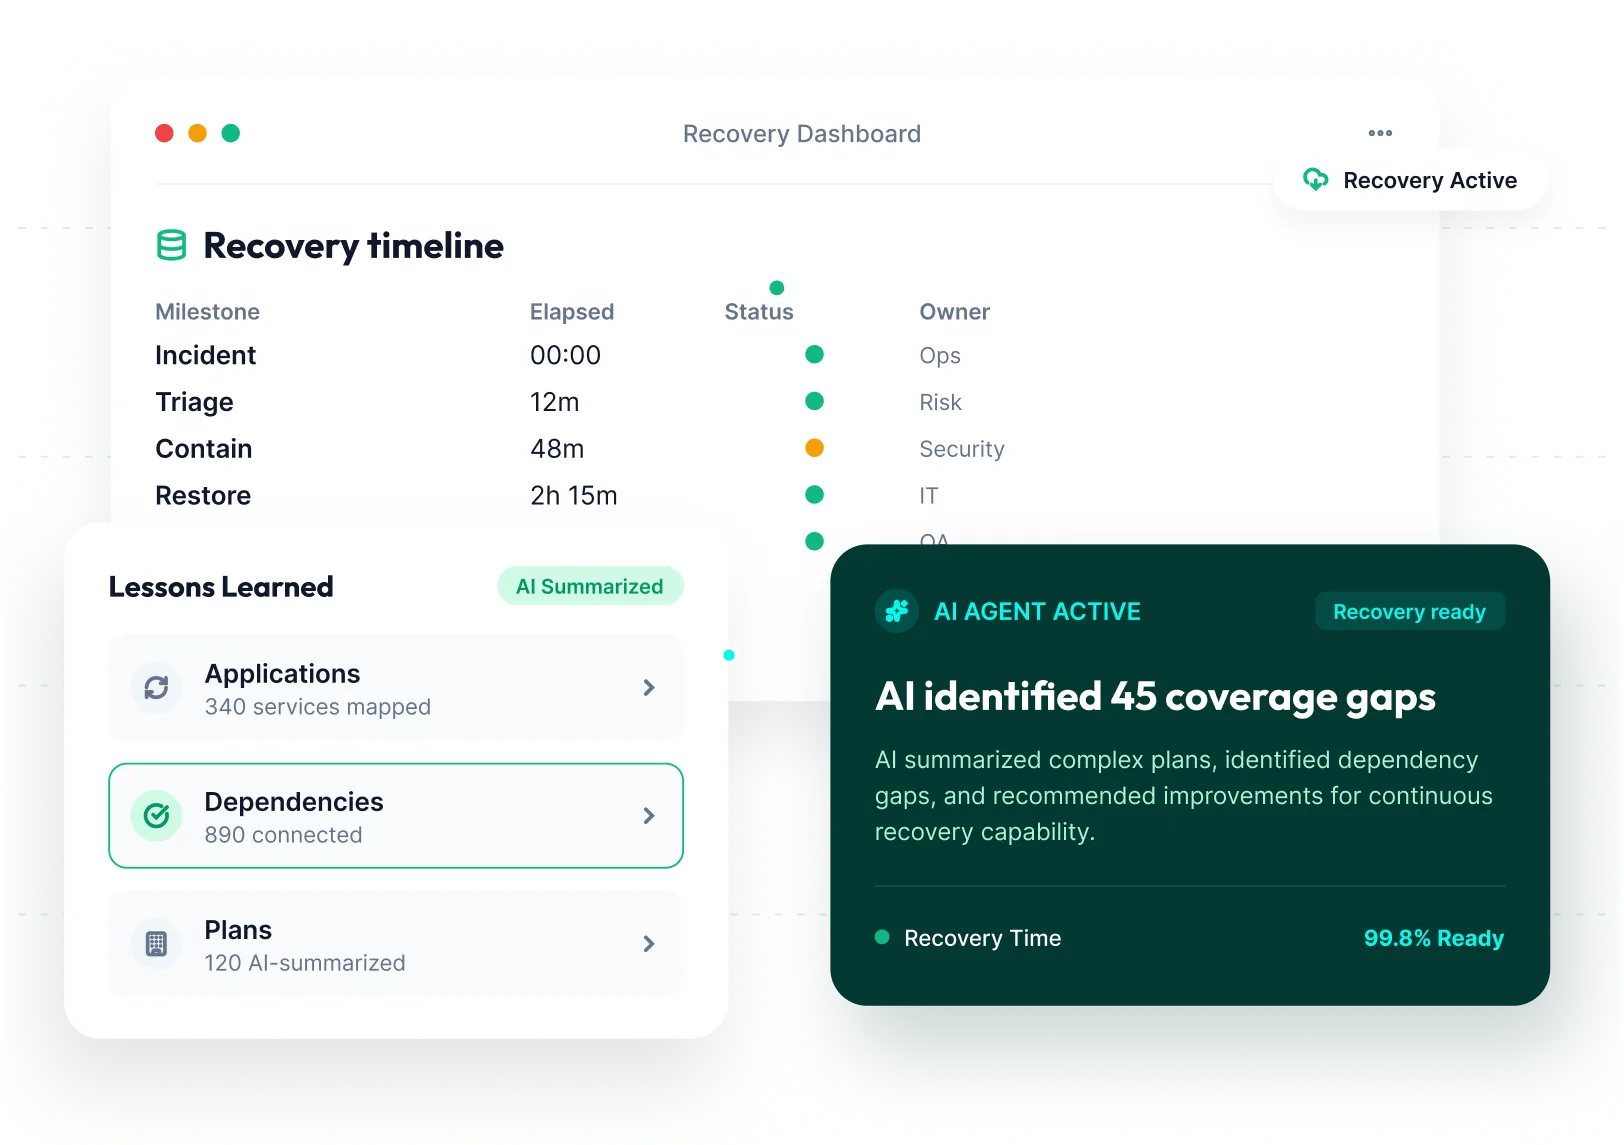
Prepare your organization to maintain or restore critical services when ICT disruptions occur. Map applications, infrastructure, data, processes, people, facilities, and third parties to business recovery objectives and continuity plans. AI summarizes complex plans, identifies dependency and preparedness gaps, and recommends improvements, helping apply lessons from incidents, assessments, tests, and exercises, so business recovery capabilities improve continuously.
Traditional DORA Compliance vs. MetricStream’s AI-Powered Solution
Embraced by the Business. Trusted by the Board. Aligned with Auditor and Regulator Expectations.
-
Deep-Domain Products
Purpose-built capabilities across every major Cyber GRC function.
-
AI-Native Platform
Federated data, assistants, agents, APIs, security, and model governance.
-
Enterprise-Grade Trust
Citations, traceability, permissions, guardrails, and human accountability.
-
Built to Adapt
Configure workflows, methodologies, taxonomies, reports, and integrations.
-
Proven Global Scale
More than one million users across over 35 countries.
-
Dedicated Experts
Cyber GRC and AI specialists support transformation, adoption, and outcomes.
See What MetricStream GRC Could Be Worth to Your Organization
Use our interactive ROI calculator, built by Forrester, to estimate what Enterprise GRC could deliver for your organization. Enter details such as annual revenue, number of GRC tools, and compliance exposure to see your potential savings, payback period, and return on investment.
Calculate My ROIInsights on AI and GRC
eBook
Demystifying RCSA: 6 Critical Factors to Build an Intelligent Risk and Control Self-Assessment Framework
Download this eBook to explore the critical factors that chief risk officers (CROs) must adopt to modernize their Risk and Control Self-Assessment (RCSA) program.
Read More
Case Study
Oil and Gas Giant Strengthens Stakeholder Trust with a Holistic Approach to Assurance
Read this case study to explore how an oil and gas giant realized its vision of integrated GRC by implementing MetricStream products for risk, audit, SOX, compliance, and policy management processes.
Read More
Whitepaper
Unlocking AI Value in GRC
Learn how GRC leaders are adopting AI responsibly and proving measurable ROI at scale.
Read MoreDigital Operational Resilience Act (DORA) Solution FAQs
DORA compliance means meeting the requirements of the EU's Digital Operational Resilience Act (Regulation (EU) 2022/2554), which has been in force since January 17, 2025. The regulation sets common rules for how financial entities manage ICT (information and communication technology) risk. Organizations must manage ICT risk, report major incidents, test their digital operational resilience, oversee ICT third-party providers, and may share cyber threat intelligence. Compliance means showing regulators that these practices are in place and working.
DORA applies to financial entities operating in the EU and to the ICT (information and communication technology) third-party providers that serve them. Covered financial entities include banks, insurers, investment firms, payment institutions, and crypto-asset service providers. ICT providers such as cloud and software vendors come into scope through their contracts with these firms. The European Supervisory Authorities directly oversee providers they designate as critical, including those based outside the EU.
DORA compliance rests on five pillars: ICT risk management, ICT-related incident management and reporting, digital operational resilience testing, ICT third-party risk management, and information sharing. The first pillar requires a documented framework to identify, protect, detect, and recover from ICT risks. The incident pillar requires organizations to classify incidents and report major ones to regulators. The testing pillar requires regular resilience testing, including threat-led penetration testing for certain entities. The third-party pillar covers contracts, due diligence, and a register of information on ICT providers. The information-sharing pillar encourages firms to exchange cyber threat intelligence within trusted communities. MetricStream's DORA solution uses AI assistants and agents to support each area, including ICT risk assessment, incident classification, testing coordination, third-party oversight, and threat intelligence.
DORA non-compliance can lead to supervisory orders and financial penalties, and the regime differs for financial entities and critical ICT third-party providers. For financial entities, national competent authorities can require corrective measures and impose administrative penalties, with amounts set by each EU member state. For critical ICT third-party providers, the European Supervisory Authorities can impose periodic penalty payments of up to 1% of average daily worldwide turnover from the preceding business year. These payments can apply for each day of continued non-compliance, for up to six months.
MetricStream's Digital Operational Resilience Solution enables financial sector organizations to proactively identify, withstand, respond to, and recover from Information Communication Technology (ICT)-related disruptions. It is purpose-built to help organizations comply with the EU's Digital Operational Resilience Act (DORA), effective January 2025, and similar regulatory frameworks globally. The solution improves visibility into ICT risks, digital business operations, cyber risk, threats and vulnerabilities, and critical third-party risks on one integrated platform.
DORA—the EU Digital Operational Resilience Act—is a regulation effective January 2025 that sets a unified framework for financial entities across all EU member states to ensure they can withstand, respond to, and recover from ICT-related disruptions. It mandates robust ICT risk management, incident reporting, resilience testing, and third-party oversight. MetricStream's Digital Operational Resilience Solution helps financial institutions comply by providing integrated capabilities for ICT risk management, compliance, IT vendor oversight, incident management, and business continuity planning.
According to customer responses and the GRC Journey Business Value Calculator, MetricStream's DORA solution has delivered an 80% reduction in third-party onboarding time, a 67% improvement in risk reporting visibility and efficiency for executive management and the board, and a 50% reduction in the time and costs required to complete third-party risk assessments and identify risks.
MetricStream's Digital Operational Resilience Solution establishes and maintains effective IT controls mapped to processes, products, risks, regulations, and audits. It harmonizes and standardizes control sets across multiple IT regulations and standards—including ISO 27001, NIST SP 800-53, and SOC 2—to eliminate duplication. Multi-dimensional risk assessments conducted in both top-down and bottom-up approaches support reporting to executives and alignment to business strategy. Cyber risk exposure can be assessed in dollar values using built-in Cyber Risk Quantification capabilities.
MetricStream's Digital Operational Resilience Solution provides integrated management of third-party risks related to digitization across the full vendor lifecycle—from information gathering and due diligence through onboarding, continuous monitoring, and risk and compliance assessments. Automated third-party registration and onboarding workflows reduce manual effort. Pre-defined questionnaires simplify risk assessments, and risk scores are automatically calculated based on third-party responses. Powerful analytics provide a holistic view of third-party risk, compliance, and performance.
MetricStream's Digital Operational Resilience Solution uses AI capabilities to quickly identify and classify issues related to ICT risk assessments, IT controls, and compliance. It maintains a single source of truth for all incidents across the organization, with the ability to directly report incidents in the system or capture them from multiple sources. Incidents can be related to other incidents, policies, regulations, processes, and controls, and classified based on severity levels—supporting the structured incident reporting required under DORA.
MetricStream's Digital Operational Resilience Solution supports DORA's resilience testing requirements through scenario analysis and testing capabilities. Organizations can identify plausible ICT disruption scenarios, simulate them, and capture learnings for further analysis. Business continuity plans are maintained and linked to critical IT assets, business processes, locations, and key contacts. Plan exercises test whether activities outlined in continuity plans are effective, and learnings are used to refine response strategies.
While MetricStream's Digital Operational Resilience Solution is purpose-built for DORA compliance, its capabilities also support compliance with the UK's Critical Third Parties (CTP) framework and US operational resilience guidance from the Federal Reserve, OCC, and FDIC. The platform's integrated approach to ICT risk management, third-party oversight, and business continuity planning provides a foundation that supports multiple regulatory frameworks simultaneously, reducing the duplication that would result from managing each framework in a separate system.
MetricStream's Digital Operational Resilience Solution provides an 80% improvement in risk reporting visibility and efficiency for executive management and boards, according to customer data. Role-based executive dashboards deliver real-time insights into ICT risks, asset risk posture, control test results, and third-party risk status. These views allow board members and senior executives to fulfill their governance and oversight responsibilities with accurate, timely, and actionable digital risk intelligence.
MetricStream's Digital Operational Resilience Solution is designed for Chief Risk Officers, IT risk managers, operational resilience leads, and compliance officers at financial institutions subject to DORA and similar operational resilience regulations. Banks, insurance companies, investment firms, payment processors, and their critical ICT service providers are among the primary target users. The solution is particularly valuable for organizations managing complex third-party ICT ecosystems where disruption at one provider could cascade into broader operational failures.