IT & Cyber Compliance Assistant
Get instant, role-based answers about requirements, controls, tests, evidence, issues, and compliance status.
AI assistants and agents deliver control intelligence and agentic testing that keep your IT compliance program audit-ready, reducing framework-by-framework assessments and repeated evidence requests.
Get instant, role-based answers about requirements, controls, tests, evidence, issues, and compliance status.
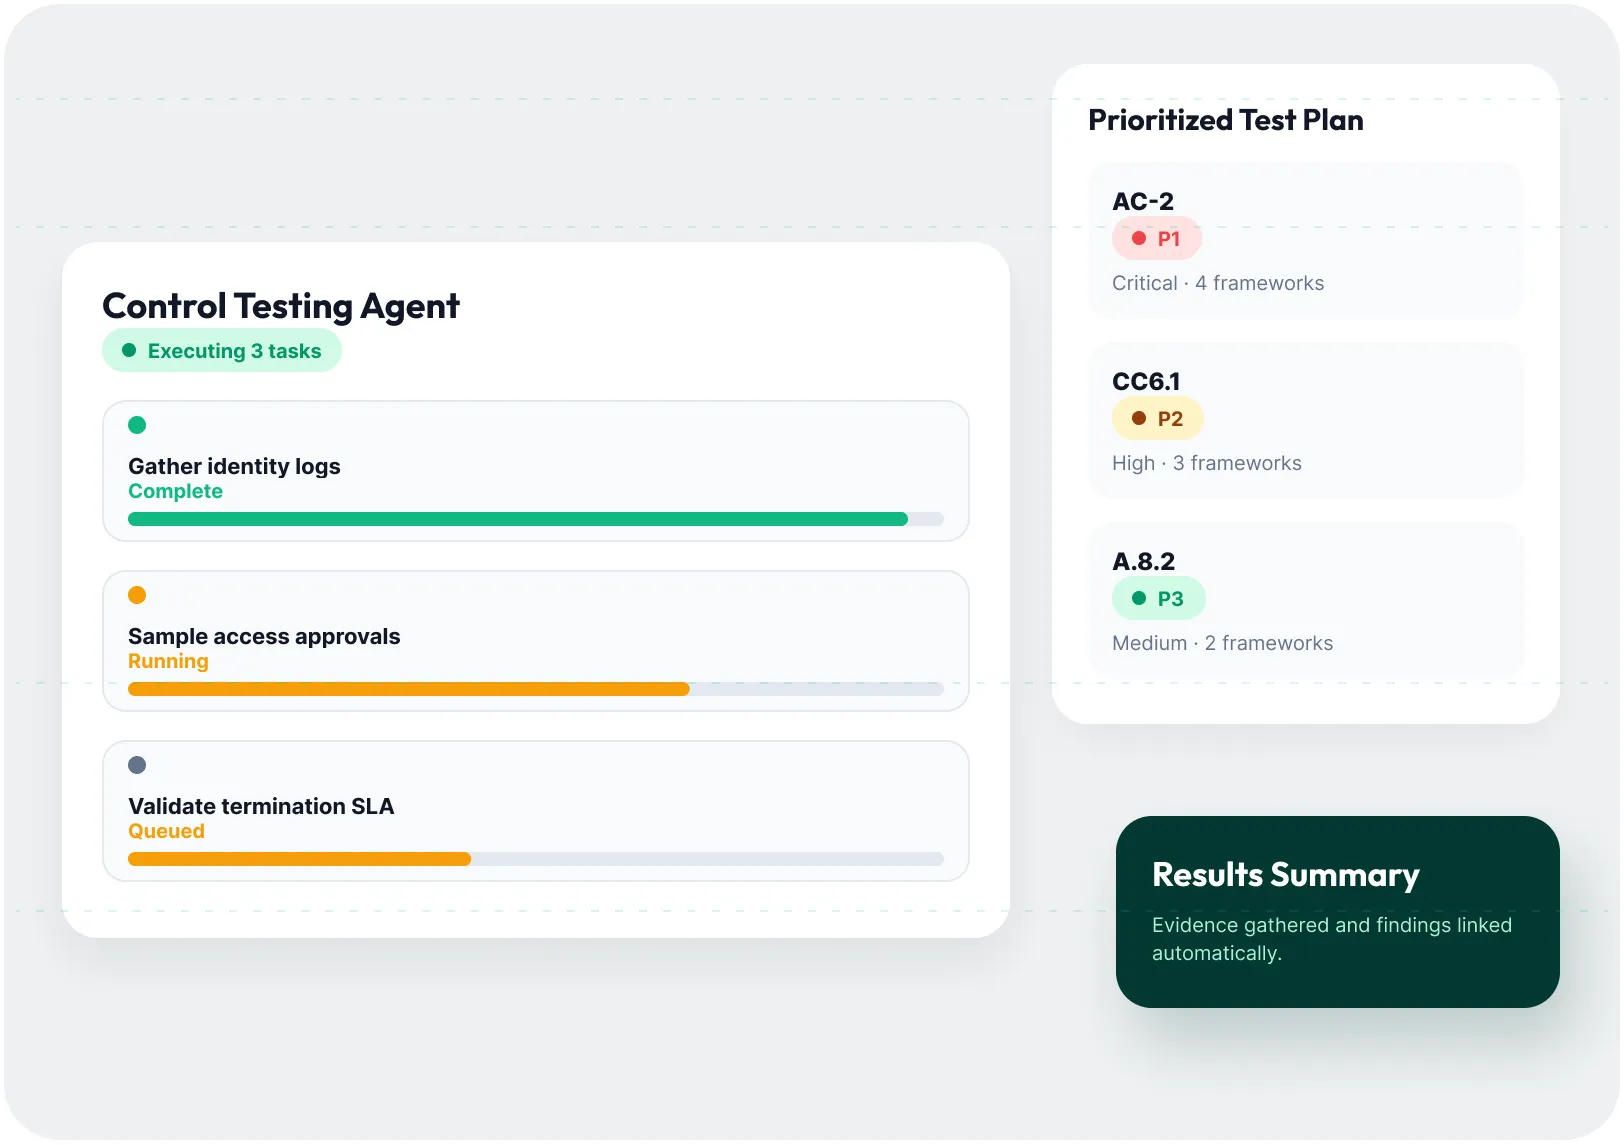
Agents execute defined tests, gather evidence, summarize results, and identify control and compliance gaps.
Build and deploy agents tailored to your cyber compliance needs with by MetricStream and partners.
60%
Improvement in multi-framework IT and cyber compliance rationalization
60%
Faster control-testing and evidence-management cycle time
40%
Fewer risk assessments and control tests through rationalization
Source: MetricStream’s Business Value Calculator
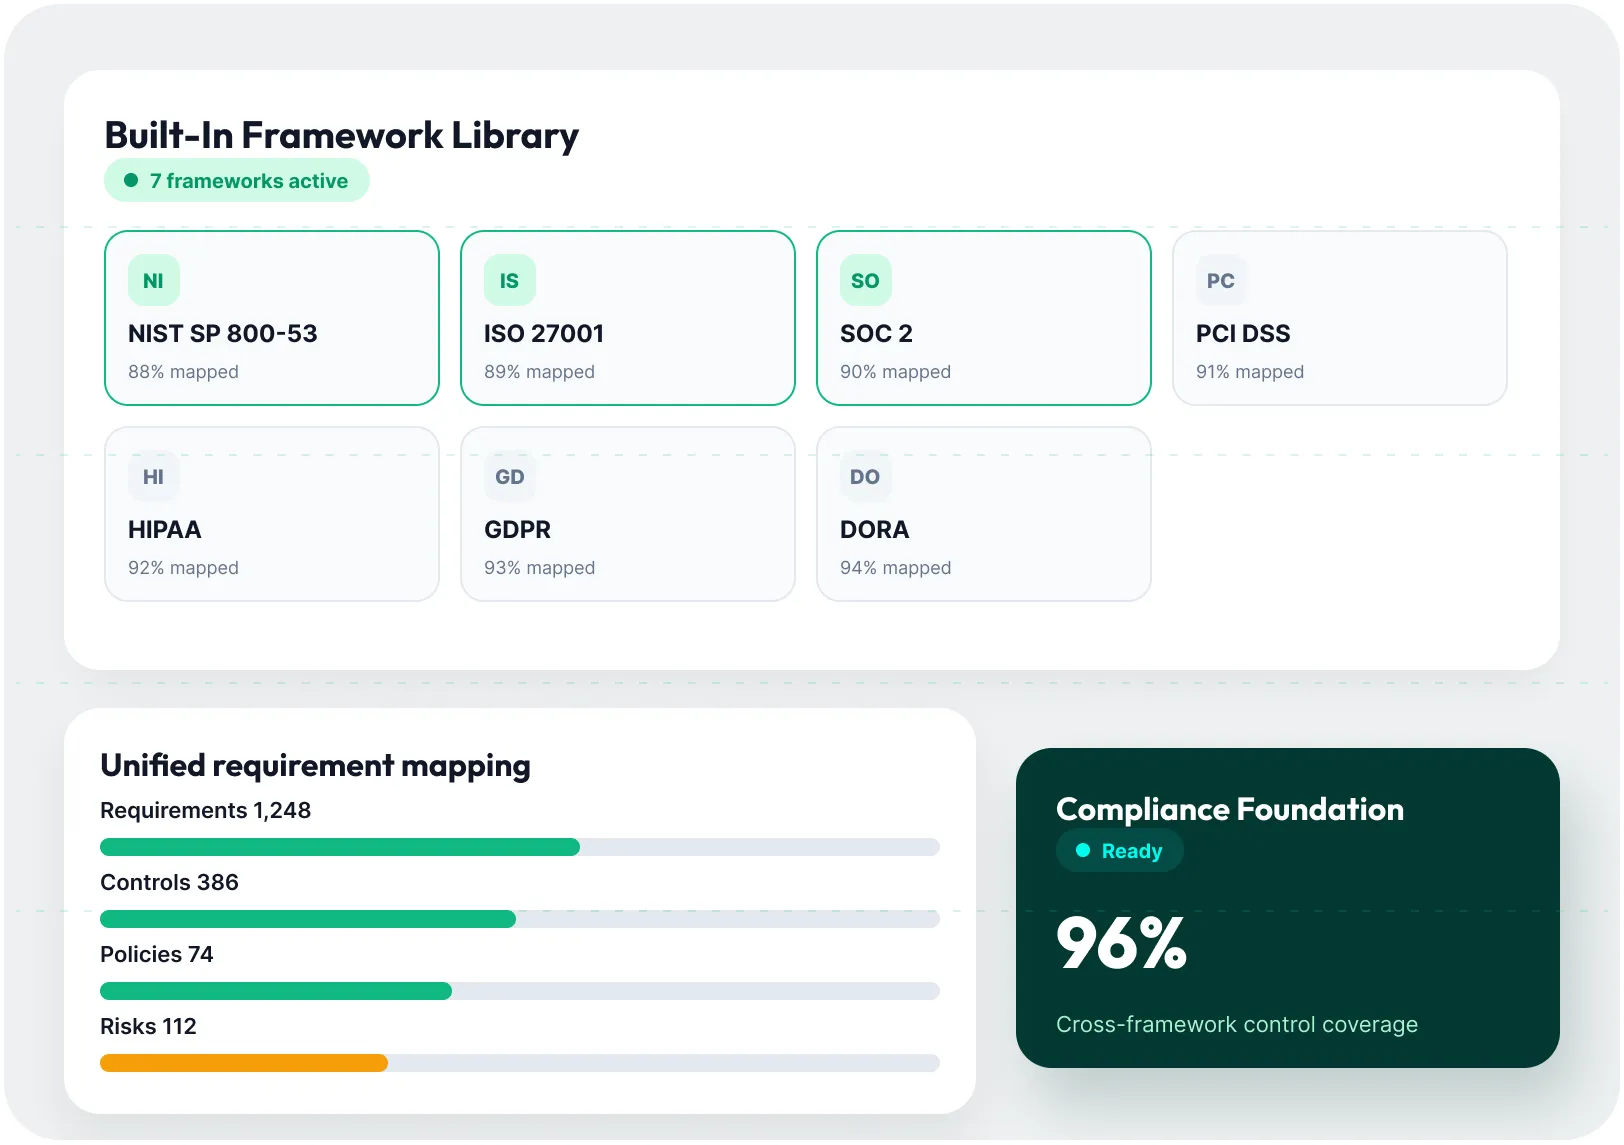
Stop rebuilding your IT & Cyber compliance program every time a new standard enters scope. Get started with built-in content for NIST SP 800-53, NIST CSF, ISO 27001/27002, SOC 2, PCI DSS, HIPAA, GDPR, DORA, and TISAX/VDA ISA. Connect requirements to controls, policies, risks, assets, evidence, and owners to create one trusted compliance foundation across the enterprise.
IT & Cyber Compliance Capability
Traditional IT & Cyber Compliance
MetricStream Agentic IT & Cyber Compliance
Frameworks
Standards managed and mapped separately
Pre-packaged frameworks and common controls create one environment
Control rationalization
Duplicate controls reviewed manually
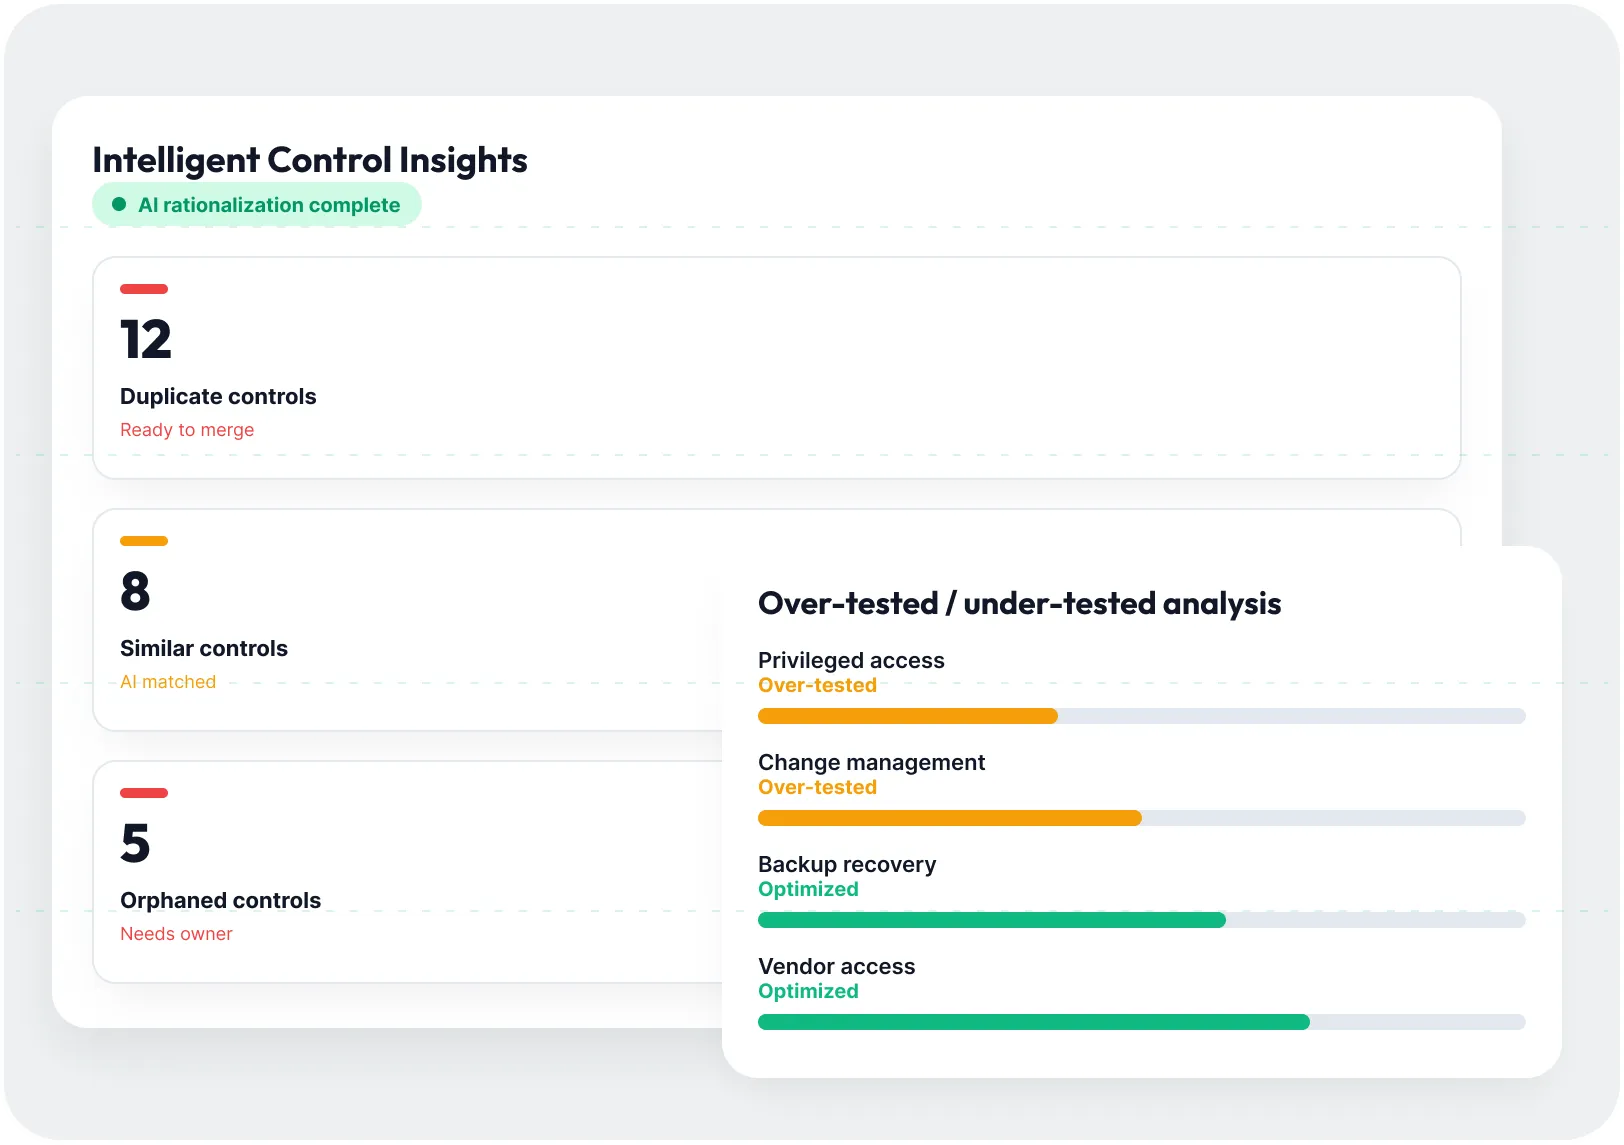
AI identifies duplicate, similar, orphan, and over-tested controls
Assessments
Manual and survey-heavy
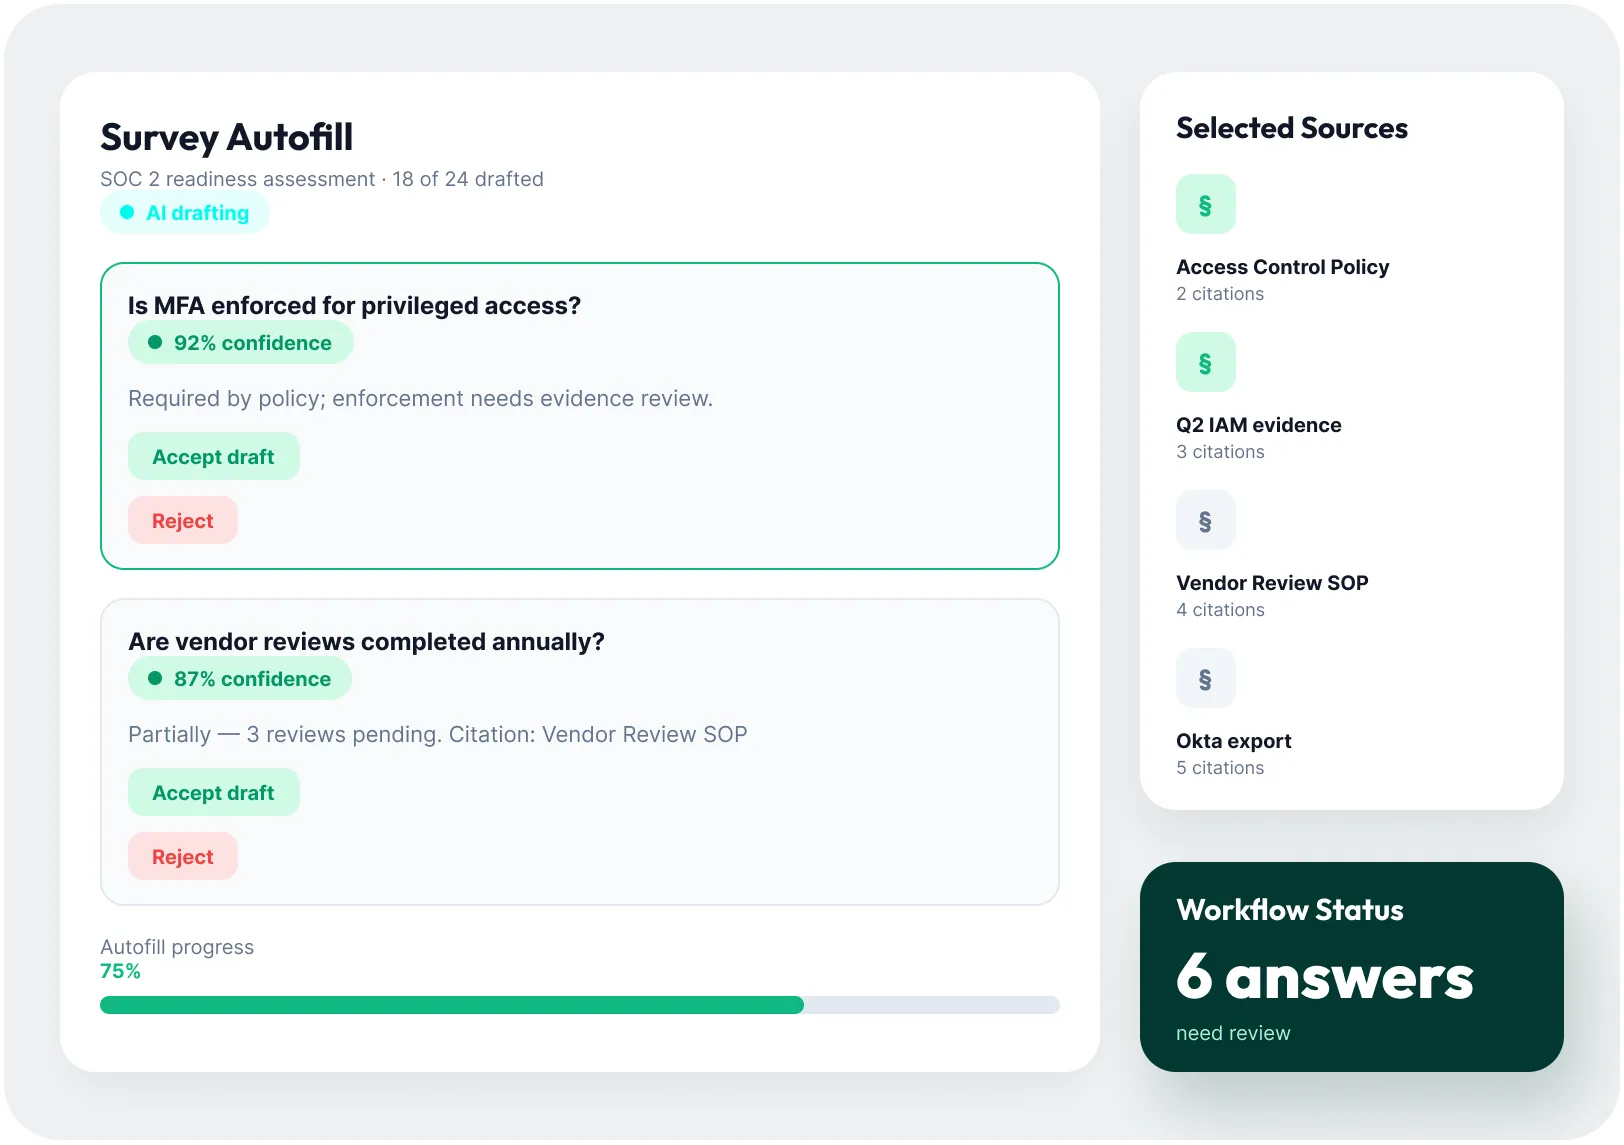
AI drafts source-backed assessment responses
Control testing
Same cadence applied across controls
AI prioritizes attention while agents execute defined testing tasks
Evidence
Requested and reviewed repeatedly
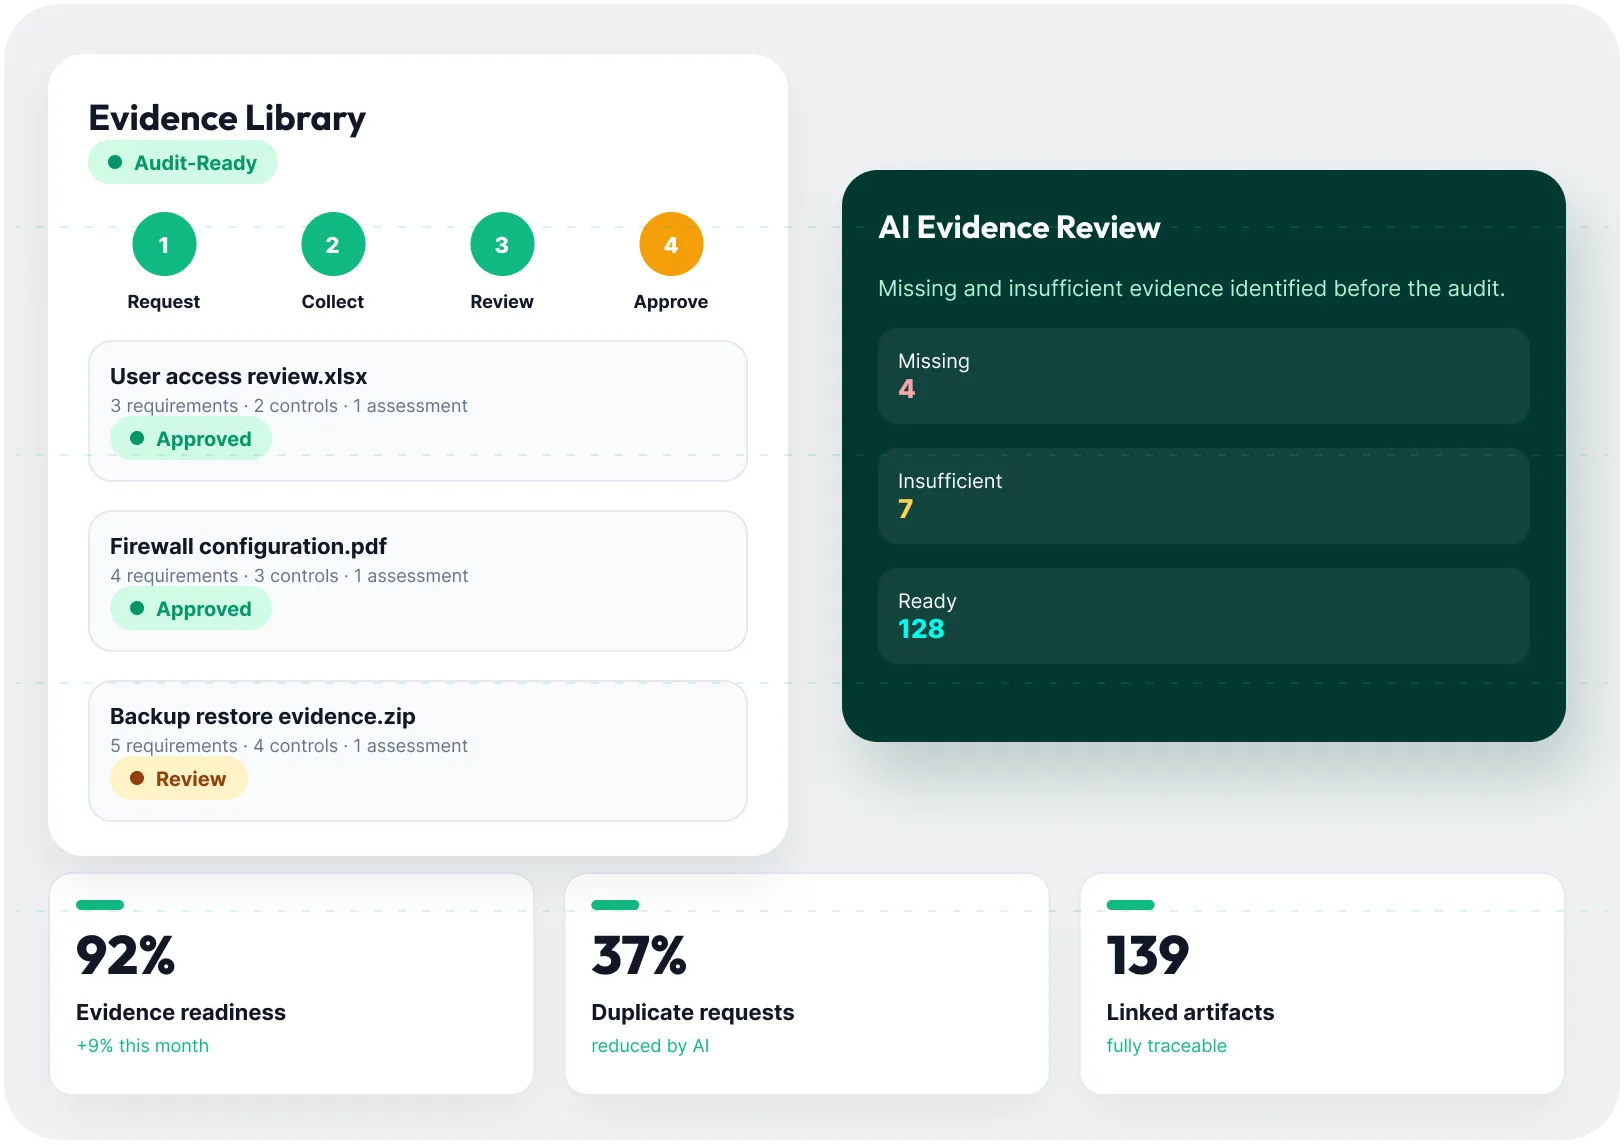
Evidence is collected, approved, mapped, and reused
Gap analysis
Manual requirement comparison
AI identifies control and evidence gaps
Reporting
Periodic compliance snapshots
AI delivers contextual, decision-ready compliance intelligence
Use our interactive ROI calculator, built by Forrester, to estimate what Enterprise GRC could deliver for your organization. Enter details such as annual revenue, number of GRC tools, and compliance exposure to see your potential savings, payback period, and return on investment.
Calculate My ROI
Start faster with leading cyber frameworks, standards, common controls, mappings, and testing guidance.
Rationalize controls and focus assessments and testing on the most material compliance risks.
Trace requirements through controls, tests, evidence, findings, issues, actions, and approvals.
Configure frameworks, assessments, tests, scoring, evidence, workflows, reports, and organizational structures.
Keep AI outputs permission-aware, source-backed, reviewable, traceable, governed, and auditable.
IT and cyber compliance specialists and AI engineers support implementation, adoption, testing, and program optimization.

Analyst Report
Download the excerpt to see why MetricStream was recognized as a GRC Leader in 2025.
Download Now
eBook
Download this eBook to learn about various aspects and requirements of the EU's Digital Operational Resilience Act (DORA) and the key steps that can help you achieve compliance.
Read More
Case Study
Learn how MetricStream helped an oil and gas giant automate cyber risk and compliance management processes and improved its overall cyber maturity and resilience.
Read More
Whitepaper
Learn how GRC leaders are adopting AI responsibly and proving measurable ROI at scale.
Read MoreMetricStream IT and Cyber Compliance Management is an AI-native IT compliance management software product that provides a common framework for managing and monitoring compliance with a broad range of IT regulations and standards. It scales across the enterprise, automating compliance workflows, consolidating control data in a central repository, and providing real-time visibility into compliance status across geographies, business units, and functional departments. The product includes more than 800 pre-built controls that can be mapped to relevant regulations.
According to customer responses and the GRC Journey Business Value Calculator, MetricStream IT and Cyber Compliance Management has delivered a 60% faster control-testing and evidence management cycle time and a 39% reduction in expected regulatory losses and other expenses.
As IT compliance software, MetricStream IT and Cyber Compliance Management supports a broad range of IT regulatory frameworks and standards, including NIST CSF, ISO 27001, HIPAA, PCI DSS, SOC 2, and more than 800 pre-packaged controls. Through integration with the Unified Compliance Framework (UCF), it maps over 9,300 IT control statements to more than 1,200 regulations, allowing organizations to rationalize compliance activities across frameworks and eliminate duplicative control assessments.
MetricStream IT and Cyber Compliance Management allows organizations to schedule automatic control assessments based on predefined criteria and checklists. Control tests are conducted using question-and-procedure formats, with evidence attached and results scored and tabulated. Electronic sign-offs can be captured at departmental and functional levels and rolled up for executive certifications. The platform's federated content library delivers alerts on IT regulatory content updates so organizations can respond promptly.
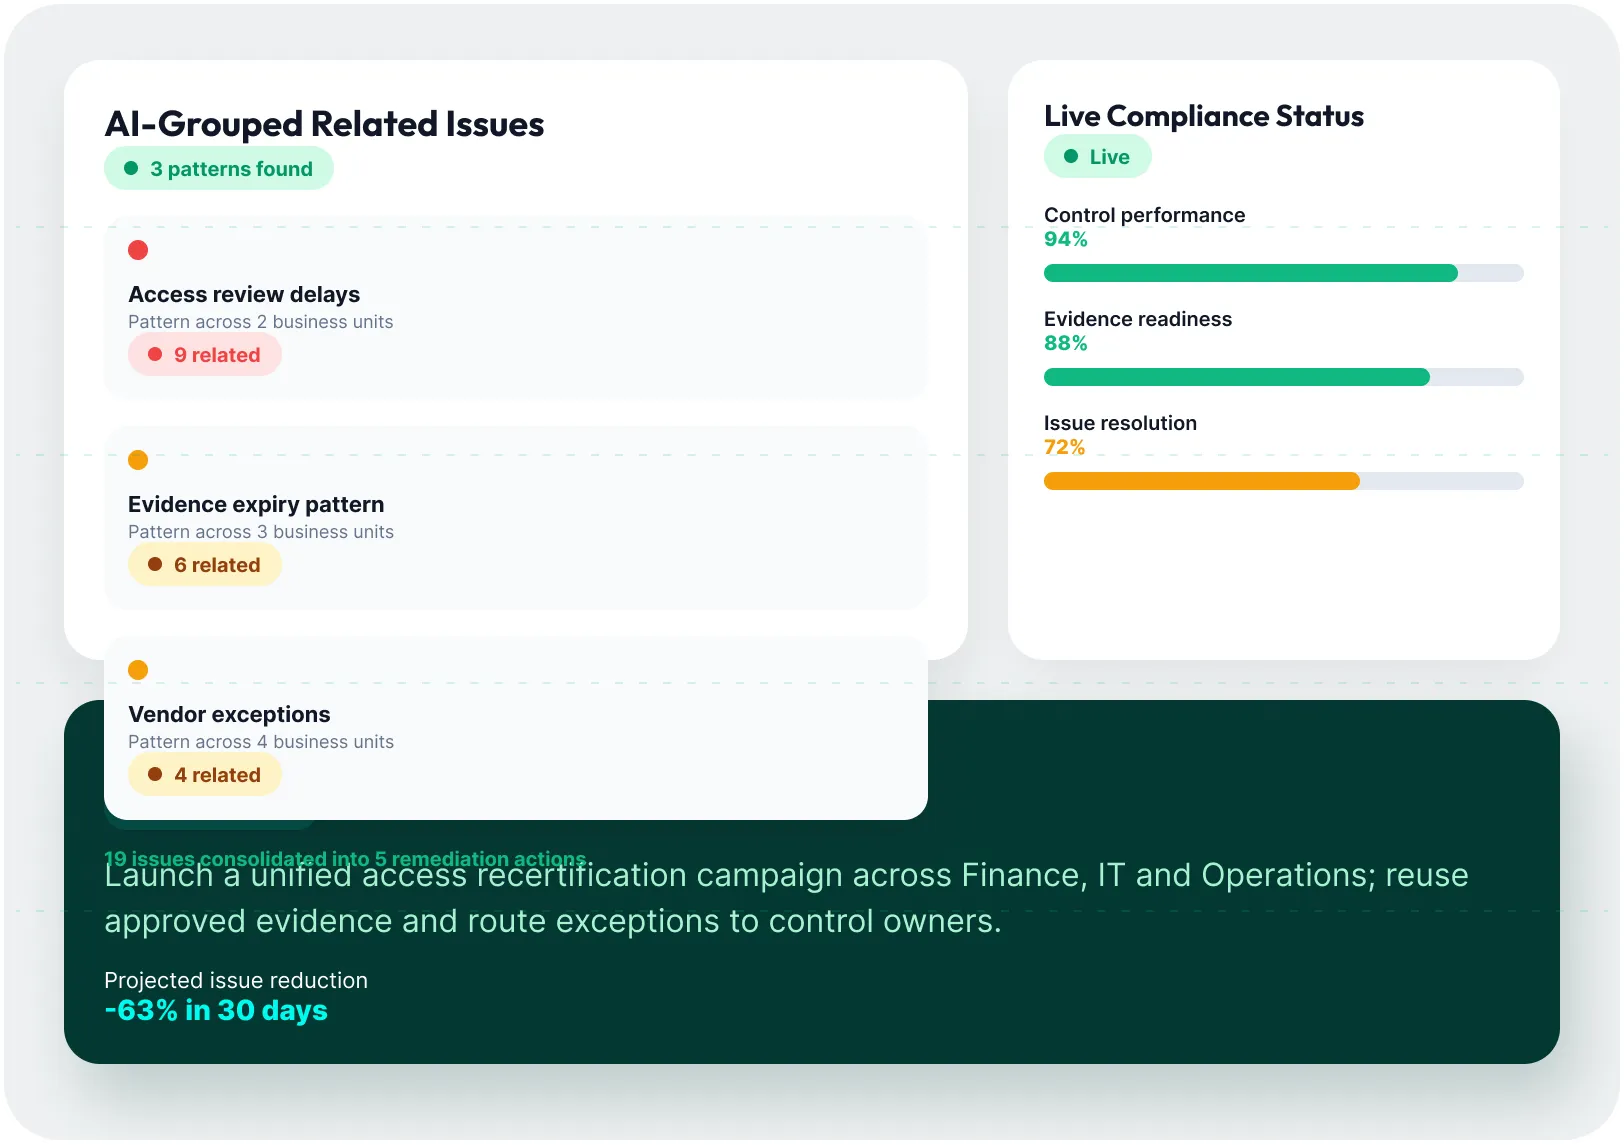
MetricStream IT and Cyber Compliance Management uses AI to streamline issue identification and classification in the compliance program. AI quickly identifies issues based on their relationship to other issues and findings, recommends appropriate issue classifications, and sends automated alerts to keep investigation and remediation task assignments on track. This reduces the manual effort required for compliance issue management and accelerates the remediation cycle.
MetricStream IT and Cyber Compliance Management provides real-time reports, user-specific dashboards, and graphical snapshots that give IT compliance professionals top-level visibility into the status of compliance assessment efforts and the overall compliance profile. These views can be filtered by geography, business unit, regulation, and control owner, allowing organizations to quickly identify compliance gaps and allocate resources to address the highest-priority issues.
MetricStream IT and Cyber Compliance Management includes a built-in evidence management capability that allows compliance teams to associate evidence with specific compliance projects, request new evidence from control owners, and export evidence for audit review. Centralizing evidence in the platform eliminates the fragmented evidence collection practices—spreadsheets, emails, shared drives—that create risk during regulatory audits.
MetricStream IT and Cyber Compliance Management includes a Federated Content Library that delivers structured content channels covering IT regulatory updates from authoritative sources. Organizations can subscribe to alerts for specific regulations and receive notifications when standards or controls change. Alerts are actionable within the platform—users can raise issues, notify stakeholders, link alerts to data objects, and generate reports directly from the notification.
MetricStream IT and Cyber Compliance Management rationalizes controls across IT compliance frameworks by maintaining a central compliance hierarchy that maps controls to multiple regulations simultaneously. A single control that satisfies requirements in both ISO 27001 and NIST CSF, for example, needs to be tested only once, with results shared across both frameworks. This cross-framework rationalization reduces the total number of control tests an organization must conduct, lowering compliance costs and resource requirements.
MetricStream IT and Cyber Compliance Management allows organizations to configure and execute IT compliance surveys, certifications, and control self-assessments using predefined templates and schedules. Assessments are uploaded through a simple form-based interface, and electronic sign-offs can be captured at departmental and functional levels before being rolled up for executive review. This structured approach to self-assessment supports audit readiness and demonstrates a mature, disciplined approach to IT compliance.