

Introduction
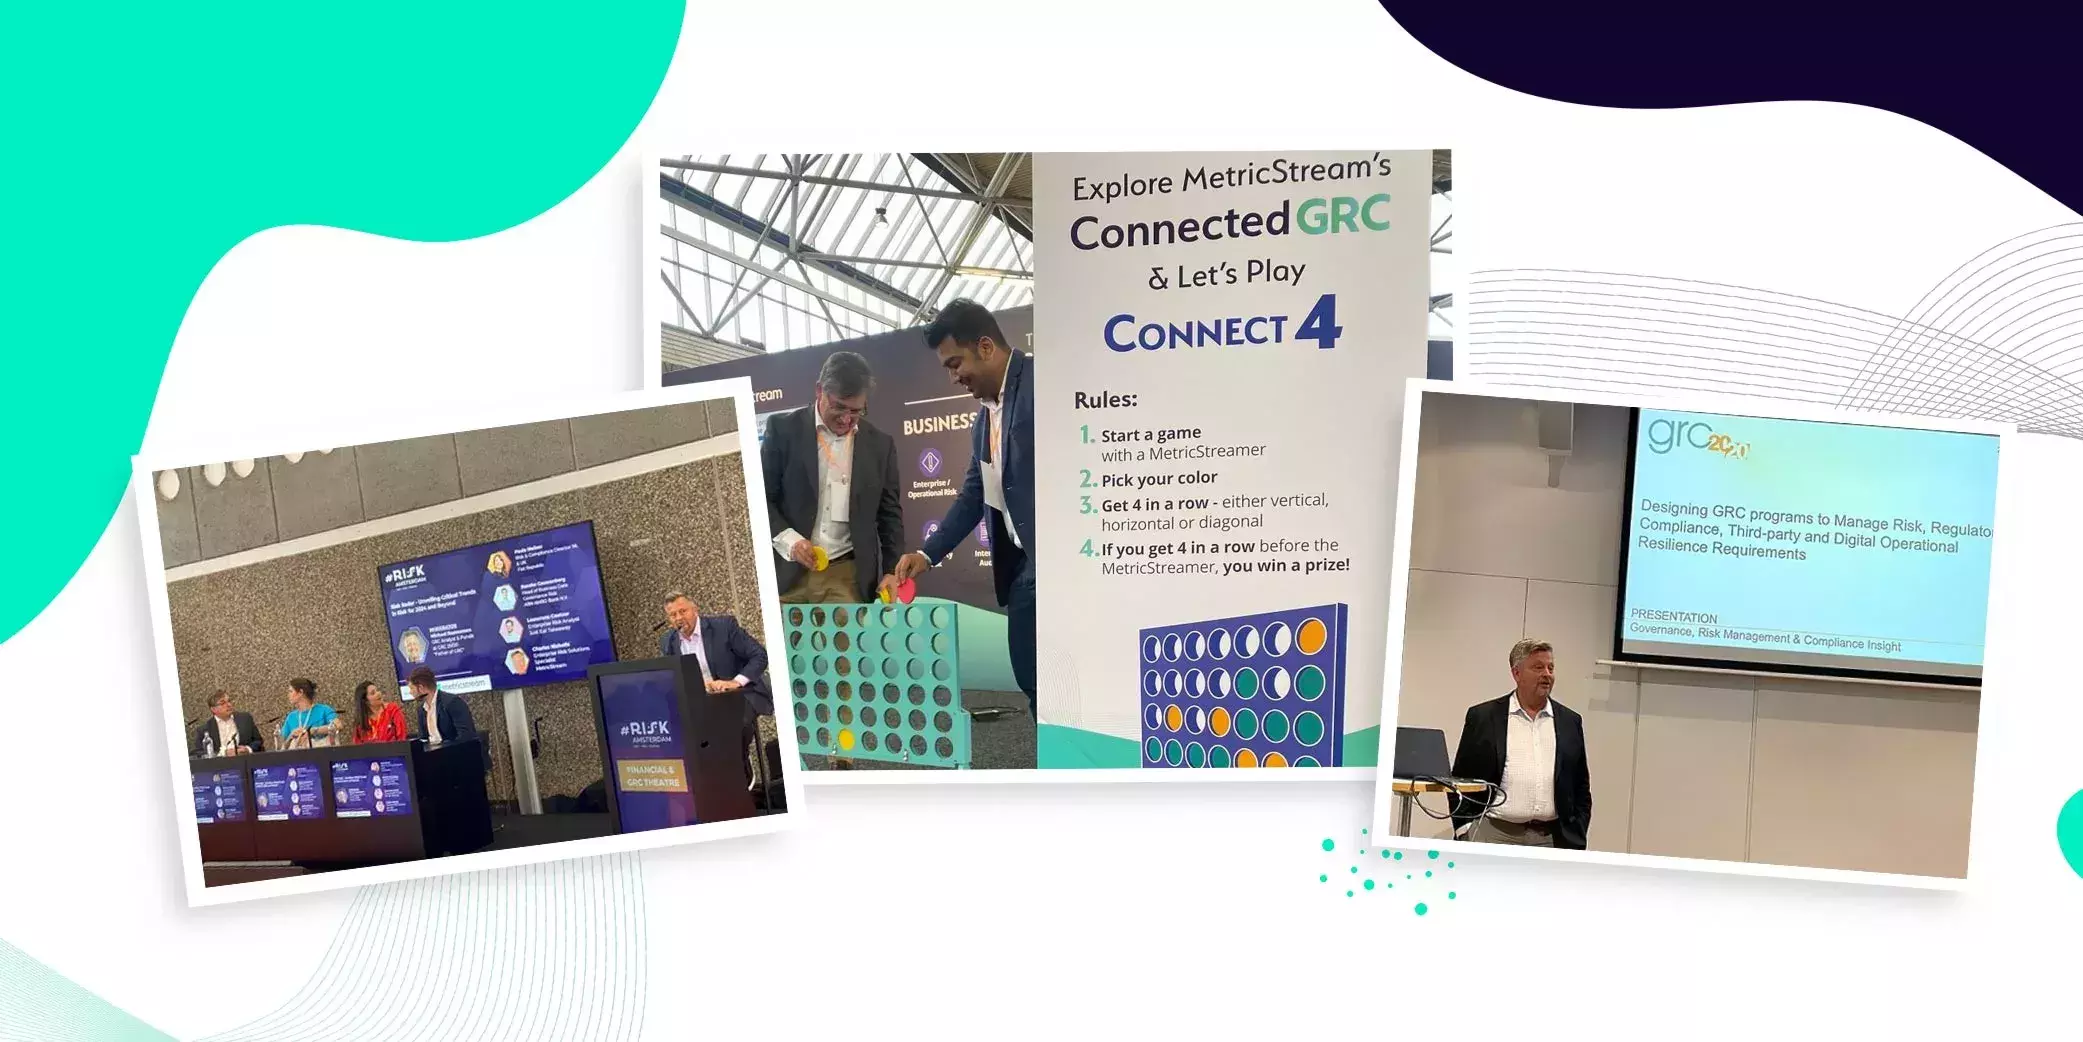
I am delighted to have spent a wonderful three days in Amsterdam with our MetricStream customers, prospects, industry experts, consultants, and solutions providers, with a peer-to-peer round table session on Tuesday, the 26th of September, followed by two days at the #Risk Amsterdam event. Here is a recap of the important highlights and key insights from the sessions that were conducted over the three days.
Executive Roundtable Session
The executive round table session on Designing GRC Programs to Manage Risk and Enhance Operational Resilience saw cross-industry operational risk, legal, and compliance experts from banking and aviation to advanced medical suppliers. Confidentiality was assured through Chatham House rules, so I will not quote specific comments and details here but simply summarize the key challenges and discussion points that were raised and discussed in the following areas:
Compliance
- Challenges faced by dealing on a global basis in different jurisdictions
- Aligning and attempting to comply in a standard and consistent manner across the organization
- The need to string internal cooperation and alignment to address these issues
- The need to use tools such as the MetricStream platform to map your policies and processes to these regulations and standards and drive this standard unified approach.
- Fragmentation and complexity of global management
- No such thing as a zero-tolerance for regulatory compliance as in the real world, there is always cost pressure vs. full compliance
- Struggle with the volume and complexity as to where to focus given daily changing priorities
- Need to engage and align with regulators as appropriate to your industry
Culture
Aligning to the above discussion on international issues, challenges, and management, the attendees shared and reviewed the challenges around:
- The differing international and corporate cultures and the “Human” element of silos and differences; as above, a fragmented view in the current state
- The potential to have a different focus on risk vs. compliance by region
- The differing and ever-changing assessments of risk vs. likelihood
- The strong concern about human corruption and intellectual property rights protection
- The need to keep abreast and be agile with ever-changing sanctions and geopolitical risks
Volume Overload
All attendees agreed to the stated challenge from one of our guests around the simple challenge of dealing with ever-increasing volumes, including the:
- The increasing number of internal controls to test
- Limited resources and budget
- Increasing standards and regulations
- The need to increase efficiency and standardization
- The consistency and transparency required in evaluation
- The need to remove duplication of effort that persists
- The need to deliver and manage effective control execution across multiple divisions and silos of the organization
The Balancing Act of Aligning Goals and Costs
- The costs of managing the ever-increasing volume weighed up against investor pressure to reduce costs, yet also investor pressure for greater assurance and transparency
Operational Resilience and Data
- Multiple regulations and different jurisdictions with slightly different requirements
- Finding the synergy across the operational risk teams is seen as a challenge with operational resilience
- Data integration challenges and alignment are being experienced
- Managing to identify the critical business processes, systems, and assets across the entire organization still presents challenges for some of our attendee
Third-Party Risk and ESG
- Concern with gathering the right data
- Managing the quality of data
- Assessing the right cadence of testing and dealing with change
- What ESG data is being tracked, and how valid is it?
Workshop by Michael Rasmussen
The roundtable discussion was then followed by a workshop with GRC Pundit Michael Rasmussen, “The Father of GRC,” where he further reviewed the above topics with a special emphasis on the “Human Factor.” He discussed in depth:
- The nested supply chain issues of 4th and 5th parties and potential impacts
- The need for the human firewall, that policies need to be detailed, adhered to, and monitored over and over, and that we need to rely on more than just conduct
- The use of AI was reviewed and discussed in appropriate circumstances, and the risks of not using AI and Machine Learning technology
#Risk Amsterdam Event
Then, on Wednesday and Thursday, the 27th and 28th of September, we participated in the #Risk Amsterdam event, and not surprisingly, much the same topics seemed to be the subject of the presentations and conversations. Although we were anticipating a significant focus and questions around the pending Digital Operational Resilience Act (DORA), most of our conversations focused on some of the component elements rather than full DORA compliance and requirements as follows:
- Policy management and aligning policies to regulations and controls
- Financial & SOX controls testing and certification
- IT and Cyber Risk: quantification of cyber risk assessments using FAIR
- Quantification and scenario testing in operational risk management / non-financial risk
- Bow-Tie analysis
- Risk and loss events treatment and reporting
- Managing impact assessments with assets and processes across the organization
- Managing control frameworks, aligning to COBIT, and yet adding your own controls, such as ISO 27001 and NIST Frameworks
- Integrating third party related content feeds into the GRC platform, including Dow-Jones; BMC, Qualys, BitSight, EcoVadis, FinregE, Compliance.ai, Cube, Reg-Room, Sustainalytics, OFAC and Sanctions Lists, among many others
Panel Session on Risk Radar- Unveiling Critical Trends in Risk for 2024 and Beyond
On Thursday afternoon, I joined the panel moderated by Michael Rasmussen with representatives from ABN Amro, Just Eat, and Fiat Republic to share our feedback on the topic “Risk Radar- Unveiling Critical Trends in Risk for 2024 and Beyond.” The big topics discussed were:
- The impact of Environmental Risks such as the extreme European heatwave and forest fires, Libyan floods, and Moroccan earthquakes and the ability to be agile and manage the usually determined low likelihood but high impact events that seem to be seen as ever-more ‘likely.’
- The onward impact on supply chains, such as the Suez Canal blockage, brown-out power outages, and then the encompassing Geopolitical, Market, Economic, and Liquidity Risks arising from the likes of the Ukraine-Russia war and other cold war scenarios such as Taiwan and the potential impacts.
- The reputational loss/ consequence issues around non-compliance on the ‘S’ or Social in ESG with modern slavery, child labor and exploitation, and human rights violations outside Europe as another major risk to manage and contend with.
- IT & Cyber Risk continuing to remain a very high threat, and the focus extended to the requirements of DORA in the risk and ability to recover quickly from technology failures
- The risks around AI, along with the associated ethical concerns and the need to remove bias from algorithm-produced results, to derive fair and equitable solutions that do not infringe on human rights, diversity, and inclusion.
- The risks of AI and benefits of AI with Deep Fakes and criminal spoofing and phishing and the importance of KYC and KYS along with AML were fully reflected upon.
- Regulatory Compliance Risks are also considered a never-ending and growing challenge that is not going away. This significantly impacts the managing and complying of internal costs, with the risk of fines now being made more personal as in the UK through SMCR enforcements on individuals rather than just the corporate fines of the past being reviewed by other global regulators.
- The interconnectedness of these risks was reflected upon and how all these risks can fully impact the supply chain of not just the third party but extended 4th and 5th parties.
On the panel, we shared our views on the strategies to overcome these risks and how, when aligned with the MetricStream platform can provide:
- Clear and transparent reporting
- Drive long-term sustainable goals and implement associated clear policies
- Drive fast, accurate data on emerging risks across the organization
- Use technology to assist predictive analytics and aid human decision-making
- Use technology to manage the vast data requirements and flow
- Need for consistency and standardized taxonomies of data against which to make decisions or a “single-source-of-truth”
- Conduct from the top, human awareness, and training and policy attestations frequently reviewed and updated
- Engage with the regulators early and get involved in the consultation process wherever possible
- Manage risk vs. reward and why more scenario analysis and appropriate quantification in the right areas are required to best determine your risk treatment or adoption
- Regular review policy exceptions due to the changing environment
Needless to say, we on the panel ran out of time on these topics, but MetricStream, through our powerful, fully federated, and scalable data model, is well placed to assist in the improved efficiency, accuracy, alignment, consistency, and transparency of residual risks and managing mitigating actions against a quagmire of external risks that are costly and challenging across all global markets.
While we at MetricStream certainly can’t do everything, we can certainly help to drive consistency, efficiency, and improved management of your company’s Governance, Risk, and Compliance program by enabling the connectedness and providing rich 360-degree views of those connections, driving faster and better quality data and management of resulting treatments and actions to give you the tools to thrive on risk.
Interested to learn how MetricStream can help? Request a demo now!
The above blog is an edited version of an article published by the author on LinkedIn. Read the original version here.