

Introduction
Modern businesses have embraced complex legal structures, while regulators have developed policies and rules to ensure the integrity of the legal system. In this labyrinth of rules, regulations, and legislations, legal risks pose a significant challenge to organizational stability and growth.
As per a survey conducted by Deloitte, 41% of non-banking and 14% of banking respondents have no definition of legal risk in place for their organization.These risks, which stem from regulatory compliance issues, contractual disputes, and a myriad of other legal vulnerabilities, can result in substantial financial losses, reputational damage, and operational disruptions.
In this guide, we explore why legal risk management is critical for businesses to navigate these complexities, especially ensuring not only compliance with the law but also safeguarding their assets and reputation – offering strategies to minimize exposure and maximize growth potential.
Key Takeaways
- Legal risk involves the potential for financial loss, reputational damage, or operational disruption due to legal actions, non-compliance with laws and regulations, or contractual failures. It is a pervasive risk that affects all aspects of business operations and requires comprehensive management strategies.
- Legal risk encompasses potential financial, reputational, and operational consequences arising from legal actions or non-compliance with laws and regulations.
- Businesses face various legal risks, including regulatory compliance issues, contractual disputes, intellectual property infringement, employment law violations, and data privacy breaches.
- Proactively managing legal risk through regular audits, robust contract management, employee training, legal counsel, and data protection measures is essential to minimize exposure and ensure business continuity.
- Integrating legal risk management into the enterprise risk management (ERM) framework provides a comprehensive approach to addressing all types of risks, leading to cost savings and improved operational resilience.
What is Legal Risk?
Legal risk is the possibility of financial loss, reputational damage, or operational disruption due to non-compliance with laws and regulations, legal actions, or contractual failures. Identifying all applicable legal risks is crucial for an organization's risk management strategy.
The 2024 Litigation Trends Annual Survey by Norton Rose Fulbright found that 61% of companies reported being engaged in at least one regulatory proceeding in the past year, with an average of 3.9 proceedings. Notably, the median number of lawsuits reported by respondents was 6 with 42% of them expecting the number to rise in 2024.
Broadly speaking, legal risk in business operations can arise due to non-compliance with regulatory requirements, employment and labor laws, contractual obligations, intellectual property, and other areas.
The scope of legal risk is extensive, requiring businesses to remain vigilant and proactive in their risk management efforts to avoid legal pitfalls and maintain operational integrity.
Potential Consequences of Legal Risk
Here are some typical types of consequences that originate out of realized legal risks.
Financial
The financial consequences of legal risk can be devastating. Organizations may incur significant costs related to legal fees, fines, penalties, and settlements. According to a study by the Ponemon Institute, the cost of non-compliance is 2.71 times higher than the cost of compliance. On average, non-compliance costs organizations $14.82 million annually, compared to $5.47 million for compliance.
These financial burdens can erode profit margins and threaten the financial stability of the business.
Reputational
Reputational damage is another severe consequence of legal risk. Negative publicity resulting from legal disputes or regulatory violations can diminish customer trust and loyalty, making it difficult for a business to attract and retain clients.
Courtesy of the digital age, news of legal troubles spread rapidly, further exacerbating the damage to an organization’s reputation.
Operational
Operational disruptions caused by legal issues can impede a company's ability to function smoothly. This can include halting production, delaying product launches, and diverting management resources to handle legal problems. In extreme cases, legal risks can lead to business closures or the need for significant restructuring.
Common Legal Risks
Businesses today operate in an ever-expanding legal and regulatory environment. From data protection mandates to labor laws and intellectual property protections, the risk spectrum is wide. Below are key areas where legal risks typically emerge:
Regulatory Compliance
Companies in all sectors are subject to numerous laws and regulatory requirements ranging from financial reporting and environmental regulations to privacy and consumer protection. Non-compliance isn’t just costly; it can lead to enforcement actions, business restrictions, and reputational damage.
- Data Breach Costs: In 2024, the global average cost of a data breach rose to US $4.88 million, a 10% increase from the prior year.
- Declining Costs in 2025: According to IBM’s 2025 report, the average breach cost dropped to US $4.44 million, marking the first decline in five years, attributed to faster detection and containment aided by AI and automation.
These figures highlight how regulatory exposure, combined with operational risk, can amplify total legal liability.
Contractual Disputes
Contracts underpin nearly every business relationship—suppliers, customers, partners—and when contract terms are ambiguous or violated, disputes follow. Such disputes can lead to litigation, arbitration, and damaged relationships.
- Typical Disputes: Disagreements over pricing, performance, delivery schedules, intellectual property clauses, and confidentiality.
- Mitigation Approaches: Use of contract lifecycle management (CLM) tools, clear terms, documented change management, and proactive legal review can reduce escalation.
Employment Law Violations
Workforce legal risks—wrongful termination, harassment, discrimination, wage and hour violations—are among the most frequent and publicly visible legal exposures a company faces.
- Rising Charges: In FY 2024, the U.S. Equal Employment Opportunity Commission (EEOC) received Legal risks extend across every aspect of a modern business. By staying informed of evolving statutes, leveraging compliance automation, and weaving legal awareness into culture, organizations can mitigate exposure, protect value, and build resilience.
- Litigation Activity: The EEOC has also filed numerous lawsuits; in FY 2024 it filed 110 employment discrimination lawsuits.
- Prevention Practices: Strong HR policies, training, consistent enforcement, and internal reporting mechanisms are critical to reducing exposure.
Data Privacy and Cybersecurity Breaches
In a data-driven economy, privacy and security risks often translate directly into legal liability.
- Cost Impact: As cited earlier, a data breach in 2024 averaged US $4.88 million globally.
Regulatory Penalties: Fines under GDPR and other privacy laws can run into the tens or hundreds of millions.
Reputational Risk: Beyond fines, breaches erode user trust and invite lawsuits or class actions.
Best Practices: Privacy impact assessments, encryption, incident response plans, and compliance monitoring are baseline requirements.
- Cost Impact: As cited earlier, a data breach in 2024 averaged US $4.88 million globally.
Emerging Legal Risks
As technology evolves, new legal risk vectors emerge:
- AI and Algorithmic Liability: Organizations deploying AI may face claims related to bias, transparency, or unfair outcomes under upcoming AI regulation (e.g. the EU AI Act).
ESG / Sustainability Disclosure: Misrepresentation or misleading sustainability claims can lead to enforcement or shareholder suits.
Data Localization & Cross-Border Transfers: Changing laws in jurisdictions like the EU and India create complexity in how data is collected, stored, moved, or processed.
- AI and Algorithmic Liability: Organizations deploying AI may face claims related to bias, transparency, or unfair outcomes under upcoming AI regulation (e.g. the EU AI Act).
Legal risks extend across every aspect of a modern business. By staying informed of evolving statutes, leveraging compliance automation, and weaving legal awareness into culture, organizations can mitigate exposure, protect value, and build resilience.
Why Manage Legal Risk in ERM?
It is essential for organizations to include the management of legal risks in the broader enterprise risk management (ERM) framework for reasons more than one:
Proactive Mitigation of Issues
Proactively managing legal risk is crucial for protecting an organization’s assets and ensuring its long-term sustainability. By identifying potential legal threats early and implementing strategies to mitigate them, companies can avoid the escalation of legal issues into more significant problems. Managing legal risks in a proactive manner requires regular monitoring of the legal environment, staying informed about changes in laws and regulations, and maintaining a vigilant approach to compliance.
Comprehensive Approach to Risk Management
Integrating legal risk management into the broader enterprise risk management (ERM) framework ensures a cohesive approach to managing all types of risks. ERM provides a structured process for identifying, assessing, and mitigating risks across the entire organization, including financial, operational, strategic, and legal risks. By incorporating legal risk into ERM, businesses can ensure that they are addressing legal threats in conjunction with other critical risks, thereby achieving a more comprehensive risk management strategy.
Cost Savings and Business Continuity
Effective legal risk management can lead to significant cost savings by preventing fines, reducing legal fees, and avoiding costly litigation. Additionally, it enhances business continuity by minimizing operational disruptions caused by legal issues. Companies that proactively manage their legal risks are better positioned to maintain steady operations and achieve their strategic goals without the interruptions that legal problems can cause.
Best Practices for Mitigating Legal Risk
Here are some proactive strategies and practices we suggest that can play a pivotal role in mitigating legal risks for organizations:
Regular Legal Audits:
Conducting regular legal audits helps ensure compliance with applicable laws and regulations. These audits involve reviewing business practices, contracts, and compliance with regulatory requirements. Regular audits can identify potential legal issues before they become significant problems, allowing for timely corrective action.
Contract Management:
Effective contract management is crucial for minimizing legal risk. This involves carefully drafting, reviewing, and monitoring contracts to ensure they are clear, enforceable, and protect the organization’s interests. Key elements of contract management include clearly defining terms, setting out obligations and responsibilities, and including dispute resolution mechanisms.
Employee Training:
Providing ongoing training to employees about legal requirements and company policies helps reduce the risk of non-compliance. Training programs should cover key areas such as data protection, anti-bribery and corruption laws, and workplace conduct. Well-informed employees are less likely to engage in activities that could lead to legal issues.
Legal Counsel:
Engaging experienced legal counsel is essential for navigating complex legal landscapes. Legal experts can provide guidance on regulatory compliance, contract negotiations, intellectual property protection, and dispute resolution. Having access to legal advice helps organizations make informed decisions and mitigate legal risks effectively.
Data Protection Measures:
Implementing robust data protection measures is critical for complying with data privacy laws and safeguarding sensitive information. This includes using encryption, access controls, and conducting regular security assessments. Data protection measures help prevent data breaches and ensure compliance with regulations such as GDPR and CCPA.
Legal Risk Management Process
To effectively manage legal risks, organizations should follow a systematic process that includes:
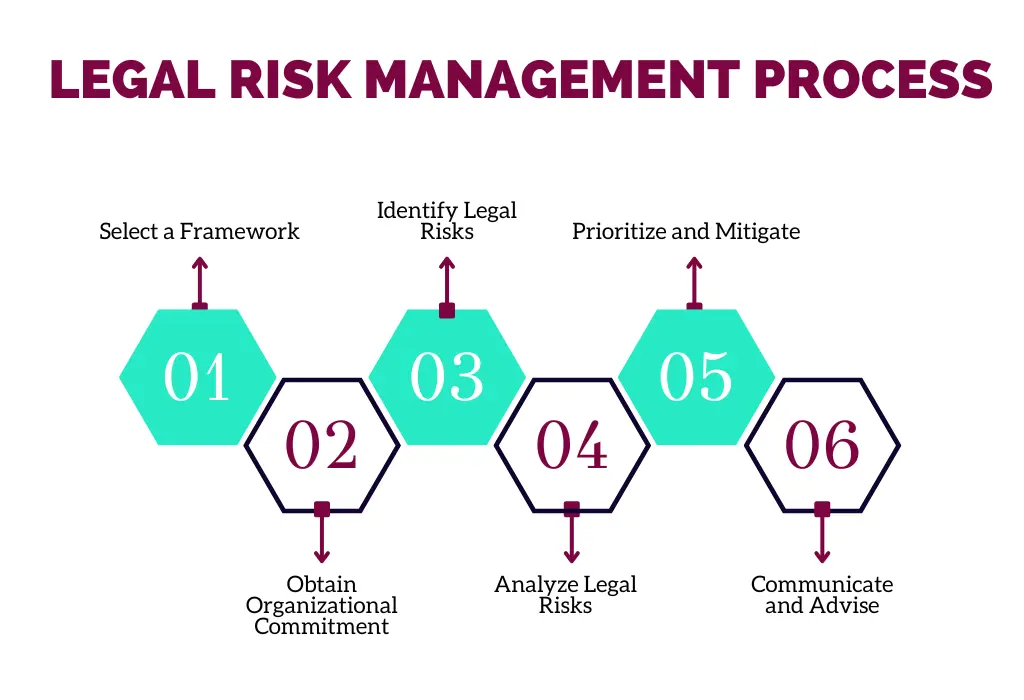
Select a Framework
Choosing the right risk management framework is essential for structuring your legal risk management efforts. ISO 31000 is a widely recognized framework that defines risk as "the effect of uncertainty on objectives." It provides a comprehensive approach to managing risks, including those with legal implications.
Obtain Organizational Commitment
Securing organizational commitment is crucial for the success of any legal risk management initiative. This involves defining the scope of the initiative, identifying the types of legal risks to be tracked, determining the key stakeholders for legal risk reporting, and allocating the necessary budget and resources.
Identify Legal Risks
Identifying legal risks involves compiling a broad list of potential risks through a structured approach:
Sources of Legal Risk:
These include contracts, regulations, litigation, and structural changes.
Recognizing Potential and Actual Risks:
Legal risks can arise from hazards, events, situations, and scenarios.
Recording Risks in a Risk Register:
This involves documenting the identified risks, along with their likelihood, consequences, and combined risk rating.
Analyze Legal Risks
Analyzing legal risks requires understanding the risks in the risk register and assessing their impact. This involves evaluating the likelihood of discovery and adverse decisions, as well as the potential consequences. Risk analysis is an iterative process and is important for refining the risk register and prioritizing risks for treatment.
Prioritize and Mitigate
Once the legal risks have been assessed, organizations need to prioritize them for mitigation measures. This is based on an organization’s risk tolerance level. Legal risks that are deemed intolerable need to be treated. Treatment options include avoiding the risk, increasing risk activities if beneficial, removing the risk source, altering the likelihood or consequences, and sharing the risk through contracts or insurance.
Communicate and Advise
Communicating the results of legal risk management efforts is essential for ensuring that all stakeholders are aware of the identified risks and the measures being taken to address them. Effective communication involves presenting risks clearly and advising on strategies to manage them.
Legal Risk Tolerance & Appetite
Organizations don’t just react to legal risk—they should define how much legal risk they are willing to live with, and what kinds. That’s what legal risk appetite and tolerance are all about.
What Are Legal Risk Appetite & Tolerance?
- Risk Appetite: The amount and type of risk an organization is willing to accept in order to pursue its strategic objectives. It’s a forward-looking policy statement.
- Risk Tolerance: Narrower, more granular: the acceptable variation an organization will allow around risk appetite. For example, even if an organization has a low appetite for regulatory breach risk, it may tolerate some small errors if they are quickly remedied.
Why Define Legal Risk Appetite & Tolerance?
- Alignment with Strategy: Legal risk appetite ensures legal risk decisions (contracts, compliance, litigation) are aligned with broader business goals. Without this, different parts of an organization may pull in conflicting directions.
- Decision-Making Clarity: If legal risk appetite is clearly articulated, managers can know when to escalate, when standard controls suffice, or when to walk away from a deal.
- Regulator Expectations & Accountability: Setting and communicating legal risk appetite signals to regulators, boards, and stakeholders that the organization is serious about legal compliance and governance.
How Organizations Set Legal Risk Appetite & Tolerance
Here are steps and considerations:
Assess Business Context & Capacity
- Understand financial strength, reputation sensitivity, industry legal landscape, regulatory pressure.
- Evaluate what losses (financial, reputational) the organization can absorb.
Categorize Legal Risks
- Regulatory compliance
- Contract obligations
- Intellectual property
- Employment law
- Privacy/data protection
Define Levels & Thresholds
- Example: “Low” appetite for regulatory non-compliance; “medium” tolerance for minor contract slip-ups; "zero" appetite for data privacy violations.
- Use quantitative thresholds where possible (e.g. monetary amounts, number of incidents, % of contracts failing standard clause checks).
Document in a Risk Appetite Statement
- Many organizations have formal statements approved by a board or the C-suite. For example, USAID’s risk appetite statement has a LOW appetite for legal risk in many domains and MEDIUM for others.
- Many organizations have formal statements approved by a board or the C-suite. For example, USAID’s risk appetite statement has a LOW appetite for legal risk in many domains and MEDIUM for others.
Monitor & Review
- Changes in business model, regulation, risk incidents, or external environment (e.g. new laws) can shift what is tolerable. Risk appetite needs periodic review.
- Changes in business model, regulation, risk incidents, or external environment (e.g. new laws) can shift what is tolerable. Risk appetite needs periodic review.
Real-World Examples & Data
- A recent industry survey showed that the legal sector’s use of AI soared from 22% to 80% in one year, indicating growing comfort with taking some risk (e.g. around AI tool reliance) if matched with controls.
- USAID explicitly has “Legal Risk – Overall Risk Appetite: LOW” for many regulatory and compliance risks.
Common Pitfalls
- Overly vague statements: If risk appetite statements are generic (“we won’t tolerate legal risk”), they won’t guide decisions.
- Discrepancy between stated appetite and actual behavior: Culture, incentives, or lack of controls may lead to taking more risk than intended.
- Not adjusting over time: Changes in regulation, legal precedence, or business direction may make earlier tolerance levels obsolete.
AI & Technology in Legal Risk Management
Technology—especially AI—has quickly become a game-changer in how organizations manage, monitor, and mitigate legal risk.
Key Use Cases & Trends
1. Contract Review & Risk Extraction
Tools like Kira Systems, LawGeex, and others automate reviewing contracts, extracting problematic clauses, and identifying deviations from baseline risk standards. This speeds up legal review cycles and reduces human error.
2. Generative AI Document Summarization & Intake
Summarizing long legal documents, triaging legal requests, classifying them by risk or urgency—all done automatically. Gartner lists “Document Summarization” and “Legal Intake/Triage” among its top use cases for generative AI in legal departments.
3. Regulatory Change Monitoring
Automatically tracking new laws, regulations, and court decisions that affect your industry, and mapping them to internal controls or compliance obligations. AI tools are increasingly used to monitor regulatory updates in real time.
4. Litigation Analytics & Forecasting
Platforms can analyze historical case law to predict outcomes, potential exposure, or preferred legal strategies. This helps legal departments decide whether to settle, dispute, or avoid certain contract terms.
5. Legal Document Lifecycle & Data Governance
Managing the entire lifecycle of legal documents, ensuring compliance for data usage, licensing, and retention. One study on dataset license lifecycle tracing showed AI can identify legal risk mismatches when data is redistributed—only 21% of datasets in one sample had licenses legally permissible for commercialization after redistribution.
Benefits of Applying AI & Tech in Legal Risk Management
1. Efficiency & Speed: Faster contract review, regulatory change detection, and document summarization reduce workload and time to decision.
2. Scalability: AI can process vast numbers of documents or regulations that would be impossible manually.
3. Consistency & Accuracy: Less variability in human interpretation, fewer overlooked clauses or obligations.
4. Proactive Identification: AI can flag potential risks before they become legal problems.
5. Cost Reduction: Fewer legal billable hours, fewer penalties or litigation costs.
Challenges & Risks When Using AI in Legal Contexts
1. Accuracy & Hallucinations: As seen in reports where AI-generated case law citations were fake, or misquoted. Human oversight is essential.
2. Ethical, Bias & Legal Liability: Biases in datasets, lack of transparency in AI decisions, risk of violating malpractice or ethical rules.
3. Data Privacy & Confidentiality: Using legal documents or client data with AI requires strict controls, consent, and secure models.
4. Regulatory & Compliance Constraints: AI tools themselves may be subject to laws (e.g., AI governance, privacy laws, regulations around legal tech).
Best Practices for Technology-Enabled Legal Risk Management
1. Govern policies for AI / tech use: Define what types of legal/AI tools are approved, data handling, oversight, and human in the loop.
2. Pilot and validate: Try tools in limited scope, validate their outputs, check for false positives/negatives.
3. Ensure qualified oversight: Legal teams need to review outputs; risk of relying blindly on AI.
4. Monitor performance metrics: Measure error rates, speed, cost savings, risk incidents triggered/not prevented.
5. Maintain security & privacy standards: Encryption, access controls, secure environments, especially when using third-party or public models.
Conclusion
Legal risk management is a vital component of an organization's overall risk management strategy. By proactively identifying and mitigating legal risks, businesses can protect their financial health, maintain their reputation, and ensure operational continuity. Integrating legal risk management into the ERM framework allows for a comprehensive approach to managing all types of risks, leading to improved resilience and sustainable growth.