Cyber Assistant
Get instant, contextual cyber insights and complete actions faster with guided assistance.
Power Cyber GRC decisions with AI assistants and agents that connect risks, controls, policies, and vendors, on one cyber risk and compliance platform, replacing disconnected security findings and fragmented programs.
Get instant, contextual cyber insights and complete actions faster with guided assistance.
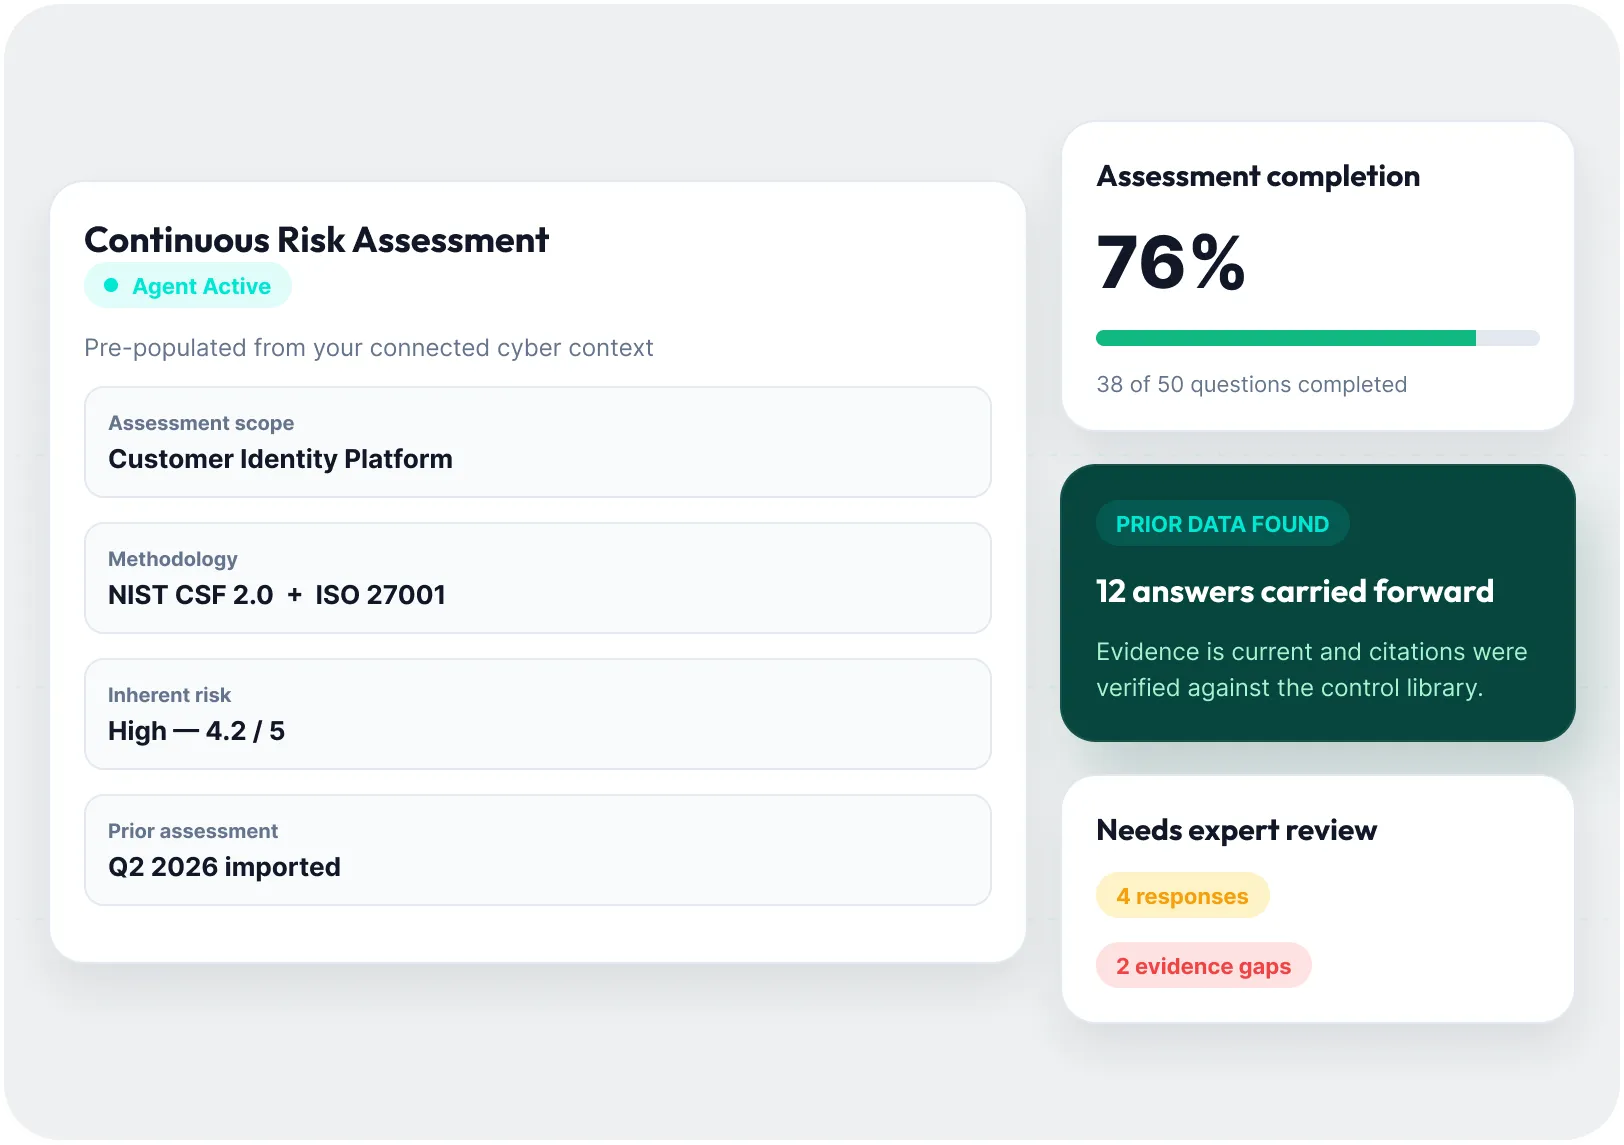
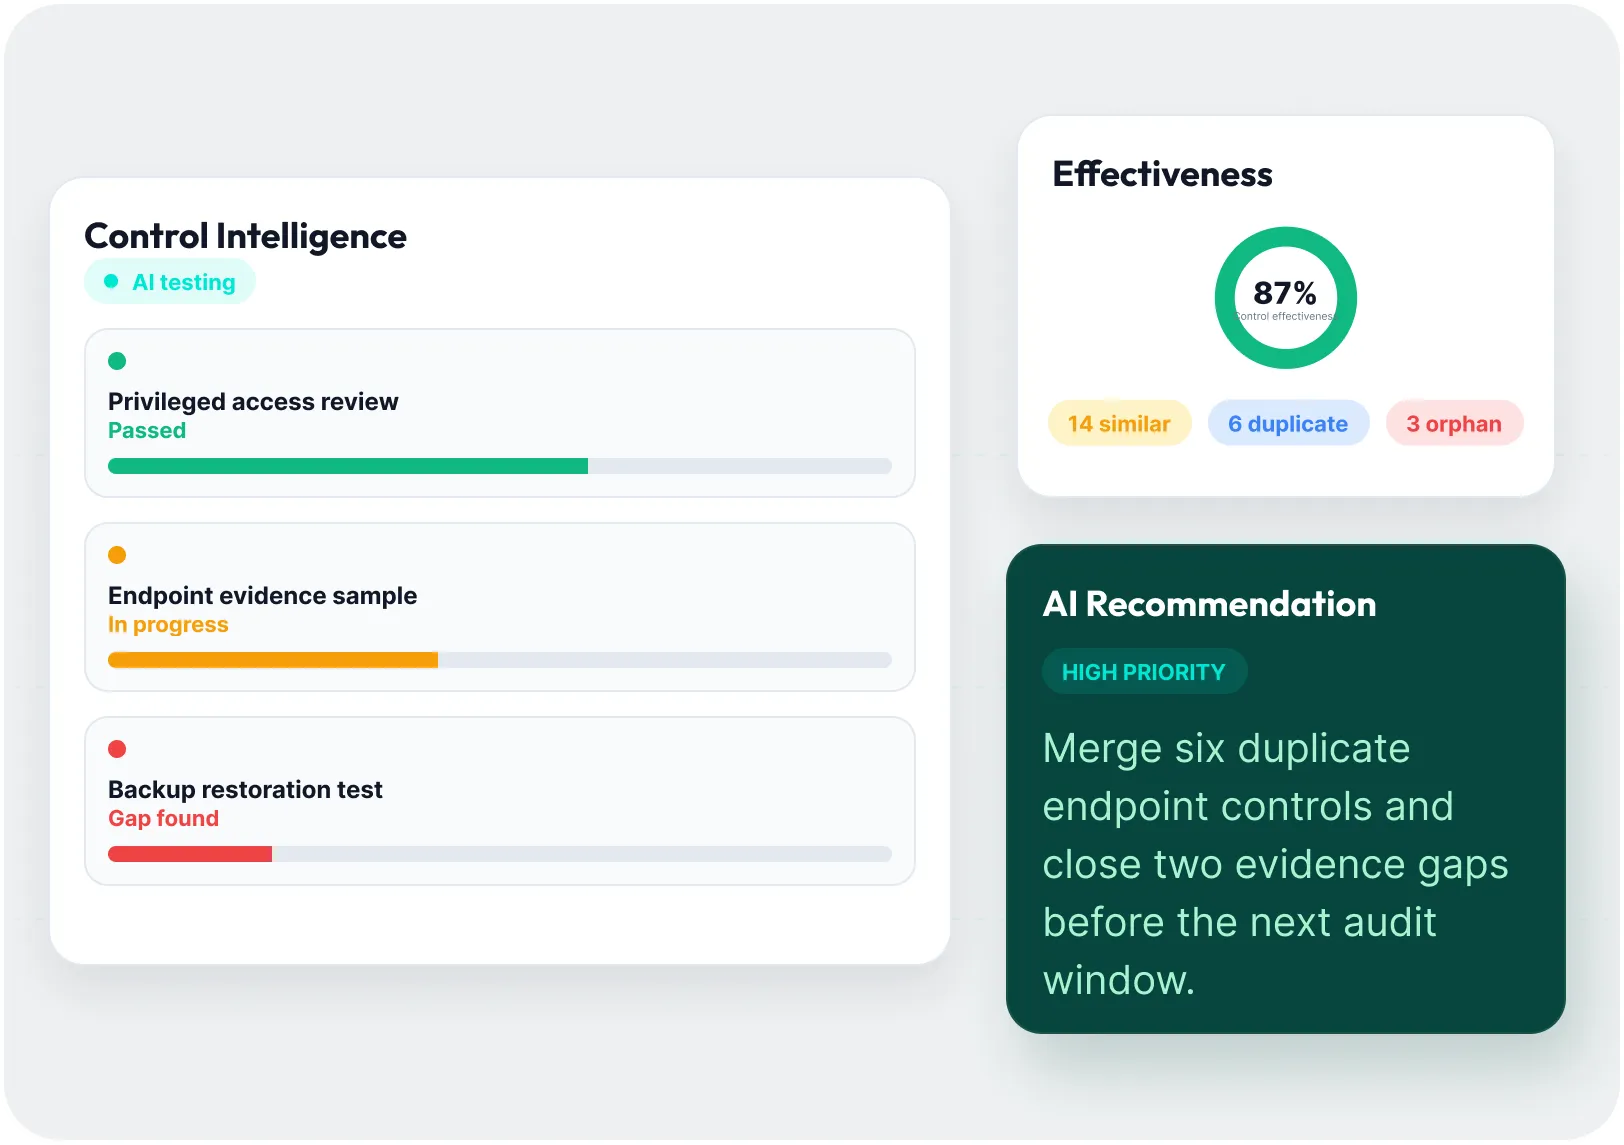
Purpose-built agents assess risks, test controls, identify gaps, gather evidence, and guide remediation.
Build and deploy agents tailored to your cyber needs with MetricStream and partners.
60%
Improvement across key Cyber GRC workflows with AI
40%
Reduction in risk assessments and control tests through rationalization
50%
Lower technology costs through consolidation of siloed GRC tools
Source: MetricStream’s Business Value Calculator
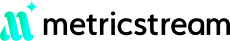
Stop piecing together cyber risk across security tools, spreadsheets, and disparate GRC programs. Connect assets, threats, vulnerabilities, controls, policies, requirements, vendors, evidence, and issues on a single governed GRC platform to see cyber risk in full context. AI reveals the relationships behind every signal, empowering cyber teams to quickly understand which assets, services, obligations, and business operations are affected and prioritize areas that need attention.
Cyber GRC capability
Traditional Cyber GRC
MetricStream Agentic Cyber GRC
Cyber context
Security and GRC data remain disconnected
AI connects signals with assets, controls, vendors, and business impact
Risk assessments
Periodic and manually assembled
Agents pre-populate assessments with connected cyber context
Control assurance
Fixed schedules and repeated evidence requests
AI prioritizes controls while agents support testing and evidence gathering
Compliance
Frameworks mapped and tested separately
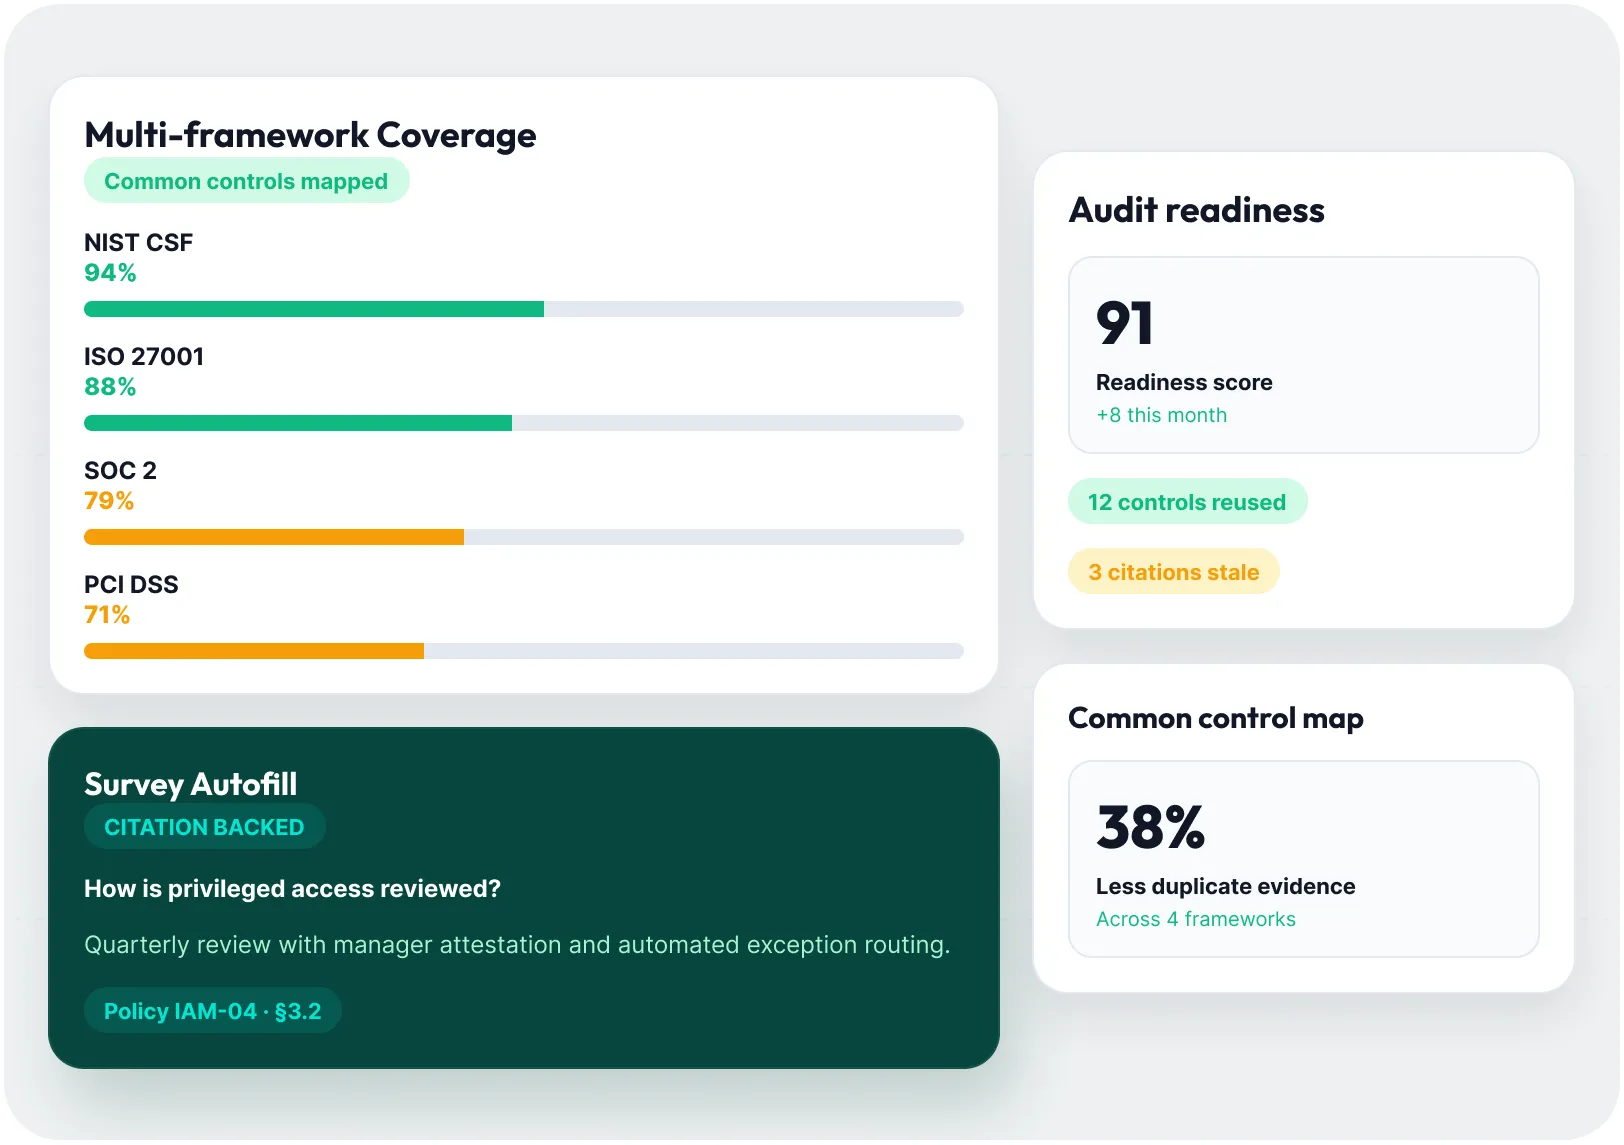
Common controls support multiple frameworks and reduce duplicate work
Policies and vendors
Managed in separate programs
Policy and vendor intelligence connect to the cyber risk picture
Issue management
Findings reviewed and routed manually
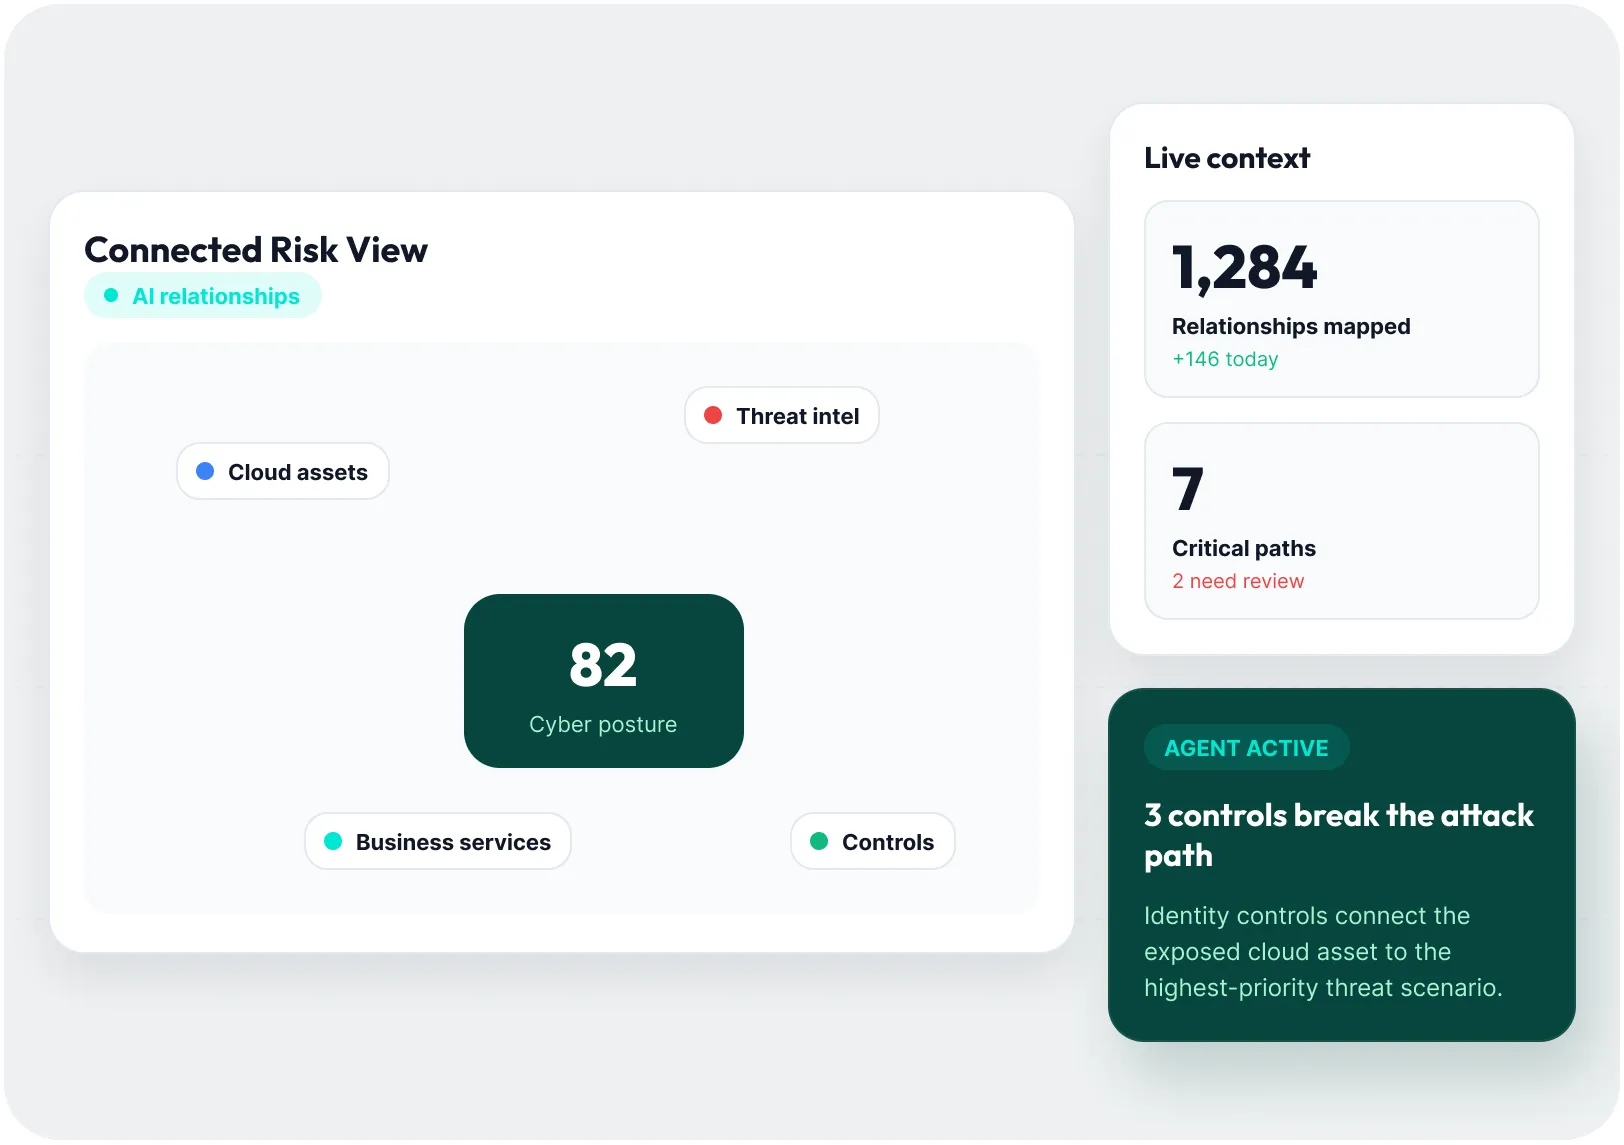
AI clusters related issues and recommends coordinated remediation
Executive reporting
Static and backward-looking
AI generates current, contextual cyber risk narratives
Use our interactive ROI calculator, built by Forrester, to estimate what Enterprise GRC could deliver for your organization. Enter details such as annual revenue, number of GRC tools, and compliance exposure to see your potential savings, payback period, and return on investment.
Calculate My ROI
Purpose-built Cyber GRC assistants and agents support cyber risk, controls, compliance, policies, evidence, and vendor oversight.
Link security findings to assets, processes, controls, obligations, critical services, owners, and business impact.
Configure frameworks, assessments, scoring, workflows, thresholds, dashboards, and integrations around your requirements. Stay ahead of evolving cyber requirements
Role-based access, citations, audit trails, guardrails, and human review support responsible agentic AI.
20+ years of supporting complex cyber governance and risk programs in highly regulated organizations.
Cyber GRC specialists and AI engineers support implementation, adoption, optimization, and measurable value.

Analyst Report
Download the excerpt to see why MetricStream was recognized as a GRC Leader in 2025.
Download Now
eBook
A CISO's guide to outsmarting cyber risk before it outsmarts you.
Read More
Case Study
Learn how MetricStream helped an oil and gas giant automate cyber risk and compliance management processes and improved its overall cyber maturity and resilience.
Read More
Whitepaper
Learn how GRC leaders are adopting AI responsibly and proving measurable ROI at scale.
Read MoreMetricStream Cyber GRC is an AI-first Cyber GRC software that enables organizations to rapidly implement an integrated IT and cyber risk and compliance program aligned with business and security objectives. It combines IT and cyber risk management, threat and vulnerability management, cybersecurity compliance, policy management, and vendor risk management on a single platform. The product supports industry standards including NIST, ISO 27001, and SOC 2, and provides a quantified view of cyber risk exposure to support informed investment decisions.
According to customer responses and the GRC Journey Business Value Calculator, MetricStream Cyber GRC has delivered a 66% reduction in the time taken to complete risk assessments, 37% cost savings in risk assessments and associated processes, 50% time savings in tracking and linking policies to regulations, and a 40% reduction of evidence requests through de-duplication.
MetricStream Cyber GRC expresses cyber risk exposure in monetary terms using advanced Cyber Risk Quantification capabilities. The product supports the FAIR (Factor Analysis of Information Risk) model and simulation techniques that convert range-based risk estimates into precise dollar values. Organizations can quantify the monetary impact of risks such as data breaches, identity theft, and infrastructure downtime, enabling executives to prioritize cyber investments based on business-aligned risk data rather than technical severity scores alone.
MetricStream Cyber GRC proactively identifies, consolidates, and prioritizes cybersecurity threats and vulnerabilities from multiple sources into a unified view. It determines combined risk ratings for business assets based on vulnerability severity and the asset's criticality, enabling security teams to make better-informed decisions about which vulnerabilities to remediate first. Integrations with third-party vulnerability scanning tools allow automated import of vulnerability data directly into the platform.
MetricStream Cyber GRC enables organizations to manage compliance with cybersecurity standards and frameworks, including NIST CSF, ISO 27001, NIST SP 800-53, and SOC 2, through a central compliance hierarchy that links controls, risks, policies, and assessments. Pre-packaged content covering 800+ controls enables fast implementation. Automated notifications alert stakeholders when standards change, and compliance status is tracked in real time through role-based dashboards.
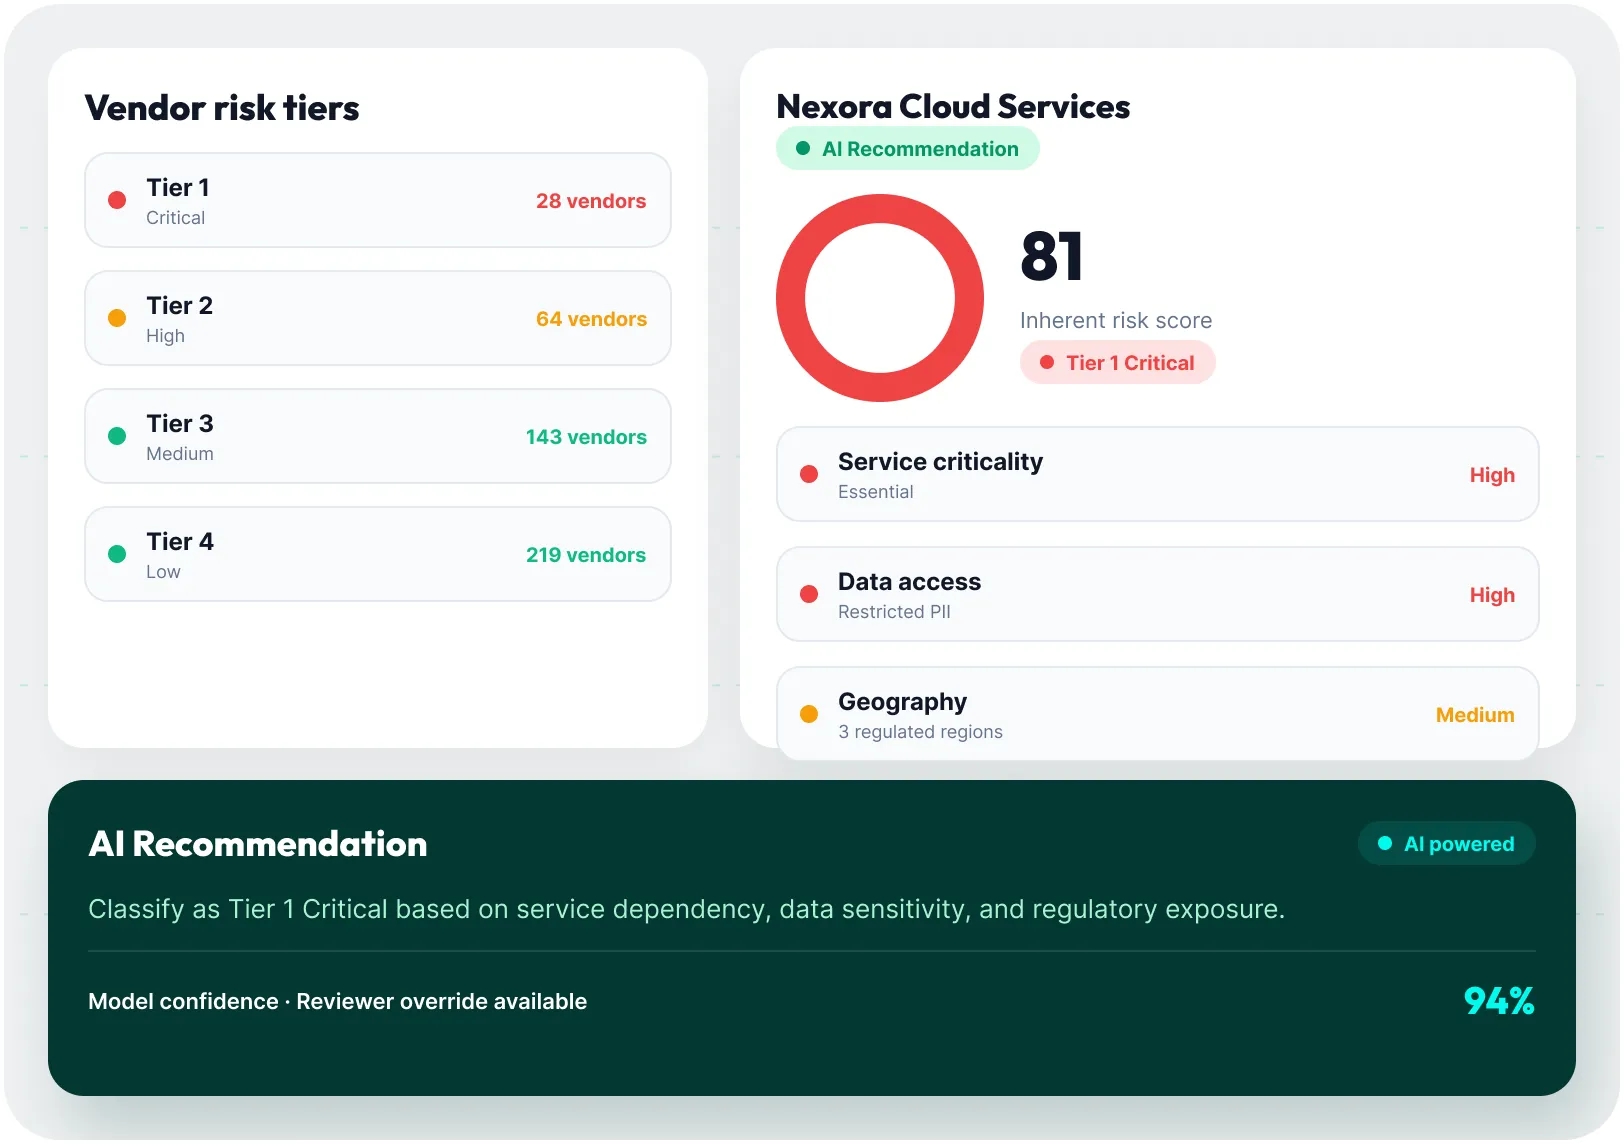
MetricStream Cyber GRC includes vendor risk management capabilities that allow organizations to identify, assess, and monitor IT vendor risks throughout the vendor lifecycle. Automated workflows accelerate vendor registration and onboarding. Pre-defined questionnaires simplify due diligence, and continuous monitoring using intelligence feeds from trusted content providers keeps vendor risk profiles current. Reports and analytics provide a holistic view of vendor risk, compliance, and performance.
MetricStream Cyber GRC is designed for CISOs, IT risk managers, cybersecurity compliance professionals, and security operations teams at organizations that need to integrate cyber risk management with their broader GRC program. It is especially valuable for organizations operating in regulated industries—such as financial services, healthcare, and energy—where cybersecurity compliance must be demonstrated to regulators, and where a quantified view of cyber risk is required for board and executive reporting.
MetricStream Cyber GRC reduces evidence request duplication by linking controls across multiple regulatory frameworks through a shared control library. A single control can satisfy requirements from several frameworks simultaneously, so organizations do not need to gather separate evidence for each framework. According to customer data, this approach has delivered a 40% reduction in evidence requests through de-duplication, significantly reducing the compliance workload on IT and security teams.
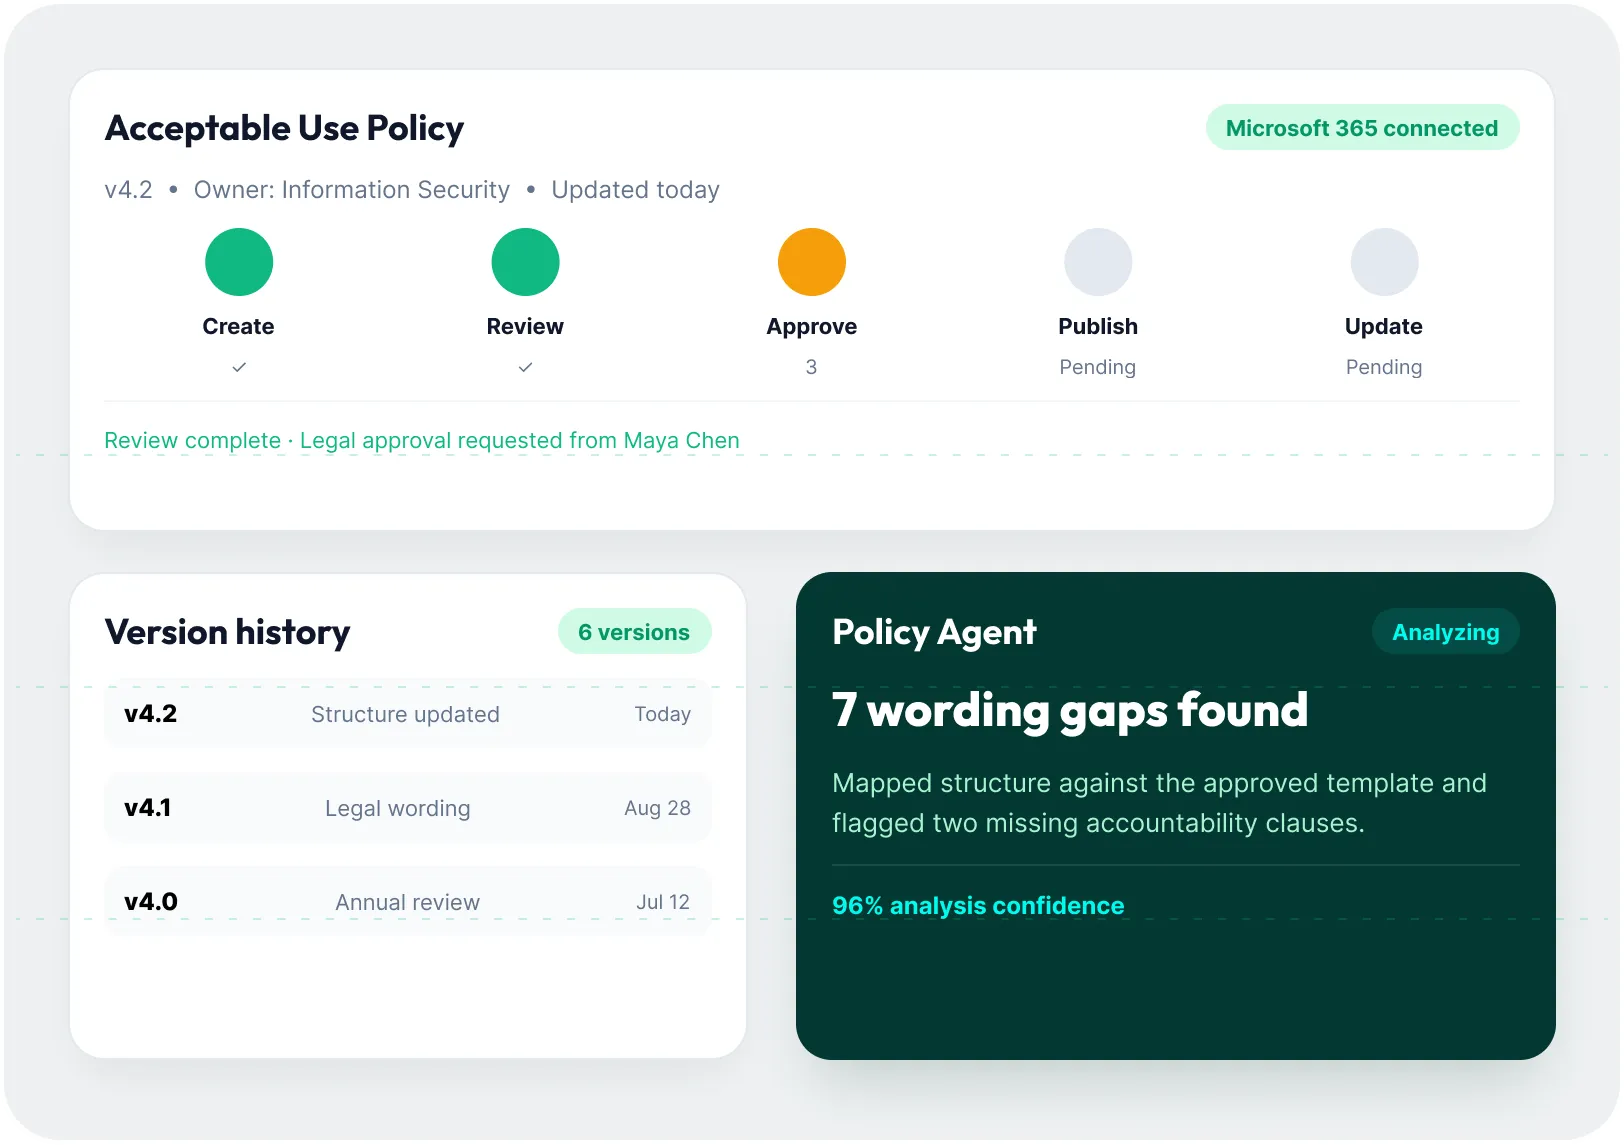
MetricStream Cyber GRC includes IT and cyber policy management capabilities that enable organizations to create, communicate, and maintain IT and cyber policies across business units and global locations. Policies are mapped to asset classes, requirements, risks, controls, processes, and regulations. Automated policy review cycles, employee attestations, and exception management workflows ensure that policies stay current and that compliance with policy requirements can be demonstrated at any time.
MetricStream Cyber GRC accelerates audit readiness by maintaining a continuously updated, evidence-linked record of IT and cyber control assessments aligned to standards such as ISO 27001, NIST CSF, and SOC 2. Pre-packaged content provides a head start on compliance program implementation, and automated workflows ensure that controls are tested, findings are documented, and remediation actions are tracked on schedule. This continuous readiness approach reduces the sprint effort typically required before an audit.